Login

BTMOB: A stealthy RAT burrowing deep into Android devices
The malware pairs remote access capabilities with ready-made campaign tools, lowering the barrier for full device compromise

Posted by Noel Butler via Fulldisclosure on May 25
So when is the fix for dovecot 2.3 source code due to be released?
Posted by outreach on May 25
-----BEGIN SECURITY ADVISORY-----
Posted by m.nageh on May 25
-----BEGIN SECURITY ADVISORY-----
Posted by m.nageh on May 25
-----BEGIN SECURITY ADVISORY-----
Posted by m.nageh on May 25
-----BEGIN SECURITY ADVISORY-----
Posted by m.nageh on May 25
-----BEGIN SECURITY ADVISORY-----
Posted by Adamczyk Blazej on May 25
━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━
Today, we welcome the 45th government onboarded to Have I Been Pwned’s free gov service: Bhutan. The Bhutan Computer Incident Response Team, BtCIRT, now has access to monitor Bhutanese government domains against the data in HIBP. As Bhutan’s national CIRT, BtCIRT is responsible for consuming threat intelligence and sharing relevant insights with its constituents, helping identify and respond to cyber risks affecting government services and the people who depend on them.
This is exactly the sort of organisation the HIBP government service was built to support: national cybersecurity teams using breach data to identify leaked credentials and compromised databases associated with their government domains.
BtCIRT now joins the growing list of national CIRTs and government cybersecurity teams using HIBP to better understand their exposure, respond quickly when new breaches appear, and reduce the risk posed by compromised credentials before attackers can take advantage.
Authorities in the Netherlands have arrested the co-owners of two related Internet hosting companies for operating IT infrastructure used by Russia to carry out cyberattacks, influence operations and disinformation campaigns inside the European Union. The two men were the focus of a 2025 KrebsOnSecurity story about how their hosting companies had assumed control over the technical infrastructure of Stark Industries Solutions, an Internet service provider sanctioned last year by the EU as a frequent staging ground for cyber mischief from Russia’s intelligence agencies.
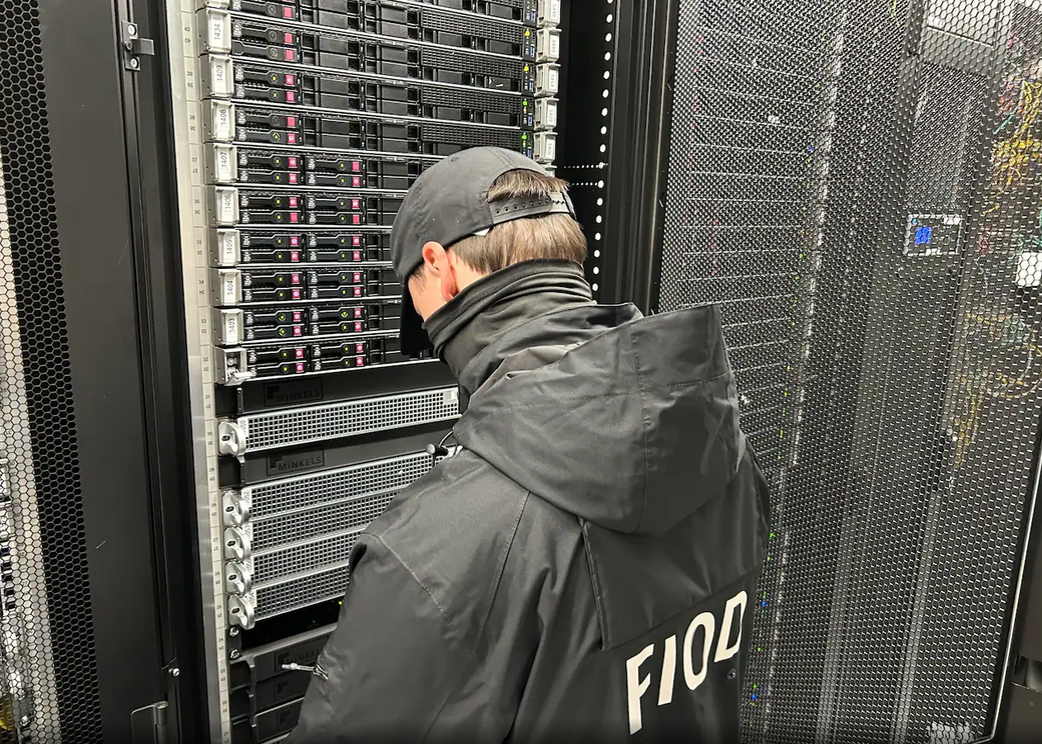
An investigator with the Tax Intelligence and Investigation Service (FIOD), the Dutch financial crimes agency, during the raid. Image: FIOD.
The Dutch daily news outlet de Volkskrant reports that the Dutch financial crime agency FIOD on May 18 arrested a 57-year-old from Amsterdam and a 39-year-old from The Hague, charging them with violating sanctions law by directly or indirectly making economic resources available to EU-sanctioned entities.
The Dutch investigation focuses on Stark Industries, a sprawling hosting provider that materialized just two weeks before Russia invaded Ukraine. As detailed in this May 2024 deep-dive, Stark quickly became the source of massive distributed denial-of-service (DDoS) attacks against European targets, and emerged as a top supplier of proxy and anonymity services that showed up time and again in cyberattacks linked to Russia-backed hacking groups.
That report identified two Moldovan brothers — Ivan and Yuri Neculiti and their company PQHosting — who were providing one of Stark’s two main conduits to the larger Internet. In May 2025, the EU sanctioned PQHosting and the Neculiti brothers for aiding Russia’s hybrid warfare efforts. But as KrebsOnSecurity observed in September 2025, those sanctions failed to target Stark’s remaining connection to the Internet — an Internet service provider based in the Netherlands called MIRhosting.
MIRhosting is operated by Andrey Nesterenko, a 39-year-old Russian native who runs the business out of the Netherlands. News that PQHosting and the Neculiti brothers were about to be sanctioned by the EU leaked in the media nearly two weeks before the sanctions were announced last year. During that time, the Stark network assets were transferred from PQHosting to a new entity called the[.]hosting, under the control of the Dutch entity WorkTitans BV.
And as our September 2025 report showed, WorkTitans was controlled by Nesterenko and a 57-year-old from Amsterdam named Youssef Zinad. On top of that, WorkTitans was getting connectivity to the larger Internet solely through MIRhosting, where Zinad had worked previously.
On May 18, Dutch financial crime investigators arrested Nesterenko and Zinad, and searched three businesses in Enschede and Almere and two data centers in Dronten and Schiphol-Rijk. A statement from the Dutch authorities said they also seized laptops, telephones and more than 800 servers.
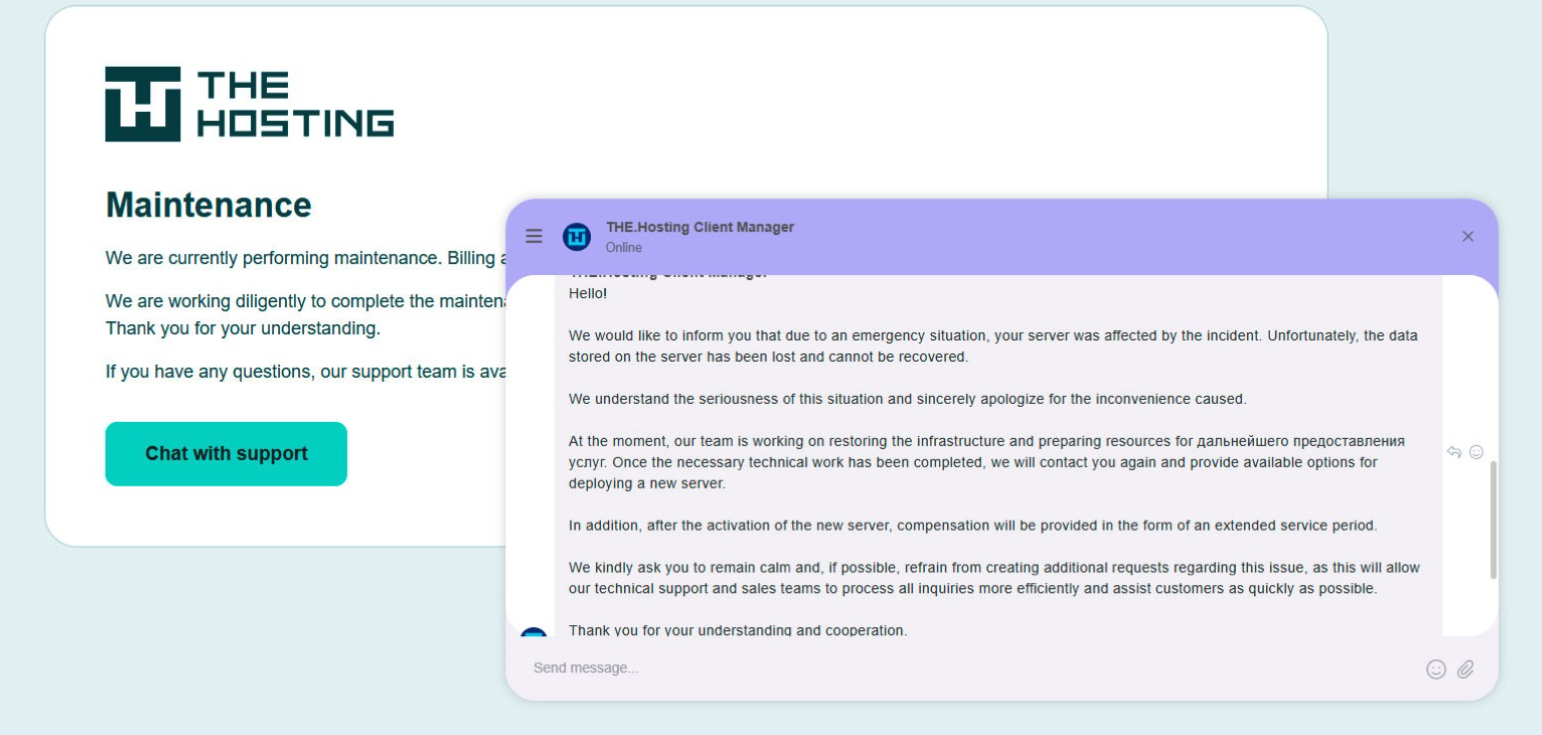
A message to the-hosting customers immediately after 800 of its servers were seized by Dutch authorities. The message says that unfortunately data stored on the server has been lost and cannot be recovered.
De Volkskrant said it reviewed data showing WorkTitans and MIRhosting were the most-used networks in pro-Russian attacks on Danish government bodies between November 13 and 19, 2025, the week of Denmark’s municipal elections.
The publication wrote that prior to Nesterenko’s arrest, the MIRhosting founder denied that he knew his servers had been misused by pro-Russian cybercriminals. “He said he had ended all services with the Neculiti brothers when the EU sanctions came into force in May 2025,” and the he “reserved all rights to take action against ‘harmful and incorrect publications,” de Volkskrant wrote.
MIRhosting released a statement saying it has initiated an internal investigation into the alleged facts concerning the elections in Denmark, and that it has temporarily paused services to WorkTitans as a precautionary measure while the matter is being reviewed further.
“Based on our preliminary findings, there are no indications that the services over which we exercise control were actually used to influence the Danish elections,” the statement reads. “No anomalies or spikes were observed in our network traffic during the period mentioned in the publication; had large-scale DDoS attacks occurred, such activity would have been evident. Furthermore, prior to the media publication, we had not received any complaints, abuse reports, or official requests regarding suspicious activities or misuse of our network. Meanwhile, our regular operational activities continue, and our service to our other clients remains fully intact.”
Born in Nizhny Novgorod, Russia, Mr. Nesterenko grew up as a piano prodigy who performed publicly at a young age. In 2004, Nesterenko founded MIRhosting’s parent Innovation IT Solutions Corp., which has the notable distinction of being the company responsible for hosting stopgeorgia[.]ru, a hacktivist website for organizing cyberattacks against Georgia that appeared at the same time Russian forces invaded the former Soviet nation in 2008. That conflict was thought to be the first war ever fought in which a notable cyberattack and an actual military engagement happened simultaneously.
Responding to questions shared via email, Nesterenko said MIRhosting does not support cybercrime, sanctions evasion, or illegal activity, and that the allegations and arrest by Dutch authorities have been extremely harmful to him and his company.
“The transition to the.hosting was not intended to evade sanctions,” Nesterenko wrote. “The hardware and customer portfolio had already been transferred to WorkTitans before the sanctions appeared. Closing or damaging a legitimate Dutch infrastructure company will not stop cybercrime, but it will harm many people who have done nothing wrong.”
Far less is public about the 57-year-old Zinad, who reportedly has been keeping a low profile since our story last year. De Volkskrant reported that Zinad blocked access to his LinkedIn account, had gone months without responding to emails, WhatsApp messages and phone calls, and told a colleague that illness was forcing him to lead a somewhat more reclusive life.
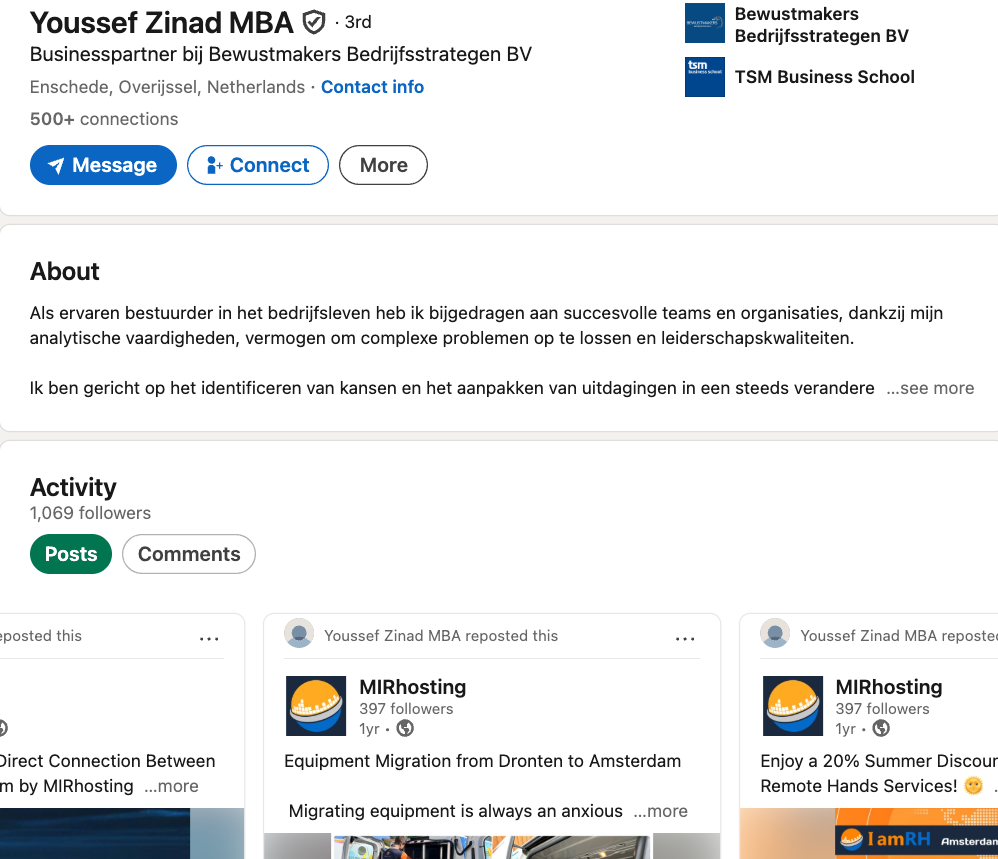
Mr. Zinad’s now-defunct LinkedIn profile. It was full of posts for MIRhosting’s services.
Mr. Nesterenko claims Zinad was never an employee of MIRhosting.
“He helped me and MIRhosting with certain business tasks under a normal business-to-business arrangement between companies,” Nesterenko explained.
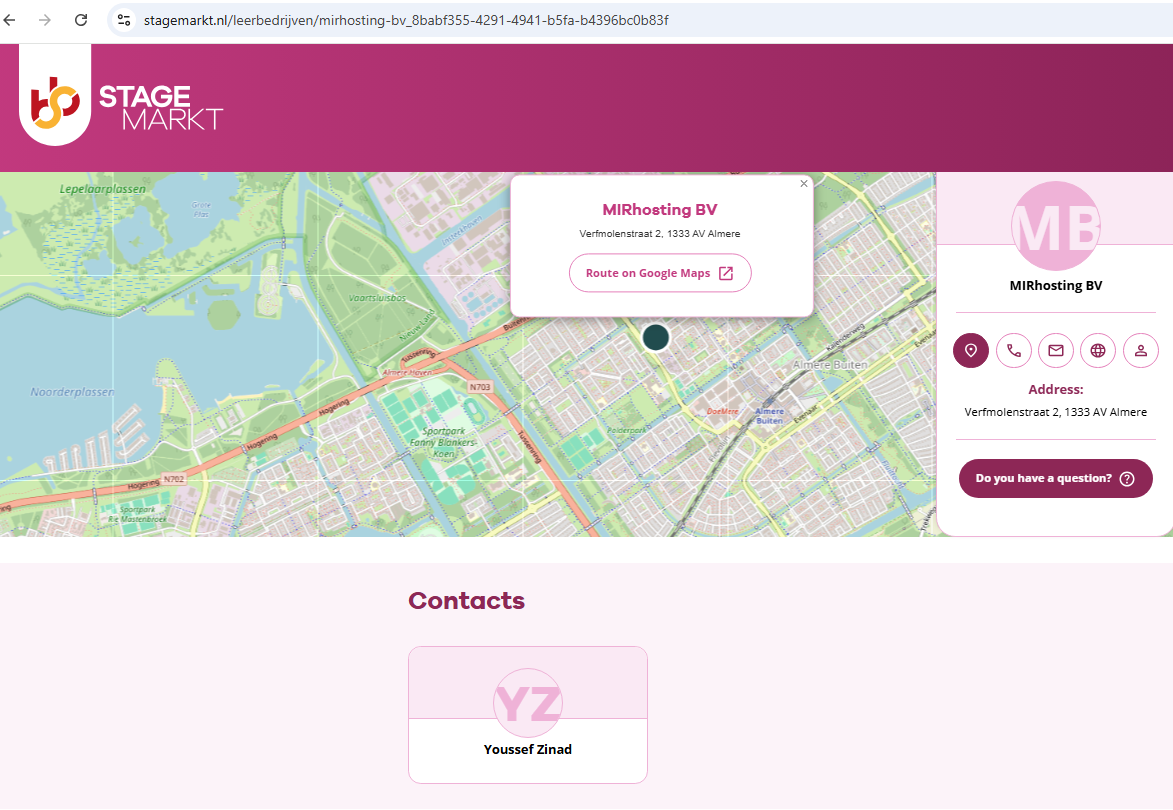
However, in previous emails to KrebsOnSecurity, Nesterenko carbon copied Mr. Zinad (who had a @mirhosting.com email), explaining that he was part of the company’s legal team. Also, the Dutch website stagemarkt[.]nl lists Youssef Zinad as an official contact for MIRhosting’s offices in Almere.
Mr. Zinad has never responded to requests for comment. Nor did de Volkskrant have any luck tracking him down. The publication said it repeatedly asked Mr. Zinad (referred to here as simply “Z”), but he reportedly avoided every form of contact.
“‘I am unavailable but will respond to your message as soon as possible,’ reads an automated reply on WhatsApp on 2 October 2025,” de Volkskrant reported. “It is the only response de Volkskrant would receive in months. He did not pick up his phone and did not call back. When an acquaintance asked him via LinkedIn to contact the reporter, he blocked access to his LinkedIn page. At an address in Almere where Z.’s personal limited company is registered, no one was present in April. The corner house’s blinds were drawn, and a pile of rubbish bags lay outside next to a container, as if someone had recently left. A neighbour said he knew the man but did not know where he was staying. Z. was later arrested at a residence in Amsterdam.”
Well, that didn't last long! Recording this on Saturday morning my time, I observed ShinyHunters having gone quiet since the massive haul that would have been the Instructure ransom. It was two weeks almost to the hour since I'd first heard rumour of payment being made, and I posited that groups like this often go quiet after they feel the heat, only to emerge shortly after, the drug that is hacking being too strong to ignore. Anyway, here we now are:
🚨🇺🇸 ShinyHunters Claims 3 New Victims
— Dark Web Informer (@DarkWebInformer) May 22, 2026
🇺🇸 https://t.co/v8Wf457Gbp: U.S.-based dental benefits administrator and oral health company.
🇺🇸 Charter Communications, Inc.: U.S. telecommunications and cable company best known for Spectrum internet, TV, mobile, and phone services.
🇺🇸… pic.twitter.com/epWcVVGRHa
DentaQuest has since been removed, but their website is currently returning "Access Denied", which isn't a great look. Obviously, the broken website doesn't look great, but neither do the optics of potentially having paid a ransom. But that does seem to be the way that many of these incidents are going now 🤷♂️

Lawmakers in both houses of Congress are demanding answers from the U.S. Cybersecurity & Infrastructure Security Agency (CISA) after KrebsOnSecurity reported this week that a CISA contractor intentionally published AWS GovCloud keys and a vast trove of other agency secrets on a public GitHub account. The inquiry comes as CISA is still struggling to contain the breach and invalidate the leaked credentials.
On May 18, KrebsOnSecurity reported that a CISA contractor with administrative access to the agency’s code development platform had created a public GitHub profile called “Private-CISA” that included plaintext credentials to dozens of internal CISA systems. Experts who reviewed the exposed secrets said the commit logs for the code repository showed the CISA contractor disabled GitHub’s built-in protection against publishing sensitive credentials in public repos.
CISA acknowledged the leak but has not responded to questions about the duration of the data exposure. However, experts who reviewed the now-defunct Private-CISA archive said it was originally created in November 2025, and that it exhibits a pattern consistent with an individual operator using the repository as a working scratchpad or synchronization mechanism rather than a curated project repository.
In a written statement, CISA said “there is no indication that any sensitive data was compromised as a result of the incident.” But in a May 19 a letter (PDF) to CISA’s Acting Director Nick Andersen, Sen. Maggie Hassan (D-NH) said the credential leak raises serious questions about how such a security lapse could occur at the very agency charged with helping to prevent cyber breaches.
“This reporting raises serious concerns regarding CISA’s internal policies and procedures at a time of significant cybersecurity threats against U.S. critical infrastructure,” Sen. Hassan wrote.
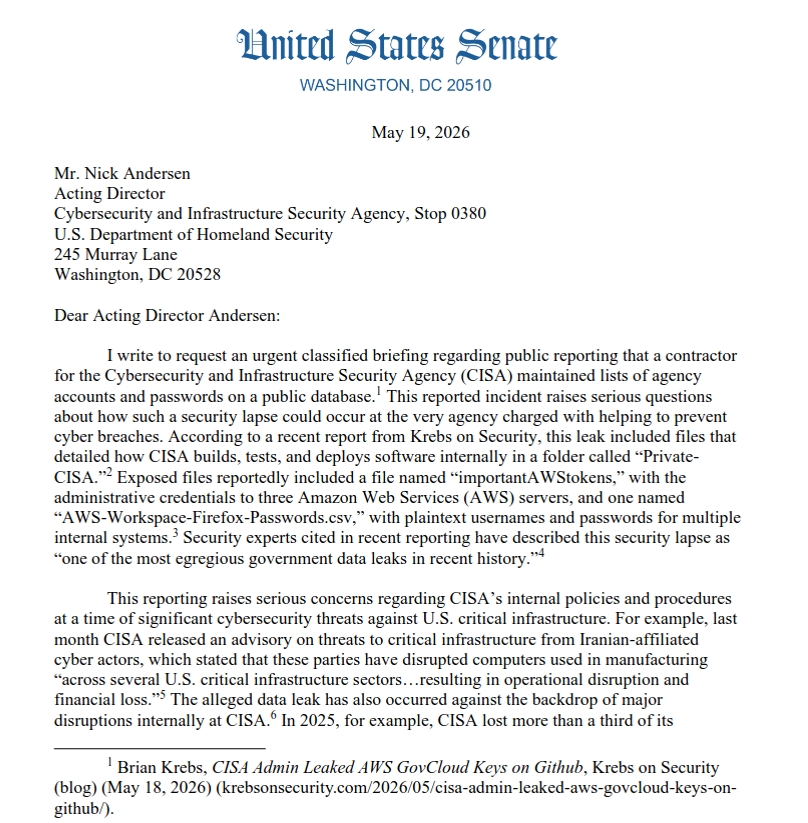
A May 19 letter from Sen. Margaret Hassan (D-NH) to the acting director of CISA demanded answers to a dozen questions about the breach.
Sen. Hassan noted that the incident occurred against the backdrop of major disruptions internally at CISA, which lost more than a third of it workforce and almost all of its senior leaders after the Trump administration forced a series of early retirements, buyouts, and resignations across the agency’s various divisions.
Rep. Bennie Thompson (D-MS), the ranking member on the House Homeland Security Committee, echoed the senator’s concerns.
“We are concerned that this incident reflects a diminished security culture and/or an inability for CISA to adequately manage its contract support,” Thompson wrote in a May 19 letter to the acting CISA chief that was co-signed by Rep. Delia Ramirez (D-Ill), the ranking member of the panel’s Subcommittee on Cybersecurity and Infrastructure Protection. “It’s no secret that our adversaries — like China, Russia, and Iran — seek to gain access to and persistence on federal networks. The files contained in the ‘Private-CISA’ repository provided the information, access, and roadmap to do just that.”
KrebsOnSecurity has learned that more a week after CISA was first notified of the data leak by the security firm GitGuardian, the agency is still working to invalidate and replace many of the exposed keys and secrets.
On May 20, KrebsOnSecurity heard from Dylan Ayrey, the creator of TruffleHog, an open-source tool for discovering private keys and other secrets buried in code hosted at GitHub and other public platforms. Ayrey said CISA still hadn’t invalidated an RSA private key exposed in the Private-CISA repo that granted access to a GitHub app which is owned by the CISA enterprise account and installed on the CISA-IT GitHub organization with full access to all code repositories.
“An attacker with this key can read source code from every repository in the CISA-IT organization, including private repos, register rogue self-hosted runners to hijack CI/CD pipelines and access repository secrets, and modify repository admin settings including branch protection rules, webhooks, and deploy keys,” Ayrey told KrebsOnSecurity. CI/CD stands for Continuous Integration and Continuous Delivery, and it refers to a set of practices used to automate the building, testing and deployment of software.
KrebsOnSecurity notified CISA about Ayrey’s findings on May 20. Ayrey said CISA appears to have invalidated the exposed RSA private key sometime after that notification. But he noted that CISA still hasn’t rotated leaked credentials tied to other critical security technologies that are deployed across the agency’s technology portfolio (KrebsOnSecurity is not naming those technologies publicly for the time being).
CISA responded with a brief written statement in response to questions about Ayrey’s findings, saying “CISA is actively responding and coordinating with the appropriate parties and vendors to ensure any identified leaked credentials are rotated and rendered invalid and will continue to take appropriate steps to protect the security of our systems.”
Ayrey said his company Truffle Security monitors GitHub and a number of other code platforms for exposed keys, and attempts to alert affected accounts to the sensitive data exposure(s). They can do this easily on GitHub because the platform publishes a live feed which includes a record of all commits and changes to public code repositories. But he said cybercriminal actors also monitor these public feeds, and are often quick to pounce on API or SSH keys that get inadvertently published in code commits.
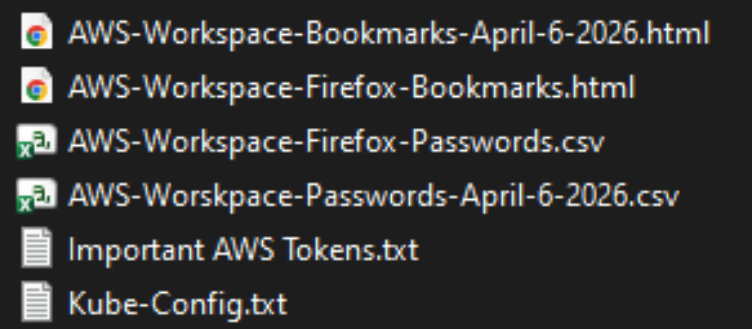
The Private-CISA GitHub repo exposed dozens of plaintext credentials to important CISA GovCloud resources.
In practical terms, it is likely that cybercrime groups or foreign adversaries also noticed the publication of these CISA secrets, the most egregious of which appears to have happened in late April 2026, Ayrey said.
“We monitor that firehose of data for keys, and we have tools to try to figure out whose they are,” he said. “We have evidence attackers monitor that firehose as well. Anyone monitoring GitHub events could be sitting on this information.”
James Wilson, the enterprise technology editor for the Risky Business security podcast, said organizations using GitHub to manage code projects can set top-down policies that prevent employees from disabling GitHub’s protections against publishing secret keys and credentials. But Wilson’s co-host Adam Boileau said it’s not clear that any technology could stop employees from opening their own personal GitHub account and using it to store sensitive and proprietary information.
“Ultimately, this is a thing you can’t solve with a technical control,” Boileau said on this week’s podcast. “This is a human problem where you’ve hired a contractor to do this work and they have decided of their own volition to use GitHub to synchronize content from a work machine to a home machine. I don’t know what technical controls you could put in place given that this is being done presumably outside of anything CISA managed or even had visibility on.”
Update, 3:05 p.m. ET: Added statement from CISA. Corrected a date in the story (Truffle Security said it found the repo gained some of its most sensitive secrets in late April 2026, not 2025).
Memorial Day weekend officially kicks off summer, and for millions of Americans, that means road trips, flights, cookouts, and a little online shopping for the deals.
Unfortunately, scammers know this. They count on the fact that you’re distracted, you’re moving fast, and you’re probably connected to a network you don’t own.
Here are five scams surging this holiday weekend, what they look like, and how to stay ahead of them.
You’re packing your bag when a text arrives: “Unusual activity detected on your account. Verify now to avoid suspension.”
It looks like it’s from your bank, or maybe your hotel loyalty program. There’s a link. There’s urgency. And that’s exactly the point.
These are brand impersonation scams, and they’re a dominant tactic year-round, but they spike around travel holidays when people are actively monitoring reservations and accounts.
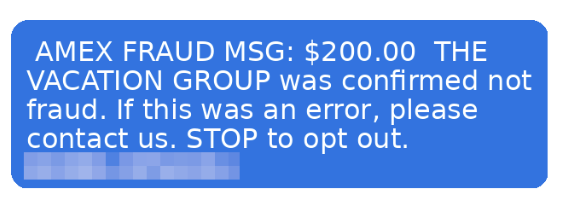
According to McAfee research, trusted brands like banks, airlines, and hotels are among the most commonly impersonated, and email scams impersonating retail and financial brands have surged up to 85% as major holidays approach.
The message will typically ask you to click a link and “confirm your details” to secure your account or honor a reservation. That link leads to a convincing-looking fake site designed to capture your login credentials, payment info, or both.
How to Avoid Travel Alert Scams:
McAfee’s Scam Detector can flag suspicious messages before you interact with them, whether they come via text, email, or social media.
Memorial Day is one of the biggest shopping weekends of the year. Scammers treat it like an open invitation.
Fraudulent retailers flood social feeds with too-good-to-be-true deals on everything from patio furniture to electronics, often impersonating legitimate brands with copycat websites and paid ads.
According to McAfee’s holiday shopping research, 91% of shoppers see ads from unfamiliar retailers, 37% say they might buy from a brand they don’t recognize, and a full 40% of consumers have abandoned a purchase out of fear that the deal wasn’t real.
The most impersonated brands in McAfee’s research span luxury labels (Coach, Dior, Gucci) to mainstream favorites (Apple, Samsung, Nintendo, Disney), exactly the kind of items that show up in “blowout sale” ads. Fake storefronts have grown significantly, with technology URL scams rising nearly 50%.
Once shoppers enter their payment details on a fraudulent site, that information goes directly to criminals. The average scam loss during the holiday shopping period runs around $840 per victim.
How to Avoid Shopping Scams:
McAfee’s Web Protection blocks malicious and suspicious sites before they load, including fake checkout pages.
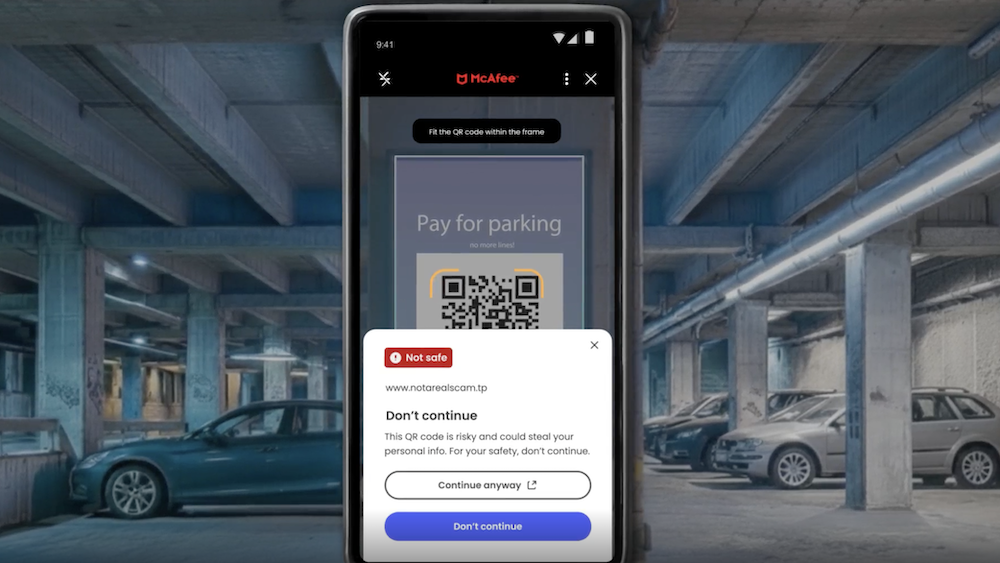
If you’re road-tripping this weekend, you may scan a QR code somewhere. It could be at the gas pump, a rest stop, a parking meter, or a roadside attraction. Scammers know this too.
Criminals increasingly place fake QR codes over legitimate ones on gas station pumps, parking kiosks, and public signs. When you scan, you’re redirected to a convincing-looking payment or login page that captures your financial information. This is known as “quishing” or phishing via QR code.
McAfee research shows just how widespread this risk has become: 68% of people scanned a QR code in the past three months, and 18% ended up on a suspicious or unsafe page after scanning. Among those who did, more than half took a risky action like entering personal information, installing an app, or connecting a digital wallet.
How to Avoid Sketchy QR Codes:
McAfee’s Scam Detector now includes instant QR code safety checks that assess risk before you tap, so you’re not flying blind at the gas pump.
Whether you’re waiting at the airport or grabbing coffee before hitting the highway, free Wi-Fi can feel like a gift. But not every “free Wi-Fi” network is what it appears to be.
Hackers set up what are called “evil twin” networks, hotspots with names designed to look exactly like the legitimate network at the airport, hotel, or café you’re in.
The moment you connect, they can use tools called packet sniffers to capture the data you send and receive: passwords, banking credentials, credit card numbers, email logins.
According to McAfee’s travel research, 63% of travelers connect to public Wi-Fi, and 49% use airport Wi-Fi, making these among the riskiest behaviors travelers engage in without realizing it.
Some of these fake networks go further, presenting a phony login screen that captures your username and password for popular services like Google or Apple before you even realize you’ve been compromised.
How to Avoid Malicious Wi-Fi :
A VPN creates an encrypted tunnel for your internet traffic, so even if a hacker intercepts it, they’ll only see scrambled data. McAfee’s VPN is included in McAfee+ plans and automatically connects when you join public Wi-Fi, exactly the protection you want when you’re traveling and connecting everywhere.
You may have seen these already: a text that says you owe an unpaid toll or parking fee, with a link to pay before penalties kick in. These scams have been circulating for a while, and there’s a good chance Memorial Day weekend is about to make them worse.
Scammers track news cycles and know that millions of Americans will be driving this weekend, many of them through toll roads and unfamiliar areas.
That means they can blast out fake “unpaid toll” texts after the holiday and a significant percentage of recipients will think: “Actually, I did drive somewhere new this weekend.” That uncertainty is exactly what they’re counting on.
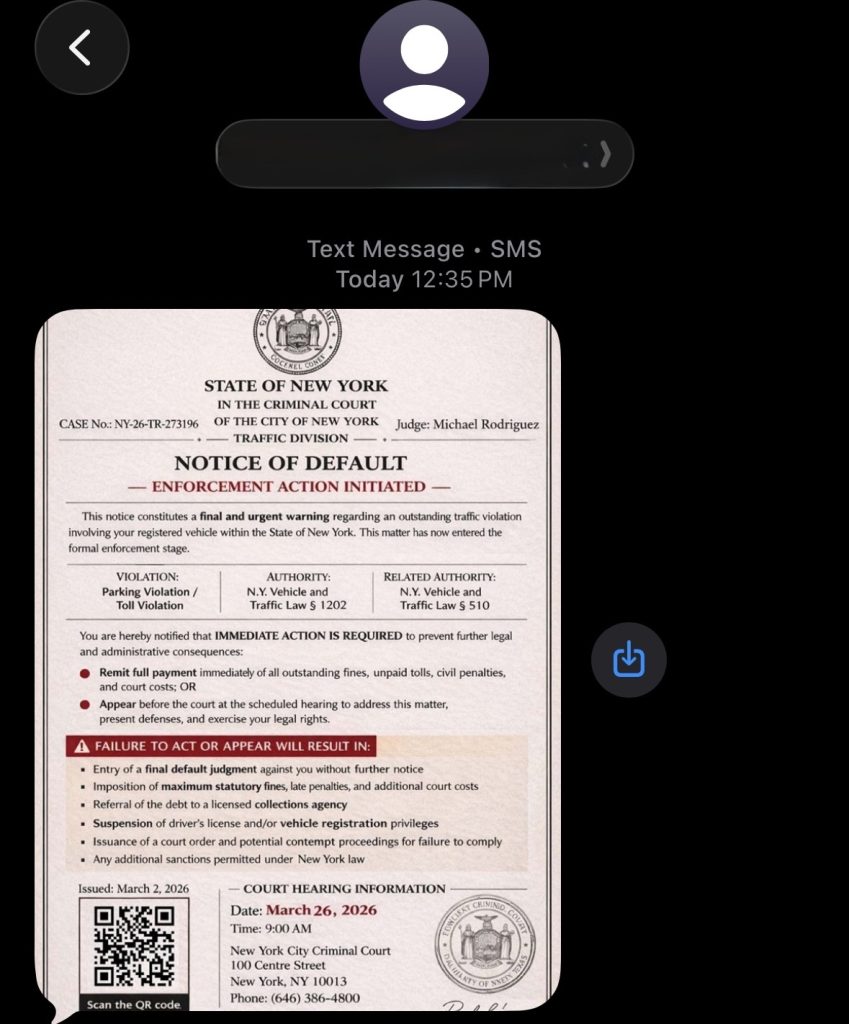
These texts typically impersonate EZPass, SunPass, or state transportation departments and create urgency around a small fee to avoid larger fines. The link leads to a fake payment page designed to steal your credit card details.
How to Avoid Toll Scams:
Scammers don’t take holidays. If anything, long weekends are peak season. The good news: a little awareness goes a long way. Slow down before you click, verify before you scan, and protect your connection before you log on.
McAfee+ Advanced comes with layered protection across all the moments where scams are most likely to strike, from the gas station to the hotel lobby to your inbox.
Stay safe out there.
The post 5 Scams to Watch for This Memorial Day Weekend appeared first on McAfee Blog.
Canadian authorities on Wednesday arrested a 23-year-old Ottawa man on suspicion of building and operating Kimwolf, a fast spreading Internet-of-Things botnet that enslaved millions of devices for use in a series of massive distributed denial-of-service (DDoS) attacks over the past six months. KrebsOnSecurity publicly named the suspect in February 2026 after the accused launched a volley of DDoS, doxing and swatting campaigns against this author and a security researcher. He now faces criminal hacking charges in both Canada and the United States.
A criminal complaint unsealed today in an Alaska district court charges Jacob Butler, a.k.a. “Dort,” of Ottawa, Canada with operating the Kimwolf DDoS botnet. A statement from the Department of Justice says the complaint against Butler was unsealed following the defendant’s arrest in Canada by the Ontario Provincial Police pursuant to a U.S. extradition warrant. Butler is currently in Canadian custody awaiting an initial court hearing scheduled for early next week.
The government said Kimwolf targeted infected devices which were traditionally “firewalled” from the rest of the internet, such as digital photo frames and web cameras. The infected systems were then rented to other cybercriminals, or forced to participate in record-smashing DDoS attacks, as well as assaults that affected Internet address ranges for the Department of Defense. Consequently, the DoD’s Defense Criminal Investigative Service is investigating the case, with assistance from the FBI field office in Anchorage.
“KimWolf was tied to DDoS attacks which were measured at nearly 30 Terabits per second, a record in recorded DDoS attack volume,” the Justice Department statement reads. “These attacks resulted in financial losses which, for some victims, exceeded one million dollars. The KimWolf botnet is alleged to have issued over 25,000 attack commands.”
On March 19, U.S. authorities joined international law enforcement partners in seizing the technical infrastructure for Kimwolf and three other large DDoS botnets — named Aisuru, JackSkid and Mossad — that were all competing for the same pool of vulnerable devices.
On February 28, KrebsOnSecurity identified Butler as the Kimwolf botmaster after digging through his various email addresses, registrations on the cybercrime forums, and posts to public Telegram and Discord servers. However, Dort continued to threaten and harass researchers who helped track down his real-life identity and dramatically slow the spread of his botnet.
Dort claimed responsibility for at least two swatting attacks targeting the founder of Synthient, a security startup that helped to secure a widespread critical security weakness that Kimwolf was using to spread faster and more effectively than any other IoT botnet out there. Synthient was among many technology companies thanked by the Justice Department today, and Synthient’s founder Ben Brundage told KrebsOnSecurity he’s relieved Butler is in custody.
“Hopefully this will end the harassment,” Brundage said.
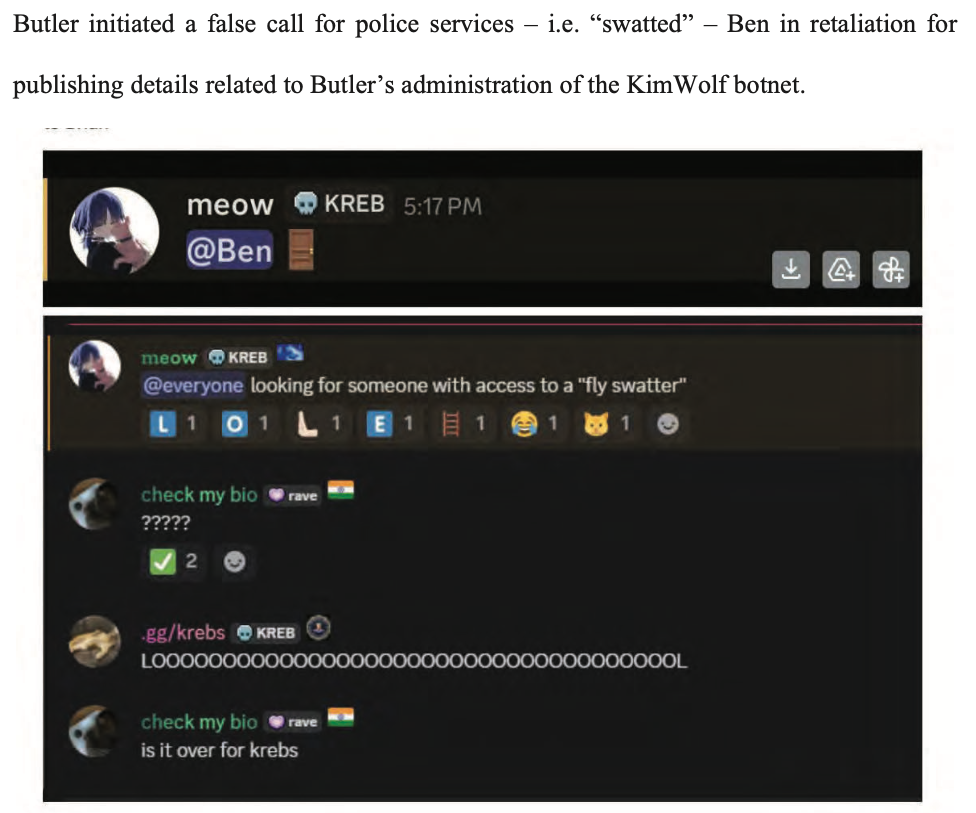
An excerpt from the criminal complaint against Butler, detailing how he ordered a swatting attack against Ben Brundage, the founder of the security firm Synthient.
The government says investigators connected Butler to the administration of the KimWolf botnet through IP address, online account information, transaction records, and online messaging application records obtained through the issuance of legal process. The criminal complaint against Butler (PDF) shows he did little to separate his real-life and cybercriminal identities (something we demonstrated in our February unmasking of Dort).
In April, the Justice Department joined authorities across Europe in seizing domain names tied to nearly four-dozen DDoS-for-hire services, although because of a bureaucratic mix-up the list of seized domains has remain sealed until today. The DOJ said at least one of those services collaborated with Butler’s Kimwolf botnet.
A statement from the Ontario Provincial Police said a search warrant was executed on March 19 at Butler’s address in Ottawa, where they seized multiple devices. As a result of that investigation, Butler was arrested and charged this week with unauthorized user of computer; possession of device to obtain unauthorized use of computer system or to commit mischief; and mischief in relation to computer data. He is scheduled to remain in custody until a hearing on May 26.
In the United States, Butler is facing one count of aiding and abetting computer intrusion. If extradited, tried and convicted in a U.S. court, Butler could face up to 10 years in prison, although that maximum sentence would likely be heavily tempered by considerations in the U.S. Sentencing Guidelines, which make allowances for mitigating factors such as youth, lack of criminal history and level of cooperation with investigators.
This is bug-fix release for 1.29.0.
Feature highlights✨:
.txt import of feed URLs in additional to e.g. OPMLBug fixes highlights 🐛:
UI highlights 🖼:
This release has been made by @Alkarex, @Frenzie, @IEEE-754, @Inverle, @McFev, @ciro-mota, @cweiske, @polybjorn and newcomer @mzl2233
Full changelog:
lib_opml library #8652, #8853,

You’re comparing airfare on your phone, watching prices climb by the hour, when a deal pops up that feels just good enough to grab. The timer’s ticking. The price looks right. You don’t want to miss it.
You’re comparing airfare on your phone, watching prices climb by the hour, when a deal pops up that feels just good enough to grab. The timer’s ticking. The price looks right. You don’t want to miss it.
That moment, when you’re rushing to lock something in, is exactly where scams thrive.
New McAfee research shows that more than 1 in 3 Americans have encountered a travel-related cyberthreat, and 41% of those impacted lost money, often exceeding $500.
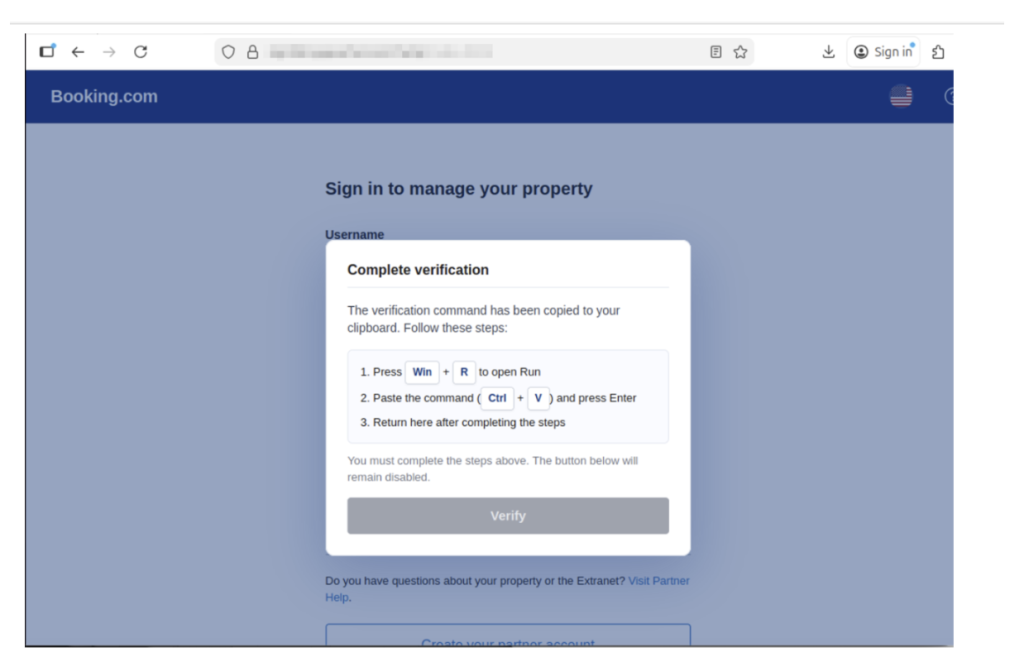
At the same time, rising travel costs and time pressure are pushing people to make faster, riskier decisions. Those are the exact conditions scammers rely on.
That’s where protection has to show up earlier.
McAfee’s Scam Detector lets you check suspicious links, messages, and booking sites before you click, so you can pause and verify instead of giving scammers the edge.
| Travel Scam Type | Key Red Flags | How McAfee Helps |
| Fake travel deals | Prices far below market, pressure to “book now,” sites you’ve never heard of | Scam Detector flags suspicious links and explains why they’re risky, so you can avoid fake deals before you book |
| Fake booking confirmations | Unexpected messages about bookings you didn’t make, mismatched sender details | Scam Detector analyzes messages before you engage, helping you avoid fake confirmations |
| Fake airline/hotel websites | Slight URL changes, poor design, being pushed to pay immediately or off-platform | Safe Browsing helps block risky sites before you enter payment details, reducing the chance of fraud |
| Payment requests outside platforms | Asked to pay via wire transfer, crypto, or direct payment instead of official platforms | Scam Detector flags suspicious payment requests, helping you avoid sending money to scammers |
| QR code scams | QR codes posted in public with no clear source or context | Scam Detector checks QR links before they open, so you don’t land on malicious sites |
| Customer service impersonation | Calls or messages asking for login credentials or payment info | Scam Detector detects deepfake AI audio impersonation attempts, helping you avoid sharing sensitive information |
| AI-generated listings | Photos that look overly polished, details that don’t quite match up | Scam Detector identifies suspicious content patterns, helping you spot listings that aren’t real |
| Public Wi-Fi attacks | Open networks with no password or security prompts | VPN helps protect your data on public networks, keeping your personal information private |
McAfee Labs found that many travel scams work because they look familiar and spread fast.
TripAdvisor was the most commonly impersonated travel app, cloned at roughly three times the rate of other major platforms like Kayak, Expedia, and Booking.com.
In some cases, thousands of scam detections traced back to just a handful of fake apps, showing how quickly a convincing scam can take off when travelers are racing to book.
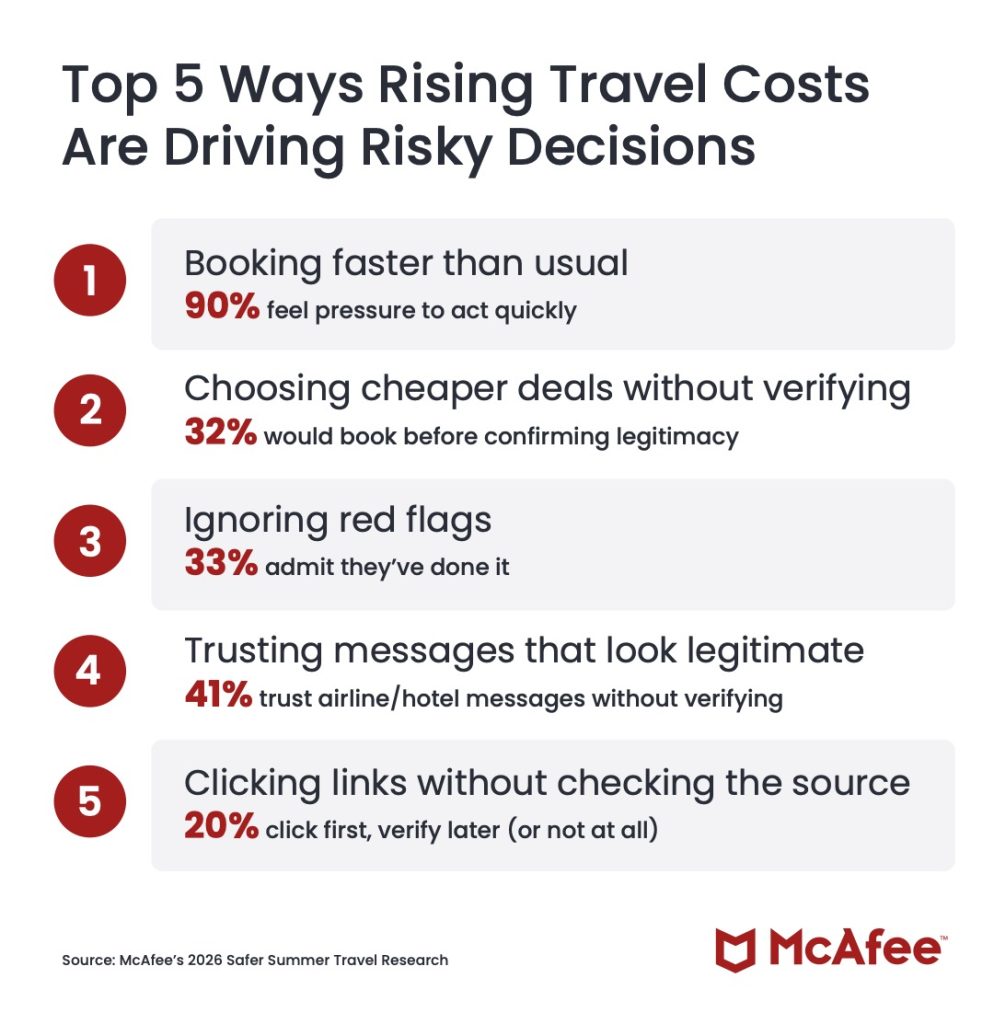
Our 2026 travel survey shows how rising prices and last‑minute pressure are changing traveler behavior, often in ways scammers exploit.
1. Booking faster than usual
90% feel pressure to act quickly
2. Choosing cheaper deals without verifying
32% would book before confirming legitimacy
3. Ignoring red flags
33% admit they’ve done it
4. Trusting messages that look legitimate
41% trust airline/hotel messages without verifying
5. Clicking links without checking the source
20% click first, verify later (or not at all)
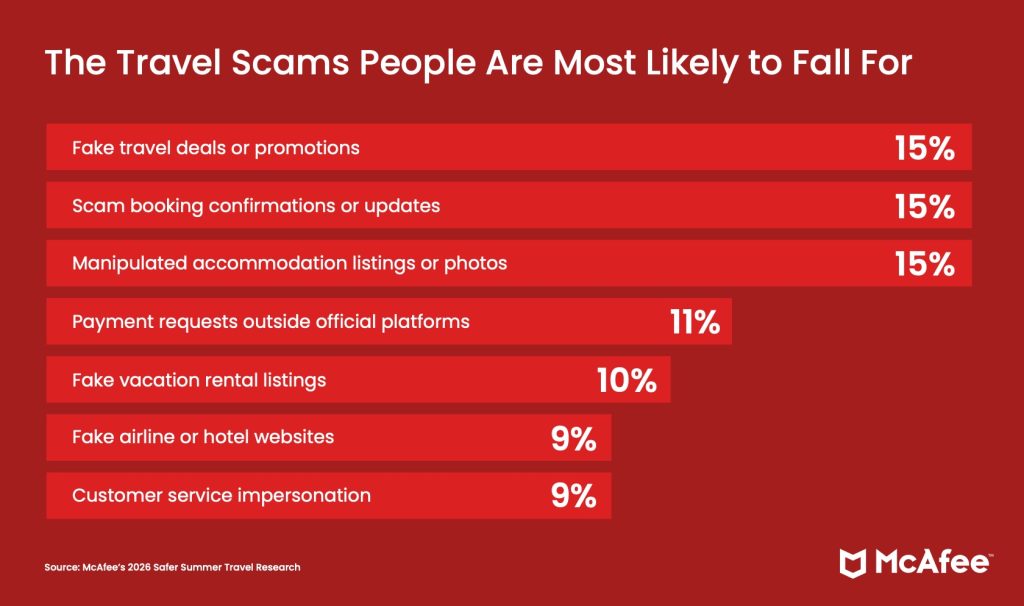
According to our consumer survey findings, those who reported falling for a travel scam said these were the methods scammers used to trick them:
1. Fake travel deals or promotions (15%)
2. Scam booking confirmations or updates (15%)
3. Manipulated accommodation listings or photos (15%)
4. Payment requests outside official platforms (11%)
5. Fake vacation rental listings (10%)
6. Fake airline or hotel websites (9%)
7. Customer service impersonation (9%)
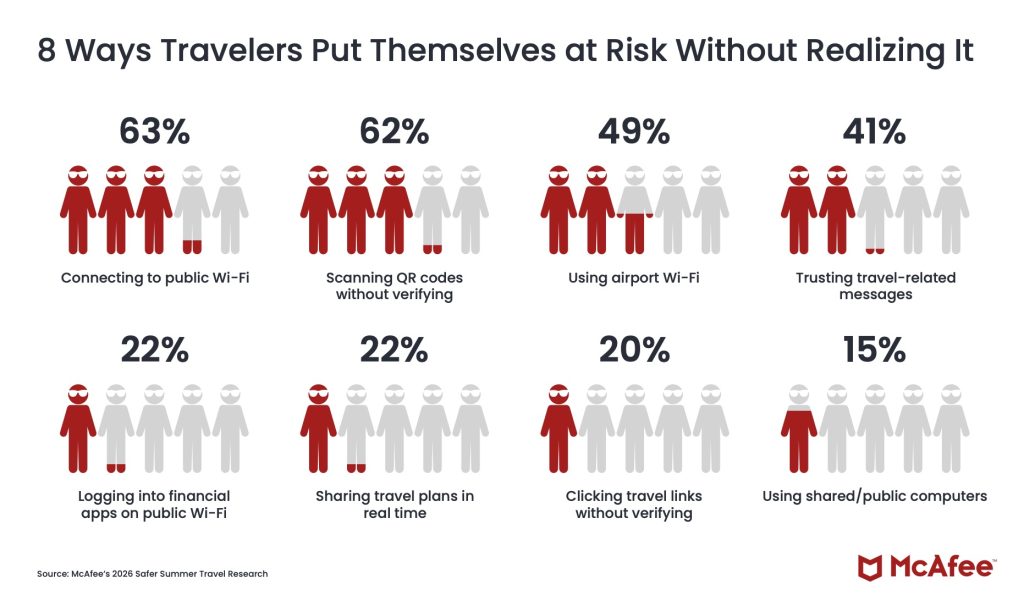
These common traveler behaviors are popular avenues for criminals to steal your information, data, and money.
1. Connecting to public Wi-Fi (63%)
2. Scanning QR codes without verifying (62%)
3. Using airport Wi-Fi (49%)
4. Trusting travel-related messages (41%)
5. Logging into financial apps on public Wi-Fi (22%)
6. Sharing travel plans in real time (22%)
7. Clicking travel links without verifying (20%)
8. Using shared/public computers (15%)
As prices rise and decisions happen in real time, it’s easy to prioritize convenience over caution. But that’s exactly the moment when small checks matter most.
| Stage of Travel | What’s Happening | How McAfee Helps |
| Before You Book | Comparing deals, clicking promotions, booking flights and hotels under time pressure | Scam Detector checks links, messages, and booking sites before you click, helping you avoid fake deals and scam listings |
| During Your Trip | Connecting to public Wi-Fi, scanning QR codes, receiving travel updates and alerts | VPN helps secure your connection on public Wi-Fi, while Scam Detector flags suspicious messages and unsafe links in real time |
| After Your Trip | Accounts remain active, travel data stored across platforms, potential exposure from breaches | Identity Monitoring alerts you if your personal information appears online, helping you act quickly before damage spreads |
With McAfee+ Advanced, multiple layers work together so you’re not left figuring it out after the damage is done.
Spend more time on your vacation, and less time worrying about scammers who want your vacation fund.
The post 1 in 3 Targeted by Travel Scams and Rising Costs are Making it Worse appeared first on McAfee Blog.