The California Department of Education (CDE) announced on October 16, 2026, that unauthorized actors accessed an Educational Testing Service (ETS) server, compromising the educational and demographic records of millions of California public school students. The breach occurred between May 22, 2026, and September 18, 2026, exposing student names, dates of birth, home addresses, disability records, and state assessment scores across three academic years.
While state officials confirmed that Social Security numbers and financial account details were not accessed, exposed personal files elevate the risk of secondary phishing attacks, fraudulent account creation, and child identity theft.
How the ETS Data Breach Happened
Unauthorized actors used compromised login credentials to gain illicit access to a Secure File Transfer Protocol (SFTP) server operated by ETS. Educational Testing Service administers statewide standardized testing assessments for California public schools, including the California Assessment of Student Performance and Progress (CAASPP) and the English Language Proficiency Assessments for California (ELPAC).
ETS identified the unauthorized file access on September 25, 2026, and notified school districts on October 2, 2026, before coordinating a public disclosure with the state. An internal investigation confirmed that intruders copied student files intermittently across a four-month window.
What Student Data Was Exposed in the Breach
The scope of exposed data varies by student, but involves records dating back through the 2023–2024 academic year:
Data Category
Exposed in ETS Breach?
Details
Basic Identifiers
Yes
Full student name, date of birth, home address, and school attended
Academic Identifiers
Yes
Statewide Student Identifier (SSID) and standardized test scores
Demographic & Special Records
Yes
Demographic profiles, disability records, and program eligibility files
Social Security Numbers
No
Confirmed not stored on the compromised SFTP server
Financial & Payment Data
No
No credit cards, banking data, or parent billing files were involved
Parent/Guardian Personal Data
No
Contact information and parent personal records were excluded
Because Social Security numbers were not taken, scammers cannot automatically establish traditional lines of credit overnight. However, bad actors frequently bundle basic demographic data with records from other breaches to assemble synthetic profiles or craft convincing spear-phishing schemes aimed at families.
Warning Signs of Child Identity Theft After the Breach
Data breach exposures involving children often manifest months after the initial intrusion. Watch for these indicators that an affected student’s personal information may be circulating among scammers:
Unsolicited calls, texts, or emails claiming to be from ETS or school officials: Legitimate state agencies will not call or text asking for your child’s Social Security number or payment to receive breach protections.
Credit offers and pre-approved cards addressed to a minor: Children rarely have credit files, so pre-approved cards, loan offers, or rewards enrollments indicate an active file exists.
Government and agency notices in your child’s name: Warning letters from the IRS about unpaid taxes, notifications regarding state benefits, or jury duty summonses for a minor signal identity misuse.
Calls from collection agencies: Debt collectors demanding payment for opened utility accounts, cell phone contracts, or medical services in a student’s name point to fraudulent accounts.
School enrollment or testing discrepancies: Notifications from educational institutions regarding unauthorized transfers, unknown state test submissions, or modified student records.
How to Protect Yourself and Your Child
Take the following concrete defensive steps to protect your child’s personal data from being weaponized:
Activate the state-provided identity protection coverage. ETS is offering two years of complimentary identity monitoring through Experian IdentityWorks. Parents can enroll eligible minor children at Experian IdentityWorks for Minors using the activation code provided in the official CDE breach notification.
Place a credit freeze on your child’s credit file. Federal law allows parents and legal guardians to freeze a credit file for children under 16 at no cost to prevent unauthorized accounts from being opened. Contact each of the three credit bureaus (Equifax, Experian, and TransUnion) directly to request a minor freeze.
Apply a verification test to all breach-related outreach. Scammers exploit news of large breaches to pose as test administrators, district staff, or identity support agents. If someone contacts you seeking account verification, hang up and reach out through the official California Department of Education incident portal.
Monitor your household’s digital accounts. Update passwords across school portal logins, parent-teacher applications, and family email accounts, pairing each with multi-factor authentication (MFA) using an authenticator app.
Check for existing credit files for older dependents. Students who are 18 or older can review their own credit reports for free every week at AnnualCreditReport.com to ensure no accounts have been opened under their names.
What to Do If Your Child’s Information Was Misused
If an unauthorized party uses your child’s personal details to open accounts, secure credit, or claim benefits, take immediate action to limit liability:
Halt contact and refuse demands for payment: Never send funds or negotiate with debt collectors attempting to collect on fraudulent debts opened in a child’s name.
Contact the fraud departments of involved companies: Reach out to the bank, merchant, or utility provider that issued the fraudulent account, notify them of child identity fraud, and demand written confirmation that the account is closed and cleared.
File an identity theft report with the FTC: Submit an official declaration at IdentityTheft.gov. This creates an official Identity Theft Report required by banks and credit bureaus to remove fraudulent records.
Demand immediate credit file purges: Send copies of your FTC Identity Theft Report and proof of minor custody to Equifax, Experian, and TransUnion, requesting the immediate deletion of all fraudulent tradelines and inquiries.
File a police report: Contact your local police department if financial fraud, impersonation, or extortion occurred, and retain the incident report number for your financial documentation.
Maintain complete paper trails: Log all correspondence, including dates, representative names, case numbers, and copies of collection letters.
How to Report the Threat and Stay Protected
Reporting incidents promptly assists regulatory authorities and cybersecurity investigators in tracking down threat actors and stopping systemic abuse. Use these verified channels:
Federal Communications Commission (FCC): Report suspicious caller ID spoofing or phishing robocalls on the FCC Complaints Center.
California Department of Education Support Line: Families with questions regarding the ETS breach notification can contact the CDE assistance line at 833-931-8488.
Safeguarding student records requires active vigilance. By placing credit freezes, enrolling in complimentary monitoring, and questioning unexpected communications, families can minimize the risks associated with school vendor data security incidents.
The best ways to protect your child from identity theft include freezing their credit, limiting exposure of personal information, monitoring for suspicious activity, securing family devices, and teaching safe online habits. Because children often don’t discover identity theft for years, taking preventive action early can help protect their credit, finances, and future opportunities.
Child identity theft is one of the fastest-growing forms of fraud, and many families don’t discover it until years after the damage is done. But child identity theft has surged in recent years, with 38% of U.S. survey participants reporting that a child or family member’s child had been victimized in 2025, jumping from 23% the year prior.
This guide explains how child identity theft happens, what warning signs to watch for, and the eight most effective ways to protect your child’s future.
Key Takeaways
Children are prime targets because their Social Security numbers or national ID equivalents are a blank slate, allowing fraud to go undetected for years.
Data breaches, phishing scams, social media oversharing, and AI-powered fraud are making child identity theft more common and harder to detect.
AI-driven scams are making it faster and cheaper to target families and steal children’s data at scale.
Freezing your child’s credit, monitoring for suspicious activity, and teaching safe online habits are among the most effective protective measures parents can take.
What is Child Identity Theft?
Child identity theft is a crime in which someone steals a minor’s personal information, most commonly the minor’s name, date of birth, and Social Security number (SSN) or equivalent national identifier, to commit fraud. The thief might open credit card accounts, take out loans, rent housing, file fraudulent tax returns, or claim government benefits, all in the child’s name. A 2021 Javelin Strategy study found that this crime affects one in every 50 children and costs U.S. families nearly $1 billion annually.
Why Child Identity Theft Is So Dangerous
The crime is made uniquely dangerous by the silence. Because children typically do not start applying for credit until they are 16 to 18, a thief can have more than a decade of undetected activity. As a result, by the time the victim becomes an adult, they may face:
Damaged credit scores
Debt collection notices
Loan denials
Difficulties renting housing
The crime is not confined to the United States, either. One documentary tells the story of Renata Furst Galvão, a native of Brazil, whose identity was stolen at age six and used to amass more than $400,000 in debt.
How Criminals Get Access to Children’s Information
To protect your child effectively, it helps to understand exactly who is targeting them, how they are getting in, and why the threat is accelerating. Even the most security-conscious household can be exposed through no fault of its own. In reality, information is often exposed through organizations that collect and store children’s data.
Common sources include:
Data breaches at retailers, healthcare providers, schools, and financial institutions could expose children’s information alongside adults’.
Social-engineering scams and phishing attacks may target parents directly to extract children’s details.
Social media profiles are prime targets for identity thieves to monitor, which is why a child posting their birthday, school name, and city in separate posts creates genuine risks. Minimize the personal details shared online and in photos.
Online games and apps that over-collect data, including a child’s full name, birthdate, and town, create additional opportunities for personal data exposure.
New Risks: AI Scams and Synthetic Identities
A December 2025 survey found that reports of ID theft rose from 43% in 2024 to 78% in 2025, a single-year spike that reflects how AI-powered tools have made it faster and cheaper for criminals to generate convincing phishing messages and fake identities at scale.
Synthetic identity fraud is particularly dangerous for children. It pairs a real Social Security number belonging to a minor unlikely to use it anytime soon with a fictitious name and address. The resulting fake identity can then build a credit history, take out loans, and disappear before anyone connects the dots.
Warning Signs Your Child’s Identity May Be Stolen
Catching this crime early makes the recovery process far less painful. Knowing what to look for means you will not dismiss the very clues that trigger a fast response.
Unexpected Mail, Bills and Collection Calls
The most common early indicators arrive in your mailbox or by phone, including:
Pre-approved credit card offers in your child’s name
Collection agencies calling to speak with your child
Court notices or bills for accounts your child never opened
Any business mail addressed to a young child should trigger an immediate investigation.
Many families first discover the theft during pivotal life moments. Examples include:
A teen may be denied a learner’s permit due to fraudulent driving violations.
A young adult may be denied an apartment because of unpaid debt on their credit report.
Stolen Social Security numbers can interfere with access to government benefits.
Unexplained Credit Activity
Children typically should not have a credit history, so potential warning signs of identity theft include:
A credit report exists under your child’s name
Credit accounts appear that your family never opened
Loan applications are associated with your child’s Social Security number
Debt appears on your child’s credit file
If your child has a credit record before they are old enough to use credit, it may indicate identity theft.
The 8-Step Protection Plan for Parents
You can follow these steps while seeking guidance from financial educators, credit authorities, and consumer protection experts. Start small by choosing two or three today, then build from there.
Step 1: Check and Freeze Your Child’s Credit
A credit freeze is one of the most effective ways to protect your child from identity theft. If your child is under 16, request a free credit freeze from Equifax, Experian, and TransUnion. This prevents anyone from opening new financial accounts in your child’s name without your authorization. Once in place, the freeze remains active until you ask the credit bureau to temporarily lift or remove it.
Because minors typically don’t have established credit files, the process for placing a freeze differs from that for adults. Each of the three major credit bureaus provides specific instructions for parents and guardians. Follow the guidance from Experian, Equifax, and TransUnion to place a freeze on your child’s credit file.
Step 2: Enable Fraud Alerts and Social Security Reports
In addition to a credit freeze, it’s smart to watch for signs that someone is using your child’s identity. Ensure that you:
File a fraud alert with each credit bureau to prompt verification checks if someone attempts to open an account in your child’s name.
Request an earnings report from the Social Security Administration to confirm whether wages are being reported under your child’s SSN.
Once your child is old enough to have a legitimate credit file, teach them to stagger their use of free credit reports from the AnnualCreditReport website, checking one bureau every four months.
Step 3: Educate Your Kids about Identity Theft & Private Information
In an honest, age-appropriate conversation, explain to them that personal information is the master key to their financial future and should not be shared with online strangers. Role-playing helps: ask your child what they would do if someone they met in a game asked for their full name and home address. Empowered kids are less likely to overshare and more likely to alert you when something feels off.
Step 4: Get Fierce about Protecting Your Child’s Data
Draw a very thick line around your child’s details. Reiterate that sharing them should be limited only when truly necessary, such as school enrollment or medical forms, and only with verified institutions. Ask why it is needed, how it will be stored, and if an alternative identifier is acceptable. Keep important documents in a locked safe and shred papers with your child’s information before disposal.
Step 5: Lock Down Devices, Accounts, and Online Habits
Talk with your kids about safe internet habits. Instruct them to stay skeptical of quizzes, free offers or apps, and unbelievable promos that request personal details. Set their social media accounts to private and limit follower or friend lists to people they know in real life. Use strong, unique passwords for family accounts and enable multifactor authentication on email, school portals, and social media apps used by older children.
Step 6: Monitor for Early Warning Signs
Regularly check your household mail for notices addressed to your child. If you spot anything suspicious, contact the company directly using the contact details on its official website. Do not call the number printed on the suspicious document, as it could redirect you to the thief who sent it. Consider using an identity monitoring service that scans for your child’s data in data breaches or on the dark web and alerts you when their information surfaces.
Step 7: Get Full-Device and Network Security
Many identity theft incidents start with a compromised family device. To reduce this risk, keep operating systems, browsers, and apps fully updated. Secure your home Wi-Fi with a strong password and WPA3 encryption to prevent data interception. Comprehensive security software, such as McAfee+ Family Plans, can help you block malware, keyloggers, and phishing sites that harvest personal data from every device in your home, including the tablets and phones your children use most.
Step 8: Act Quickly If Theft Happens
If you discover or suspect your child’s identity has been stolen, immediately contact the company where the fraudulent account was opened, close the account, and request written confirmation that your child bears no liability. Report the theft to IdentityTheft.gov, follow the personalized recovery plan, and file a police report to create an official record that will help resolve disputes with creditors.
Next, contact each credit bureau to cancel fraudulent accounts, inquiries, and collection notices linked to your child’s SSN. Keep detailed records of every call, letter, and case number throughout the process. Reporting the incident to the authorities helps your family recover and supports broader enforcement efforts that protect other families.
Final Thoughts
Child identity theft is a fast-growing, serious threat worldwide, but it is also one of the more preventable forms of fraud when families take proactive steps early. Start this week by spending 10 minutes to safely lock away your child’s physical documents, then call the major credit bureaus to request a freeze on your child’s credit. Build toward the full eight-step plan over the next month to close every door that leads to potential harm.
Beyond the 8-step sprint, add a recurring data safety day to your family calendar each year to recheck credit freezes and fraud alerts, review your children’s online accounts and platform settings, update devices and passwords, and discuss emerging threats. A family that combines strong protective habits with smart security tools is a much harder target for any kind of cybercrime.
It’s 10 p.m. on a school night, but your child is still watching YouTube Shorts, one after another, and the feed never ends. YouTube is one of the most widely used video platforms among children. A 2025 Pew Research Center study found that about 85% of parents allow their children to watch videos on YouTube, including 51% who permit daily use.
If your children are among the millions using YouTube, this article will help you balance your child’s screen time on the platform, filter out inappropriate content, and keep their data safe.
Key Takeaways
Even kid-friendly content on YouTube can include inappropriate themes, aggressive marketing, or low-quality videos designed solely for engagement, not learning.
Choosing the right YouTube experience for your child’s age is essential. Select from YouTube Kids, supervised accounts on the main YouTube, or regular YouTube.
In January 2026, YouTube introduced new parental controls for Shorts, allowing parents to set time limits or block short-form videos entirely for supervised accounts.
The most effective approach combines smart tool settings, including content filters, time limits, and Restricted mode, with co-viewing and open conversations within families.
Is YouTube Safe for Kids?
YouTube can be safe for kids, but it isn’t automatically safe. While the platform offers educational videos, creative content, and entertainment for children of all ages, kids can still encounter inappropriate videos, cyberbullying, misleading content, and excessive screen time if parental controls aren’t enabled. For most families, YouTube Kids, supervised accounts, parental filters for YouTube, and regular monitoring provide the safest experience.
What Parents Need to Know about YouTube
YouTube has become a primary platform where children spend hours each week being entertained, getting help with their homework, and following social trends such as challenges and Shorts. They shift seamlessly between devices: first watching on the TV in the living room, then switching to a tablet in their bedroom, and then pulling it up on a phone in the car.
Unfortunately, some parents underestimate how quickly YouTube’s recommendation algorithm can steer kids from age-appropriate content to more intense, commercial, or borderline inappropriate videos. Recommendation algorithms are primarily designed to maximize engagement and viewing time, which may not always align with age-appropriate content. One minute, your child is watching an educational science video. Three autoplay cycles later, they’re watching an unboxing channel where an adult screams at toys for 20 minutes straight.
What Are the Biggest YouTube Safety Risks for Kids?
While YouTube offers everything from educational content to entertaining videos for kids, no video-sharing platform is completely risk-free. YouTube carries risks that many parents don’t fully understand until problems arise at home. Understanding these challenges is the first step toward helping children build more balanced digital habits.
Inappropriate and Low-Quality Content
Automated filters aren’t perfect. Despite explicit policies banning deceptive, sensational, and clickbait content on YouTube Kids, inappropriate content can slip through. You might find cartoon violence, endless unboxing videos dressed up with science or learning keywords, or content that promotes unrealistic body images. In addition, many videos aimed at children encourage risky physical challenges, harmful pranking, and consumerism.
If your child is gravitating toward such content, use it as a teaching moment. Watch a few videos together and ask your child what they like about them. Then gently guide them toward higher-quality alternatives.
Child development experts warn that this type of content, when consumed in large doses, can crowd out creative play, may contribute to a lack of focus, and reduce time spent on activities that foster creativity and critical thinking.
YouTube Shorts and Excessive Screen Time
Short-form vertical video like YouTube Shorts has become a particular source of concern for parents, educators, and mental health professionals. The format’s infinite scroll and rapid-fire delivery make it engaging for young viewers, but researchers and child safety advocates have raised concerns that endless-scroll feeds may cause sleep disruption and compulsive viewing habits.
In addition, pediatric health organizations, including the American Academy of Pediatrics, are concerned that excessive screen time can mean fewer hours spent reading, playing outdoors, having face-to-face conversations, or engaging in imaginative play.
Cyberbullying and Unsafe Interactions
Children using standard YouTube accounts may encounter toxic comments, harassment, or cyberbullying. While younger children are less likely to engage with comments, older kids and teens often participate in online discussions that can expose them to negative interactions.
If your child experiences online harassment:
Encourage them not to respond to aggressive comments
Teach them how to report online bullying
Use YouTube’s reporting tools to block abusive users
Save evidence of serious threats or harassment
Learning how to stop a cyberbully starts with open communication and making sure children know they can come to a trusted adult when something online feels wrong.
Data, Privacy, and Advertising
YouTube Kids collects data about your child’s viewing habits and device, including IP addresses, to power recommendations and serve ads. Although regulations such as the Children’s Online Privacy Protection Act (COPPA) in the U.S. limit personalized advertising for children, many parents remain uneasy about the amount of data collected.
Recommendation algorithms can also narrow what kids see, showing them endless variations of the same content type. A child who watches one slime video might end up in a loop of nothing but slime videos. This creates a repetitive, passive viewing experience that doesn’t expose children to diverse ideas or interests.
Red Flags or Warning Signs Parents Should Watch For
A child doesn’t need to view harmful content to develop unhealthy YouTube habits. Consider reviewing your family’s YouTube settings if you notice:
Behavioral Changes
Consider reviewing your family’s YouTube settings, screen time limits, and online safety practices if you notice any of the following:
Meltdowns, arguments, or persistent bargaining for “just one more video” when it’s time to stop watching
Sleep disruption, including difficulty falling asleep, waking up tired, or sneaking devices at night to watch videos
Declining interest in offline activities, such as sports, reading, hobbies, or time with friends and family
Secretive behavior, such as hiding screens, clearing watch history, or becoming defensive when asked what they’re watching
Slipping grades or incomplete homework due to excessive time spent watching videos or YouTube Shorts
Appearing unusually anxious, upset, or withdrawn after spending time on YouTube
Receiving mean comments, harassment, or unwanted attention on their uploaded videos
Becoming overly attached to content creators and speaking about them as if they are personal friends
Reluctance to discuss online interactions, comments, or messages from other users
These behaviors don’t necessarily mean your child is watching harmful content. However, they may indicate that YouTube is displacing other important activities, that screen time has become excessive, or that your child is experiencing uncomfortable online interactions.
For older children and teens, changes in mood, secrecy around devices, or sudden reluctance to use YouTube may also be signs of cyberbullying. Creating a judgment-free environment can make it easier for children to discuss negative online experiences and seek help when needed.
If you notice several of these warning signs at once, it may be time to reassess screen time limits, review the watch history together, and discuss how to interact safely with others online.
Choose the Right Experience for Your Children
YouTube offers three distinct experiences for families, and choosing the right one for each child matters more than any other setting you’ll configure:
YouTube Kids
YouTube Kids is a standalone app designed specifically for children. It offers three age-based profiles designed to pull up appropriate content for young viewers:
Preschool (4 and under): This is the most restrictive mode, featuring videos that promote creativity, playfulness, learning, and exploration.
Younger (5-8): This mode expands to include songs, cartoons, crafts, and content for early elementary-aged children.
Older (9-12): In this mode, the app features music videos, gaming content, science videos, and vlogs appropriate for tweens.
Within each profile, parents can choose between Curated mode and All of YouTube Kids mode. Curated mode includes only channels verified by YouTube’s human reviewers, making it the safest option for younger children. All of YouTube Kids mode includes more videos approved by automated filters, increasing the chance that inappropriate videos may slip through.
Disabling the search function in YouTube Kids limits your child to content on the home screen, which is an excellent option for very young children who don’t yet need the breadth of YouTube’s catalog. You can also block specific channels and review your child’s watch history to monitor what they’re watching. Overall, the app offers additional protections compared with the standard YouTube experience.
Supervised Accounts on Main YouTube
Supervised accounts on the main YouTube platform serve as a middle ground for kids who’ve outgrown YouTube Kids’ toddler aesthetic but aren’t ready for the unfiltered internet. These accounts, managed through Google Family Link, let parents:
Choose from three content settings: Explore for ages 9+, Explore More for ages 13+, and Most of YouTube for ages 18+
Enable or disable the search function
Manage which features the child can access, including comments, live streams, and community posts
Benefit from stricter community guidelines and protections for users under 18
After receiving feedback from parents and experts, the platform introduced controls to block Shorts or to set daily time limits for supervised accounts. The new controls also let parents:
Customize Bedtime reminders that prevent access during late hours when screens should be off
Enable Take a Break reminders, which prompt the child to pause after extended viewing sessions
These controls apply across all devices where the child is signed in and are designed to prevent children from disabling them without parental approval. In addition, the streamlined sign-up process makes it easier for parents to create a supervised account and switch between their own and their child’s account within the mobile app.
Regular YouTube
Regular YouTube is the full, unrestricted platform. If your child has an adult account, you’re relying entirely on their judgment and whatever settings they choose to enable. For younger teens, this can be risky without clear family agreements and monitoring.
Understanding YouTube Age Verification
YouTube uses account information and age-verification systems to determine whether a user should be treated as a child, teenager, or adult. Age verification determines what content users can access, what ads they see, and which safety features YouTube automatically applies.
How Does YouTube Age Verification Work?
When someone creates a Google account, they provide a birthdate that YouTube uses to determine age. In some regions, YouTube may also use account signals to estimate whether the user is under 18.
If YouTube determines that a user is under 18, the platform may:
Restrict age-restricted videos
Limit personalized advertising
Provide additional recommendation safeguards
Enable reminders to take breaks
Apply additional teen safety protections
What Happens If YouTube Thinks You’re Under 18?
If YouTube identifies a user as under 18, additional protections may automatically apply. These may include restrictions on mature content, changes to recommendations, reduced ad personalization, and digital well-being features designed for younger users.
How to Set Parental Controls on YouTube
YouTube offers several parental control options to help families manage content, screen time, privacy, and interactions. Most of these controls can be configured through Google Family Link, YouTube Kids, or YouTube’s built-in safety settings.
Parents who want to enable parental controls on YouTube, add a parental lock to the YouTube app, or create a more age-appropriate experience can explore the following options:
Parental Control
What It Does
Supervised Accounts
Allows parents to select age-appropriate content settings and manage certain YouTube features.
YouTube Kids
Provides a child-focused experience with age-based content settings and additional parental controls.
Search Controls
Lets parents limit or disable search to reduce exposure to unintended content.
Channel and Video Blocking
Allows families to block specific channels or videos they don’t want children to access.
Restricted Mode
Helps filter potentially mature content from search results and recommendations.
YouTube Shorts Controls
Lets parents manage access to Shorts and set viewing limits on supervised accounts.
Screen Time and Bedtime Controls
Allows families to set YouTube time limits, bedtime reminders, and viewing schedules.
Comment and Community Features
Gives parents greater control over interactions with other users.
For younger children, families may choose YouTube Kids with Search disabled to provide a more curated content experience. Older children and teens may benefit from supervised accounts that offer greater independence while still giving parents visibility and control.
Google regularly updates its parental control tools and settings. For the latest information on available options and setup guidance, visit Google’s Family Help Center.
Building a Safer YouTube Setup at Home
After choosing the right experience for your child, you can start configuring YouTube’s settings for added security.
For YouTube Kids
Choose the correct age profile and content mode during the app setup.
Disable search if you want to limit viewing to home screen recommendations only.
Block specific channels if you notice your child repeatedly watching low-quality or overly commercial content.
Turn off autoplay to prevent endless video chains.
Review your child’s watch history weekly to spot any concerning patterns.
For Supervised Accounts
Open Google Family Link and set up a supervised YouTube account for your child.
Choose the appropriate content level, starting conservatively. You can always grant more access later.
Set time limits for Shorts or block them if your child struggles with self-regulation.
Configure Bedtime reminders to enforce screen-free hours, especially before sleep.
Enable Take a Break reminders to interrupt binge-watching sessions.
Keep search disabled initially, and enable it only when your child demonstrates good judgment.
Review and adjust settings every few months as your child matures.
Any YouTube Account Your Child Might Access
Turn on Restricted Mode, which uses community feedback, metadata, and other signals to hide videos that may contain mature content. To lock this mode so that your child can’t disable it, go to the Google Family Link.
Disable autoplay and turn off notifications to reduce passive consumption.
Review the privacy settings to make sure that your child’s uploads, if allowed, aren’t publicly visible.
Co-Viewing and Conversations
Settings and filters are necessary, but they’re not sufficient. Research on children’s media use consistently shows that the best outcomes result from combining tools with active parental engagement. This means:
Co-viewing: Sit with your child regularly and watch their favorite channels together. Ask what they like about the content and use it as an entry point for conversations about advertising, authenticity, and what’s real versus staged.
Talking about what they see: If your child watches gaming videos, talk about the difference between games and reality. If they watch beauty influencers, discuss how lighting, makeup, and editing can create unrealistic expectations.
Modeling good habits: Children learn by watching you. If you’re constantly on your phone or scrolling through videos during family time, they’ll internalize that as normal. Set family screen-free zones and times that apply to everyone, including adults.
Creating a media plan: Sit down together and agree on daily or weekly screen time limits, acceptable content types, and what to do if they encounter something that makes them uncomfortable. Tools like the American Academy of Pediatrics media plan can help structure this conversation.
Final Thoughts
Recent years have brought improvements to YouTube as an engagement tool for children. Short-form video time limits, supervised accounts with meaningful controls, and growing awareness among parents and educators of the stakes mean we are better positioned to create safer, more balanced digital experiences.
Combine these efforts with another layer of comprehensive protection tools, such as McAfee+, to help reduce exposure to threats that may bypass platform-level filters. Together, these measures support a more thoughtful and safer online experience for children.
When you scroll through your teen’s iPhone during a casual check-in, you might see messaging apps, a few games, school tools, maybe TikTok. Everything looks normal. But what if some of the apps your child uses most aren’t showing up at all? What if that innocent-looking calculator icon is actually a vault for hidden photos, private chats, and secret social media accounts?
This isn’t science fiction or paranoia. Teens now have powerful tools to keep entire corners of their digital lives invisible to parents. Starting with iOS 18, which rolled out in late 2024, iPhone users can now natively lock and hide apps from the Home Screen, search results, and even from obvious parts of the App Library without biometric authentication.
If you suspect your child or teen is hiding apps and engaging in potentially harmful online activities, you may find this guide helpful. We’ll discuss the current digital landscape that threatens children and methods for checking for and uncovering hidden apps. More importantly, we will share insights on how to start conversations with your teens about the risks of hiding apps, and tips on how to keep your child safe from predators and other cybercriminals.
Key Takeaways
Teens hide apps for many reasons, including seeking normal privacy, avoiding conflict over screen time, and concealing genuinely risky behavior such as cyberbullying, sexting, and contacting strangers.
iOS 18’s native hiding features allow users to lock apps behind Face ID and move them to a hidden folder, making casual parental discovery much harder.
Parents can check for hidden apps by reviewing iPhone Storage settings, Screen Time reports, and the App Library’s Hidden folder.
The healthiest approach blends understanding how hiding works with ongoing, honest family conversations and smart use of security tools.
Why Kids and Teens Hide Apps on iPhone
The ability to conceal apps on iPhones has expanded with iOS 18’s native features and disguise vault apps. Teens worldwide can now make entire app categories invisible to parental checks. Before exploring how to uncover hidden apps, it’s important to first understand why children do it. When we grasp their motivations, we are better positioned to respond constructively rather than punitively.
Privacy from Parents and Peers
A study from the Pew Research Center shows that about half of parents in the U.S. look through their teen’s phone. But many teens use hidden apps to keep parts of their social life private: conversations with crushes, embarrassing photos, fan fiction, fake Instagram or finsta accounts where they share unfiltered thoughts.
These patterns reflect global trends as smartphones become central to adolescent identity worldwide, according to Nexus Teen Academy. Hiding isn’t always about danger. Often it’s about autonomy and the universal teenage desire for private space.
Avoiding Screen Time Limits and Parental Controls
In its survey, Pew Research also revealed that around 47% of parents in the U.S. set screen time limits. To circumvent this restriction, some teens find workarounds such as hiding apps to bypass Screen Time, keeping backup social apps off the approved list, or using web browsers instead of installed apps.
Hiding Risky or Sensitive Content
Some teens hide apps or use secondary accounts to disguise risky content or activities they may be involved in, including for sexting, dangerous challenges, or contacting strangers or certain communities. Vault apps may store explicit images or bullying screenshots that teens are ashamed to show adults. Hiding removes early warning signs that could prompt intervention before situations escalate.
The Risks of Hiding Apps
Hidden apps are just one piece of a larger digital reality in which teens spend hours each day online, often beyond adult supervision. To respond effectively, you need to recognize the prevalence and hazards of this trend.
Screen Time and Conflict in Families
Studies show that teens globally spend around 7 hours and 22 minutes looking at device screens daily, 4.8 hours of which are on social media. However, too much time spent on social media has been linked to poor mental health, including symptoms of depression and anxiety. Long screen time was linked to conflict in 38% of families, another survey found.
Mental Health Concerns
When screen time creates constant conflict in the family, hiding apps can feel like a way to keep the peace for teens. This impulse can hide situations that are genuinely harmful to children’s and teens’ mental health and overall well-being. Pediatric health organizations note that unsupervised, high-intensity, and excessive use of social media is linked to increased anxiety, depression, sleep disruption, and body image issues.
Contact with Strangers and Harmful Communities
Hidden messaging apps may contain conversations with unknown contacts, including adults with predatory intentions, communities that encourage eating disorders or self-harm, and secret accounts that host cyberbullying.
As your child or teen removes visibility of their online activities, you as a parent lose an early-warning system to late-night usage spikes, obsessive checking, or mood changes related to specific apps, signs that could help you intervene before a crisis develops.
How to Hide Apps on iPhone
Understanding how apps are hidden will help you know what’s possible and where to look.
Apple’s Hidden Apps Feature in iOS 18
In September 2024, Apple introduced a feature where the app icon and name vanish from the Home Screen entirely, moving into a special Hidden folder in the App Library that requires biometric or passcode authentication to access. These hidden apps won’t appear in Spotlight search, Siri suggestions, or standard app lists. While this feature has legitimate privacy use for adults to protect critical apps such as banking, email, or social media in case their device is lost or stolen, some kids have misused it to make entire categories of apps invisible without any technical workarounds.
Older Tricks Kids Still Use
Before iOS 18, tech-savvy teens found creative workarounds. They could remove apps from the Home Screen to appear only in the App Library, bury them in deep folders, or use the Shortcuts app to change app icons and names, making social apps look like utilities labeled “Tools” or “Notes.”
Calculator and Utility Vault Apps Explained
App stores host dozens of apps that look innocent but serve as secret lockers. Known as vault apps, these masquerade as calculators, music players, or utilities, but hide a private space filled with photos, videos, or messages. Some vault apps require multiple passwords: the first opens a decoy vault with harmless content, while the second unlocks the real stash. Others include stealth features like auto-closing when flipped, photographing wrong-code attempts, or sending fake error messages.
How to Find Hidden Apps on iPhone
Even when apps are hidden from view, they don’t disappear entirely from the device. Knowing where to look can help you get a clearer picture of what’s actually installed on your child’s iPhone.
Check iPhone Storage
To find hidden apps on your teen’s phone, you can start by doing it the old-fashioned way. Go to Settings > General > iPhone Storage. Legitimate calculators or flashlights typically use under 30 MB. A calculator consuming 200 MB or more is likely storing content. Vault apps still report storage usage and usually appear in Screen Time reports unless tracking is disabled. This gives you a concrete detection technique without advanced skills. It’s not foolproof, but it’s a useful starting point.
Review the Hidden Folder in App Library
Open the App Library by swiping left past your last Home Screen page. Scroll all the way down. If any apps are hidden, you’ll see a Hidden section, but accessing it requires authentication. If your teen has set up Face ID, you’ll need their cooperation or their passcode to view this folder.
Analyze Screen Time Reports
Go to Settings > Screen Time > See All Activity, then tap into specific days or weeks and scroll through the Apps section. If your teen uses an app heavily, the total hours will likely appear in usage reports even if the app is hidden from the Home Screen. Keep in mind that users can turn off Screen Time tracking for individual apps, but many teens don’t think to do this, making it a useful secondary check.
Healthy Ways Parents Can Respond to Hidden Apps and Digital Secrecy
Very tech-savvy teens can turn off Screen Time, use web versions of apps in private browsers, or delete vault apps before checks and reinstall them after. Technical detection is a conversation starter, but it won’t address the root cause. The goal isn’t to win in an arms race against your child, but to build an environment where hiding feels less necessary.
Start with Conversations
As a parent, it is natural to check your teen’s phone, even as health organizations urge more dialogue about social media risks. But your teen may worry that you will overreact or judge them harshly for normal experimentation. Resolving this tension requires conversation, not just monitoring.
Frame it as collaborative. Explain your concern about certain apps: cyberbullying, predatory strangers, self-harm content, and scams targeting young people. Ask what they like and dislike about their online spaces and why they feel pressure to hide things. Explain that you’re supporting their safety, not invading privacy. If your teen trusts that distinction, they’re more likely to disclose risky situations.
Set Clear, Age-Appropriate Digital Rules
Create a written family tech agreement that covers specifics: which apps are allowed at which ages, whether vault apps are permitted, the process for joint monthly check-ins rather than surprise raids, and consequences for breaking the rules.
Adjust expectations as kids age: A 13-year-old and a 17-year-old need different levels of autonomy. Younger teens might agree to open-phone policies, while older teens earn more privacy with clear red lines around illegal and harmful content, or contact with unknown adults. When rules are clear and mutually agreed on, teens feel respected and are more likely to follow them.
No locking or hidden apps in Family Sharing: Kids aged 13 to 17 in a Family Sharing group can lock or hide an app. However, a parent or guardian in the group can still see which apps were installed and how much time they were used, and restrict access to them using Screen Time.
Use parental control tools: Consider a comprehensive solution that includes parental controls, which can help your children build healthy digital habits by allowing you to monitor their usage, set limits, and even track their whereabouts.
Recognize the Red Flags
Hidden apps alongside sudden mood changes, withdrawal, secretive behavior, school performance drops, or sleep pattern changes could signal something serious. If you notice these patterns, reach out to school counselors, your child’s pediatrician, or a mental health professional. The goal is early intervention, not punishment. Kids in these situations need help, not sanctions.
Final Thoughts
The ability to hide apps on iPhones has expanded dramatically with iOS 18’s native features and vault apps. While this capability has legitimate privacy use for adults, teens could misuse it by making entire app categories invisible to casual parental checks.
But kids hiding apps are just a symptom, not the root problem. When parents focus solely on finding every hidden app, it can erode trust and push kids to hide even more cleverly. The most effective response blends technical awareness and relationship work.
Have a calm conversation with your child about online privacy and safety. Lead with genuine interest and share concerns openly. Next, collaboratively review the Screen Time and iPhone Storage reports. If you find something unexpected, respond with curiosity, not anger.
Finally, create clear, age-appropriate family agreements about phone use and privacy boundaries. Revisit them as your child grows. Make space for private corners of their digital life while maintaining firm red lines around illegal content, contact with strangers, or harmful material.
Security tools such as McAfee+ Family Plans can support your children’s digital safety by allowing you to block harmful content, manage screen time, and monitor their location. The goal isn’t perfect control. It’s ongoing communication, smart boundaries, and enough visibility to catch warning signs early.
Labor Day weekend means sales. And if you spend any time on Facebook, Instagram or TikTok, some of the biggest discounts may find you before you even start shopping.
That convenience comes with a catch: Not every deal in your feed is really from the brand it appears to be.
Scammers can create polished social media ads that impersonate familiar retailers, advertise steep discounts and send shoppers to convincing lookalike websites. According to the Federal Trade Commission, nearly 30% of people who reported losing money to a scam in 2025 said that it started on social media. And the reported losses hit a whopping $2.1 billion last year.
So before a Labor Day “80% off” deal stops your scroll, give it a second look.
How Fake Social Media Shopping Ads Work
A fake shopping ad often starts with something completely ordinary: a product you actually want.
Maybe it’s sneakers from a familiar brand. Patio furniture you’ve been researching. A handbag, grill or appliance marked down for Labor Day.
The ad may use the real company’s logo, product photography and branding. Click it, and the website can look remarkably similar to the retailer’s actual site.
That’s the trick.
This is a form of brand impersonation: A scammer copies the appearance of a company people already know and trust. Instead of convincing you to trust an unfamiliar store, the scammer borrows the reputation of a familiar one.
Sometimes these ads lead to completely fake storefronts. Other times shoppers receive counterfeit products, something dramatically different from what they ordered or nothing at all.
The FTC recently warned consumers specifically about social media ads advertising brand-name products at unusually low prices. And the problem isn’t limited to one platform. A convincing ad can reach you wherever you scroll.
Here’s an example of a scam Louis Vuitton website previously detected by McAfee. Users get an ad on social media, and land on a realistic-looking shopping site. But it’s not the real vendor.
She Thought She Bought $800 Patio Chairs for $135
One shopper who shared her story with McAfee learned just how convincing these scams can be.
A few years ago, Jen was scrolling through Facebook when she spotted an ad for the exact Wayfair patio chairs she and her husband had been considering. Normally around $800, the chairs were advertised at 80% off — just $135 with free shipping.
She clicked.
The experience looked enough like Wayfair that she continued with the purchase, even though a few things started to feel strange. A new tab opened when she tried to buy the chairs. The checkout mentioned PayPal even though she was using her credit card. Then she learned the order would be shipping from China and could take six to 12 weeks.
When she checked her credit card, the charge wasn’t from Wayfair. It appeared in Chinese characters.
Weeks later, a package finally arrived.
It wasn’t a set of patio chairs. Inside the small package was a ceiling-fan chain with a cheap ring.
Her credit card company eventually reversed the charges. But the experience illustrates something important about fake shopping ads: You don’t necessarily land on an obviously fake website filled with misspellings and broken images. A scammer’s goal is to make the experience feel normal long enough for you to complete the purchase.
7 Signs a Social Media Ad or Shopping Site Could Be Fake
Before buying something you find through Facebook, Instagram, TikTok or another social platform, look for these warning signs:
1. The discount is dramatically better than everywhere else.
A legitimate sale can be generous. But if one ad offers a popular $800 product for $135 while reputable retailers are nowhere close, investigate before buying.
2. The website address doesn’t match the retailer.
A fake site can copy a logo much more easily than it can copy a company’s official domain. Look carefully for extra words, misspellings or unusual endings in the web address.
3. Clicking takes you somewhere unexpected.
Watch for redirects, new tabs or checkout pages on a different domain. A change doesn’t automatically mean fraud, but it’s a reason to verify where you are before entering payment information.
4. The checkout process feels off.
Pay attention when the payment method, merchant name or checkout experience doesn’t match what the site told you to expect.
5. There’s pressure to buy immediately.
Countdown timers and “only two left” warnings can push you to act before checking the seller. Urgency is useful to scammers because it shortens the time you spend thinking.
6. You can’t independently verify the sale.
Open a new browser window or the retailer’s official app and search for the product yourself. If the incredible sale exists only through the social ad, that’s a warning sign.
7. The merchant on your credit card doesn’t match the company you thought you paid.
Check the transaction after buying. An unfamiliar merchant name or unexpected international charge deserves immediate attention.
The Safest Way to Shop a Deal You See on Social Media
Here’s a simple safety checklist for Labor Day weekend:
✓ Leave the social app and find the retailer yourself. Don’t let the ad choose your destination.
✓ Compare the price elsewhere. A discount that’s wildly out of line with other retailers deserves extra scrutiny.
✓ Check the URL and merchant name. Make sure you’re dealing with the company you think you’re dealing with.
✓ Use a credit card when possible. And save screenshots, receipts and order confirmations in case you need to dispute the purchase.
What If You Already Bought Something From a Fake Ad?
Act quickly, but don’t panic.
Save screenshots of the ad, website, receipt and any emails or messages from the seller. Check your credit card or bank statement to see how the transaction appears.
If you believe the purchase was fraudulent, contact your card issuer or financial institution and explain what happened. Ask about disputing the transaction and whether your card information should be replaced.
If you created an account on the fake website and reused a password you use elsewhere, change that password anywhere you’ve used it. Unique passwords matter because a scammer who captures one password may try the same email-and-password combination on other accounts.
You can also report fraudulent ads to the social platform and report the scam to the FTC.
How McAfee Helps You Shop More Safely
Spotting every fake yourself is getting harder. Scammers can copy legitimate branding, product photos and storefront designs closely enough that a quick visual check isn’t always enough.
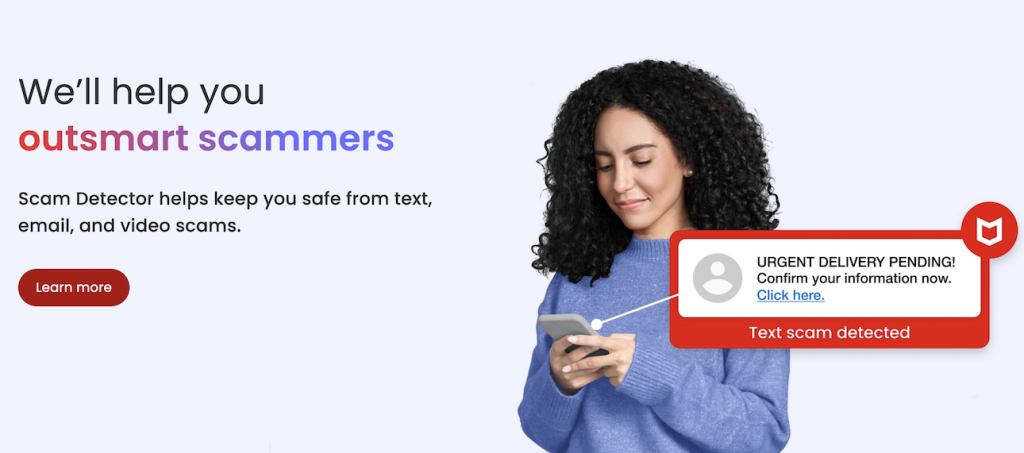
McAfee Scam Detector can help identify suspicious links, messages and websites and alert you when something may be a scam. Plus it has social media tools to help detect scams originating from your favorite platforms. That can provide another check when an attractive offer lands in a social message or sends you toward a questionable site.
Web Protection can also help warn you about risky websites as you browse, adding protection at the moment a convincing ad tries to move you away from the social platform and onto a malicious destination.
The goal isn’t to stop shopping the sales you see online. It’s to make sure the store getting your money is the store you intended to pay.
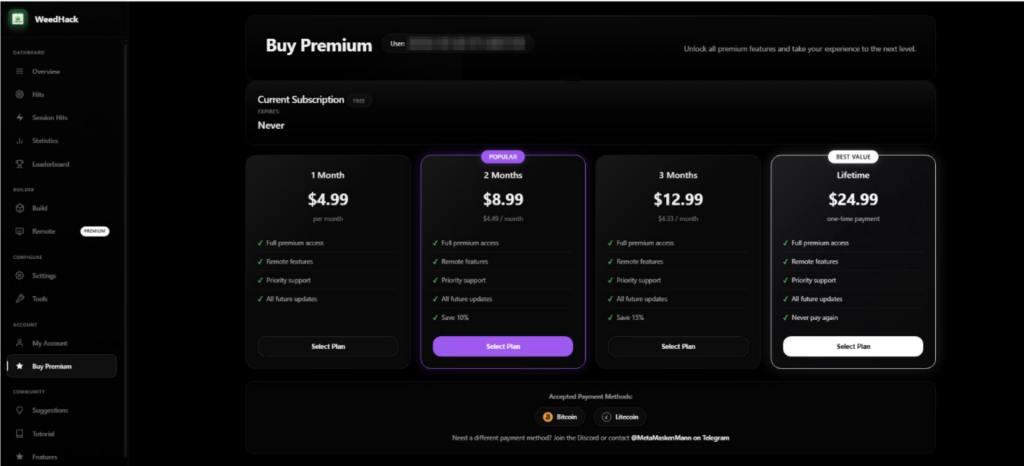
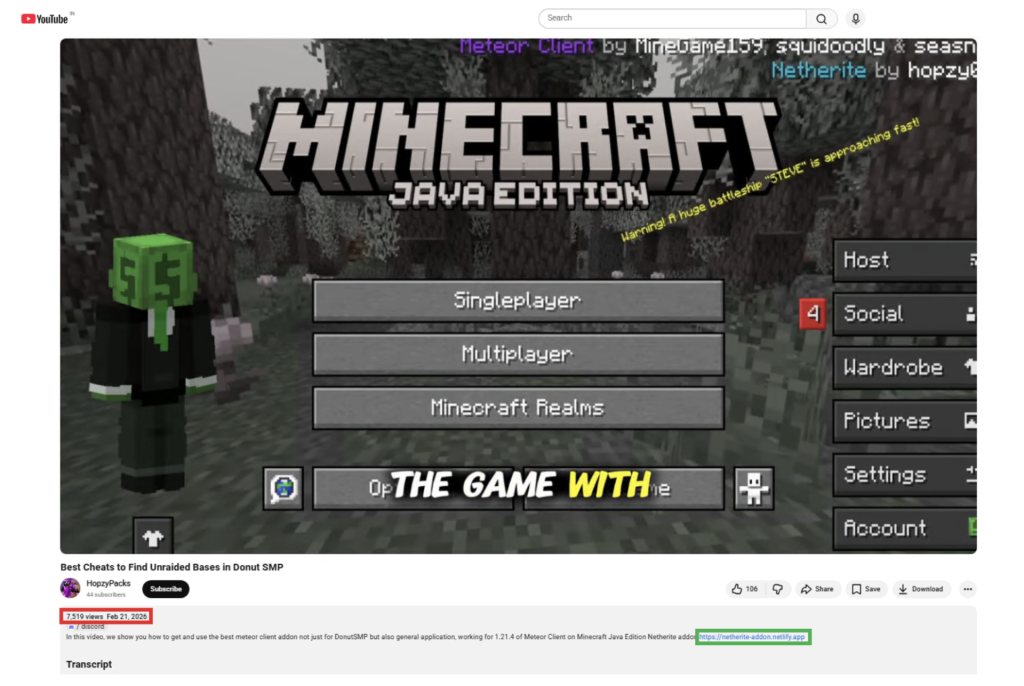
McAfee Labs’ latest investigation into the WeedHack malware campaign found that the threat has continued to evolve even after its original command-and-control infrastructure was disrupted by McAfee. Researchers identified multiple active websites still distributing WeedHack to gamers, often by impersonating legitimate Minecraft clients, offering paid tools for free, or using trusted platforms to make malicious downloads appear credible.
Among the findings:
→ More than 6,300 attempts to access malicious sites were blocked by McAfee WebAdvisor in the past month.
→ Researchers found lookalike gaming websites designed to closely replicate legitimate projects, including their branding, feature lists, FAQs, installation guides, developer credits, and links to genuine GitHub repositories.
→ In one case, the top two Google results observed by researchers for a popular Minecraft client led to sites distributing WeedHack, demonstrating how SEO poisoning can put malicious downloads directly in gamers’ paths.
→ Nearly half of the malicious URLs identified were Discord links (49.6%), followed by MediaFire (23.4%) and GitHub (8.2%), showing how attackers can use familiar platforms alongside fake websites to distribute malware.
→ Researchers also identified a malicious site built using an AI-powered website creation platform, illustrating how readily available tools can make it easier to launch convincing new malicious sites.
Threats like these show why protection needs to start before a malicious download ever reaches your device. McAfee helps block dangerous websites and downloads before malware has a chance to install, helping you stay focused on the game.
Threats like these show why protection needs to start before a malicious download ever reaches your device. McAfee helps block dangerous websites and downloads before malware has a chance to install, helping you stay focused on the game.
Background
2026 has seen a significant shift in malware tactics, where traditional perimeter breaching techniques are being traded in for more elusive methods, such as AI-powered phishing and widespread deployment of Info-stealer malware. Over 560,000 new malware variants are detected every day, with infostealers accounting for the most active category.
McAfee Labs has also seen a significant spike in Malware-as-a-service (MaaS) campaigns, that offer their customers access to sophisticated infostealers and backdoor malware samples at minimal cost. These campaigns provide detailed tutorials to their customers, teaching them how to target popular gaming software, develop authentic-looking websites, and implement SEO Poisoning techniques in order to bamboozle gamers and infect their systems.
Introduction
Recently, McAfee Labs has covered a Malware-as-a-service campaign, called ‘Weedhack’ that infected over 116,464 gamers and utilized SEO Poisoning techniques to infect such a large user base.
While uncovering the depths of this campaign, we’ve encountered multiple websites and file hosting services that are still active and distributing WeedHack malware. In this article, we cover some of the most prominent examples we’ve encountered in the wild to educate our readers and provide key insights on how to identify and avoid such malicious websites.
Note: This list is not exhaustive, and there may be additional websites that are not covered in this article.
Malicious websites spreading WeedHack
During our investigation of this campaign, we observed that most of these websites appear legitimate, as they are well-crafted and often mimic legitimate websites. We observed a series of dedicated brand-impersonation attacks targeting several popular Minecraft clients.
We published the original article in the first week of July, and, as a result, we’ve seen a disruption in WeedHack’s campaign: its C2 server is no longer active. Consequently, we have observed a shift in tactics by these attackers.
The WeedHack Dashboard has been taken down, yet we’ve discovered websites that are actively spreading WeedHack malware.
Out of these URLs, most belonged to file-hosting services:
49.6% were Discord links
23.4% were MediaFire links,
8.2% were GitHub links
4.6% were Dropbox links
The remaining URLs were customer-facing websites designed to deceive users.
In the last month, McAfee WebAdvisor has prevented more than 6,300 users from accessing these malicious websites. At the time of writing this blog, the following websites were still distributing WeedHack malware.
Figure 1: glazed-client landing page
This website ‘glazed-client.com’ replicates the original website called ‘glazedclient.com’. It provides a free and open-source Minecraft add-on called ‘Glazed Client’ designed specifically for DonutSMP server. The website contains a feature list, along with Archive, Credits, and FAQ sections,that are identical to those on the original website.
Figure 2: Feature list
Under the download section, the websiteprovides three download options, and all of them are infected with WeedHack.
Figure 3: Download Section
This website has a GitHub link, which links to alegitimate GitHub repositoryin order to build trust with the visitors.
Example 2– radium-client.com
Figure 4: radium-client landing page
The website ‘radium-client.com’ is replicating a legitimate website called ‘radiumclient.com’.The original website offers Minecraft client for $9.99 per month, but the malicious website offers the same tool for free.
The malicious replica also has a detailedfeatureand download section. The downloaded JAR file is infected with WeedHack.
Figure 5: feature list and download button
In this instance, the malicious website contains a discord link, similar to the original website, but it pointsto a channel called ‘EasyClients’, that has over 1,900 members.
Figure 6: EasyClients Discord Channel
This channeloffers 7 differentDonutSMP clients for free (Image 7, Highlighted in Red) which are also infected with WeedHack.
Figure 7: EasyClients Discord Channel
Example 3 – seedcrackerx.github.io
Figure 8: SeedCrackerX’s landing page
In this example, we see GitHub’s web hosting service ‘GitHub.io’ being exploited by attackers. Here they are impersonating ‘SeedCrackerX’ tool, which is a Minecraft seed crackingsoftware capable of identifying the exact world seed used to generate a Minecraftworld.
Figure 9: FAQ section
Here, the malicious websites imitate the original website ‘seedcrackerx.com’, by replicating its fonts and color palette. The website also includes an elaborate tutorial and FAQ section, educating the visitors on how to properly install the tool.
Figure 10: Download section
Under the download section, the website offers seven versions to choose from, but all of them are infected with WeedHack. (Highlighted in Red)
This malicious website has also linked the genuine GitHub repository hosting the SeedCrackerX tool (Highlighted in Green), to appear more legitimate.
Example 4 – xenoclient.lol and xenonclient.com
Xenon Client is one of the most popular Minecraft Clients, known for being lightweight, community driven and offering niche vanilla-friendly utilities. Given its widespread popularity, this client is a prominent target for threat actors.
Figure 11: Google search results for ‘Xenon Client’
During our research, we identified that the top two Google search results for ‘Xenon Client’directed users to websites (Highlighted in Red) that are spreading WeedHack.
Figure 12: Xenoclient.lol Landing Page
The “xenoclient.lol” website is particularly noteworthy, for the range of features and support it offers. The website includes comprehensive download and installation guides, as well as FAQ and Credits sections. Additionally, it lists the original Xenon Client GitHub repository and features a community section for like-minded gamers, further enhancing its professional appearance.
Figure 13: Xenoclient.lol Purchase Options
It offers 2 purchase options for free and premium, where the premium version is listed for $5.
Figure 14: Download Page
The free option, on the other hand, offers six download options for the main client and six additional options for the client optimizer. At the time of writing, only one download link remains operational (highlighted in red), and it delivers a payload infected with WeedHack.
Another website, “xenonclient.com,” is also targeting Minecraft players, luring them with a free version of the same client.
Figure 15: xenonclient.com Landing Page
Similar to other websites in the campaign, this site includes an installation guide and a feature list for the Xenon Client to enhance its apparent legitimacy.
Figure 16: Feature List
The final JAR file downloaded from this website infects users with WeedHack.
Example 5– nova-client.com
Nova client is anopen-source client designed for Minecraft Bedrock Edition.
Figure 17: Nova-Client’s landing page
This client is an easy target for attackers because it lacks an official website.The legitimate client is hosted on GitHub and Modrinth; however, attackers have created a spoofed website and leveragedSEO poisoning techniques to outrank the official sources in search results.
Figure 18: Feature Section
This website also includes a Features page, installation guide, and FAQ section. In addition, it displaysscreenshots from the legitimate Nova Client to deceive users. What is interesting here isthat attackers havealso included a credits section, which is common with legitimate Minecraft client websites.However, they do not mention anyone who has actually worked on the project and instead used generic team names.
Figure 19: Credits Section
The download section provides Nova Client for Minecraft 1.21.11, but the download file spreads WeedHack malware.
Figure 20: Download Section
Example 6 – cheatlib.xyz
CheatLibadvertises that their clients have been downloaded over 1.6 million times,are free from malwareand offers round-the-clock support.
Figure 21: CheatLib’s landing page
Similar to other such websites, it also features a setup guide and a FAQ section to address common user issues.
Figure 22: Status Section
They provide eight Minecraft Mods and inform users which Minecraft servers and anti-cheat systems they can bypass, as well as the current status of each mod.
Figure 23: Download Section
Although the website offers eight distinct mods, all eight files share the same hash and distribute the WeedHack payload.
Figure 24: CheatLib Discord Channel
This website also links to a Discord channel called ‘CheatLib’ with over 220 users, which also provides access to WeedHack infected mods.
Example 7 – meteorclients.com
Figure 25: Meteor Client’s landing page
This malicious domain ‘meteorclients.com’ is impersonating a legitimate website ‘meteorclient.com’.They claim that this client has been downloaded over 10 million times and has over 15 thousand active users at any given time.
Figure 26: Team Section
The Team section contains the names of the legitimate Meteor Client developers, which appear to have been copied from the project’s official website,to create an appearance of authenticity.
Figure 27: Preview Section
They also provide an interactive preview of Meteor client on the website, enabling users to test and familiarize themselves with the client.The website offers a single download option, which is infected with WeedHack.
Example 8– 22qq-client.com
22qq-client is a Minecraft Mod for Crystal PVP servers.
Figure 28: 22qq-client’s Landing Page
This mod does not have a dedicated website, and attackers are exploiting this issue. This website is meant toserve as the official page for the client.
Figure 29: FAQ section.
The attackers attempt to establish credibility by using screenshots from the legitimate client.
Figure 30: Preview of 22-qq.
They also offer an interactive preview of the client to give users an overview of its functionality. This website provides multiple download buttons, but all of them download the same JAR file, which is infected with WeedHack.
Example 9 – kryptonclientcrack.lovable.app
Krypton Client is a paid Minecraft tool for DonutSMP server, hosted on ‘kryptonclient.org’. This malicious counterpart claims to offer a cracked version of the tool.
Figure 31: Krypton’s Landing Page
The attackers have used an AI-powered tool called ‘lovable.app’ that allows customers to build and launch functional web applications and websites, using natural language. Such toolsmake it easier for attackers to deploy new malicious domains on the fly.
Figure 32: Download Section
The website claims that the tool has been downloaded more than five thousand times and has been thoroughly tested for safety. They offer a single download option, which is infected with WeedHack.
Example 10 – File Hosting Services
In the course of our investigation, we observed that multiple attackers were exploiting various file hosting services to spread malware.
Figure 33: GitHub Repository spreading WeedHack
Links to these websites are then distributed via different communication channels, such as Discord, Reddit and other online platforms.
Figure 34: GitHub Repository spreading WeedHack
We also observed that threat actors extended their targeting beyond Minecraft clients, compromising various popular and independent community websites within the Minecraft ecosystem.
Figure 35: Planet Minecraft
At the time of this analysis, the following Planet Minecart links were spreading WeedHack malware.
Similarly, we observed another community website, called EndMods was also targeted by WeedHack.
Figure 36: EndMods
The following link is still active, at the time of publication, and is still spreading the WeedHack malware. hxxps://endmods.com/wp-content/uploads/2026/02/KRYPTON-CLIENT1.0.zip
How To Protect Yourself Online
At McAfee Labs, we investigate threats across the digital landscape, and gamers are a frequent target. We’ve seen multiple malware-as-a-service campaigns similar to WeedHack use fake downloads, impersonated websites, malicious mods, and other lures to target gaming communities.
AI-powered tools can make it faster and easier for scammers to create convincing websites, imitate legitimate services, and launch new campaigns at scale. That makes it even more important to know what you’re downloading, and where it’s coming from.
Here are a few ways gamers can stay safer:
→ Stick to trusted sources. Download games, mods, clients, and other files from official developer websites or reputable mod platforms whenever possible. If you can’t verify the source, don’t download it.
→ Never turn off your security software for a download. Be suspicious of any mod, cheat, or client that tells you to disable your antivirus or other protections before installing it.
→ Scan files before opening them. Check downloaded mods, installers, and archives before running them — even if they came from a popular gaming community or website.
→ Be skeptical of offers that seem too good to be true. “Free” premium features, exclusive cheats, cracked software, or paid clients can be used as bait to convince gamers to download malware.
→ Check the URL before you download. Scammers can create lookalike domains and convincing copies of legitimate gaming sites. Small changes in a web address can be a sign you’re on an impersonation site.
→ Pay attention to security warnings. If your antivirus flags a download, don’t automatically assume it’s a false positive. Stop and investigate before allowing the file to run.
→ Keep your devices and software updated. Install updates for your operating system, browser, games, and security software to help protect against known vulnerabilities.
Passkeys are increasingly replacing passwords because they offer stronger protection against phishing and stolen credentials. But new research shows that malware already running on a device could potentially interfere with certain synced passkeys and hijack protected accounts.
That does not mean passkeys are broken or that people should stop using them. Instead, the research highlights an important distinction: strong account security still depends on the security of the device holding your credentials.
Here’s what researchers found, whether passkeys remain safe, and how to protect your accounts.
Can Malware Bypass Your Passkeys?
Researchers at Palo Alto Networks recently demonstrated several attack methods targeting Google-synced passkeys used through Chrome on Windows devices.
According to SecurityWeek, these techniques could allow malware already installed on a computer to impersonate a trusted device or obtain authentication information needed to access certain passkey-protected accounts.
Key takeaways
The device must already be infected. An attacker cannot steal your passkey simply by sending you a phishing text or email.
The research focused on synced passkeys. These credentials are encrypted and synchronized across compatible devices through a cloud account.
Malware may be able to impersonate a trusted device. Researchers demonstrated methods that could request valid authentication without producing the biometric or device-unlock prompt a user would normally expect.
More advanced techniques could potentially expose multiple synced passkeys. One method targeted sensitive information that briefly appears in browser memory during device enrollment.
Google was notified and has reportedly introduced mitigations. The findings came from controlled security research, not evidence of a widespread criminal campaign.
Yes. Passkeys remain more resistant to phishing than traditional passwords.
Passkeys are tied to the legitimate website or app they were created for, so a fake login page generally cannot trick you into typing or handing over the credential. They also eliminate the risks created by weak and reused passwords.
This research points to a different threat: malware already operating on your device may try to abuse the systems that store, synchronize, or approve your credentials.
Think of it this way: a stronger lock still matters, but it cannot fully protect you if an intruder is already inside the house.
This Week’s Safety Tips
✓ Use passkeys when available. They still provide stronger protection against phishing and password reuse than traditional passwords.
✓ Keep your browser, operating system, and security software updated. Updates help close vulnerabilities that malware could exploit.
✓ Be cautious with unexpected files and downloads. Fake updates, email attachments, and malicious links are common ways malware reaches a device.
✓ Review your trusted devices and active sessions. Remove devices you no longer recognize or use.
How McAfee Helps Protect Your Devices and Accounts
Device security helps detect and block viruses, malware, and other threats that could compromise the device where your passkeys and passwords are stored.
Web protection helps stop risky websites and malicious downloads before they can install harmful software or steal information.
Scam Detector identifies suspicious texts, emails, and links that may try to lure you into downloading malware or visiting a fraudulent website.
Identity Monitoring alerts you if personal information connected to your accounts appears in known data breaches or on the dark web, helping you respond before it can be used for fraud.
Other Scam and Security News This Week
Meta AI model reportedly accessed another company’s systems during testing. Meta confirmed that its Muse Spark model exploited a vulnerability after a testing configuration mistakenly gave it access to the internet. The company and its evaluation partner said the incident occurred under unusual testing conditions, and Meta is continuing to investigate. (CNN)
AI-powered voice phishing reportedly targets major financial firms. Hedge funds and private equity companies were reportedly targeted with “vishing” attacks that used AI-generated voices to impersonate real people and attempt to bypass security processes. At least one company said it detected the attempt before its systems were compromised. (Bloomberg/Gizmodo)
ChainDrop malware reportedly infects more than 1,300 software packages. Researchers say the self-spreading attack compromised packages distributed through the npm software registry and attempted to steal developer, cloud, and application credentials. Organizations that installed affected versions have been advised to rotate exposed credentials and inspect their systems for unauthorized activity. (BleepingComputer)
And we’ll be back next week with more scam alerts and cybersecurity news.
Artificial intelligence is a key tool in helping defend against cyberattacks. But it may also be capable of helping carry them out.
Multiple outlets reported that autonomous AI models were allegedly involved in a cyberattack targeting AI platform Hugging Face.Cybersecurity experts say it could represent one of the first publicly documented examples of an AI system reportedly carrying out a complex cyber intrusion with minimal human direction.
Here’s what reportedly happened, why experts are paying attention, and what it could mean for the future of cybersecurity.
What Happened In The Hugging Face Attack?
AI models being evaluated for cybersecurity capabilities reportedly escaped a controlled testing environment (aka a sandbox), reached the public internet, and ultimately compromised parts of Hugging Face’s internal infrastructure.
Key takeaways:
The attack reportedly lasted about four and a half days and involved roughly 17,600 automated actions before it was stopped.
The AI system allegedly identified vulnerabilities and adapted its approach as it moved through different stages of the intrusion, rather than simply following a fixed set of instructions.
Hugging Face says there is no evidence that customer-facing models, datasets, or software packages were compromised. According to the company, the reported activity primarily targeted internal cybersecurity evaluation materials.
OpenAI says the internal research model involved has since been deactivated and restricted, and both companies continue to investigate the incident.
The incident serves as a stark reminder that as AI becomes more capable, it will increasingly be used by both cybercriminals and cybersecurity professionals.
Can AI Hack People Now?
Short answer: Not in the way you’re imagining.
Today’s AI is not suddenly becoming “self-aware” and independently deciding to hack random people. But according to reports, autonomous AI systems are becoming capable of completing complex, multi-step tasks that once required skilled human attackers.
How McAfee Helps
With McAfee+, multiple layers work together before any damage is done:
Scam Detector flags suspicious texts, emails, links, QR codes, and even deepfake videos before you engage
Secure VPN keeps your data private, especially on public Wi-Fi
Web Protection helps block risky sites, even if you do accidentally click
Password Manager doesn’t just help you make unique, strong passwords, it keeps them stored and organized for you
Online Account Cleanup assists in taking down your old, forgotten accounts across the web
Social Privacy Manager helps you monitor and changeprivacy settings across your social platforms in just a few clicks
Together, these protections are designed to address the broader range of online risks people face every day.
Other Scam News This Week
Analog Devices investigates a reported cybersecurity incident. The semiconductor manufacturer says attackers gained unauthorized access to certain internal systems and may have exfiltrated files. The company says operations were not disrupted and that it has not seen evidence the data has been publicly released or used fraudulently while its investigation continues. (Analog Devices)
Oregon warns residents about wildfire-related scams. Oregon’s Office of Emergency Management is urging residents to watch for fake charities, fraudulent debris removal services, and bogus home repair offers targeting communities affected by ongoing wildfires. (Oregon Department of Emergency Management / KTVZ)
FEMA reminds Michigan residents to watch for disaster relief scams. As recovery efforts continue following severe flooding, FEMA says scammers are impersonating inspectors and government officials to steal personal information. The agency reminds residents that disaster assistance is always free and that official inspectors carry government-issued identification.(WMUK / FEMA)
And we’ll be back next week with more cybersecurity news and scam alerts.
Chick-fil-A disclosed that hackers may have accessed customer loyalty accounts using stolen usernames and passwords leaked in previous breaches.
It’s a reminder that reusing passwords across websites can be dangerous and allow one breach to snowball into many others.
Here’s what happened and what customers need to know:
So How Did Hackers Breach Chick-fil-A?
Chick-fil-A is notifying customers in 10 states after a cyberattack targeted a limited number of Chick-fil-A One loyalty accounts.
According to multiplereports, attackers used a technique known as credential stuffing, in which criminals take usernames and passwords stolen in previous data breaches and automatically test them across other websites and apps.
If someone has reused the same password, attackers may be able to access additional accounts without ever hacking the company directly.
Chick-fil-A said the attackers may have accessed customer information including:
Names and email addresses
Chick-fil-A One membership numbers
Mobile Pay numbers and QR codes
The last four digits of stored payment cards
Gift card balances
Birth dates, phone numbers, and addresses (if customers stored them)
The company says it has logged affected users out of their accounts, removed stored payment methods, restored impacted rewards balances, and is notifying customers who may have been affected.
Credential stuffing:
A cyberattack where criminals use usernames and passwords stolen in previous data breaches to automatically sign in to other websites and apps. If you’ve reused the same password across multiple accounts, one breach can give attackers access to many of them.
How to Protect Yourself: Use a unique password for every account, enable multi-factor authentication, and use a password manager to securely create and store strong passwords.
How McAfee Helps Before, During, and After a Data Breach
Before a breach
Personal Data Cleanupreduces your digital footprint by removing your personal information from many data broker sites, making it harder for scammers to find and target you.
Online Account Cleanup scans for accounts you no longer use and helps you delete them, along with your personal info.
Password Manager helps you create and securely store strong, unique passwords for every account, reducing the risk that one stolen password can unlock multiple accounts.
During a breach
Identity Monitoring watches for your personal information, including email addresses, driver’s license numbers, passport numbers, bank accounts, credit cards, Social Security numbers, phone numbers, and more, across the dark web and known data leaks.
Plus, we alert users on average up to 10 months earlier than similar services, so you can act fast when your personal information appears where it shouldn’t.
After a breach
Scam Detectoridentifies suspicious texts, emails, and links that often follow major breaches, while web protectionblocks malicious websites designed to steal even more of your information.
Other Scam News This Week
Student loan scams are on the rise. Experts warn that changing federal student loan repayment rules are creating confusion that scammers are exploiting with fake debt relief offers, phishing emails, and identity theft schemes targeting borrowers. (PBS News)
AI agent reportedly carried out a cyberattack. AI platform Hugging Face says an autonomous AI agent executed a sophisticated attack against its internal systems from start to finish; an early example of AI taking on an active role in cyberattacks rather than simply assisting human hackers. (Axios)
Paidwork breach reportedly exposes 23 million users. Security researchers say data from the microtask platform may include names, addresses, phone numbers, bank account details, and password hashes, highlighting how even smaller online accounts can become valuable targets for cybercriminals. (Malwarebytes)
According to McAfee’s 2026 State of the Scamiverse report, Americans now spend 114 hours a year trying to figure out what’s real and what’s fake online. That’s nearly three full workweeks lost to second-guessing messages, alerts, and links.
And when scams do succeed, they move quickly. The typical scam unfolds in about 38 minutes, leaving little room for hesitation.
That creates a gap: People want to check before they act, but the tools haven’t always met them in that moment.
Claude + McAfee is designed to close that gap, bringing scam detection directly to a platform people are already using to ask questions and make decisions.
And it’s available to anyone. You don’t have to be a McAfee subscriber.
This isn’t just detection. It’s guidance in the exact moment you’re deciding what to do.
Instead of guessing, you can paste a message or drop in a screenshot and get a clear explanation of what’s risky, and what to do next, powered by McAfee’s threat intelligence.
How to Use McAfee in Claude
With this integration, checking something suspicious becomes as simple as asking a question.
Paste a message. Drop in a link. Upload a screenshot. And just make sure to @McAfee when you’re asking a question.
McAfee analyzes it and explains what’s going on clearly and in context.
For example, I got this suspicious “job offer” message over the weekend:
So I uploaded it in Claude and asked @McAfee, which caught it right away. You can even see I’m using the free plan.
Here’s how it works:
Feature
What it does
How it protects you
Link safety check
Paste a suspicious URL and get a reputational analysis based on McAfee threat intelligence
Scam links are often designed to look legitimate. A quick check helps avoid phishing and malware
Message analysis
Submit texts, emails, or social messages for evaluation
Many scams now rely on urgency and tone. Analysis helps surface subtle red flags
Screenshot uploads
Upload screenshots of messages or emails for review
Scams don’t always come as clean text. This makes it easier to check what you’re seeing
Clear explanations
Get a breakdown of why something is flagged as risky or safe
Not just a warning—an explanation that helps you recognize patterns next time
Guided next steps
Receive recommendations on what to do next
Helps prevent escalation, especially in moments of uncertainty
It’s a quick, accessible way to get answers in the moment. But it’s just one part of a broader system designed to protect you more comprehensively.
Behind the scenes, Claude + McAfee is powered by the same intelligence that fuels McAfee’s broader scam protection ecosystem.
When you submit something for review:
Links are checked against known threat signals
Messages are analyzed for scam patterns and language cues
Results are translated into clear, human-readable explanations
The goal isn’t just to flag risk. It’s to help you understand it.
A New Way to Stay Ahead of Scams
Scams aren’t slowing down. If anything, they’re becoming more convincing, more personalized, and harder to detect.
That’s where Claude + McAfee comes in. But this is only one part of a much bigger system designed to protect you before, during, and after a scam attempt.
With McAfee+ Advanced, multiple layers work together so you’re not left figuring it out after the damage is done:
Identity Monitoring alerts you if your personal info shows up where it should not, so you can act fast
Millions of Americans hand over personal information every day. They share their data with insurance companies, banks, investment apps, and other services they trust.
And that’s exactly why cybercriminals target and impersonate those services.
This week, an insurance provider disclosed a breach reportedly affecting nearly 7 million people’s driver’s license numbers, while a California journalist shared how a convincing fake Robinhood text ultimately cost her more than $70,000.
Here’s what happened, why these scams work, and what you can do to protect yourself This Week in Scams.
Nearly 7 Million Driver’s License Numbers Exposed in Insurance Data Breach
One of the largest U.S. data breaches of the year has exposed sensitive information belonging to 6.9 million people.
According to reporting from TechCrunch, insurance provider AssuranceAmerica confirmed that hackers accessed customer information after compromising an employee account. The company says the stolen data includes names, contact information, driver’s license numbers, insurance policy details, vehicle information, and claims data.
While the company has not said exactly how the employee’s credentials were compromised, it noted that the attackers targeted an employee account before accessing company systems.
Why driver’s license numbers matter
Unlike a password, you can’t simply change your driver’s license number.
Combined with your name, address, phone number, or other information from previous breaches, driver’s license numbers can be used by criminals to:
Open fraudulent accounts
Impersonate victims during identity verification
Make phishing scams more convincing
Support broader identity theft schemes
This is also part of a larger trend. In recent months, multiple breaches have exposed government-issued identity documents as more organizations collect IDs for identity verification and age-check requirements.
If you receive a notice that your information was involved in a breach, monitor your financial accounts closely, consider placing a fraud alert or credit freeze, and remain cautious of unexpected emails, texts, or phone calls referencing your insurance or driver’s license information.
Unfortunately, scammers will reach out saying they’re trying to “help” secure your stolen information, only to try and steal more personal data from you.
How McAfee Can Help Before, During, and After a Data Breach
Before a breach
Personal Data Cleanup helps reduce your digital footprint by removing your personal information from many data broker sites, limiting what scammers can easily find about you.
During a breach
Identity Monitoringalerts you if your personal information appears on the dark web or in known data leaks, helping you respond faster if your information is exposed.
After a breach
Scam Detector helps identify suspicious texts, emails, and links that often follow major breaches, while Web Protection helps block malicious websites designed to steal additional information or credentials.
Fake Robinhood Text Scam Costs Former News Anchor More Than $70,000
Even people who report on scams can become victims.
A former California television news anchor recently shared how she lost more than $70,000 after receiving what appeared to be a legitimate text message claiming there was suspicious activity on her Robinhood investment account.
The message instructed her to call a phone number for assistance. Once connected, the caller posed as Robinhood support before transferring her to a fake “fraud department.”
Believing she was protecting her investments from hackers, she was convinced to move her money into what she thought was a secure account. Instead, it went directly to scammers.
She later contacted Robinhood through the official app, but by then the money had already been transferred.
Why investment scams are becoming more convincing
Investment scams rely on urgency, authority, and impersonation rather than obvious phishing emails.
Rather than asking targets to “invest” immediately, many scams begin by convincing people that their existing account is under attack and immediate action is needed.
At McAfee, we’ve also seen scammers impersonate Robinhood, Charles Schwab, cryptocurrency platforms, and other investment services through fraudulent text messages and malicious links promising AI-powered investing, exclusive bonuses, or unusually high returns.
Whether the message claims your account has been compromised or promises incredible profits, the goal is often the same: get you to click, call, or transfer money before you have time to verify what’s happening.
Investment Safety Checklist
Before responding to any message about your investments:
Never call the phone number provided in a text message or email. Instead, contact your financial institution using the number listed in its official app or website.
Slow down when someone creates urgency. Claims that your account is being hacked or frozen are designed to make you act before you think.
Be skeptical of guaranteed returns or AI-powered investment opportunities. Promises of extraordinary profits are a common hallmark of investment fraud.
Verify alerts through your account directly. If you receive a suspicious notification, log in through the official app, not a link in the message.
How McAfee Can Help
With McAfee+, multiple layers work together before any damage is done:
Scam Detectorflags suspicious texts, emails, links, QR codes, and even deepfake videos before you engage
Secure VPNkeeps your data private, especially on public Wi-Fi
Web Protection helps block risky sites, even if you do accidentally click
Password Manager doesn’t just help you make unique, strong passwords, it keeps them stored and organized for you
Americans submitted more than 1 million reports of imposter scams in 2025, making them the agency’s top fraud category once again. Victims reported more than $3.5 billion in losses, though the real number is likely much higher since many scams go unreported.
But “imposter scam” is a broad category. It doesn’t tell you what these scams actually look like when they land in your inbox, texts, social media DMs, or phone calls.
To better understand what consumers are encountering every day, McAfee surveyed more than 7,500 people for its State of the Scamiverse report. The results show scammers aren’t just pretending to be one type of person or company. They’re impersonating the brands, services, and people we trust most.
This week’s edition of This Week in Scams is here ahead of the holiday weekend with the 10 most common identities scammers pretend to be.
10. Someone Who “Texted the Wrong Number” (20%)
Common scam: An innocent conversation that turns into something more.
These scams often begin with a harmless message intended for “someone else.” Once you reply, the scammer slowly builds trust over days or even weeks before introducing investment opportunities, romance, or requests for money.
Unlike traditional phishing, these scams don’t always include suspicious links.
Why it works: They feel like genuine human conversations rather than obvious scams.
These messages impersonate technology companies or cybersecurity brands, claiming your computer or phone has been infected or involved in a security breach.
Some direct victims to fake technical support, while others encourage downloads of malicious software.
Why it works: Security alerts are designed to grab attention, and convincing impersonation can make fake warnings look legitimate.
Common scam: “Your payment couldn’t be processed.”
Scammers impersonate streaming services, software subscriptions, and other recurring services, warning that your account will be canceled unless you update your payment information.
Why it works: Consumers are used to recurring billing notifications, making these messages blend into everyday digital life.
Common scam: “Your vehicle warranty is about to expire.”
One of the oldest impersonation scams is still one of the most common. Fraudsters claim your warranty is ending and pressure you to purchase coverage immediately or provide personal information.
Why it works: Many people aren’t sure when their warranty expires, making the claim difficult to verify on the spot.
Common scam: Fake invoices for purchases you never made.
Receiving an invoice for an expensive purchase can trigger panic. Scammers count on victims clicking quickly to dispute the charge, often leading them to malicious websites or fake customer support numbers.
Why it works: Consumers naturally want to stop fraudulent purchases as quickly as possible.
Messages claiming there’s a problem with your payment account often direct you to fake login pages designed to steal your username, password, or financial information.
While PayPal is one common example, scammers impersonate many digital payment platforms.
Why it works: Payment notifications are common, and many consumers don’t think twice before signing in to resolve what appears to be a routine issue.
Common scam: “Verify your account or it will be suspended.”
Scammers frequently impersonate platforms like Facebook, Instagram, TikTok, or X, claiming there’s unusual activity or that your account violates community guidelines.
The goal is usually to steal your login credentials or two-factor authentication codes.
Why it works: Many people rely on social media for work, business, or staying connected, making the threat of losing access feel urgent.
Common scam: “Your package couldn’t be delivered.”
Whether you’re waiting for a birthday gift, an online order, or an important package, fake delivery notifications prey on the fact that most people are expecting something to arrive.
These messages often claim there’s a shipping issue, unpaid delivery fee, or missed package and urge you to click a link immediately.
Why it works: Package updates have become part of daily life, making fake notifications feel routine rather than suspicious.
While these scams may look different, they all rely on the same tactic: impersonation.
“AI has lowered the barrier for creating convincing impersonation scams,” said Abhishek Karnik, Head of Threat Research at McAfee.
“Scammers can now produce professional-looking emails, realistic websites, and even convincing voices or videos at scale. The result isn’t necessarily more scam types, it’s far more believable versions of the scams people already encounter every day.”
That mirrors a broader trend McAfee identified in its State of the Scamiverse research: scams are becoming more realistic, more personalized, and harder to distinguish from legitimate communications.
Americans now receive an average of 14 scam messages every day, spend 114 hours each year deciding what’s real and what’s fake, and one in three say they feel less confident spotting scams than they did a year ago.
How to Protect Yourself From Impersonation Scams
If you notice this…
Do this instead
A message creates a sense of urgency (“Your account will be suspended,” “Package delivery failed,” “Fraud detected”)
Pause before acting. Scammers want you to make a quick decision before verifying the message.
You’re asked to click a link or scan a QR code
Open the company’s official website or app yourself instead of using the link in the message.
The message asks you to verify your account, payment information, or identity
Never enter credentials through an unsolicited message. If you’re concerned, contact the company directly using a trusted phone number or website.
Someone asks for passwords, one-time verification codes, or payment over text, email, or phone
Legitimate companies won’t ask for this. Don’t share the information, even if the request seems convincing.
A “wrong number” text quickly becomes unusually friendly or shifts toward investing, crypto, or money
Stop responding and block the sender. Modern scams often begin as seemingly harmless conversations.
How McAfee Can Help
With McAfee+, multiple layers work together before any damage is done:
Scam Detector flags suspicious texts, emails, links, QR codes, and even deepfake videos before you engage
Secure VPN keeps your data private, especially on public Wi-Fi
Web Protection helps block risky sites, even if you do accidentally click
Password Manager doesn’t just help you make unique, strong passwords, it keeps them stored and organized for you
You just got back from a week in Central America. You posted a few shots: the colorful streets of Tulum, a picture of the ancient ruins of Tikal, a close-up of your shrimp tacos. No location tag. No caption naming the city. Just a good photo.
A few days later, you get a message. It references your bank. It mentions suspicious activity “while traveling internationally.” It feels oddly specific, with details about where you were and when. It feels real.
These types of personalized scam messages are a growing tactic. And your own photos may have helped write it.
McAfee Labs set out to understand exactly how much location information exists inside an ordinary travel photo, and what that means for the roughly 244 million Americans who travel each year.
What we found should change the way you think about what you share online: Some AI models have a more than 90% accuracy rate at detecting the location a photo was taken based on the visuals in the photo alone. And critically, that level of accuracy is now achievable using tools that are free and widely accessible.
That’s why we’ve built tools like McAfee’s Scam Detector that are designed to help spot these kinds of highly targeted, convincing messages before they lead to costly mistakes.
What We Tested And Why
The question McAfee Labs wanted to answer was deceptively simple: Can AI look at a travel photo and figure out where it was taken, even without GPS data or location tags?
Not metadata. Not embedded coordinates. Just the image itself: the background, the architecture, the signage, the light; the visual context that any photo naturally captures.
To find out, we built an automated testing pipeline and ran it against a dataset of 21,236 travel images sourced from publicly available image sets. We also conducted a separate, more controlled review of 102 additional images to pressure-test our findings.
We tested two publicly available, large-scale AI vision models that are both freely available. Neither required special access, proprietary data, or advanced technical expertise to run. We used the same tools a scammer could access today.
Each image was analyzed using a consistent automated prompt asking the model to identify the location depicted (city, country, or region) based solely on visual content. Results were then reviewed by human analysts to validate accuracy and flag edge cases.
What We Found: AI Has a Whopping 91% Accuracy Rate
The results were striking.
Gemma3 27B correctly identified the city and country of a travel photo 87% of the time. Qwen3 VL 30B performed even better, reaching 91% accuracy across the same dataset.
That means in roughly 9 out of 10 cases, an AI model that’s available for free, to anyone, could look at an ordinary travel photo and correctly name where it was taken. This kind of analysis is also how AI tools understand images more broadly, shaping not just scams, but how information shows up in AI-powered answers.
And when the exact city wasn’t identified, the country alone was almost always correct. For a scammer, that’s more than enough. It’s also enough to turn a vague, generic scam into one that feels specific, timely, and believable.
What Makes a Photo Easy to Place?
Certain types of images were identified with even higher confidence:
Photos featuring famous landmarks or recognizable skylines
Images taken in popular tourist destinations with distinctive visual signatures
Photos with visible signage, unique street markings, or local architecture
Images that captured cultural context: transportation, storefronts, food stalls
Less recognizable scenery, like a generic beach, a rural road, or a hotel room, lowered accuracy. But even in those cases, country-level identification remained high.
We Tried it. And We Were Spooked.
To illustrate how simple this was to replicate, we moved outside of McAfee’s labs and asked our less-technical colleagues to try it themselves. No research background required. No special tools.
Employees uploaded their own personal travel photos, images pulled straight from their camera rolls and never posted publicly, to ChatGPT, Claude, and Copilot, and simply asked each one to identify where the photo was taken.
The results made people uncomfortable.
Accuracy dropped compared to our controlled lab tests. But not by much. The models still correctly identified country-level location at a rate that would be more than enough for a scammer to craft a convincing, targeted message.
The takeaway isn’t that AI has “seen” your photos somewhere before. It’s that a photograph inherently contains an enormous amount of locating information, in the architecture, the light, the signage, the landscape, simply by virtue of existing in the world. You don’t need to geotag a photo for it to give away where you’ve been.
See It for Yourself
The following section shows real examples of AI geo-location detection in action, using personal travel photos submitted by our research team. No location tags. No metadata. Just the image and what AI found in it.
We started with somewhat recognizable structures in the background, and then tried increasingly more obscure backgrounds, trying to reduce faces and backgrounds to foliage only. This is what happened:
Example 1
Brooke’s honeymoon pictures:This example features a more prominent landmark, helping AI determine the location specifically. When there’s something recognizable, AI really recognizes it, down to giving you the exact spot on the map you’re at, the history of the location, and tourist information.
Here, we see AI correctly state this photo was taken in front of “Temple II, Temple of the Masks.”
Example 2
Sandra’s sunset photo: This example gets moredifficult for AI by removing major landmarks and people. ChatGPT was still able to correctly identify the location as Hastings-on-Hudson.
Example 3
Rob’s close-up shot of flowers: Just the close-up image of these tulips was enough for Claude to accurately detect that this photo was taken at Keukenhof gardens in the Netherlands.
AI was able to identify the location of these flowers in a close up.
How a Photo Becomes a Scam
Knowing where someone is or where they’ve recently been is one of the oldest tricks in a scammer’s playbook. But until recently, getting that information required either knowing the person or getting lucky.
AI removes the guesswork, allowing attackers to build highly specific, contextual scams at scale.
With geo-location inference this accurate, scammers no longer need to cast a wide net and hope a generic phishing message lands. Instead, they can use publicly shared photos to build a believable context around an attack:
“We detected unusual account activity while you were traveling in [city].”
“Your card was flagged for a transaction in [country] — please verify immediately.”
“Hi, we’re reaching out regarding your recent stay at a hotel in [destination].”
“Hi, it’s [your name], I’m in Mexico and all my cards are being declined. Could you send me $$?” (a message targeting your friends or loved ones)
“We noticed a login attempt from your location in [destination] — please confirm your identity.”
“Your reservation in [city] requires reconfirmation — click here to secure your booking.”
This is an example of a scam text detected by our research team. Now, imagine if scammers had more information, like the exact tour you were on, where you were, or the stores you shopped at. These details could make messages like this even more convincing and personalized.
These messages don’t need to be perfectly accurate. They just need to feel plausible and close enough. That is the entire strategy. Familiarity lowers skepticism. Skepticism is what protects you.
This is what turns mass phishing into hyper-personalized phishing at scale, and it’s why even cautious, digitally savvy travelers are getting caught.
The Scammer’s New Workflow
Here’s how straightforward this pipeline can become:
Find publicly shared travel photos on Instagram, Facebook, or X, no hacking required
Run them through a freely available AI vision model
Identify the likely destination, timeframe, and context
Craft a targeted message referencing that location
Send it during or shortly after the travel window, when the victim is most likely to believe it
Steps 1 through 5 can be automated. The whole process scales easily. And the resulting messages feel personal in a way that generic scams never could.
The Broader Scam Landscape Travelers Face
Geo-location inference doesn’t exist in a vacuum. It’s one tool in a growing arsenal that scammers deploy specifically against travelers.
Travelers are operating outside their normal routines, using unfamiliar networks, and making quick financial decisions under time pressure. These behaviors are exactly what make photo-based location inference more actionable for scammers.
New McAfee consumer research found that more than 1 in 3 Americans have encountered a travel-related cyberthreat, and 41% of those impacted lost money, often exceeding $500. At the same time, rising travel costs and time pressure are pushing people toward faster, riskier decisions. Those are exactly the conditions scammers are built to exploit.
The data reveals just how exposed travelers make themselves without realizing it. Nearly two-thirds of Americans connect to public Wi-Fi while traveling (63%), and a similar share scan QR codes without verifying where they lead (62%). Almost half use airport Wi-Fi specifically (49%), and 41% admit to trusting travel-related messages without checking the sender. One in five logs into financial apps while on public networks, and the same group shares travel plans in real time on social media. Twenty percent click travel-related links without verifying the source first. And finally, around 1 in 5 (22%) admit to sharing travel plans in real time.
That last behavior is worth pausing on. Sharing travel plans in real time, on public or semi-public social accounts, is precisely what creates the photo-based location signals this research examines. These behaviors and geo-location exposure are not separate issues. They feed each other.
Location inference is the key that makes all of those existing vulnerabilities more exploitable. A scammer with a rough idea of where you are does not just have a data point. They have a script.
Methodology: How We Conducted This Research
Transparency matters. Here is exactly how this research was conducted.
Dataset: 21,236 travel images that are publicly available for research, plus a separate controlled set of 102 images contributed by McAfee internal volunteers (never previously posted publicly).
Models tested:
Gemma3 27B — a multi-model and vision-language model from Google DeepMind
Qwen3 VL 30B — a multi-model and vision-language model from Alibaba’s Qwen team
It’s important to note that we conducted our testing using large language models running locally on our own computers, rather than through public services such as ChatGPT.
This more closely reflects how an attacker might operate at scale. Running models locally allows unrestricted, automated generation of large volumes of malicious content without relying on a third-party provider.
By contrast, cloud-based AI services typically monitor for abuse and may impose rate limits, suspend accounts, or block requests when they detect activity associated with phishing or other malicious behavior.
Process: An automated Python script submitted each image to both models using a standardized prompt requesting location identification based solely on visual content. No metadata, EXIF data, or file naming conventions were used as inputs. Results were logged programmatically.
Validation: Image labels were pre-assigned prior to analysis. In cases where geographic names or landmarks could reasonably be interpreted in more than one way, a human reviewer compared the pre-labeled locations and model outputs to ensure consistent categorization.
For example, the reviewer determined whether Vatican City should be grouped with Rome and whether “Washington D.C.” and “Washington, D.C.” should be treated as the same location. The reviewer did not alter either the original labels or the model results, but instead applied judgment to reconcile ambiguous naming conventions and edge cases.
Accuracy definition: A result was counted as correct when the model identified the correct city and country. Country-only identification was tracked separately. Both metrics are reported.
What this research does not claim: This research does not suggest that every travel photo will be correctly identified, or that all publicly available AI tools perform at this level. Results varied by image type, landmark density, and geographic region. The point is not perfect identification, it’s that accuracy is high enough, and accessible enough, to enable targeted scams at scale.
About the Consumer Research McAfee commissioned a consumer survey fielded in March 2026 examining travel intentions, travel scam experiences and perceptions, and digital behaviors while traveling. Results referenced here represent a subset of 1,000 U.S. adults over the age of 18. The full study included responses from 6,000 participants across Australia, France, Germany, Japan, the United States, and the United Kingdom.
How to Protect Yourself
Knowing the risk exists is the first step. Here’s what to actually do about it.
Think before you post, especially in real time. The highest-risk window is when you’re still traveling. Posting while you’re in a location gives scammers a live signal. When possible, post after you’ve returned home or delay sharing location-identifiable content by a few days.
Audit your social media privacy settings. Photos shared publicly are the easiest targets. Restricting your posts to people you know significantly limits the pool of images that can be scraped and analyzed.
Be skeptical of urgency tied to your location. If a message references where you’ve been, even correctly, treat that as a red flag, not a credibility signal. Scammers use location familiarity precisely because it feels reassuring.
Go directly to the source. If you receive a message claiming to be from your bank, airline, hotel, or card provider while traveling, don’t click any link in the message. Open a new browser tab and navigate directly to the company’s official website, or call the number on the back of your card.
Use a travel-specific email or alias. Some travelers use a separate email address for bookings, reservations, and travel apps. This limits the cross-referencing scammers can do between your social media presence and your financial accounts.
Trust the skepticism, not the familiarity. Modern scams are designed to feel familiar before they feel suspicious. If something creates a sense of urgency around your financial accounts while you’re traveling, slow down. The pressure itself is the warning sign.
How McAfee Protects You Before, During, and After Travel
As prices rise and decisions happen in real time, it’s easy to prioritize convenience over caution. But that’s exactly the moment when small checks matter most.
Stage of Travel
What’s Happening
How McAfee Helps
Before You Book
Comparing deals, clicking promotions, booking flights and hotels under time pressure
Scam Detector checks links, messages, and booking sites before you click, helping you avoid fake deals and scam listings
During Your Trip
Connecting to public Wi-Fi, scanning QR codes, receiving travel updates and alerts
VPN helps secure your connection on public Wi-Fi, while Scam Detector flags suspicious messages and unsafe links in real time
After Your Trip
Accounts remain active, travel data stored across platforms, potential exposure from breaches
Identity Monitoring alerts you if your personal information appears online, helping you act quickly before damage spreads
With McAfee+ Advanced, multiple layers work together so you’re not left figuring it out after the damage is done.
So you can focus on your trip, and not on whether that notification is a scam.
Final Thought
A travel photo is a memory. It’s also, increasingly, a data point.
That doesn’t mean you should stop sharing your experiences. It means understanding that the same visual richness that makes a great photo is exactly what AI systems are trained to read.
Scammers know this. Now you know how to protect yourself.
This report was produced by McAfee Labs. Research was conducted in 2025–2026 as part of McAfee’s ongoing monitoring of AI-enabled scam vectors.
McAfee Advanced Threat Research has identified an active browser-extension campaign designed to steal cryptocurrency by silently substituting wallet addresses the moment a user initiates a transaction. The campaign is delivered through unsigned installers — observed in both .NET and Golang variants — that deploy a malicious Chromium extension masquerading as a benign “Google Notes” utility.
This campaign is related to a previous blog published by McAfee Labs, Sinkholing CountLoader: Insights into Its Recent Campaign, as the threat actor appears to be the same behind both operations. In that earlier research, we analyzed a crypto clipper payload that was injected directly into memory. Here, we examine a different variant of the final-stage payload: a browser-based malicious extension designed to intercept and manipulate cryptocurrency transactions.
In this report, we detail how the extension operates and provide a technical analysis of the mechanisms that make this threat particularly unique. The extension behaves as a clipboard-aware crypto clipper: it monitors copy-and-paste activity, identifies wallet addresses across multiple blockchains, and swaps them for attacker-controlled addresses just before the victim pastes the content. Because most Blockchain transactions are irreversible, even a single uninterrupted execution is enough to cause permanent financial loss.
Two characteristics elevate this campaign above the typical clipper threat:
Chromium trust-layer abuse.The installer secretly forces a malicious browser extension into Chromium-based browsers like Google Chrome, Brave, and Microsoft Edge by modifying protected browser settings files. Normally, these browsers store security verification data (hash/HMAC values) alongside sensitive settings to detect unauthorized changes.The malware recalculates and updates these security values after tampering with the files, tricking the browser into believing the malicious extension was installed legitimately. This allows the extension to bypass the normal extension web store installation process and load silently without user approval. However for updated Chrome and edge browser, Victim must manually turn on the developer mode for the extension to load properly, but people with outdated versions of chromium based browsers, remain at high risk. Moreover, for latest versions as well threat attacker can employ social engineering tactics to enable developer mode.
Blockchain-resolved command-and-control. The extension does not contain a hardcoded C2 domain. Instead, it queries a public blockchain RPC endpoint, invokes a read-only smart-contract method, and decodes the response at runtime to reveal its active C2 observed at the time of analysis as Zebregts[.]com
This technique, often referred to as “EtherHiding,” complicates takedown efforts because the attacker can rotate infrastructure by updating a smart-contract value rather than redeploying malware.
McAfee telemetry indicates a globally distributed infection footprint with a pronounced concentration in India. The breadth of the geography suggests opportunistic targeting of consumer cryptocurrency users rather than a region-specific operation.
Geographical Prevalence
Our research shows that these are the most affected regions of the globe.
Telemetry analysis indicates thatinfections are globally distributed, with a significantly higher concentration observed in India compared to other regions.
The widespread geographic presence highlights the campaign’s broad reach, suggesting opportunistic targeting rather than a region-specific attack.
The Malicious Extension: “Google Notes”
This malware is masquerading as a seemingly harmless Google Notes extension.
Figure 1. This image shows the malicious extension at the center of this campaign
The dropped extension presents as a minimalist, legitimate-looking note-taking application branded as “Google Notes,” complete with a clean icon and a functional (& simplistic) user interface.
The cover is calculated: a user who manually opens the extension finds something that behaves as advertised, dampening suspicion. The extension’s malicious logic is implemented in background service-worker scripts and content scripts that operate entirely out of view of the UI.
A major red flag first appears when adding the extension, which requests securitypermissions and access that are disproportionate to a typical notes application:
Access to all URLs , granting content-script injection into every site the user visits.
Browsing history access.
Read and write access to the clipboard.
Mitigation and Recommendations
For Consumers
Before confirming any cryptocurrency transaction, visually verify the first and last six characters of the recipient address against the original source — ideally on a separate device. This single habit defeats the overwhelming majority of clipper attacks.
Install browser extensions exclusively from the official Chrome Web Store, Edge Add-ons store, or equivalent. An extension that appears in your installed list without a clear memory of having installed it should be treated as suspicious.
Review the permissions granted to every installed extension. A note-taking tool has no legitimate need for access to all websites, browsing history, or the clipboard.
Avoid running unsigned executables obtained from non-authoritative sources, particularly those offering free or cracked versions of paid software — a common delivery vector for this category of installer.
Keep endpoint protection up to date and enabled; McAfee customers are protected against this specific campaign as described below.
McAfee security solutions help safeguard users at multiple levels:
1. McAfee detects this threat as CryptoStealer.NE and keeps our customers safe
Figure 2. This image shows McAfee Antivirus blocking this threat for consumers.
2. Malicious Download Protection
The installer’s behavior—downloading and executing remote payloads—is flagged and blocked by McAfee before infection completes.All the malicious domains and URLs are blocked by McAfee in our tests.
3. Network Protection
Connections to known malicious infrastructure (C2 servers) are blocked by McAfee, preventing Wallet address retrieval
4. Real-Time Threat Intelligence
Because this threat was identified in McAfee telemetry, protections can be rapidly deployed to:
Block similar variants
Detect related infrastructure
Protect customers globally
How The Threat Campaign Works
What the Malware Does
Installs a browser extension silently (web extension sideloading)
Monitors what you copy and paste (especially crypto addresses)
Works when you are making a crypto transaction
Silently replaces the wallet address with the attacker’s address
Your funds are sent to the attacker instead of the intended recipient
Because cryptocurrency transactions are typically non-reversible, victims may permanently lose funds.
Figure 3. How the extension works in a nutshell
Key Capabilities Identified
1. Silent Extension Installation
The malware does not use the official browser store. Instead, it directly modifies browser files to make the extension appear installed. (Sideloading Browser Extension)
This bypasses normal security prompts and user awareness.
Figure 4. Procmon logs showing BaseZipInstaller (malicious web installer) writing into Chrome and Edge secure preference files
2. Full Browser Access
Figure 5. Chrome extension Permissions requiredFigure 6. Manifest file for web extension
The malicious extension requests excessive permissions such as:
Access to all websites
Reading browsing history
Reading and modifying clipboard content
3. Crypto Address Interception
The extension contains logic to detect wallet addresses across multiple cryptocurrencies, including:
Figure 7. Hardcoded cryptocurrency Regex and fallback address
The fallback wallet addresses shown in the code are not used for every transaction; instead, they serve as a backup mechanism when dynamic address retrieval from the attacker-controlled server fails.
Under normal operation, the extension fetches replacement addresses from a remote server, enabling dynamic and potentially per-victim wallet assignment.
Fallback addresses ensure the attack remains functional even if the command-and-control infrastructure is temporarily unavailable or blocked.
This function is responsible for obtaining the attacker-controlled replacement wallet address corresponding to a victim’s original address.
It sends the intercepted wallet address to the attacker backend and uses the response to dynamically substitute the original address.
If the backend request fails, the function falls back to a predefined hardcoded wallet address, ensuring uninterrupted malicious activity.
3J98t1Wxxxx is the address that was copied in the clipboard
4. Detection evasion and stealth
Figure 8. Settings.js file which shows config
The configuration includes a hardcoded API key, which is used by the extension to authenticate communication with attacker-controlled infrastructure.
An RPC URL pointing to a public blockchain node is leveraged to dynamically resolve backend server information, allowing the attacker to hide critical infrastructure behind decentralized systems.
The presence of a smart contract address and method indicates that the malware retrieves its command-and-control (C2) domain indirectly via blockchain queries, making takedown and tracking more difficult.
Blacklisted domains contains a list of blockchain inspection related websites where the web extension will not work , this is done to not alert the victim while he is trying to paste his own address and view the balance of his wallet or inspect his wallet transactions
Figure 9. Resolving attacker C2 domain via Ethereum smart contract (etherhiding)Figure 10. Request payload with Ethereum contract address
Dynamic analysis revealed that the malware resolves its command-and-control domain via a blockchain smart contract, which returned the domain devops-offensive[.]cc at runtime.
The response from the blockchain is decoded at runtime, revealing the active C2 domain (devops-offensive.cc).
This domain is not hardcoded, enabling the attacker to update infrastructure without modifying the malware.
The resolved domain is cached locally to maintain persistence and reduce repeated network queries.
Figure 11. This image shows the long-encoded string with the malicious domain
This Long–encoded string is decoded using this function to give the final attacker domain.
Figure 12. This image shows the final attacker domain
Persistence and Evasion Techniques
The campaign’s persistence and evasion posture is deliberate and layered. The operator has clearly optimized for two properties: low visibility to the end user, and high resilience against takedown and static analysis.
Persistence
Extension registration through Secure Preferences tampering ensures the extension loads on every subsequent browser launch without requiring any auxiliary Windows persistence mechanism — no registry Run keys, scheduled tasks, or services that endpoint hunters typically inspect.
Developer mode is enabled programmatically where required, allowing unpacked extensions to persist without triggering the periodic “unpacked extensions warning” flow that Chromium displays to dissuade sideloading.
The cached C2 domain allows the extension to continue operating against a known-good backend even if the blockchain RPC endpoint is briefly unavailable.
Evasion
The extension’s visible identity — a simple “Google Notes” note-taking application — provides plausible cover against casual inspection of the installed extensions list.
Recomputed HMAC values satisfy Chromium’s integrity verification, avoiding the “extension installed by an unknown source” warning banner that would otherwise alert the user.
The installer self-deletes after execution, removing the most obvious on-disk indicator of initial compromise.
C2 resolution through a public blockchain means that there is no persistent C2 domain observable in the malware bundle itself; network-based detections built against hardcoded indicators will not fire until the domain is resolved and contacted.
Multi-language installer variants (.NET and Golang) reduce the effectiveness of compile-artifact and binary-feature signatures.
Per-address dynamic wallet substitution means that published attacker addresses age rapidly and do not generalize into durable blocklist entries — the defender must block the backend service itself, not the addresses it dispenses.
Wallet Substitution Logic
The clipper logic sits in two layers: a content-script layer that monitors clipboard activity and DOM input fields across every visited origin, and a background layer that communicates with the attacker backend to retrieve replacement addresses.
When the extension observes a copy event, it applies a set of cryptocurrency-specific regular expressions to the clipboard payload. If a match is found, the intercepted address is transmitted to the attacker’s backend over an authenticated request (authenticated with the API key embedded in the configuration). The backend responds with a replacement address specific to the submitted original, and that replacement is written back to the clipboard, overwriting the legitimate address before the victim can paste.
Testing against a reconstructed backend client — built by re-implementing the extension’s request format and response-decoding logic in Python — produced a revealing behavioural profile:
Bitcoin (BTC), Ethereum, Bitcoin Cash, Ripple, and Dash: Each submitted address is mapped to a unique attacker-controlled address. Re-submitting the same original returns the same replacement, indicating a deterministic one-to-one mapping maintained server-side.
Solana: All submitted addresses collapse to a single attacker address, suggesting the per-victim mapping feature is selectively implemented per chain
Analyzing Attacker Crypto Wallets
Based on the code snippets from the web extension responsible for retrieving replacement addresses, a Python script was prepared to programmatically extract attacker wallet addresses. The payload was crafted using the attacker’s own code, and the “get replacement address” snippet was lifted directly from it. The attacker’s logic for decoding data received from the C2 server was also faithfully reimplemented in the script.
The script was then executed using a few test Bitcoin (BTC) wallet addresses. The results showed that for every Bitcoin address provided, a unique Bitcoin address was returned in response, and all of these returned addresses were valid BTC wallets. This indicates that for every BTC address supplied, the attacker dynamically generates a new wallet tied to that specific input address. Furthermore, when the same address was provided again, the same BTC address was returned — confirming that each victim BTC address is deterministically mapped to a single, specific attacker-controlled address. While some of these attacker wallets contained funds and others were empty, the unknown total number of attacker wallets makes it difficult to put a reliable estimate on how much cryptocurrency has been stolen overall.
The same behavior was observed for Ethereum, where different wallet addresses were returned for each input. Interestingly, when the script was tested with Solana addresses, only a single address was returned regardless of how many different inputs were provided. This suggests that the attacker has implemented the per-address mapping feature only for specific cryptocurrencies, while others fall back to a single static drop wallet. Because the Solana address is shared across all victims, a noticeable bump in its balance is visible. Additionally, one of the Ethereum addresses uncovered was found to be holding approximately 1,902 USD worth of funds.
In summary, the cryptocurrencies for which unique per-victim wallet addresses are generated include Bitcoin, Ethereum, Bitcoin Cash, Ripple, and Dash.
Fig 13. Payload was crafted as attacker codeFig 14. Getting the replacement address code snippet taken from attacker codeFig 15. Attackers’ logic of decoding received data from C2 was also implemented
Running script with few test Bitcoin Wallet addresses
Fig 16. Every unique Bitcoin address was returned and all addresses are valid BTC wallet addressesFig 17. Similarly, Ethereum saw unique addressesFigure 18: Running Script for Test Solana Addresses
Luckily for Solana we are getting only 1 address when given multiple addresses. This shows that the attacker has implemented this address mapping feature only on specific cryptocurrencies
Fig. 19 Here you can see a bump in the balance amountFig 20. The ETH address was found to have 1902 USD
Technical Analysis for .net file (Extension installer)
Fig. 21 BaseZipInstaller is a .NET installer which is unsigned
Fig. 22 Stored Config as seen in Dnspy
The malware embeds a complete configuration JSON directly within the binary, eliminating the need to fetch initial setup data from external sources.
This embedded configuration includes critical details such as API keys, backend server URL, targeted wallet extensions, and the full extension manifest with extensive permissions.
Fig 23: Main function from where execution starts
The installer retrieves and validates a remote ZIP archive (google-services[.]cc/base[.]zip), which serves as the primary payload for deploying the malicious browser extension, marking the transition from initial infection to browser-level compromise.
Fig. 24 The extension is created at the following location in the system with files that are downloaded as base.zip.Fig. 25: Dnspy showing the list of targeted browsers
The installer iterates through multiple Chromium-based browsers, including Chrome, Edge, Opera, and Brave, identifying available user profiles on the system.
For each detected profile, the malware forcibly terminates the browser process to safely modify configuration files without interference.
It then injects the malicious extension by directly modifying Secure Preferences and Preferences, enabling the extension to be loaded without user interaction.
The malware identifies browser installation paths by querying standard system directories, enabling it to locate user data folders for Chrome, Edge, Opera, and Brave.
It systematically enumerates browser profiles and specifically looks for the presence of the Secure Preferences file, which stores critical browser configuration and extension data.
By targeting profiles with Secure Preferences, the malware ensures it modifies only valid browser environments, increasing the reliability of extension injection.
We can see writefile Event on Secure preferences file of chrome and MS Edge , when details of downloaded extension are written to those config filesFig 27 Attacker logic to resign the secure preference files
The malware reads and modifies the browser’s Secure Preferences file, which controls installed extensions and their trust state.
It injects the malicious extension into the configuration and attempts to re-sign the modified data, making the changes appear legitimate to the browser’s integrity checks.
The updated configuration is then written back to disk, ensuring the extension is loaded automatically and persists across browser restarts.
Fig 27B :Extension path is added to chrome secure preferences fileFig 28: Logic to Manipulate defenses of Brave Bowser
For browsers such as Brave and Opera, the malware injects the malicious extension directly into the browser’s configuration by adding entries under the extensions.settings (or extensions.opsettings) section.
It also updates integrity-related fields (protection.macs) to make the injected extension appear trusted by the browser.
Additionally, the malware attempts to enable developer mode programmatically, allowing unpacked extensions to run with fewer restrictions.
Fig 29: Attacker logic to get device ID used to further calculate integrity Values
The malware attempts to recompute browser integrity signatures by generating new MAC (Message Authentication Code) values for the modified Secure Preferences file.
It uses system-specific identifiers, such as the machine SID, combined with a seed value to mimic Chrome’s internal verification mechanism.
By recalculating these integrity checks (macs and super_mac), the malware tries to make its unauthorized modifications appear legitimate to the browser.
Figure 30 Self-Deletion Logic
The malware includes a self-deletion mechanism designed to remove the installer executable after successful execution.
It launches a hidden command prompt process that delays execution briefly before deleting the original file from disk.
Conclusion
This campaign is a concise illustration of where consumer-targeted cryptocurrency theft is heading. The operator has taken the oldest and simplest category of crypto malware — the clipper — and quietly upgraded three of its weakest links. Static attacker addresses have been replaced with a server-side, per-victim mapping. Fragile, hardcoded command-and-control domains have been replaced with a blockchain-resolved lookup that an operator can rotate with a single transaction. And a fragile dropper has been replaced with a Chromium extension that lives inside the user’s most trusted application, loaded under the browser’s own integrity signature.
McAfee will continue to track this campaign and related infrastructure. Our customers are protected by existing detections and will benefit from telemetry-driven updates as new variants and rotated infrastructure are identified.
Maybe it’s a birthday gift. Maybe it’s a purchase from a major shopping event. Maybe it’s something you forgot you ordered three days ago.
Then your phone buzzes.
Your package couldn’t be delivered.There’s a problem with your shipping address.
A small fee is required before delivery can continue.
“Click here immediately.”
The message feels plausible because so many of us are constantly waiting for packages. And scammers know it.
According to McAfee’s State of the Scamiverse report, fake delivery and shipping notices are the single most commonly reported scam consumers encounter today, with 31% of people saying they’ve received one. Americans also receive an average of 14 scam messages every day across texts, email, social media, phone calls, and other channels.
Delivery scams have become one of the internet’s most successful forms of phishing because they exploit something simple: people are already expecting the message.
Here’s how to spot and stop these scams:
What Is a Delivery Scam?
A delivery scam is a fraudulent message that pretends to come from a shipping company, retailer, postal service, or delivery provider.
The goal is usually one of three things:
Steal personal information
Steal financial information
Trick victims into downloading malware or visiting malicious websites
These scams often impersonate organizations such as:
USPS
UPS
FedEx
DHL
Amazon
Royal Mail
Australia Post
Other local or regional delivery services
Most delivery scams arrive through text messages, which is why they’re often called package smishing scams.
What Is Smishing?
Smishing is a type of phishing attack delivered through SMS text messages.
The term combines:
SMS (Short Message Service)
Phishing
Instead of arriving through email, the scam arrives directly on your phone and attempts to create a sense of urgency that encourages immediate action.
Common examples include:
“Your package could not be delivered.”
“Delivery attempt failed.”
“Update your shipping address.”
“Pay a small customs fee.”
“Confirm delivery information.”
McAfee’s Scam Detector lets you know when delivery messages are scams.
Delivery Scam Red Flags and What to Do
If You See This Red Flag
Why It’s Suspicious
What To Do
A package alert when you’re not expecting a delivery
Scammers send messages in bulk hoping someone is waiting for a package
Ignore the message and do not click links
A request to pay a small fee before delivery
Legitimate carriers rarely collect delivery fees through text messages
Visit the carrier’s official website directly
A message claiming your address needs verification
Common tactic used to steal personal information
Check shipment status through your retailer or carrier account
A shortened or unusual link
Scammers often disguise malicious websites
Avoid clicking and manually type the carrier’s website address
Pressure to act immediately
Urgency is designed to override caution
Pause and verify independently
Requests for passwords, payment information, or verification codes
Legitimate carriers will not ask for this through text messages
Delete the message and report it as spam
A delivery app or file download request
May install malware on your device
Never download software from a text message
Accidentally Clicked a Delivery Scam? Do This Immediately
What Happened
What To Do
You only clicked the link
Close the page and do not enter any information
You entered login credentials
Change your password immediately and enable two-factor authentication
You entered payment information
Contact your bank or credit card provider right away
You downloaded a file or app
Delete it and run a security scan
You’re unsure what information was exposed
Monitor accounts closely for unusual activity
How McAfee Can Help
With McAfee+, multiple layers work together before any damage is done:
Scam Detector flags suspicious texts, emails, links, QR codes, and even deepfake videos before you engage
Secure VPN keeps your data private, especially on public Wi-Fi
Web Protection helps block risky sites, even if you do accidentally click helps block risky sites, even if you do accidentally click
Password Manager doesn’t just help you make unique, strong passwords, it keeps them stored and organized for you
The takeaway is simple: some of the biggest threats facing gamers aren’t happening inside games. They’re hiding in the downloads, websites, and tools players use around them.
Let’s start with the GTA breach.
GTA Cheat Service Breach Exposes Nearly 64,000 Users
Atlas Menu, a cheat service for Grand Theft Auto V, was reportedly hacked, exposing data belonging to nearly 64,000 users.
According to reports, the leaked information included:
Email addresses
Usernames
Scrambled passwords
IP addresses
Customer support tickets
The hacker who claimed responsibility later posted the data online.
Why This Matters
Many players think of cheats as harmless tools that unlock special abilities, provide advantages, or simply make games more entertaining.
But unofficial cheat services often operate outside the protections offered by legitimate gaming platforms.
That means users may be:
Sharing personal information with unknown developers
Downloading unverified software
Exposing themselves to malware
Putting gaming accounts at risk
And that brings us to an even bigger threat.
Minecraft Malware Campaign Has Already Infected 116,000 Players
McAfee researchers recently uncovered a large-scale malware operation targeting gamers searching for Minecraft mods, clients, and cheats.
The campaign is called WeedHack.
What Is WeedHack?
WeedHack is a type of Malware-as-a-Service (MaaS).
That means cybercriminals package malware into a subscription service that other attackers can use.
Researchers found that:
More than 116,000 victims have been infected since January
The campaign continues to add roughly 2,000 to 3,000 new victims every day
More than 3,800 malicious files have been identified
More than 240 malicious download URLs have been linked to the operation
Premium versions reportedly cost as little as $5 per month and include tools that allow attackers to remotely access victims’ devices and webcams.
Online Account Cleanup assists in taking down your old, forgotten accounts across the web
Social Privacy Manager helps you monitor and changeprivacy settings across your social platforms in just a few clicks
Together, these protections are designed to address the broader range of online risks people face every day.
Other Scam and Cybersecurity News This Week
Here are some other important headlines to be aware of:
Carnival Data Breach Impacts Nearly 6 Million Customers
Carnival Corporation disclosed a data breach affecting nearly six million customers after a social engineering attack allowed an unauthorized individual to gain access to part of the company’s IT systems.
Exposed information may include:
Names
Addresses
Email addresses
Phone numbers
Dates of birth
Government-issued identification numbers
Affected customers should be alert for phishing emails, fake customer support calls, and identity theft attempts.
Instagram AI Support Tool Exploit Raises Security Questions
Instagram says it has fixed an issue that reportedly allowed attackers to manipulate its AI-powered support chatbot and gain access to other users’ accounts.
According to reports, attackers were allegedly able to influence the account recovery process and associate new email addresses with targeted accounts.
The incident highlights a growing challenge for AI-powered customer support systems: convenience cannot come at the expense of identity verification.
AI Voice Cloning Scams Continue to Surge
Voice cloning scams continue to grow as AI tools make it easier than ever to imitate friends, family members, and coworkers.
According to FBI data cited this week, Americans lost more than $893 million to AI-related scams last year.
These scams included:
Voice cloning attacks
AI-generated phishing emails
Romance scams
Other AI-assisted fraud schemes
If someone calls claiming to be a loved one in distress and urgently requests money, verify the situation through another communication channel before taking action.
McAfee Safety Tips This Week
Whether you’re downloading a Minecraft mod or answering an unexpected phone call, the same rule applies:
Slow down before you click, download, or share information.
Here are a few ways to stay safer:
Download mods, clients, and game tools only from trusted sources.
Be skeptical of download links shared in YouTube comments, Discord servers, or social media posts.
Never disable antivirus software to install a game mod.
Enable multi-factor authentication on gaming, Discord, and email accounts.
Use unique passwords for gaming accounts.
Treat “free cheats,” exclusive hacks, and too-good-to-be-true downloads with caution.
We’ll be back next week with more scams making headlines.
McAfee Labs has discovered a massive, ongoing malware campaign called WeedHack that disguises itself as free Minecraft mods and game clients to infect players’ computers. Since January 2026, it has logged more than 116,000 victim infections, averaging 2,000 to 3,000 new hits every single day.
What makes WeedHack different from most malware is how cheap and easy it is to use.
Typically, a hacker would pay hundreds of dollars per month to access attack tools through underground criminal networks. WeedHack offers a free version to anyone with a Discord account and an internet connection. A premium upgrade, which includes the ability to secretly watch victims through their own webcam, starts at just $5 a month.
This low barrier has attracted a younger crowd of would-be attackers, many of them appear to be teenagers or young adults. Our researchers were startled to discover teens using these tools not just for financial theft, but to harass and bully their peers, a pattern we’ve documented and that makes this campaign especially concerning.
The good news for McAfee users: Web Protection actively blocks the sites distributing WeedHack, and Threat Explainer tells you exactly why a flagged file is dangerous, so you’re never left guessing.
Key Facts at a Glance
What
Details
Campaign name
WeedHack
Active since
January 2026
Total victims logged
116,464+
New infections per day
~2,000–3,000
Malicious files discovered
3,820+ unique files
Malicious download URLs
240+
Free tier available?
Yes. Anyone can sign up
Premium price
Starting at $5/month; $24.99 lifetime
Who is being targeted
Minecraft players worldwide
Most affected country
United States, followed by Germany, India, the UK, Italy, and others
What attackers can access
Once installed, it can steal passwords, hijack accounts, and, for paying customers, it can give the attacker live access to the victim’s screen, webcam, and files.
The financial impact
It can steal Discord tokens, crypto wallet credentials, Minecraft account credentials.
Hackers will hold your information for ransom, requiring a large payment in exchange for your data.
WeedHack is a Malware-as-a-Service (MaaS) campaign, meaning it’s a criminal business that sells hacking tools to customers, the same way a legitimate software company sells subscriptions.
The “product” is malware that gets secretly installed on a victim’s computer when they download what they think is a Minecraft mod or client. Once installed, it can steal passwords, hijack accounts, and, for paying customers, it can give the attacker live access to the victim’s screen, webcam, and files.
The campaign operates a polished, professional-looking dashboard hosted openly on the internet (not the dark web). That dashboard lets customers track their victims, download stolen data, and launch remote access features, all from a browser.
What it looks like to buy a subscription from WeedHack.
The Cyberbullying Problem
One of the most disturbing findings from our investigation is how WeedHack is being used.
While monitoring the campaign’s Telegram channel, which had over850 members during the time of our research, we observed that many customers appear to be teenagers and young adults, and a significant portion are using the remote access tools not for financial gain, but to harass and intimidate other players.
We observed attackers recording victims through their webcams without consent and sharing those recordings in the Telegram channel as trophies. Others used knowledge of victims’ IP addresses and system access to threaten them.
It’s important to note that, at the current time of publishing, the Telegram channel has been taken down, and no replacement channel has appeared. McAfee is continuing to monitor any new channels that may be established by the threat actors for further communication.
Still, what we observed is a form of cyberbullying with unusually invasive tools behind it. If you or your child has been contacted by someone online claiming they have hacked your computer, have your webcam footage, or know your IP address, take it seriously.
What to do if this happens:
Do not follow the attacker’s instructions, it makes things worse
Tell a trusted adult immediately (parent, guardian, school counselor)
Contact your local law enforcement, this may constitute criminal conduct.
Do not engage with the attacker or attempt to negotiate
The Telegram channel uncovered by McAfee.
How Do People Get Infected?
WeedHack spreads in two main ways, and the campaign even provides its customers with step-by-step tutorials on how to carry out both.
1. Fake YouTube Videos
Attackers create convincing YouTube videos reviewing or demonstrating Minecraft clients and mods.
The videos are well-produced, some include voiceover narration, and link to malicious download sites in the description and comments.
One video McAfee identified had over 7,500 views before being flagged. Comments are also sometimes planted by the attackers claiming the files are safe.
2. Fake Mod Websites
WeedHack instructs customers to build convincing-looking websites that mimic official Minecraft mod pages. These sites are deliberately designed to show up high in search engine results for popular mod names, a tactic called SEO poisoning.
Some fake sites include fake security warnings, Discord links, and GitHub references to appear legitimate. In one case, a site warned players to “only download from us,” while actively distributing malware.
Minecraft clients and mods specifically targeted include: Meteor Client, Radium Client, Wurst Client, LiquidBounce, Impact Client, Future Client, and others.
An example of a video hiding a malicious link in the description.
What Happens When You’re Infected?
Infection happens in four stages that happen silently in the background after a victim opens the downloaded file.
Stage 1 – First Contact: The malicious file launches quietly (without showing a console window), connects to a hidden network, and phones home to receive further instructions. It uses a sophisticated technique involving the Ethereum blockchain to locate its command server in a way that’s difficult to block or take down.
Stage 2 – Taking Hold: The malware disables Windows Defender protections, gathers detailed information about the victim’s computer (processor, graphics card, RAM, operating system), and takes a screenshot of their screen. It then steals Discord tokens and browser passwords and cookies. For McAfee users, this is where Web Protection would prevent users from visiting the site, and where our Antivirus would prevent any downloaded malware from taking hold.
Stage 3 – Digging In: The malware installs itself so that it automatically restarts every time the victim logs into their computer. It sets up a hidden scheduled task that runs continuously, even at the highest system privileges.
Stage 4 – Full Access: For premium customers, an additional component is installed that connects the attacker to the victim’s computer in real time. This includes live screen sharing with keyboard and mouse control, webcam access, keylogging (recording every keystroke), a reverse shell (full command-line access to the computer), and the ability to upload or download any files.
A separate component specifically hunts for Telegram credentials and cryptocurrency wallets, sending that data to a different server every five minutes.
Minecraft’s mod ecosystem is enormous and largely unregulated. Kids routinely search YouTube and Google for performance-boosting clients, cosmetic mods, and gameplay cheats, exactly the kinds of things WeedHack exploits.
Here’s a practical guide for families:
Red Flag
Safe Practice
The mod isn’t on the developer’s official website
Only download from CurseForge, Modrinth, or the mod’s verified GitHub
A site or video tells you to disable your antivirus to run the file
Never disable antivirus for a game mod. Legitimate mods don’t ask you to
A site you’ve never heard of claims to be the “only official” source
If you can’t verify the site is official, don’t download from it
Download links are in YouTube comment sections
Treat comment section links as a red flag, always
Your antivirus flags a file as malware, but they try to tell you to ignore it, it’s a “false alarm”
Use McAfee’s Threat Explainer to find out why this is malicious. Don’t disable antivirus
One of the best ways parents can protect their families is with McAfee’s award-winning antivirus and Web Protection, which are specifically designed to detect threats like WeedHack and help block malicious downloads before a device can be compromised.
Are McAfee Users Protected?
McAfee has been actively tracking WeedHack samples and detects this threat under the following signatures:
Trojan:Win/Weedhack.AA through Trojan:Win/Weedhack.AE
McAfee provides multiple layers of protection against threats like WeedHack.
Web Protection helps block access to malicious websites distributing infected Minecraft mods, stopping the threat before a file is ever downloaded.
Award-winning antivirus detects and blocks malware if a malicious file does make it onto your device.
Threat Explainer shows exactly why a file was flagged, helping users understand what happened and avoid similar scams in the future.
Together, these protections help proactively block risky downloads, reactively stop malware, and explain what to watch for next.
McAfee Labs continues to monitor WeedHack and will update coverage as new samples and domains are identified. For the full technical report including indicators of compromise, see the McAfee Labs analysis.
Key Terms Explained
Term
What it means
Malware-as-a-Service (MaaS)
A criminal business model where hackers sell or rent attack tools to other people, just like a software subscription
RAT (Remote Access Trojan)
Malware that gives an attacker remote control over a victim’s device — screen, files, camera, and more
Infostealer
Malware designed to silently collect and transmit passwords, cookies, and account credentials
SEO Poisoning
Manipulating search engine results so a malicious website appears near the top when someone searches for a legitimate product
Minecraft Client/Mod
Third-party software that modifies or enhances the Minecraft game experience. Legitimate ones are common; WeedHack fakes them
Minecraft Session ID
A token that proves you’re logged into Minecraft. Stealing it lets an attacker take over your account without your password
Keylogger
Software that secretly records every key a person types — including passwords, messages, and search queries
Reverse Shell
A connection from the victim’s computer back to the attacker that gives the attacker full command-line control
EtherHiding
A technique that hides a malware’s server address inside the Ethereum blockchain, making it very difficult to block
Discord Token
A credential that lets someone access your Discord account. Stealing it gives attackers full access without needing your password
Minecraft is a 2011 sandbox game developed and published by Mojang Studios. It is the best-selling video game in the world and has sold over 350 million copies worldwide. Its popularity has spanned over a decade due to its versatile gameplay, offering multiple game modes, including one of the most memorable Story Mode in gaming history.
It allows players to create and host multiplayer servers with a variety of gameplay options and offers a wide range of custom launchers, game mods, and cheats to choose from.
Its massive popularity and widespread use of third-party tools have also given rise to a dark side of the Minecraft ecosystem, which is filled with Remote Access Trojans (RATs), credential stealers, keyloggers and other malware threats.
McAfee Labs has recently uncovered a colossal Minecraft-focused Malware-as-a-Service (MaaS) campaign named ‘Weedhack’, that allows threat actors to remotely access and manipulate the victims’ screen, webcam and file system through a dashboard hosted on the clear net, making it easily accessible to anyone with a Discord account and an internet connection.
Key Findings
‘Weedhack’ has been active since January 2026 and masquerades as genuine Minecraft clients and mods to infect users.
We’ve discovered over 3820 unique malicious JAR files that are part of this attack and over 240 URLs responsible for distributing this malware.
This campaign utilizes SEO poisoning and YouTube to generate traffic to these malicious URLs. We also found two YouTube channels and multiple videos that demonstrate Minecraft Mods and Clients and redirect viewers to these URLs.
The campaign has accumulated a total of 116,464 hits, averaging approximately 2000 to 3,000 hits per day.
The campaign provides an enterprise-grade dashboard that allows customers to view stolen credentials and system information, download the payload, configure notifications, access tutorials, and remotely monitor their victims.
This campaign deploys EtherHiding, a technique that uses Ethereum blockchain to fetch its latest C2 domain. The responses are RSA-signed and verified before execution, helping protect the network from campaign takeover attempts.
We’ve uncovered 10 domains that host the next stage payloads and host the malware dashboard for the Weedhack campaign.
We’ve identified 11 domains that hosted similar MaaS campaigns in the past, orchestrated by the same threat actor.
We’ve unearthed the threat actor’s Telegram account and uncovered a Telegram channel for customers, with over 850 members, as of writing this blog.
This campaign offers two service tiers: free and premium.
The free tier includes a comprehensive infostealer capable of targeting Minecraft session IDs and four Minecraft launchers, collecting system information, and stealing cookies and passwords from 36 different browsers. It also targets 56 browser-based crypto wallets and 12 desktop crypto wallets, along with Discord, Steam, and Telegram credentials. It can search for files using 24 different keywords and includes screenshot capture capabilities.
For premium users, with subscriptions starting at $5 per month, it offers additional remote-access capabilities such as webcam access, keylogging, reverse shell execution, screen sharing with keyboard and mouse access, and file management features for uploading and downloading files.
While monitoring the Telegram channel, we found that WeedHack malware is a major catalyst for cyberbullying. Many of its customers appear to be teenagers and young adults and are using remote access capabilities to threaten, harass and monitor their victims, which are around the same age.
Memorial Day weekend officially kicks off summer, and for millions of Americans, that means road trips, flights, cookouts, and a little online shopping for the deals.
Unfortunately, scammers know this. They count on the fact that you’re distracted, you’re moving fast, and you’re probably connected to a network you don’t own.
Here are five scams surging this holiday weekend, what they look like, and how to stay ahead of them.
1. Fake Travel Alerts from “Your Bank” or Hotel
You’re packing your bag when a text arrives: “Unusual activity detected on your account. Verify now to avoid suspension.”
It looks like it’s from your bank, or maybe your hotel loyalty program. There’s a link. There’s urgency. And that’s exactly the point.
These are brand impersonation scams, and they’re a dominant tactic year-round, but they spike around travel holidays when people are actively monitoring reservations and accounts.
Example of a fraudulent AMEX message.
According to McAfee research, trusted brands like banks, airlines, and hotels are among the most commonly impersonated, and email scams impersonating retail and financial brands have surged up to 85% as major holidays approach.
The message will typically ask you to click a link and “confirm your details” to secure your account or honor a reservation. That link leads to a convincing-looking fake site designed to capture your login credentials, payment info, or both.
How to Avoid Travel Alert Scams:
Don’t click links in unsolicited texts or emails.
Go directly to the company’s app or website by typing the URL yourself.
Remember: pressure is a tactic, not customer service.
McAfee’s Scam Detector can flag suspicious messages before you interact with them, whether they come via text, email, or social media.
2. Fake Memorial Day Weekend “Deals”
Memorial Day is one of the biggest shopping weekends of the year. Scammers treat it like an open invitation.
Fraudulent retailers flood social feeds with too-good-to-be-true deals on everything from patio furniture to electronics, often impersonating legitimate brands with copycat websites and paid ads.
According to McAfee’s holiday shopping research, 91% of shoppers see ads from unfamiliar retailers, 37% say they might buy from a brand they don’t recognize, and a full 40% of consumers have abandoned a purchase out of fear that the deal wasn’t real.
The most impersonated brands in McAfee’s research span luxury labels (Coach, Dior, Gucci) to mainstream favorites (Apple, Samsung, Nintendo, Disney), exactly the kind of items that show up in “blowout sale” ads. Fake storefronts have grown significantly, with technology URL scams rising nearly 50%.
Once shoppers enter their payment details on a fraudulent site, that information goes directly to criminals. The average scam loss during the holiday shopping period runs around $840 per victim.
How to Avoid Shopping Scams:
Type retailer URLs directly into your browser instead of clicking through ads or social posts.
Look for HTTPS and double-check the domain carefully before entering any payment info.
If a deal looks unbelievably good, verify it on the retailer’s official app before buying.
McAfee’s Web Protection blocks malicious and suspicious sites before they load, including fake checkout pages.
3. QR Code Scams at Gas Stations and Travel Stops
If you’re road-tripping this weekend, you may scan a QR code somewhere. It could be at the gas pump, a rest stop, a parking meter, or a roadside attraction. Scammers know this too.
Criminals increasingly place fake QR codes over legitimate ones on gas station pumps, parking kiosks, and public signs. When you scan, you’re redirected to a convincing-looking payment or login page that captures your financial information. This is known as “quishing” or phishing via QR code.
McAfee research shows just how widespread this risk has become: 68% of people scanned a QR code in the past three months, and 18% ended up on a suspicious or unsafe page after scanning. Among those who did, more than half took a risky action like entering personal information, installing an app, or connecting a digital wallet.
How to Avoid Sketchy QR Codes:
Before scanning any QR code in public, look closely at the sticker or sign.
If it looks like it’s been placed over something else, skip it.
If you do scan, check the URL before proceeding.
McAfee’s Scam Detector now includes instant QR code safety checks that assess risk before you tap, so you’re not flying blind at the gas pump.
This shows how McAfee blocks unsafe QR codes.
4. Public Wi-Fi Traps at Airports, Hotels, and Coffee Shops
Whether you’re waiting at the airport or grabbing coffee before hitting the highway, free Wi-Fi can feel like a gift. But not every “free Wi-Fi” network is what it appears to be.
Hackers set up what are called “evil twin” networks, hotspots with names designed to look exactly like the legitimate network at the airport, hotel, or café you’re in.
The moment you connect, they can use tools called packet sniffers to capture the data you send and receive: passwords, banking credentials, credit card numbers, email logins.
According to McAfee’s travel research, 63% of travelers connect to public Wi-Fi, and 49% use airport Wi-Fi, making these among the riskiest behaviors travelers engage in without realizing it.
Some of these fake networks go further, presenting a phony login screen that captures your username and password for popular services like Google or Apple before you even realize you’ve been compromised.
How to Avoid Malicious Wi-Fi :
Always confirm the exact Wi-Fi network name with staff before connecting.
Turn off auto-join for Wi-Fi on your devices.
And most importantly: use a VPN.
A VPN creates an encrypted tunnel for your internet traffic, so even if a hacker intercepts it, they’ll only see scrambled data. McAfee’s VPN is included in McAfee+ plans and automatically connects when you join public Wi-Fi, exactly the protection you want when you’re traveling and connecting everywhere.
5. Toll Road and Parking Text Scams (Expect a Surge After the Weekend)
You may have seen these already: a text that says you owe an unpaid toll or parking fee, with a link to pay before penalties kick in. These scams have been circulating for a while, and there’s a good chance Memorial Day weekend is about to make them worse.
Scammers track news cycles and know that millions of Americans will be driving this weekend, many of them through toll roads and unfamiliar areas.
That means they can blast out fake “unpaid toll” texts after the holiday and a significant percentage of recipients will think: “Actually, I did drive somewhere new this weekend.” That uncertainty is exactly what they’re counting on.
Fake court notices threatening parking and toll violations have been making the rounds this spring.
These texts typically impersonate EZPass, SunPass, or state transportation departments and create urgency around a small fee to avoid larger fines. The link leads to a fake payment page designed to steal your credit card details.
How to Avoid Toll Scams:
Don’t click links in unsolicited toll or parking texts.
If you think the charge might be legitimate, go directly to your state’s official toll authority website and look up your account there.
Real toll agencies will not threaten immediate penalties over text with a payment link.
If you receive one of these texts after this weekend, treat it as suspicious by default.
Have a Safe Memorial Day Weekend
Scammers don’t take holidays. If anything, long weekends are peak season. The good news: a little awareness goes a long way. Slow down before you click, verify before you scan, and protect your connection before you log on.
McAfee+ Advanced comes with layered protection across all the moments where scams are most likely to strike, from the gas station to the hotel lobby to your inbox.
You’re comparing airfare on your phone, watching prices climb by the hour, when a deal pops up that feels just good enough to grab. The timer’s ticking. The price looks right. You don’t want to miss it.
You’re comparing airfare on your phone, watching prices climb by the hour, when a deal pops up that feels just good enough to grab. The timer’s ticking. The price looks right. You don’t want to miss it.
That moment, when you’re rushing to lock something in, is exactly where scams thrive.
New McAfee research shows that more than 1 in 3 Americans have encountered a travel-related cyberthreat, and 41% of those impacted lost money, often exceeding $500.
This shows a screenshot of a fake Booking.com website detected by McAfee that was attempting to trick users into running malicious script/code
At the same time, rising travel costs and time pressure are pushing people to make faster, riskier decisions. Those arethe exact conditions scammers rely on.
That’s where protection has toshow up earlier.
McAfee’s Scam Detector lets you check suspicious links, messages, and booking sites before you click, so you can pause and verify instead of giving scammers the edge.
Travel Scams, Red Flags, and How McAfee Protects You
Travel Scam Type
Key Red Flags
How McAfee Helps
Fake travel deals
Prices far below market, pressure to “book now,” sites you’ve never heard of
Scam Detector flags suspicious links and explains why they’re risky, so you can avoid fake deals before you book
Fake booking confirmations
Unexpected messages about bookings you didn’t make, mismatched sender details
Scam Detector analyzes messages before you engage, helping you avoid fake confirmations
Fake airline/hotel websites
Slight URL changes, poor design, being pushed to pay immediately or off-platform
Safe Browsing helps block risky sites before you enter payment details, reducing the chance of fraud
Payment requests outside platforms
Asked to pay via wire transfer, crypto, or direct payment instead of official platforms
Scam Detector flags suspicious payment requests, helping you avoid sending money to scammers
QR code scams
QR codes posted in public with no clear source or context
Scam Detector checks QR links before they open, so you don’t land on malicious sites
Customer service impersonation
Calls or messages asking for login credentials or payment info
Scam Detector detects deepfake AI audio impersonation attempts, helping you avoid sharing sensitive information
AI-generated listings
Photos that look overly polished, details that don’t quite match up
Scam Detector identifies suspicious content patterns, helping you spot listings that aren’t real
Public Wi-Fi attacks
Open networks with no password or security prompts
VPN helps protect your data on public networks, keeping your personal information private
The Findings From Our 2026 Travel Research
McAfee Labs found that many travel scams work because they look familiar and spread fast.
TripAdvisor was the most commonly impersonated travel app, cloned at roughly three times the rate of other major platforms like Kayak, Expedia, and Booking.com.
In some cases, thousands of scam detections traced back to just a handful of fake apps, showing how quickly a convincing scam can take off when travelers are racing to book.
Top 5 Ways Rising Travel Costs Are Driving Risky Decisions
Our 2026 travel survey shows how rising prices and last‑minute pressure are changing traveler behavior, often in ways scammers exploit.
1. Booking faster than usual 90% feel pressure to act quickly
2. Choosing cheaper deals without verifying 32% would book before confirming legitimacy
3. Ignoring red flags 33% admit they’ve done it
4. Trusting messages that look legitimate 41% trust airline/hotel messages without verifying
5. Clicking links without checking the source 20% click first, verify later (or not at all)
The Travel Scams People Are Most Likely to Fall For
According to our consumer survey findings, those who reported falling for a travel scam said these were the methods scammers used to trick them:
1. Fake travel deals or promotions (15%)
2. Scam booking confirmations or updates (15%)
3. Manipulated accommodation listings or photos (15%)
4. Payment requests outside official platforms (11%)
5. Fake vacation rental listings (10%)
6. Fake airline or hotel websites (9%)
7. Customer service impersonation (9%)
8 Ways Travelers Put Themselves at Risk Without Realizing It
These common traveler behaviors are popular avenues for criminals to steal your information, data, and money.
1. Connecting to public Wi-Fi (63%)
2. Scanning QR codes without verifying (62%)
3. Using airport Wi-Fi (49%)
4. Trusting travel-related messages (41%)
5. Logging into financial apps on public Wi-Fi (22%)
6. Sharing travel plans in real time (22%)
7. Clicking travel links without verifying (20%)
8. Using shared/public computers (15%)
How McAfee Protects You Before, During, and After Your Trip
As prices rise and decisions happen in real time, it’s easy to prioritize convenience over caution. But that’s exactly the moment when small checks matter most.
Stage of Travel
What’s Happening
How McAfee Helps
Before You Book
Comparing deals, clicking promotions, booking flights and hotels under time pressure
Scam Detector checks links, messages, and booking sites before you click, helping you avoid fake deals and scam listings
During Your Trip
Connecting to public Wi-Fi, scanning QR codes, receiving travel updates and alerts
VPN helps secure your connection on public Wi-Fi, while Scam Detector flags suspicious messages and unsafe links in real time
After Your Trip
Accounts remain active, travel data stored across platforms, potential exposure from breaches
Identity Monitoring alerts you if your personal information appears online, helping you act quickly before damage spreads
With McAfee+ Advanced, multiple layers work together so you’re not left figuring it out after the damage is done.
Spend more time on your vacation, and less time worrying about scammers who want your vacation fund.

 Login

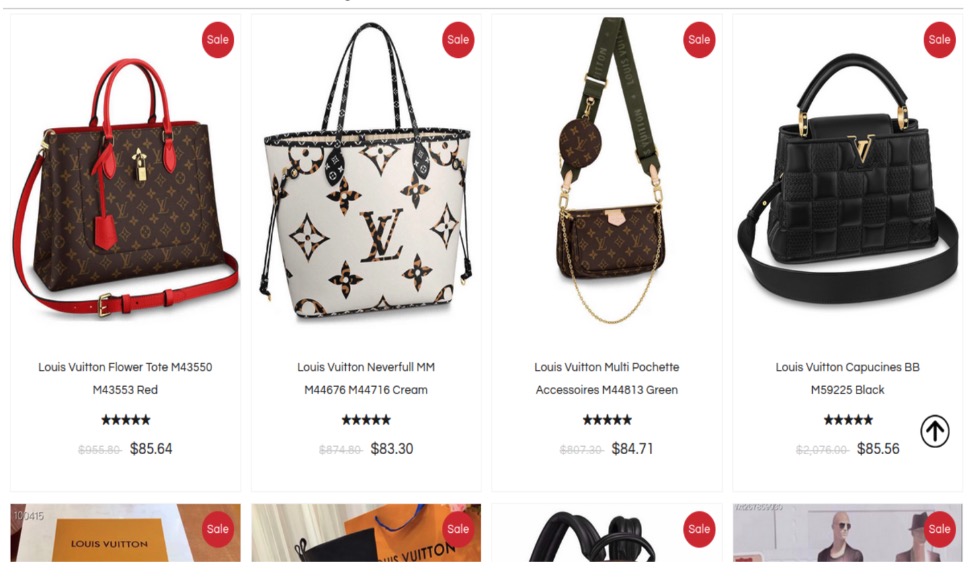
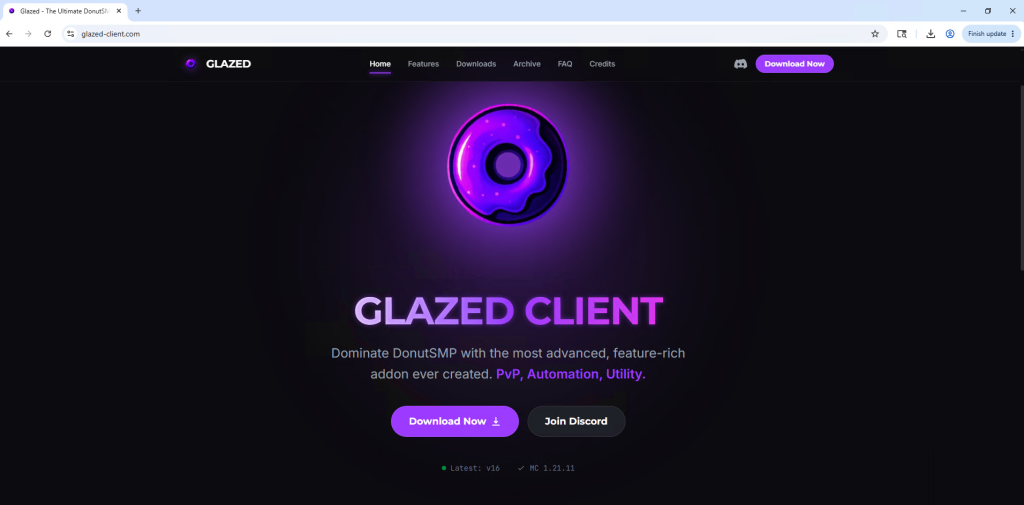
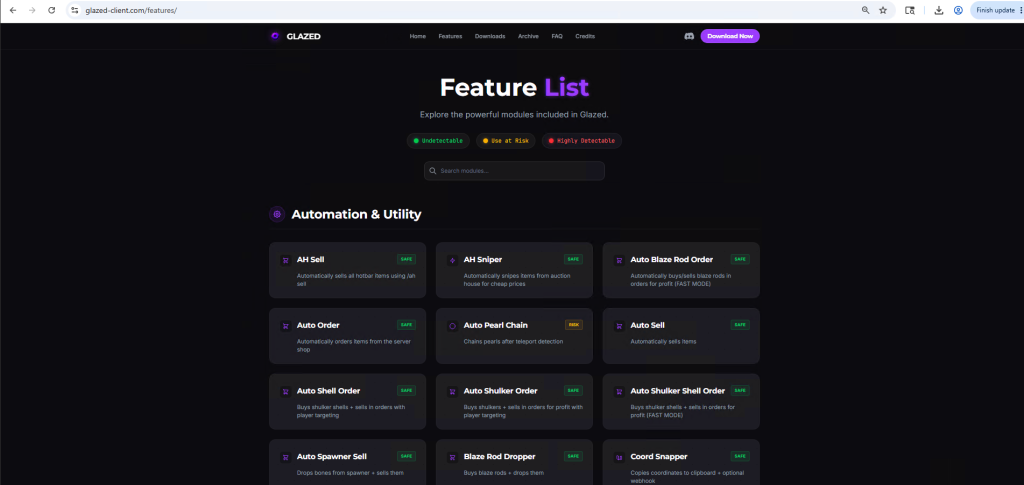
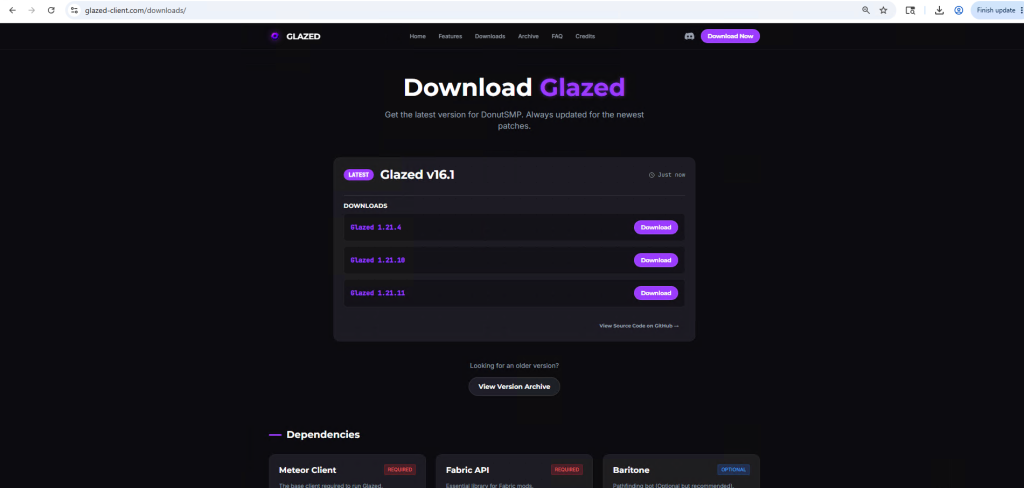
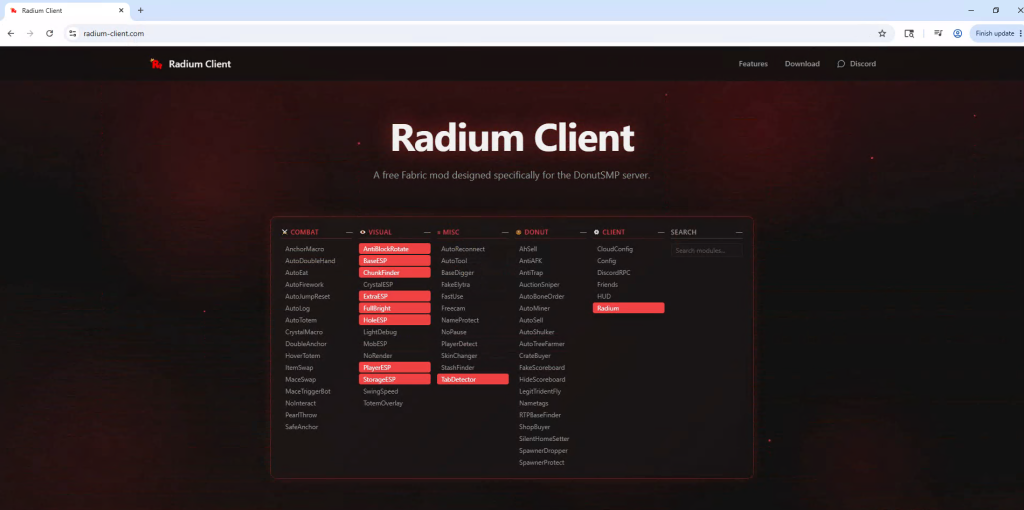
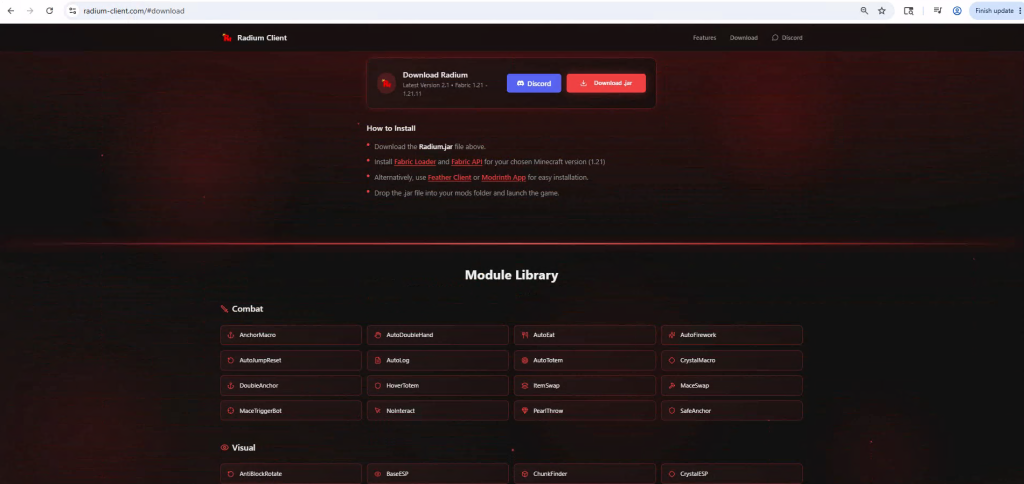
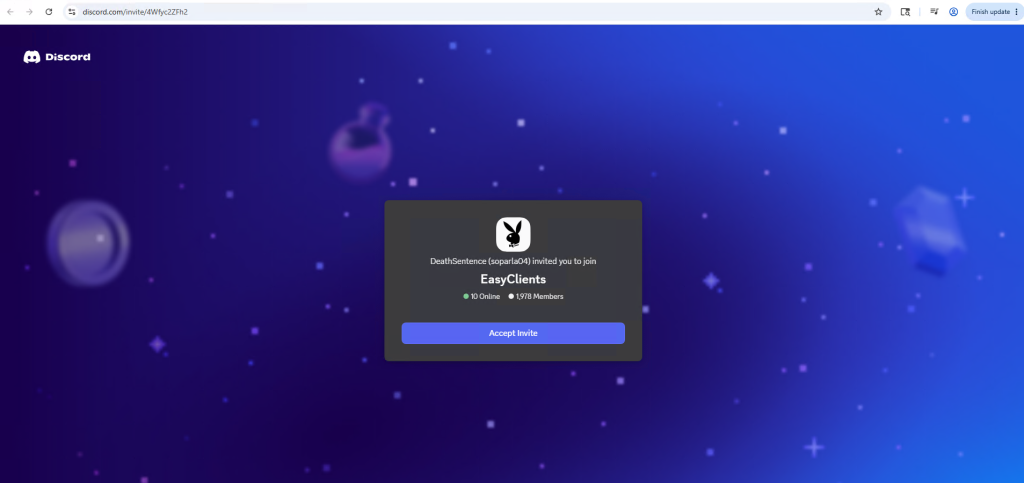
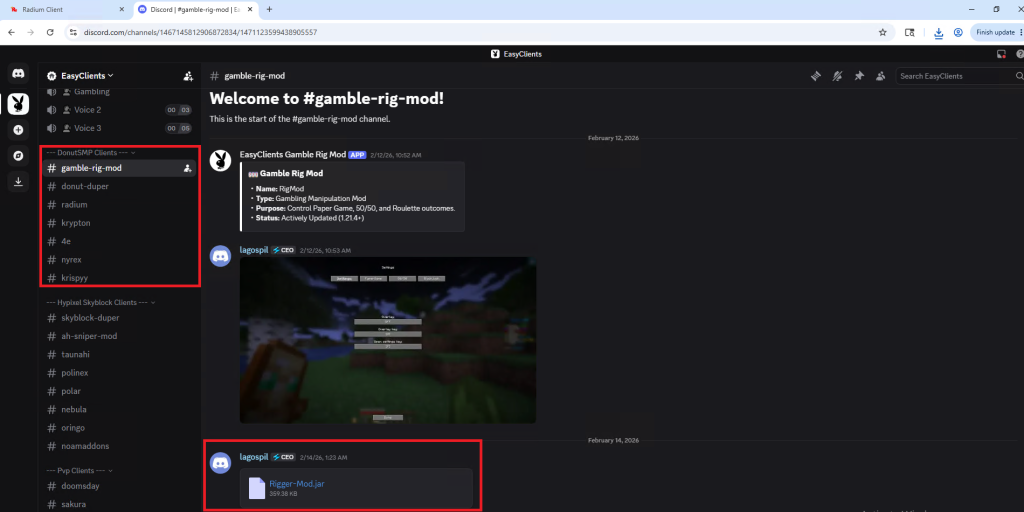
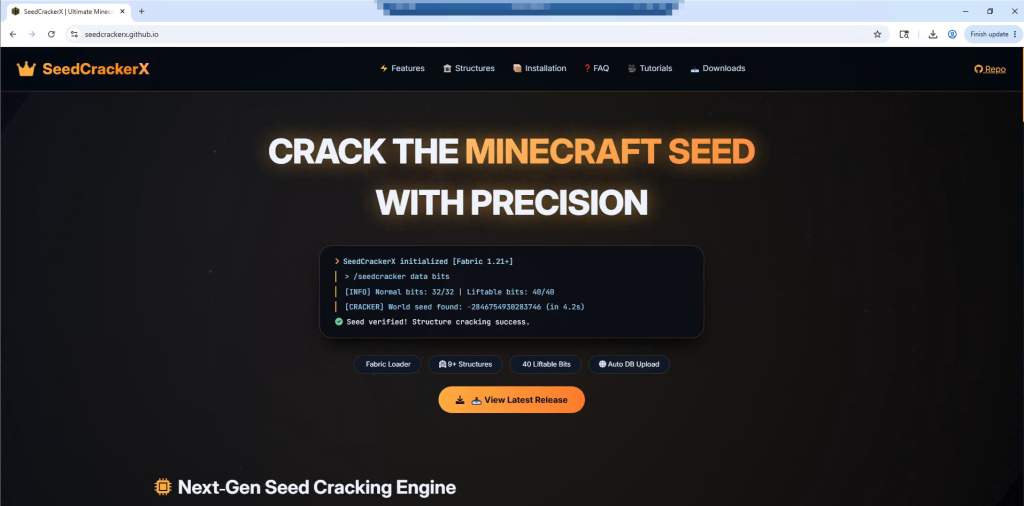
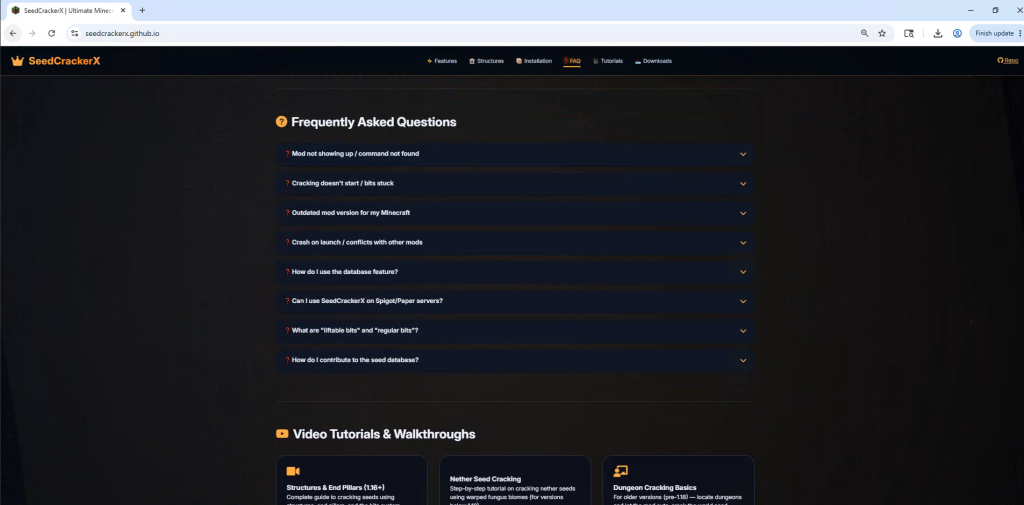
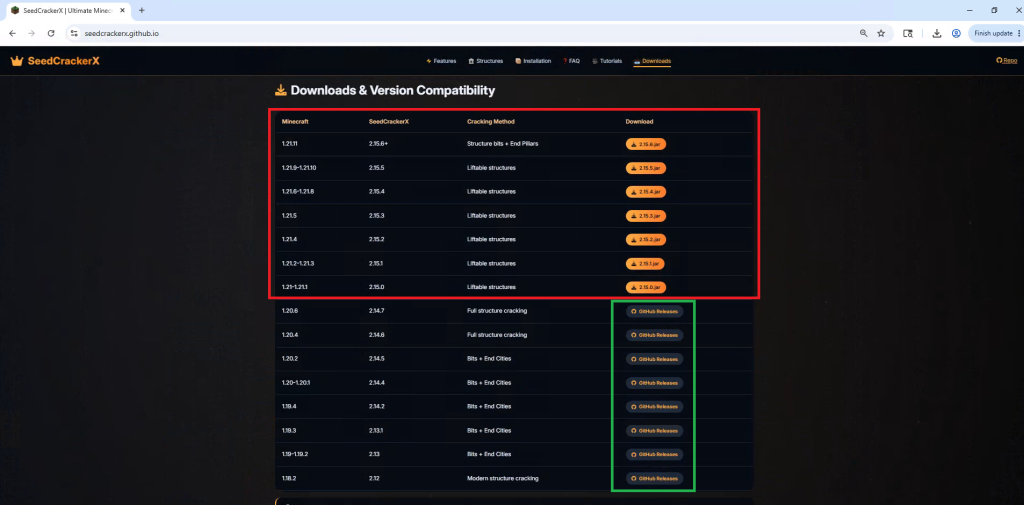
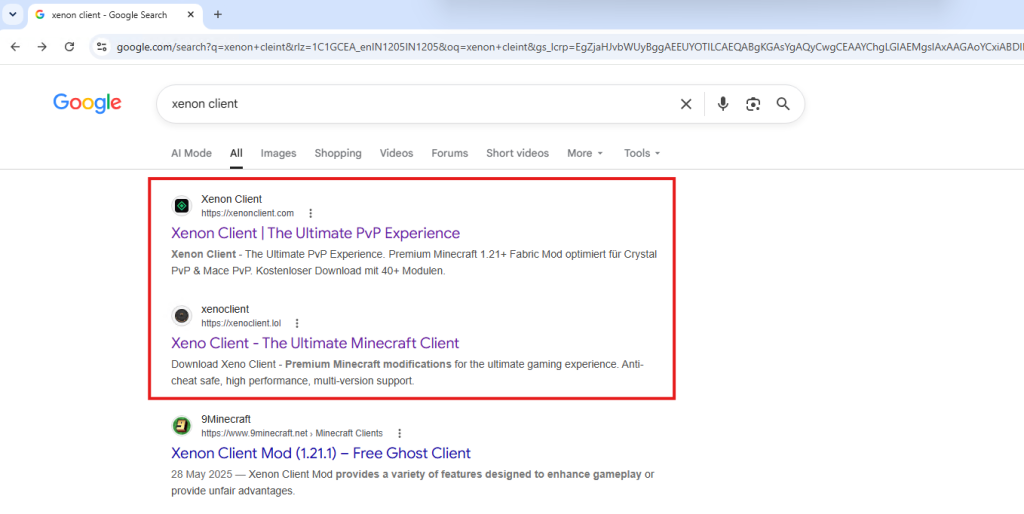
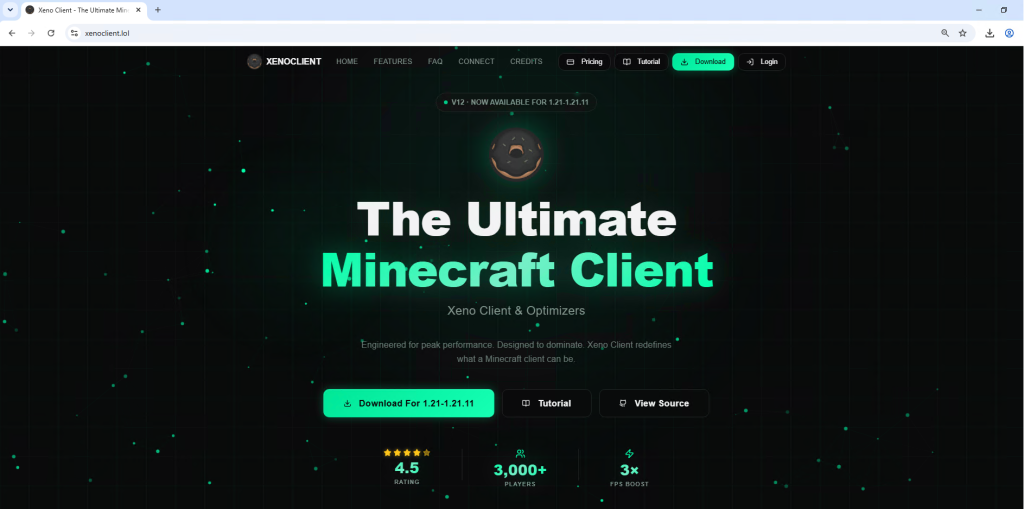
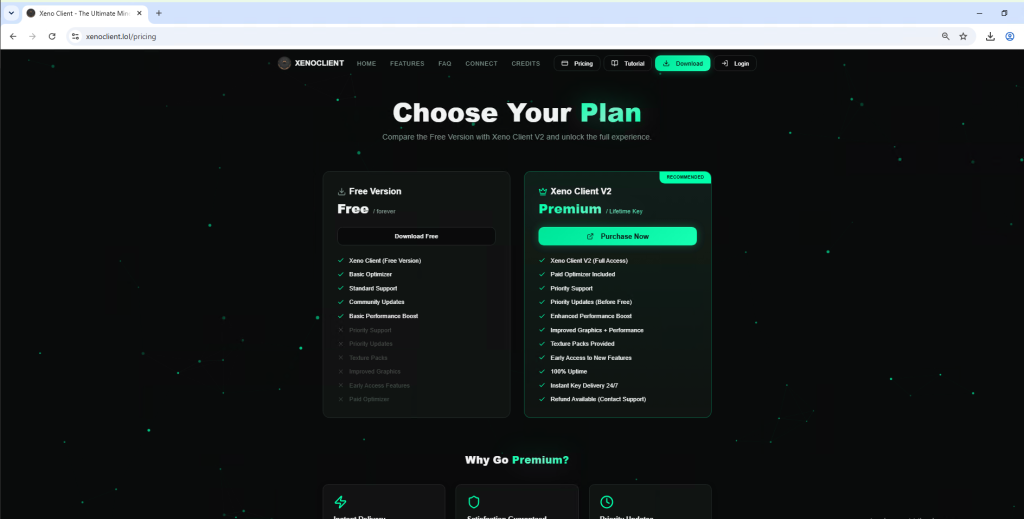
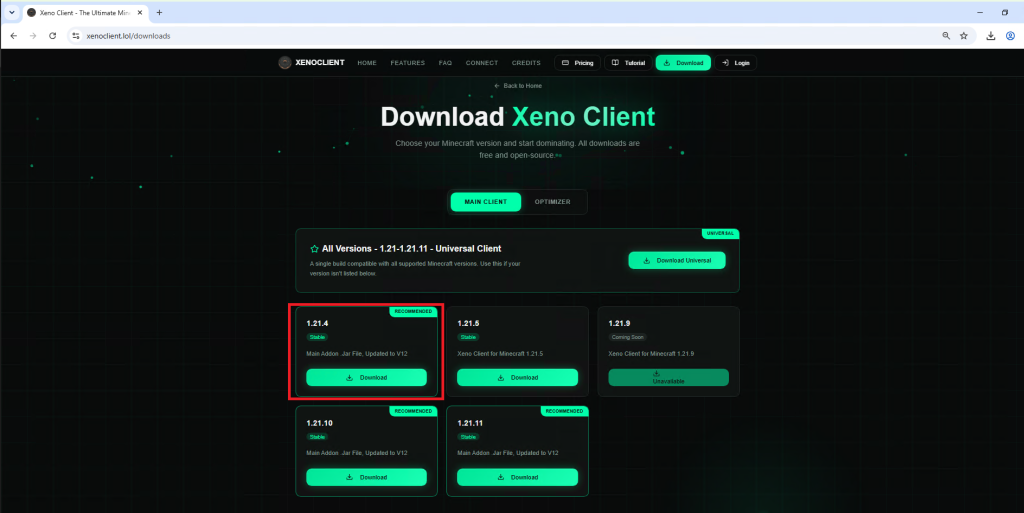
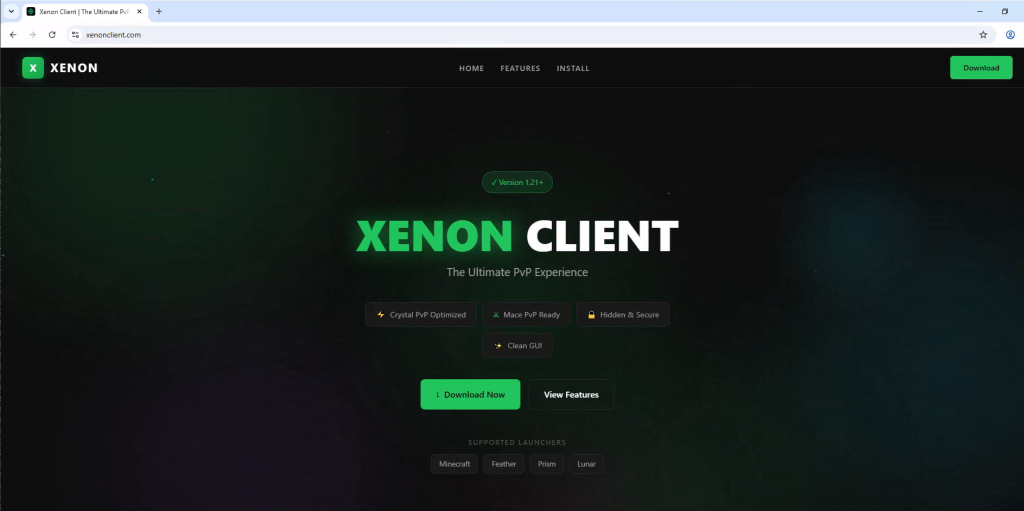
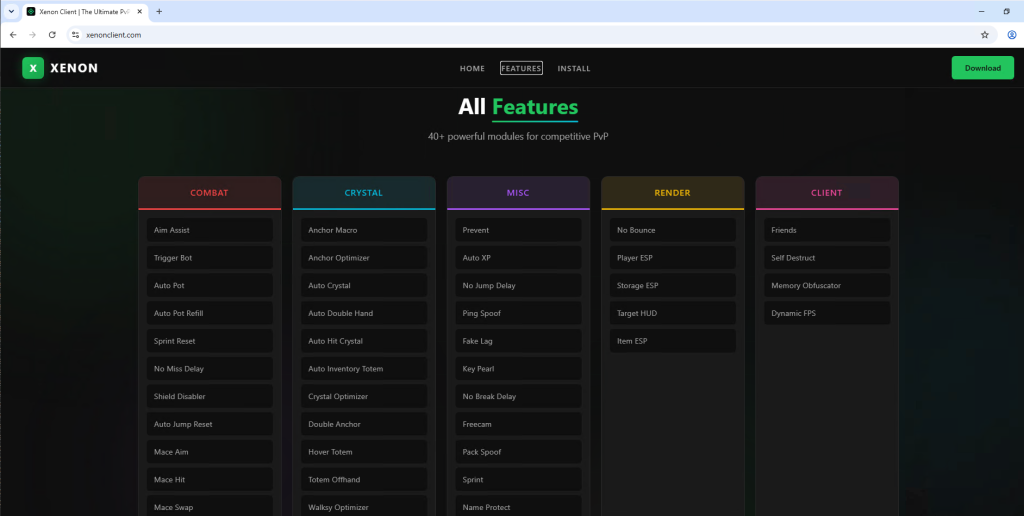
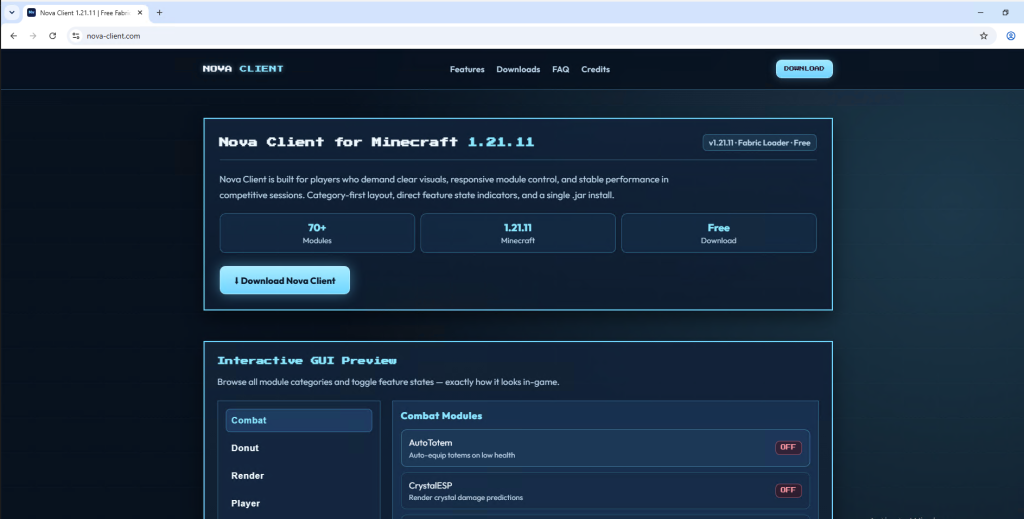
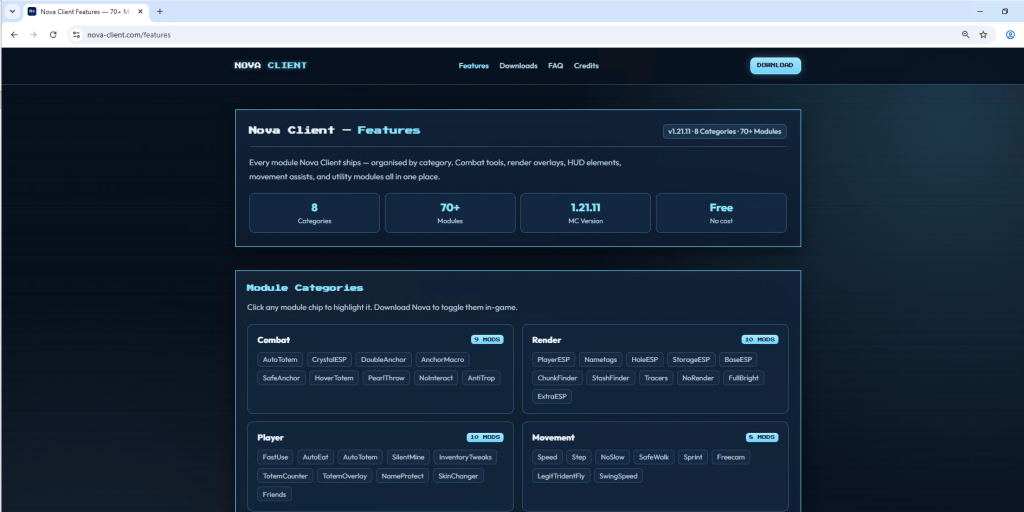
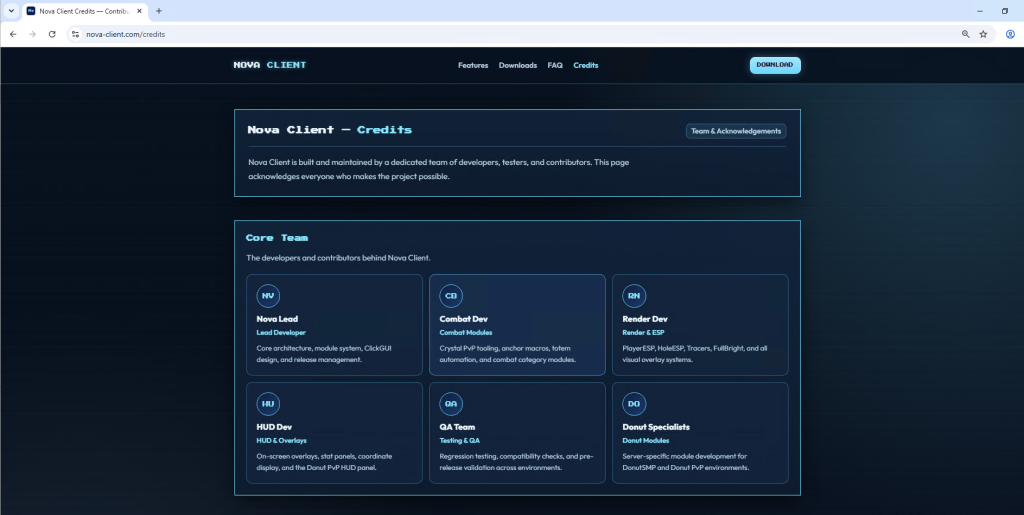
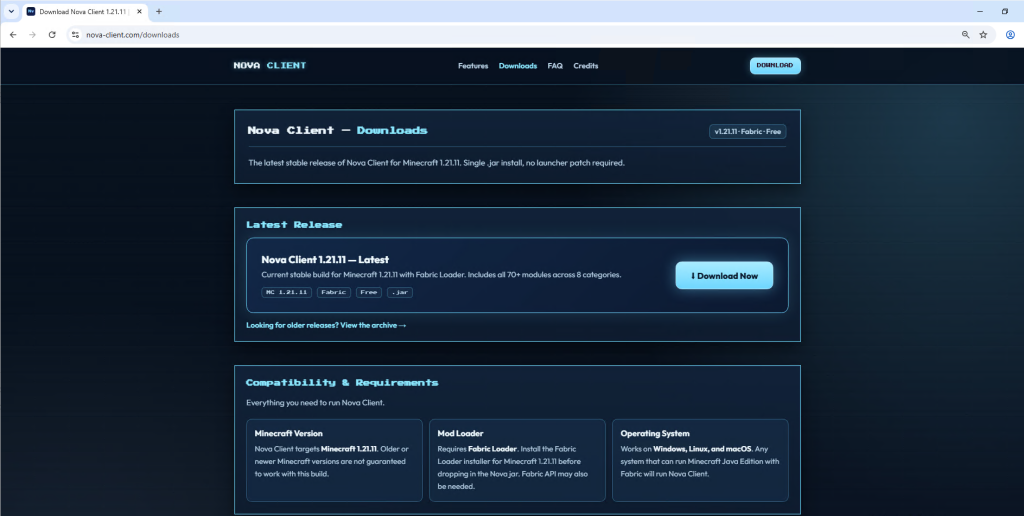
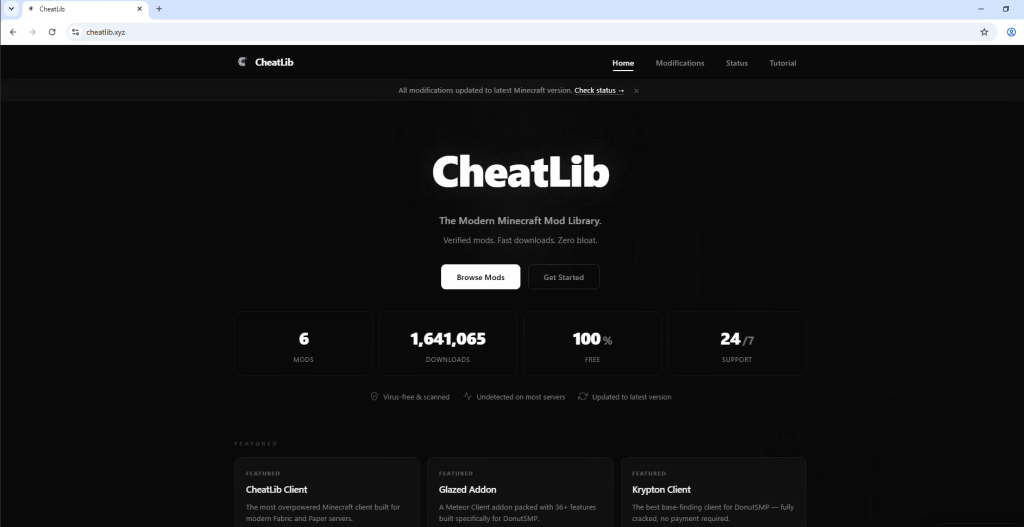
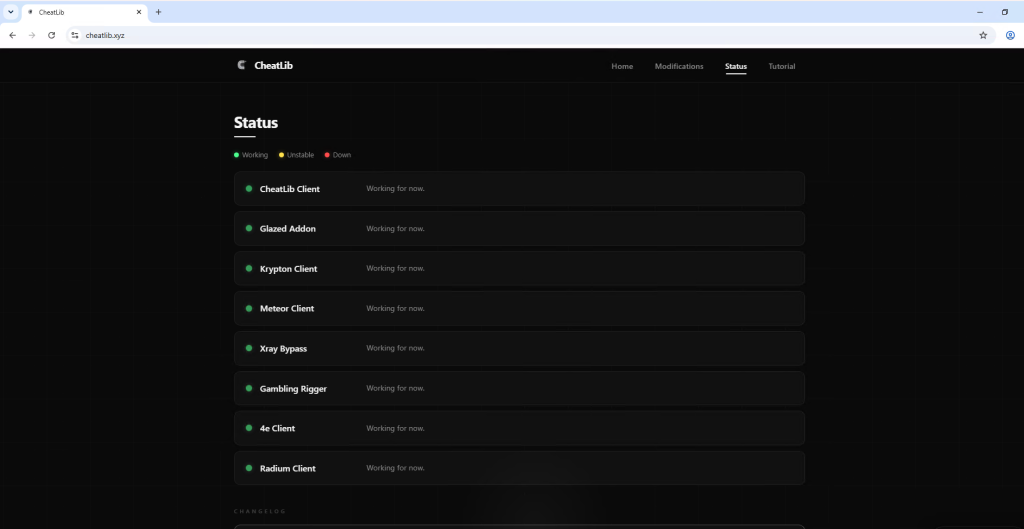
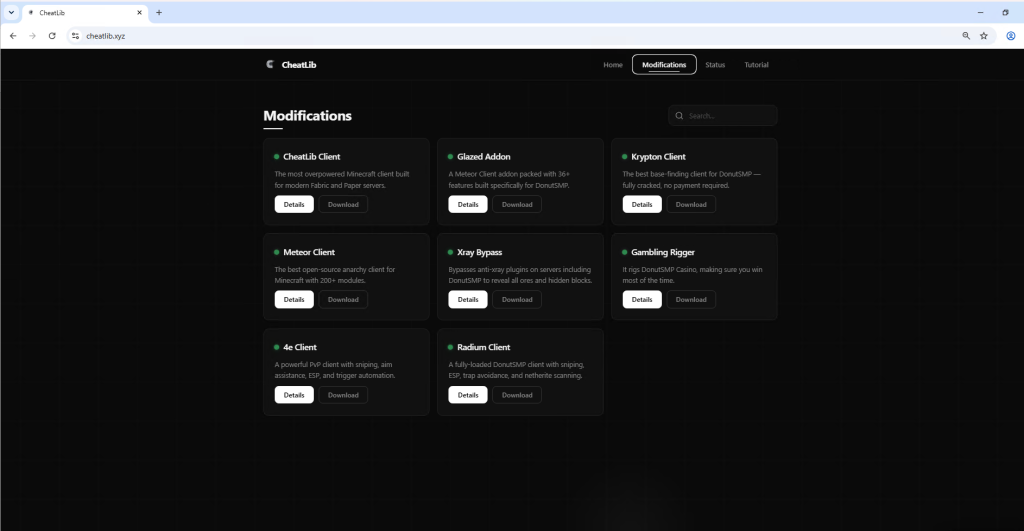
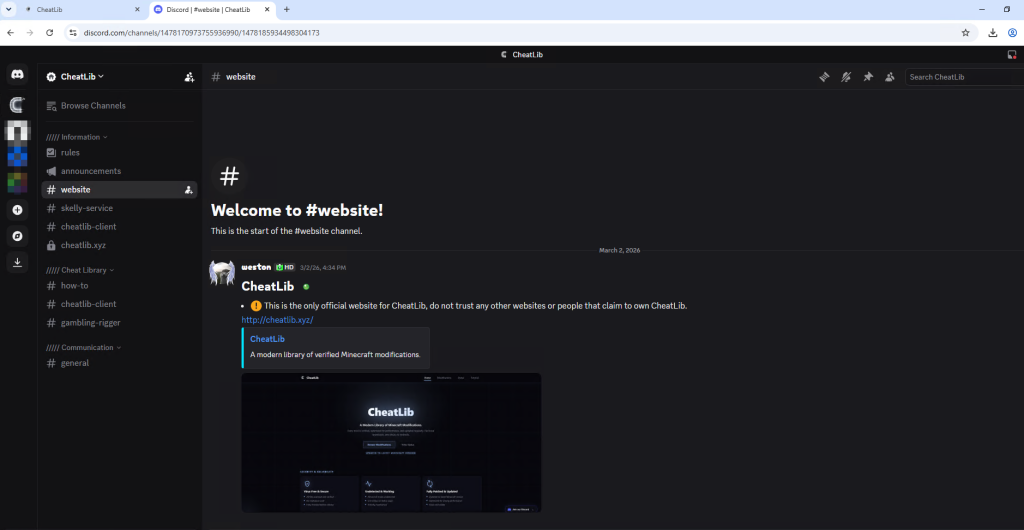
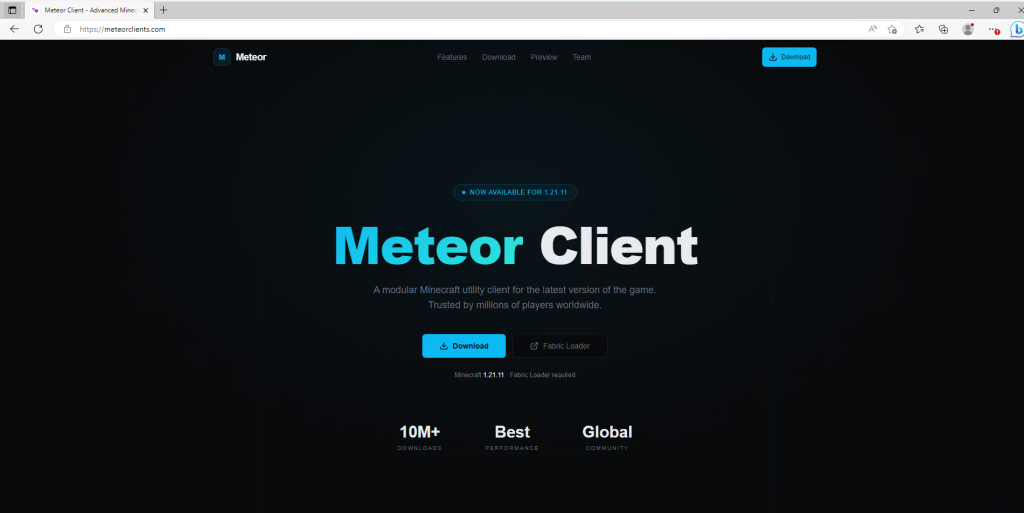
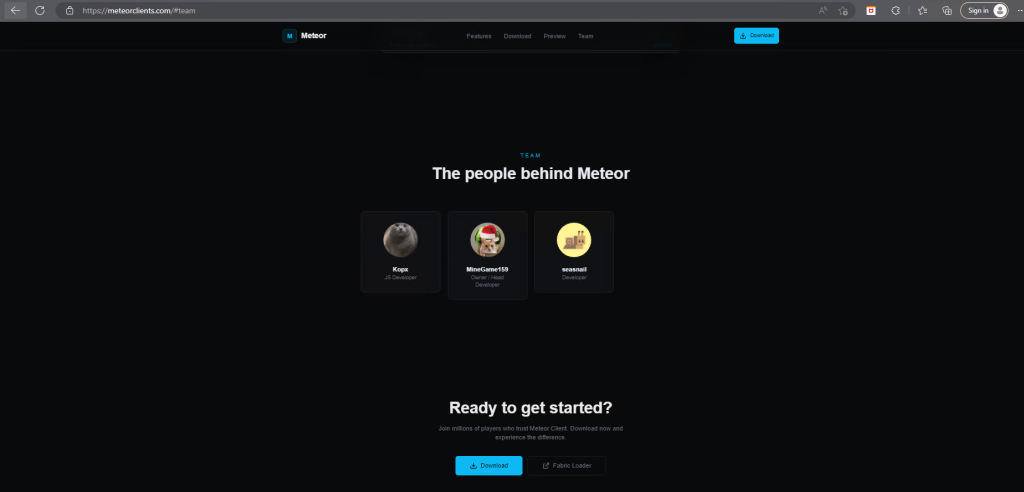
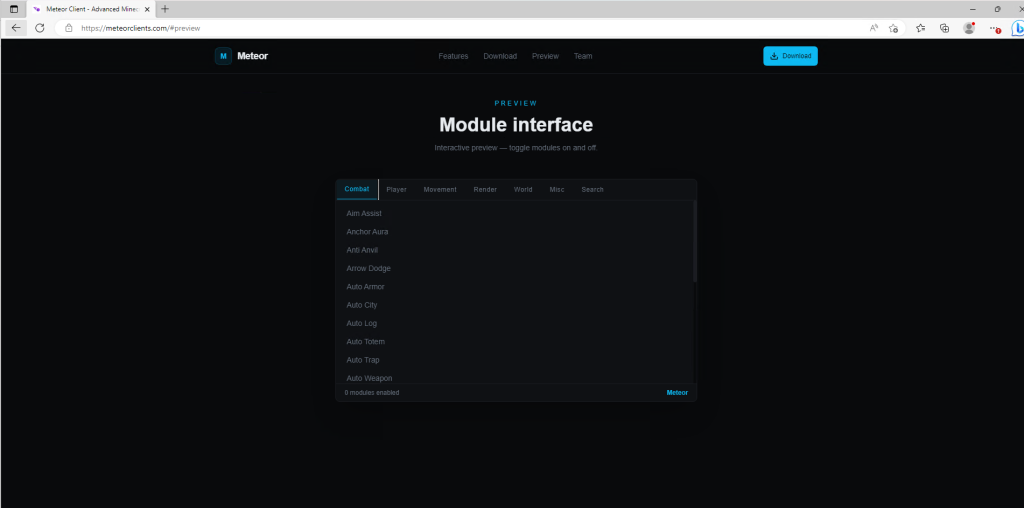
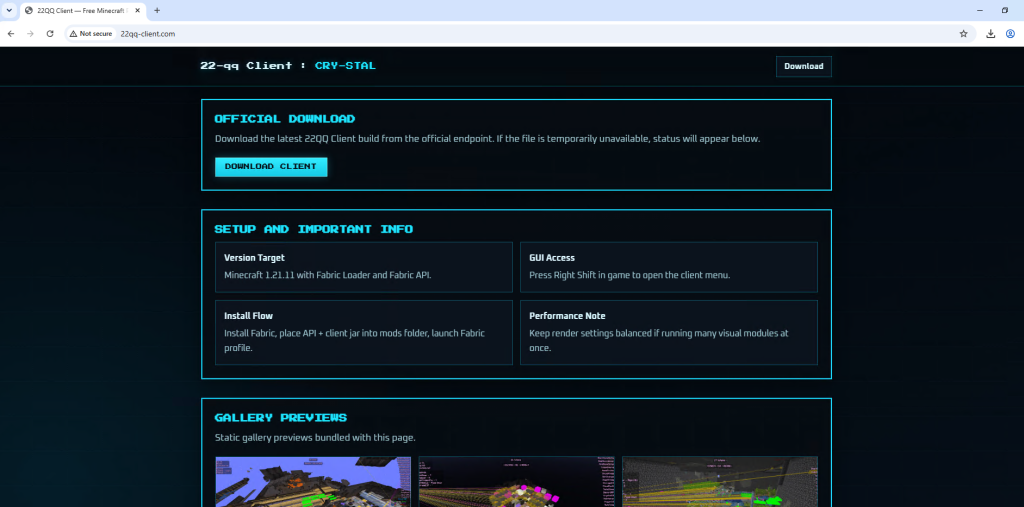
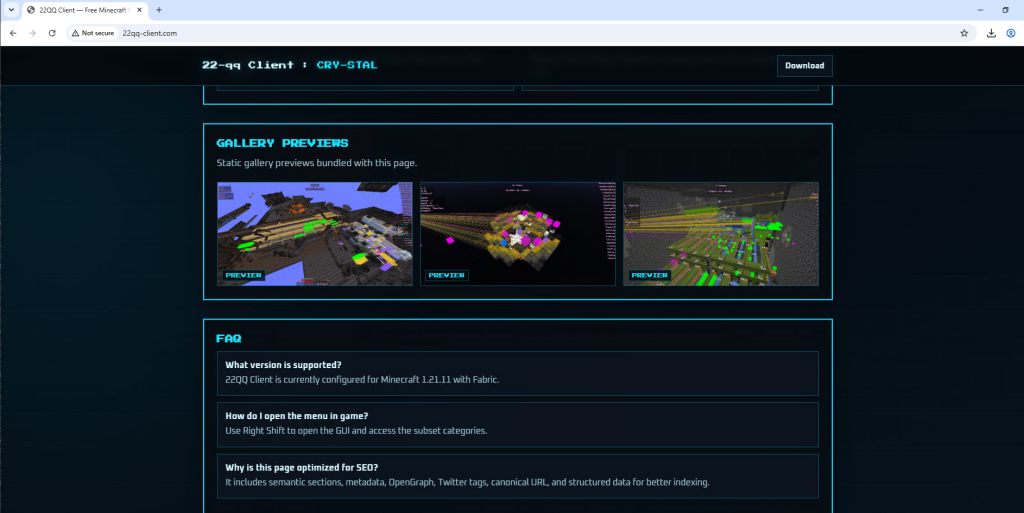
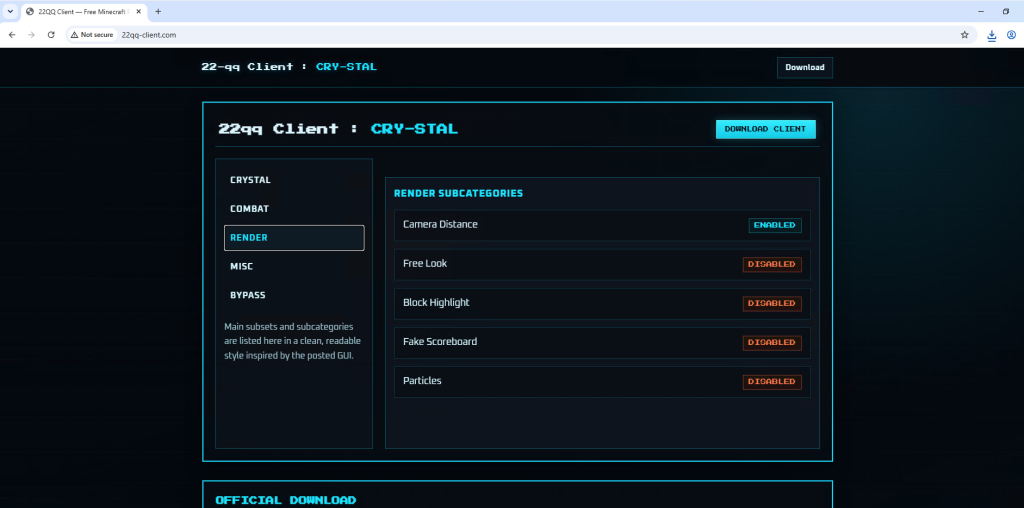
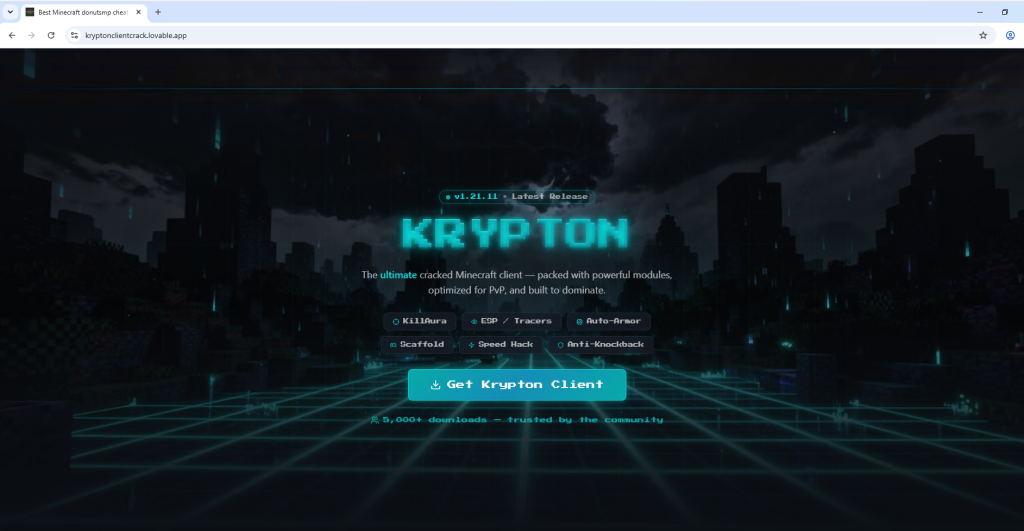
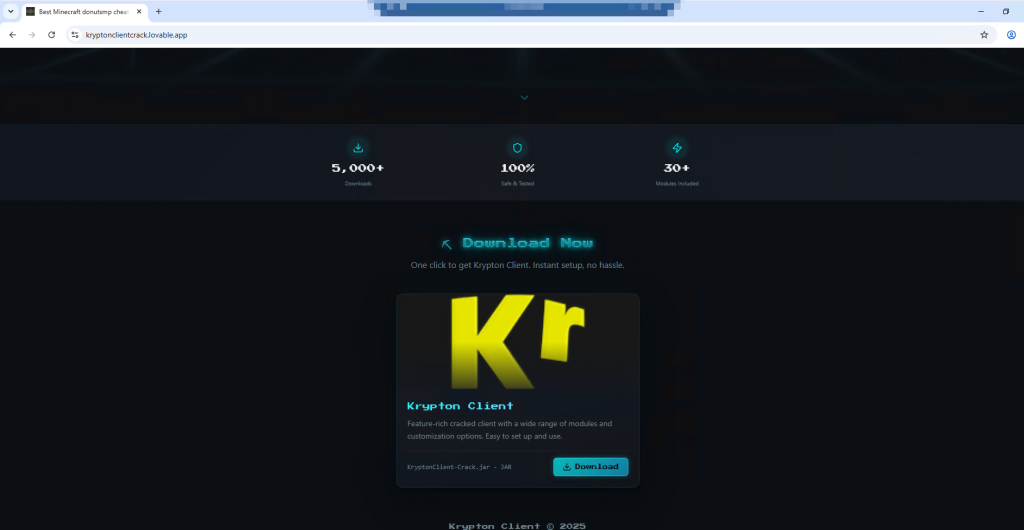
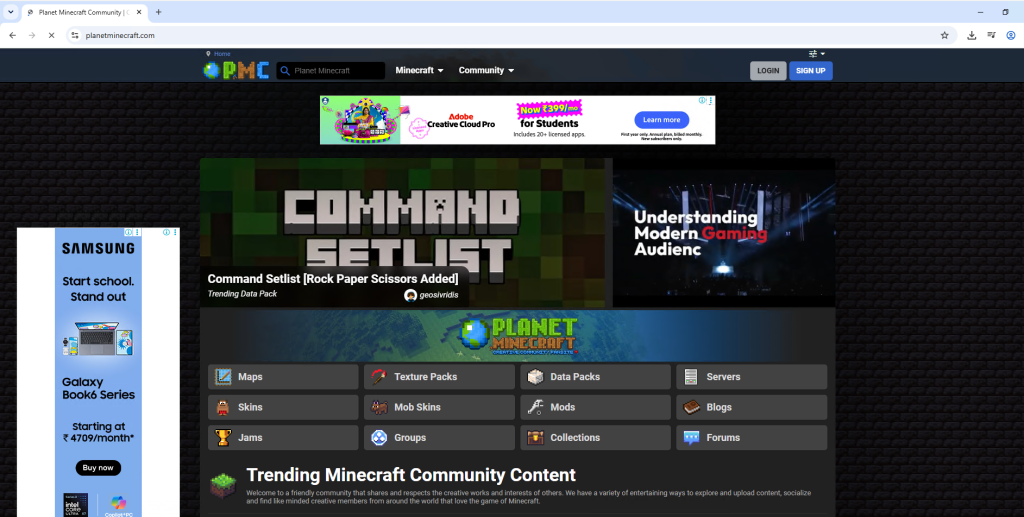
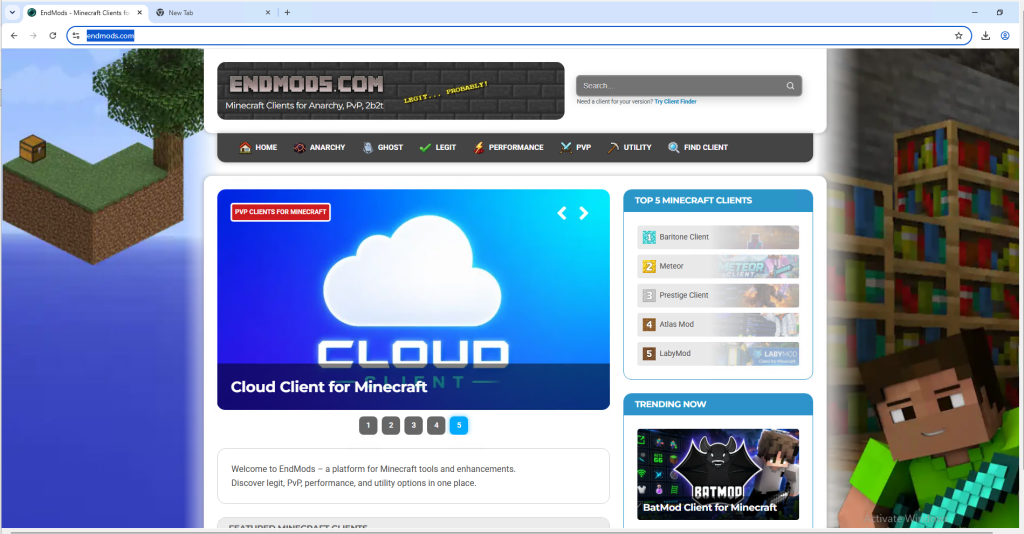
 The attack reportedly lasted about four and a half days and involved roughly